1) First of all observe how legitimate domain authentication requests are handled between domain controller and client
2) Wdigest downgrade attack
3) Pass the hash
4) Pass the ticket
5) DCSync and golden ticket attack
All of them can be carried out using Mimkatz!
#dfirlabs
@sailingbikeruk@pry0cc Many ways, easiest is covert to flat decimal
Say you have 8.8.8.8
(8x256)+ 8x256)+ 8x256)+8= 133744072
Ping 133744072
This can be done with any IP (replace 8!) and bypasses string detection looking for ‘IP. IP. IP. IP’
If you're a bug bounty hunter, you will 💚 this GitHub repository.
It contains all assets that we uncover on public bug bounty targets, and it is updated automatically, frequently 😎
Enjoy! 🚀
https://t.co/3Rf0WSZC9K
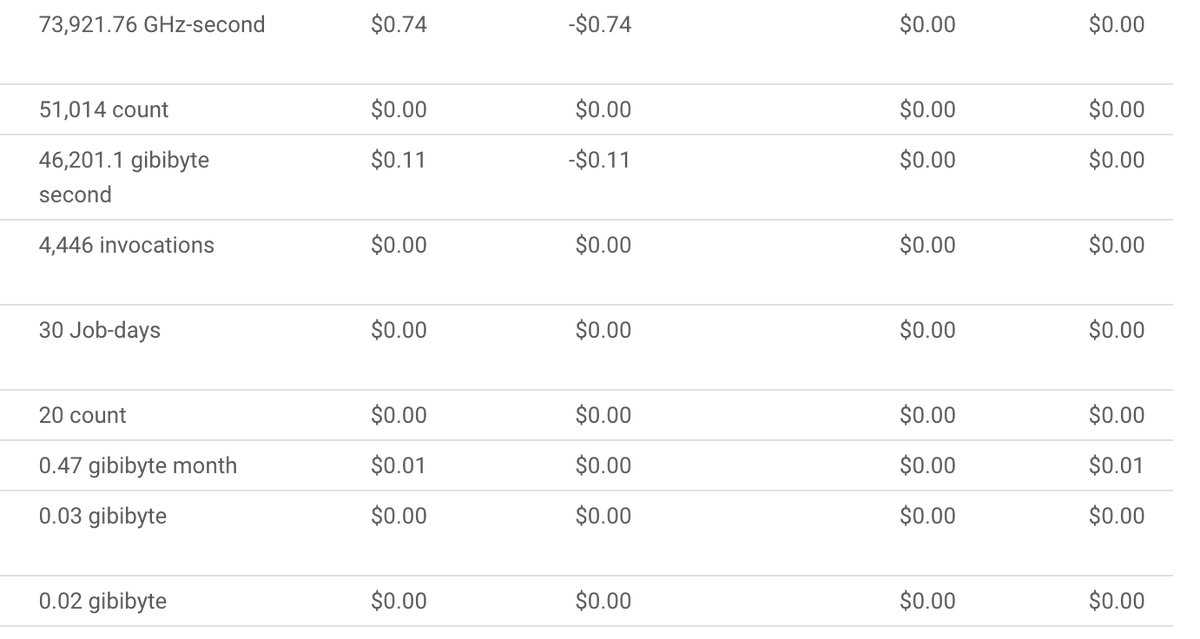
AWS/GCP Free tier stuff is so underrated, I've been running parts of my recon automation in the cloud for as low as 0.01$ per month for a long time, and it's been nothing but amazing!
🔒 Tool: SSH No Ports
SSH to a remote Linux host/device without that device having any open ports (not even 22) on external interfaces
All network connectivity is outbound
No need to know the target's IP
By @atsigncompany
https://t.co/ASampjUMqV
1/ #Linux#Forensics: pssst... I will now reveal my favorite interview question for candidates who want to work in our IR team ;) "In the process list, I see a (running) binary, but the binary is no longer present on disc. How can I restore the original binary? (screenshot 👇)"