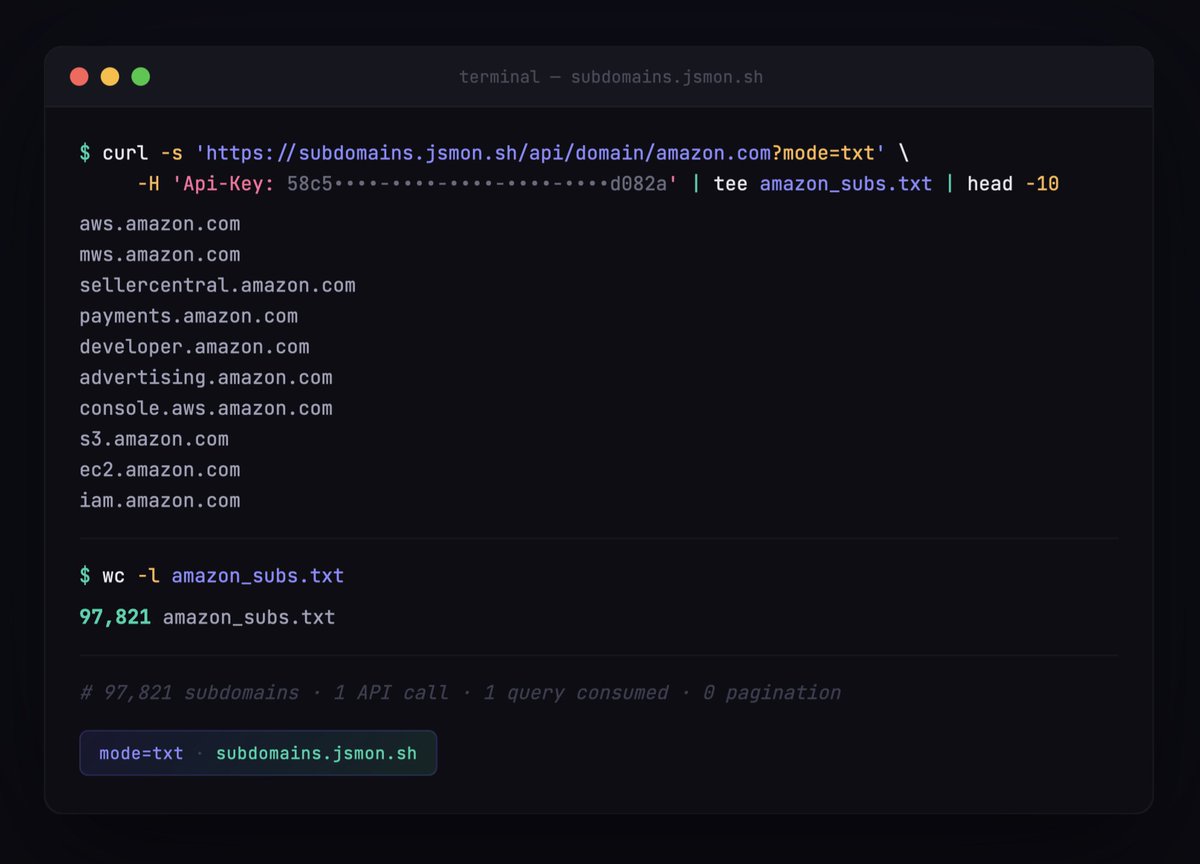
🚀 New Update: ?mode=txt on https://t.co/Huec3oviKv
One API call - Fetch all subdomains. Even if a domain has 500K subdomains, full output in seconds.
curl -s -H 'Api-Key: YOUR_KEY' 'https://t.co/IbvFtVUpZ9'
Available on Pro and Max plans.
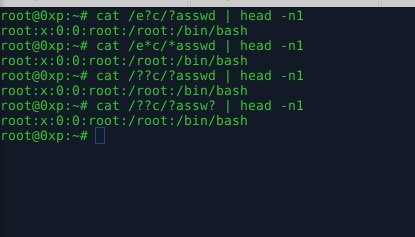
/etc/passwd ==> WAF restriction? Use these:
/e?c/?asswd
/e*c/*asswd
/??c/?asswd
/??c/?assw?
Doesn't work always, just give it a try. 🎯
#bugbountytip#bugbountytips#bugbounty
Join https://t.co/JjpdaifY9z
Unauth WordPress LFI → PHP exec. Public PoC is live!!!
CVE-2026-87902. get_page_template() builds page-{urldecode($pagename)}.php. locate_template() includes it with no theme-root jail.
No account. Pair a page-templates/ theme with pearcmd.php (register_argc_argv=On) and you get two-request www-data RCE. Lab-verified Sept 22.
Fixed in 7.1.2 / backports to 4.7.37.
https://t.co/D2d5ylfS5K
#Cybersecurity #AI #AISecurity #MCP #Claude #GPT #Infosec #Trending #WordPress #RCE #BugBounty
FOUND A TOOL THAT GIVES YOUR AI AGENT INTERNET ACCESS 🤯
Agent Reach lets agents access:
• Twitter/X
• Reddit
• YouTube
• GitHub
• Bilibili
• XiaoHongShu
• websites
• RSS
it handles the setup and picks the available backend for each platform
works with Claude Code, OpenClaw, Cursor, Windsurf and more
install it with one command:
https://t.co/76HLIvSLsz
open source and free to use
🚨 BUENO, POR SI NO ALCANZABA CON COPY FAIL… LLEGÓ DIRTY FRAG ☠️
Una vulnerabilidad Linux que permite escalar privilegios a root en prácticamente todas las distros importantes!
• Sin race conditions
• No crashea el kernel si falla
• Vulnerable hace 9 años
• No hay CVE ni parches todavía porque se rompió el embargo
Afecta Ubuntu, Fedora, RHEL, Alma, CentOS, openSUSE y más.
Para mitigarlo de forma temporal, podemos ejecutar lo siguiente:
sh -c "printf 'install esp4 /bin/false\ninstall esp6 /bin/false\ninstall rxrpc /bin/false\n' > /etc/modprobe.d/dirtyfrag.conf; rmmod esp4 esp6 rxrpc 2>/dev/null; true"
Esto desactiva los módulos involucrados hasta que salgan los patches correspondientes!
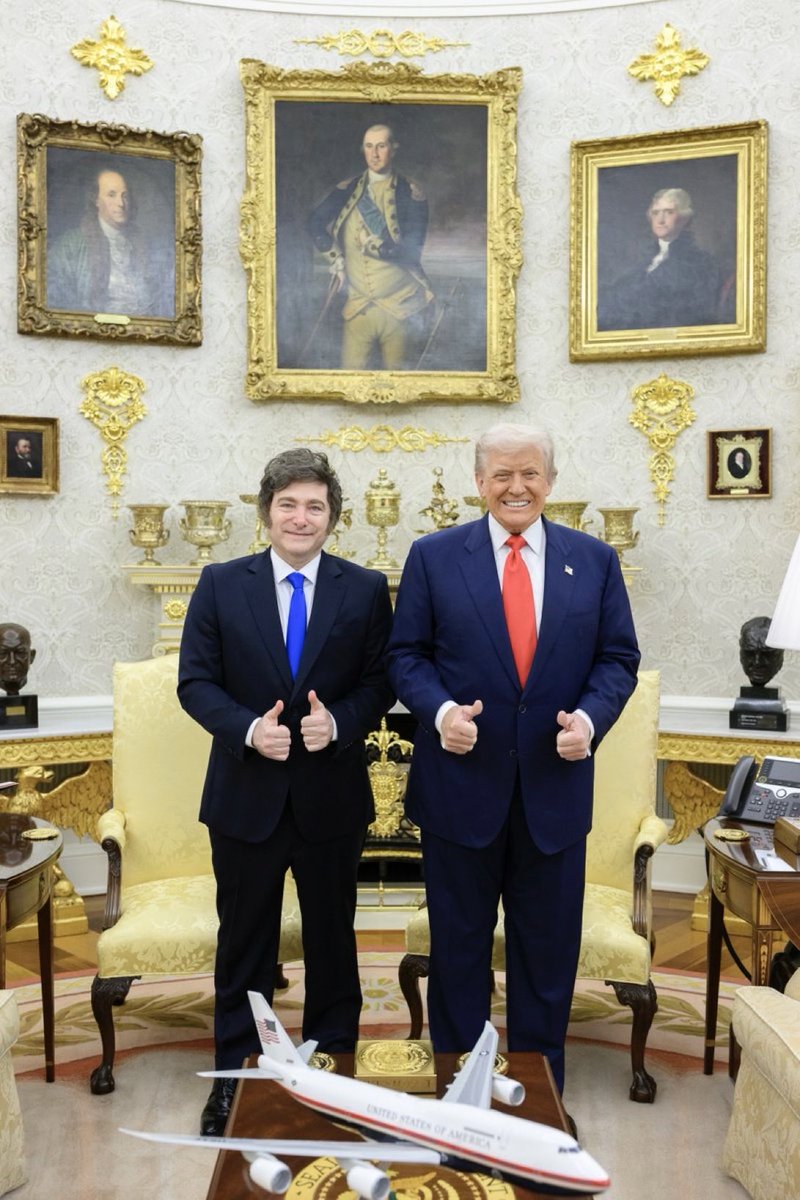
Muchas gracias Presidente Trump por recibirme en la Casa Blanca.
Desde antes de ser Presidente vengo sosteniendo que la República Argentina debe ser una aliada estratégica de los Estados Unidos de América y ahora que el pueblo argentino confió en mí para guiar los destinos de nuestra patria, cumplir con esa promesa es un paso más en la dirección que emprendimos el 10 de diciembre del 2023: Hacer Argentina Grande Otra Vez (MAGA).
El apoyo que Usted y su gran país nos ha dado es de vital importancia para la continuidad del largo camino de reformas que hemos emprendido. Los Argentinos saben que la principal potencia del mundo continuará apoyándonos salvo que volvamos a abrazar al populismo.
La situación es clarísima: si el país se alejara de la senda de las ideas de la libertad para volver al populismo, Estados Unidos dejará de apoyar a nuestro País. En su defecto nos van a seguir acompañando.
Pero yo confío en que ésta vez el esfuerzo va a valer la pena, que los argentinos no van a volver al pasado y que vamos a volver a ser una potencia mundial donde la inflación, la inseguridad y la pobreza sean solamente un mal recuerdo del pasado.
VIVA LA LIBERTAD CARAJO...!!!
Cc: @POTUS@realDonaldTrump
403 bypass methodology !
1- using space symbols
exmaple:
/admin -> 403
/admin%09 -> 200
/admin%20 -> 200
2- use traversal
Example:
/admin -> 403
/..;/admin -> 200
you can fuzz with traversal sometimes that's end with results
Example: /..;/FUZZ
#bugbountytips by @viehgroup
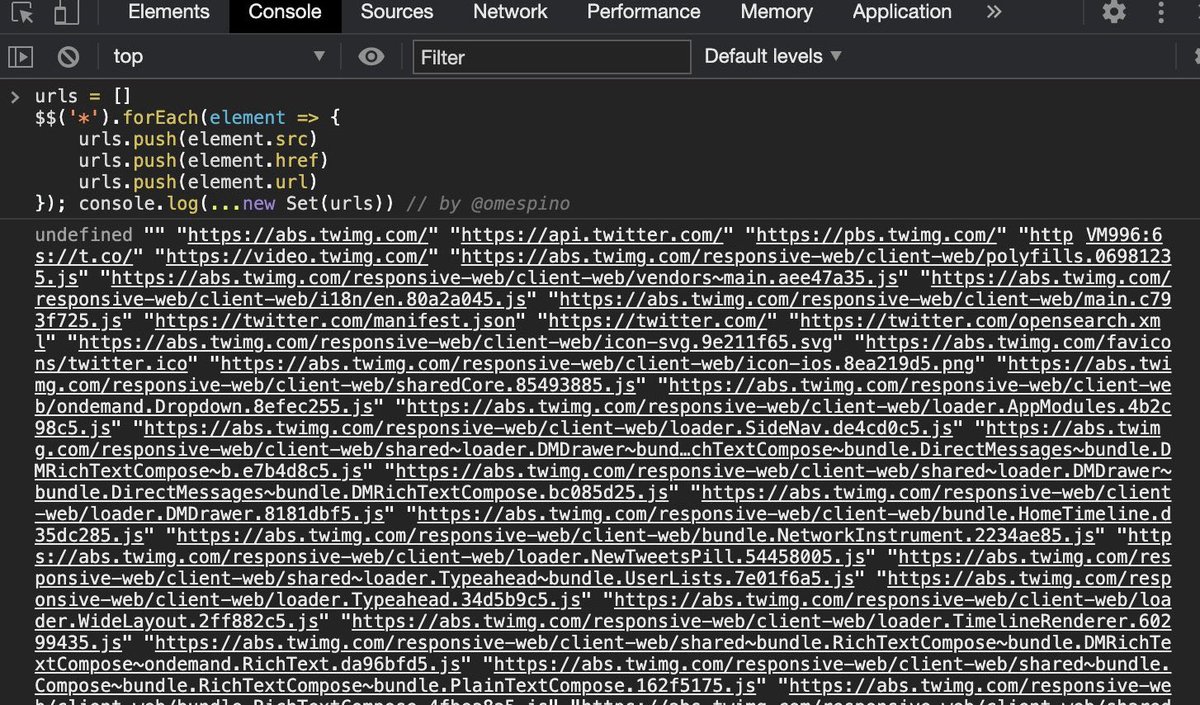
javascript How to extract urls,srcs and hrefs from all HTML elements in any website? Open DevTools and run
urls = []
$$('*').forEach(element => {
urls.push(element.src)
urls.push(element.href)
urls.push(element.url)
}); console.log(...new Set(urls))
#infosec #cybersec #bugbounty
Red Teaming 101 :
FUD Reverse Shell and Advanced Social Engineering on Windows (Part 4) : https://t.co/qUK1O6FYA9
Privilege Escalation on Windows Using LNK Files (Part 3) : https://t.co/V3wrbJoKvq
Part 2 : Bypass Mark of the Web (MotW) on Windows : https://t.co/J93gL9idrk
Part 1 : Using LNK Files for Initial Access : https://t.co/9abRlBQvsT
Malware Development :
Part 8 : Reverse Shell Via Dll Hijacking : https://t.co/PK2nSLlF3j
Part 7 : Advanced code injection : https://t.co/Wpa8ZGQzjl
Part 6 : DLL Hijacking : https://t.co/e84vMXGiIg
Part 5 : DLL injection into the process : https://t.co/DqI9rSCtTz
Part 4 : https://t.co/YgqXOsk9pb
Part 3 : https://t.co/eIaQkUq6TQ
Part 2 :
https://t.co/DzpUgER92Z
Part 1 : https://t.co/AdRu7NsYXt