What is veBTC and veMEZO??
Do you have an idea of what they are?
Go over to taskify follow the steps and get a chance to earn from the reward pool.
https://t.co/nSpak8fwNX
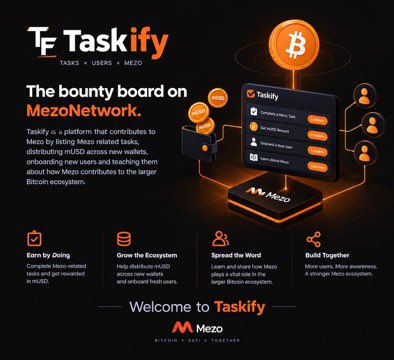
Taskify is the bounty board for @MezoNetwork.
A platform built to actively contribute to the Mezo ecosystem by turning participation into action.
Through Taskify, users can:
Discover and complete Mezo-related tasks
Earn mUSD rewards
Learn how Mezo connects Bitcoin to the broader DeFi ecosystem
Contribute to the growth and awareness of Mezo
The goal is simple: more tasks, more contributors, more users, and a stronger Mezo ecosystem.
Welcome to Taskify.
Taskify is live on mainnet.
Browse open tasks → apply for your fit → earn as you contribute.
Post a task of your own → for developers or the community.
Open to everyone. Live on Mezo.
Get started: https://t.co/PKmuOp0O3o
You feel something is not going right and you've got a solution BUILD
You Need something but it's not available BUILD
An idea crossed your mind BUILD
In this time of AI make sure you are BUILDING
Happy Sunday.
New week same grind different goals
Day 47/100 of ZK
Today we focused on the prover side of Groth16: how the actual proof is constructed once the QAP is ready.
From Witness to Polynomial Evaluations
The prover starts with the witness vector w (public inputs, private inputs, and all intermediate values). Using this witness, the prover evaluates the three QAP polynomials at the secret point τ from the trusted setup:
A(τ) = sum of (witness coefficients × powers of τ from the proving key)
B(τ) = same process for the B polynomial
C(τ) = same process for the C polynomial
These evaluations are performed as multi-scalar multiplications against the precomputed powers of τ stored in the proving key. This is usually the most expensive part of proving.
Adding Blinding Factors
If the prover simply sent [A(τ)], [B(τ)], and [C(τ)], an attacker could potentially extract information or forge proofs by solving linear equations. To prevent this, the prover adds random blinding terms.
The final proof elements become:
π_A = [A(τ) + α·r + blinding terms]₁
π_B = [B(τ) + β·s + blinding terms]₂
π_C = [C(τ) + H(τ)·Z(τ) + more blinding terms]₁
Here r and s are fresh random field elements chosen by the prover. The extra terms cancel out correctly during verification for an honest prover but break the equations if someone tries to cheat.
Assembling the Three Proof Elements
After the blinded evaluations are computed, the prover packages them into the three group elements that form the complete Groth16 proof. These three elements are all that the verifier will ever see.
The entire process compresses the full witness and the entire QAP into a constant-size proof, independent of the number of constraints.
Valor is back, so is Gooddollar with the Celo network
Claiming and identity verification are live again.
The team acted fast, and the issue has been resolved.
Thank you for your patience. We hope this doesn’t happen again. Play on.
Day 48/100 of ZK 🔐
Today we focused on the verification side of Groth16: the exact pairing checks the verifier performs and how public inputs are incorporated.
The Core Verification Equation
After receiving the three proof elements π_A, π_B, and π_C, the verifier uses the verification key to check a pairing equation of the following form:
e(π_A, π_B) = e([α]₁, [β]₂) · e(public_input_terms, [γ]₂) · e(π_C, [δ]₂)
In expanded form this checks that:
A(τ) · B(τ) = αβ + public_input_contribution + C(τ) + H(τ)·Z(τ) · δ-related terms
The left side comes from the product of the first two proof elements. The right side reconstructs the expected value using the verification key and the public inputs.
How Public Inputs Are Handled
Public inputs are not hidden. The verifier knows them and therefore can compute a linear combination of the corresponding verification-key elements. This combination is inserted into the pairing equation so that the public values are correctly accounted for without the prover having to hide them.
If the public inputs are wrong, or if the prover used inconsistent private values, the equation fails.
Why Blinding Terms Cancel
The random blinding factors the prover added on Day 47 are carefully constructed so that they cancel out on both sides of the pairing equation when the proof is honest. A malicious prover who tries to forge a proof without a valid witness cannot make the blinded terms cancel correctly, so the pairings will not match.
Result
If all pairing checks pass, the verifier is convinced that the original R1CS constraints were satisfied for the given public inputs, without learning anything about the private witness.