TRUMP JUST REPOSTED JFK’S MOST TERRIFYING SPEECH — AND THE DEEP STATE IS PANICKING
JFK saw it coming. In 1961. And now, Trump has just made sure 300 million Americans see it, too.
“A lot of people hate Trump, and that's fine. But if you're watching a news network that refuses to air the president of the United States, they're not giving you a chance to think for yourself. They're telling you what to think.”
Couldn’t be more true!! If you hate Trump and watch the news, you’ve probably been programmed 🎯
Intune Custom Compliance Policies and the Hourly Cadence Fix
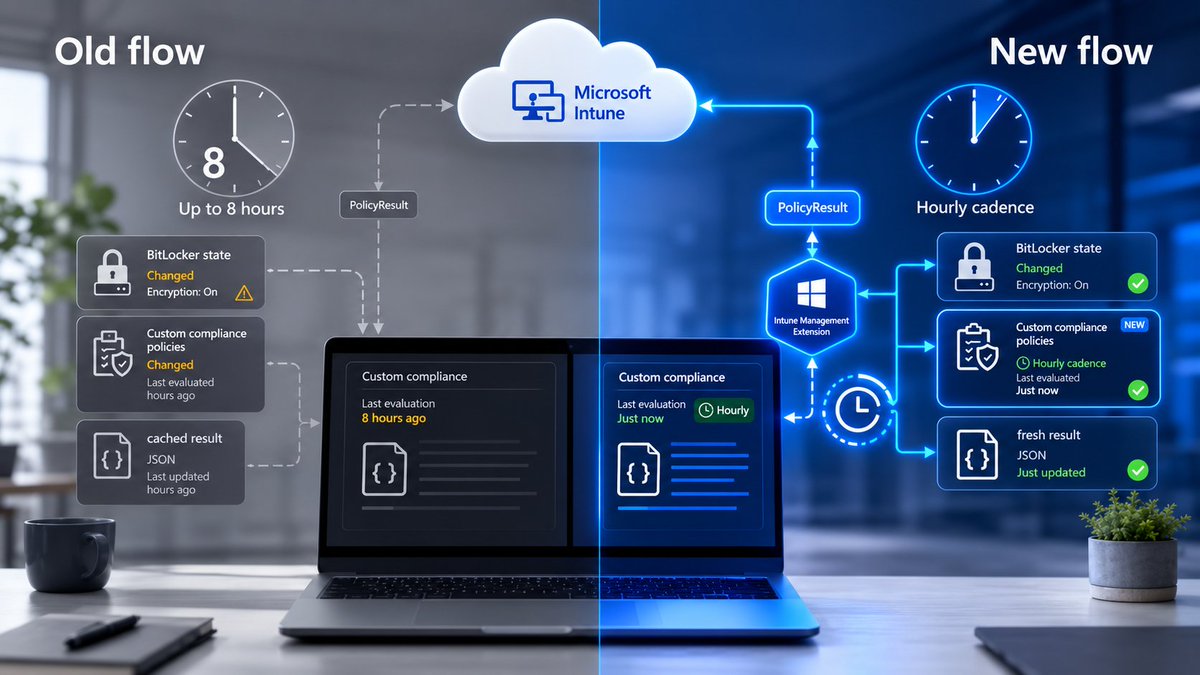
When the built-in Intune compliance settings were not enough, custom compliance policies gave us the flexibility to check almost anything we wanted.
The biggest downside was always the same.
After the device state changed, we could still wait up to 8 hours before the discovery script ran again to get the device compliant or non-compliant.
IME version 1.103.101.0 now appears to also introduce an hourly cadence for custom compliance scripts. (that IME version is full of new features!!)
That could make one of the most powerful compliance features in Intune much more useful in practice. Not instant, but potentially a lot less waiting.
Read the full technical breakdown here: https://t.co/lNyOD21xti
#MSIntune #Intune #Compliance
🚨 Anthropic just showed a 27-minute workshop on how to actually do prompts for Claude.
Taught by the people who built it.
Free. No registration. No paywall.
I've seen $300 courses that don't cover what they teach in the first 8 minutes.
Watch the session
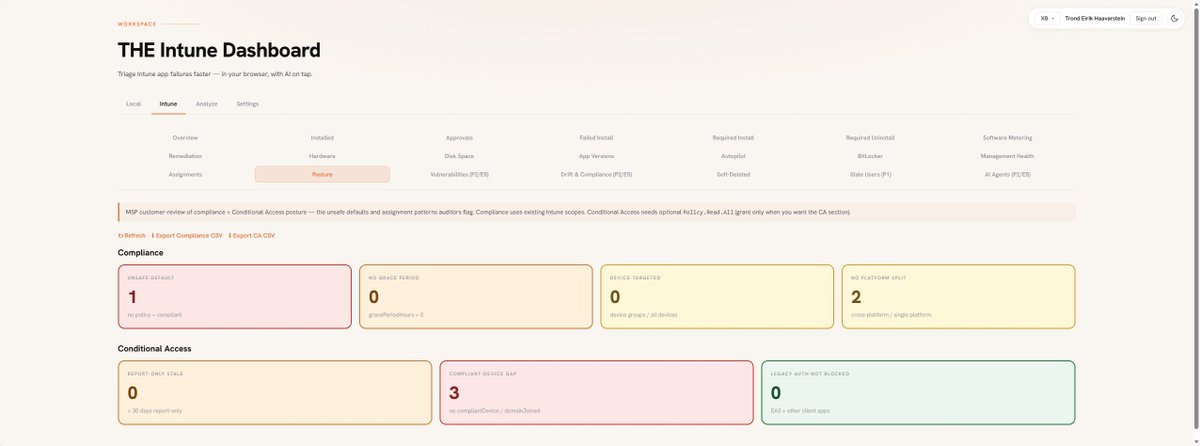
Why didn’t somebody tell me before that "compliant" in Intune can still mean no compliance policy at all? 😩
Auditors flag this every time. Today you open three blades and squint.
The FREE Intune Dashboard now has a Posture tab — one page for the gaps that matter:
Compliance • Unsafe default (no policy = compliant)
• No grace period
• Device-targeted compliance
• No platform split
Conditional Access (optional https://t.co/FAhzaWEM6W.All)
• Report-only stale > 30 days
• Compliant-device gap
• Legacy auth not blocked
Click a tile → drill-in + deep-links. CSV export when you need the cleanup list.
MSP customer reviews just got a lot less painful.
@MSIntune #Intune
You can remove preinstalled Microsoft Store apps such as Clipchamp, Xbox, Weather, and Feedback Hub. Follow our guide to learn more:
https://t.co/ag8YAaQSle
#MSIntune#Microsoft#Apps#SCDudes
Reminder⏰: Intune-managed Win32 app delivery will be HTTPS-only 🛜, affecting Connected Cache customers.
Starting today, #MSIntune will be enforcing HTTPS-only delivery for managed Win32 app content.
For more information, refer to https://t.co/vwCFk9D5nv
Why didn’t somebody tell me before how messy our hardware inventory actually was? 😩
Just opened the new Hardware view in the Intune Dashboard:
- 100% on Windows 11 (678 devices)
- 0 Windows 10 left (good, EOS was Oct 2025)
- BUT… 15 devices haven’t checked in for 90+ days
- 117 devices with **no primary user** (empty UPN)
- 60 devices still on only 8 GB RAM
- 1 device with basically no storage left
Perfect for Win11 readiness checks, post-EOS cleanup, and planning the next refresh cycle.
The FREE Intune Dashboard gives you the full picture + CSV export ready for Entra group imports in one click.
@MSIntune #Intune
🚨 Anthropic just showed a 27-minute workshop on how to actually do prompts for Claude.
Taught by the people who built it.
Free. No registration. No paywall.
I've seen $300 courses that don't cover what they teach in the first 8 minutes.
Watch it and bookmark it now.
I wish somebody would have told me before! 😩
111 devices show as “Encrypted” in Intune…
…yet only 106 recovery keys are actually escrowed in Entra.
That GAP of 6?
Those 6 devices are fully encrypted with NO recovery key backed up.
Drive fails. User calls helpdesk. You have nothing.
The FREE Intune Dashboard shows you exactly which ones — before the audit finds them first.
@MSIntune #Intune #BitLocker
You can remove preinstalled Microsoft Store apps such as Clipchamp, Xbox, Weather, and Feedback Hub. Follow our guide to learn more:
https://t.co/ag8YAaQSle
#MSIntune#Microsoft#Apps#SCDudes
New Update | KB37864969 is the second hotfix rollup released for #ConfigMgr version 2509 that supersedes the previously released KB 36949461 update. https://t.co/0PwFK6wgGf
Entra Hardening Tip #9 🔐
Don’t use client secrets for app authentication.
Use this decision tree when a developer or vendor asks for an app registration to be created in your tenant. 👇
1/14
Should I assign my permissions to my Managed Identity, or should I assign them to an App Registration first? https://t.co/QmX7lg8f0g ❔
Assigning Graph API permissions to a Managed Identity can only be done through the Graph API itself, which requires an App Registration. Whereas federating your Managed Identity with an App Registration, then assigning Graph API permissions to that, adds additional risk and operational overhead, but the permissions can be managed from the Entra admin center.
Which do you prefer?