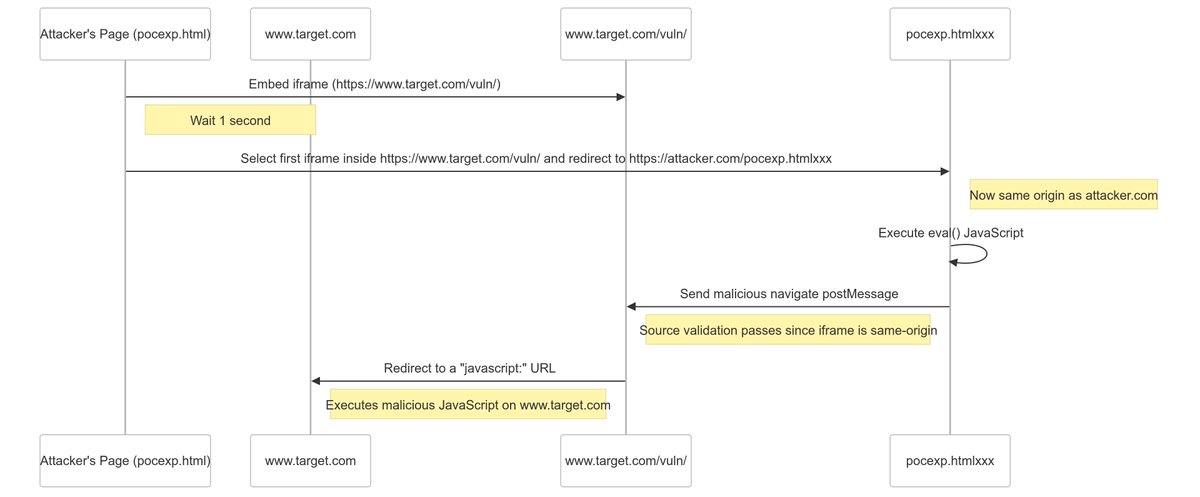
Found a page with an onmessage tracker that redirects users without scheme validation. It verified messages from a trusted iframe, but missing X-Frame-Options let me iframe the target page, swap the trusted iframe’s location inside it with mine, bypass validation, and achieve XSS
very pleased to announce the release of my new article based on my research that led to CVE-2024-46982 titled:
Next.js, cache, and chains: the stale elixir
https://t.co/UFndJxNYLI
note: does not cover the latest findings shared in my recent posts
enjoy reading;
Use google dork "site:https://t.co/hv8LXswBsa"
you will find tons of exposed invitation links to workspaces.
you can join these workspaces even if the option "Require admin approval" is on.
because these leaked invites are made by the admins it Self