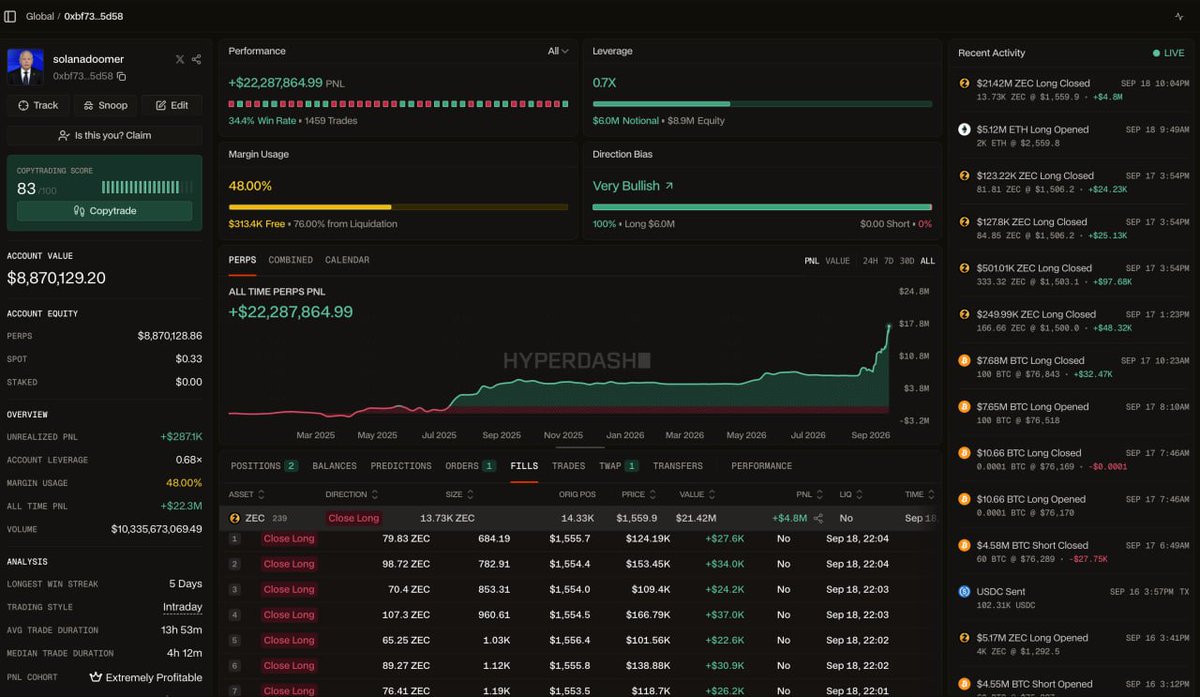
After closing his ZEC long earlier this week, @solanadoomer1 went long $35M of ETH and is currently up $2.2M on his position.
He is currently the #1 top trader globally by realized pnl this month at $12.3M.
https://t.co/eCQ9wADssm
@solanadoomer1 cut $21.42M of his ZEC long, realizing $4.8M of profit. He is still long $1M with an unrealized gain of $200k.
His total lifetime profit is now $22.3M on Hyperliquid.
https://t.co/eCQ9wADssm
@CL207@AndyHazelton Funny to see you responding to a meteorologist. This image is for forecast hour 126, which for this run is valid Friday, July 31 at 12:00 UTC.
@WazzCrypto@big_duca Can wait for Andrew for an official response but we’re already working with Groomlake to beef everything up. Details on what was leaked will be released eventually.
Hello friends,
On the evening of April 1st, Awaken was attacked.
The whole day was a tough day for crypto.
And that evening, while I was at dinner with my fiancee’s family celebrating our engagement, our alarms went off.
We started investigating. And noticed an attacker had gained unauthorized access to parts of our system.
Since discovering the attack, our team has worked with third-party forensic experts to confirm containment and document the scope of the incident.
Because this investigation is ongoing, we will notify users over email of the details.
But I want to share that during the attack, the attacker stole information that will likely be used in social engineering and phishing attempts.
So please be vigilant. We put suggestions in our email, and my personal email is below.
A lot of people are concerned about 1099-DAs.
In general, we minimize the amount of user data we store. These files specifically are stored securely (signed access) and encrypted at rest. At this time, our investigation has found no evidence that these files were accessed.
While this attack was happening, I avoided posting on X. It felt weird bc I like to overshare.
Tbh, I was a bit scared.
I know that right now, whoever attacked us is reading this message.
Ultimately, it’s our responsibility to do everything in our power to make sure this does not happen again.
Like any crypto company, we expect to continue being targeted. So we are redoubling our security efforts.
We started working with the chads @0xGroomLake on penetration testing and opsec.
We work really hard to build a great product bc our team loves crypto. We really fucking care.
And we aren’t going anywhere.
If you have specific questions, my email is: [email protected].