"Who TryHackMe is" (https://t.co/jMm73cpQ0M).
We have quite an intense culture, it's not for everyone - but it means everyone here is so talented and hard working.
This video from our TA team captures just how impressive our people are. When I look back at what we've built and achieved this year, no company our size comes close.
If you clock watch at work, don't love Mondays, and finish at 5 on the dot, you're in the wrong job. If what you watch excites you, we're hiring (link in comments).
🚨 Yesterday, PHP2Shell made headlines. Today, we're already teaching you how to exploit it. Yeah, we're THAT fast⚡ Two critical PHP vulnerabilities. 9.2 CVSS. Unauthenticated RCE.
And you can already exploit the chain, bypass ASLR, and pop a shell in our latest recent threat room.
Hackers don't wait. Neither do we 🟢 Go Get hands-on: https://t.co/76TcpTLxpr
Your manager might finally be useful 👀Get them to join our FREE Blue Team readiness webinar and score 2 BONUS prize tickets in our Strange & Unusual CTF! 🗓️ 26 Oct | 3 PM GMT
They learn. You get more chances to win. 🤝
🔗 Save their seat! https://t.co/ODqcUbntgq
We’re hosting a live webinar next Thursday, 22nd Oct at 9:00 AM EDT / 2:00 PM BST, on Hacking & Securing Apps Where Devs Ship AI Written Code.
@springjben and @KevalJagani1 will cover the vulnerabilities AI tends to introduce, why it happens, and how to secure them.
Register now, link in comment 👇
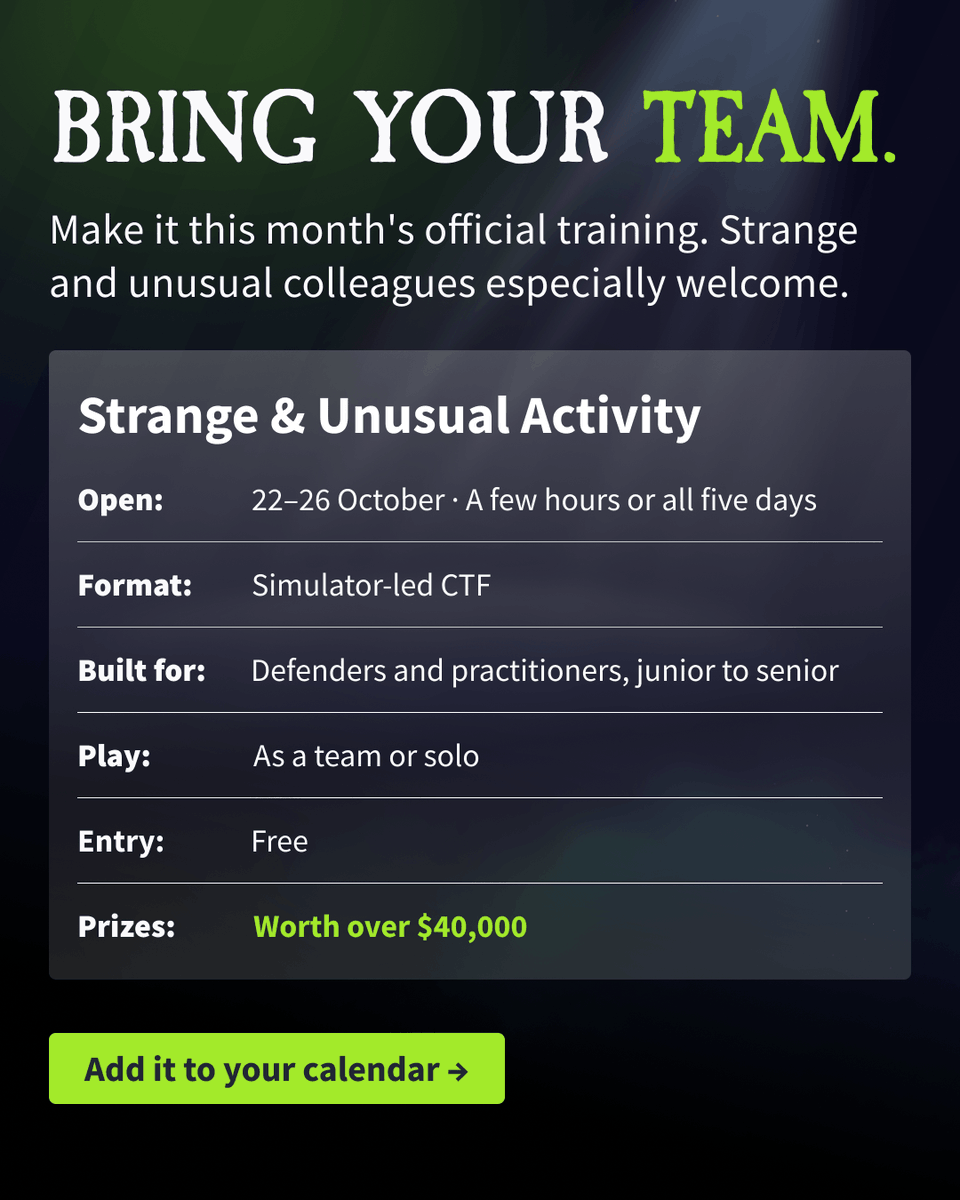
🚨 BLUE TEAMERS, THIS ONE'S FOR YOU 🚨 A NEW & EXCLUSIVE Blue Team CTF is coming to TryHackMe. Four simulators. Five days. Over $40,000 in prizes.
And absolutely nowhere to hide 😈
Tag your dream team below and join in ▶️ https://t.co/BXXS99Cx7q
Jira integration is now live on NoScope.
Every finding now syncs directly to the Jira dashboard, with severity, evidence and remediation steps attached to each ticket.
We tested JEV and Grok 4.7 on 200 cases to see how well each catches harmful agent actions before they run. JEV answered in 324ms vs 16.44s for Grok, at about $0.084 vs $3.79 per 1,000 checks. Grok was more accurate, and the full numbers are in the post.
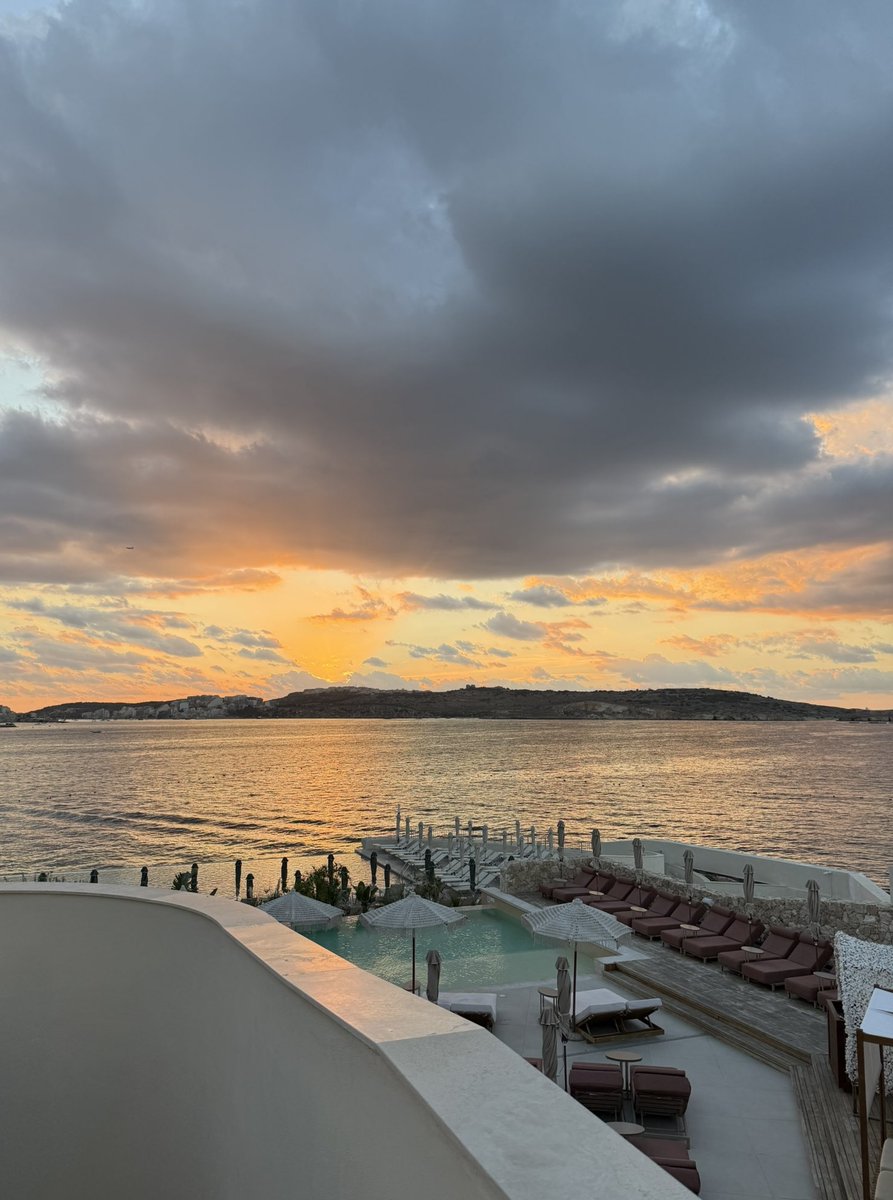
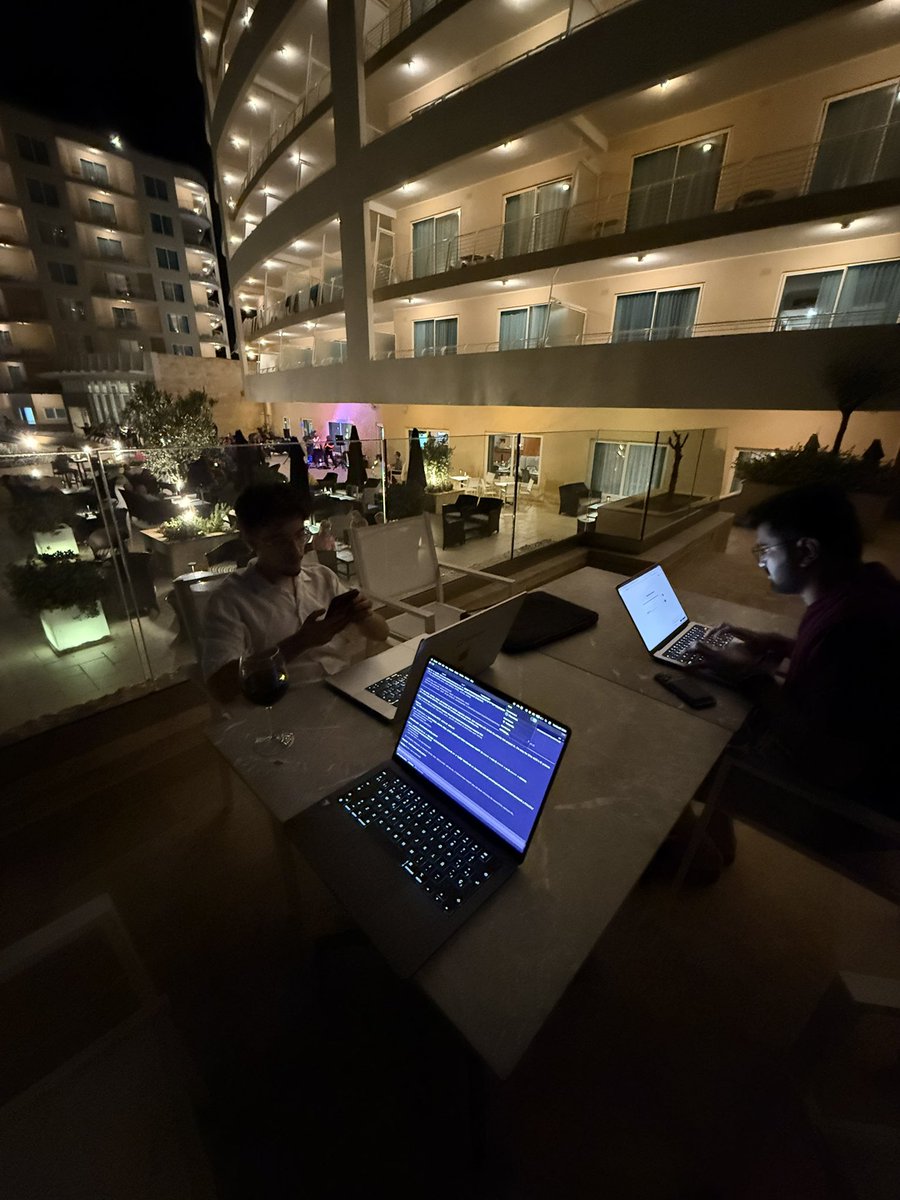
Just back from an amazing work trip in Malta with the @trynoscope and @tryhackme team.
We had deep convos on cyber in 5y, how AI changes it, and getting our customers ready for that shift
We had some intense days (and nights) building. We're dropping some insane research soon!
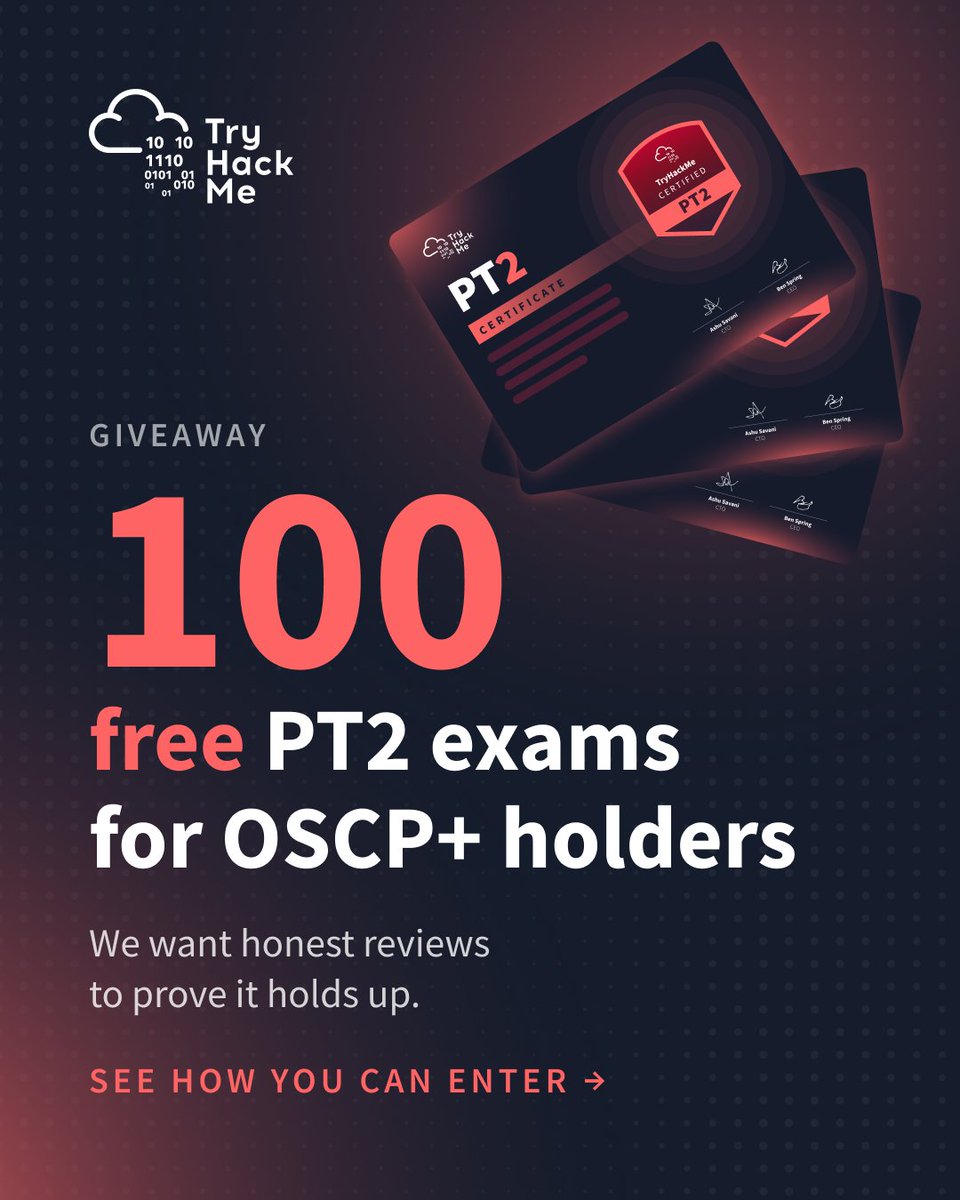
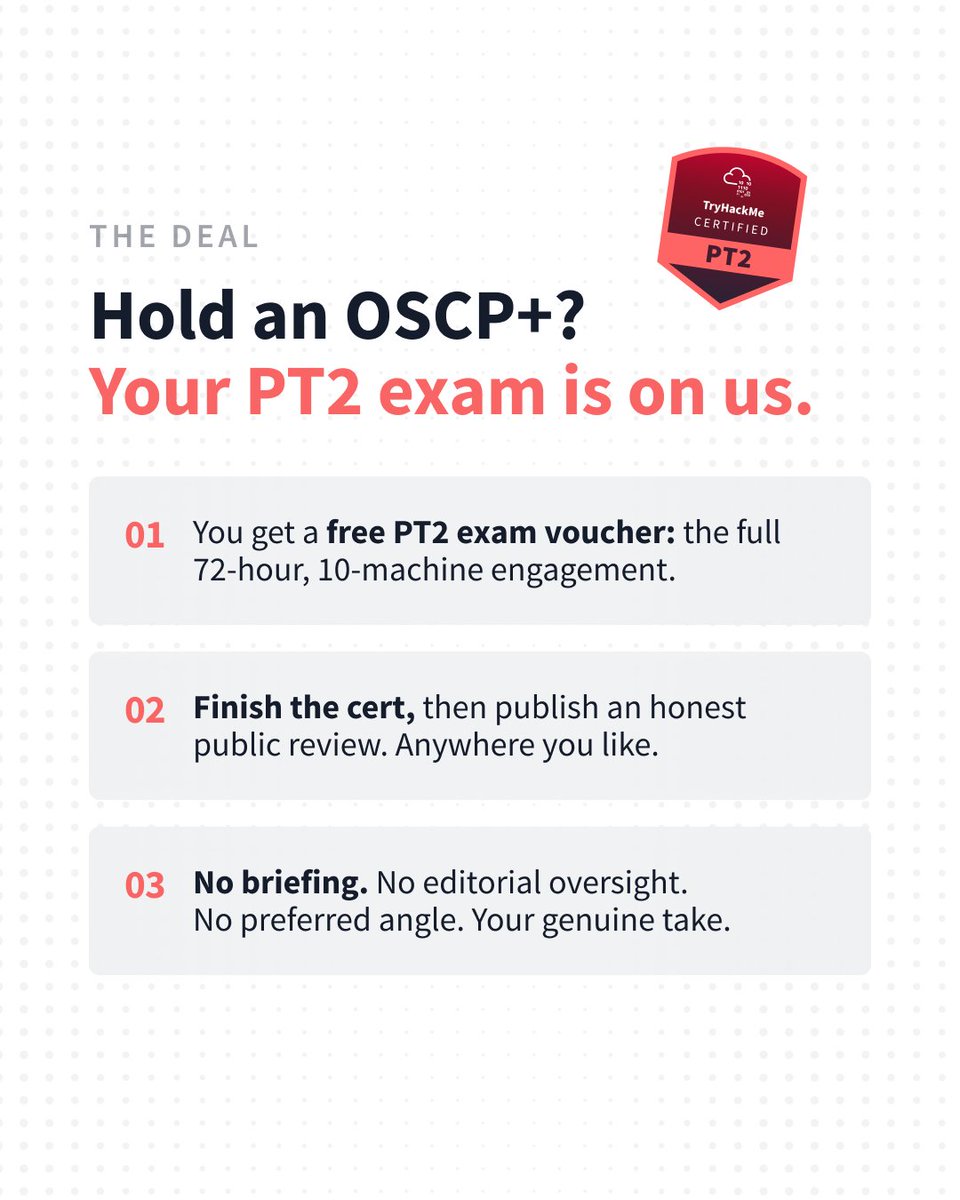
Hold an OSCP+? Your PT2 exam is on us 🔓 We're giving away 100 free exam vouchers to certified pentesters and all we ask for is an honest public review.
Fill in the form to enter. Share this with an OSCP+ holder who needs to know 👊 ▶️ https://t.co/KqRYO6mIKp
September 20 at 23:59 PM (UK time)
Salesforce just listed SAL1 (TryHackMe’s entry level defensive certification) as a recognised cert for their Associate Incident Responder role. That's not just a milestone for TryHackMe. It's proof that the skills you're building here are the ones the industry is hiring for. If you're working toward SAL1, this is your sign to keep going. Go check it out 👉 https://t.co/vhwPYaX3FV
Earn $5000+ & build your personal brand with TryHackMe's 8 million users by teaching live classes.
We're looking for industry practitioners to run live classes on TryHackMe. These are small, instructor-led sessions (30-45 people) that run from a few hours to a multi-week programme. You run the class with TryHackMe and we handle promotion, charging $200-$850 per seat (depending on topic and audience).
TryHackMe's audience consists of Fortune 500 companies, governments, and aspiring practitioners. There's existing demand for live classes, and we want to partner with experts to deliver them.
Whats in it for you:
💰 Earn a minimum of $5k per class
🎤 Build your personal brand across TryHackMe's 8M global security community
🪖 Share your war stories and shape other practitioners' careers
Who we're looking for:
▪️ Practitioners, managers, CISOs, or anything in between
▪️ People with real war stories worth sharing
▪️ (Optional) Experience at a well-known company
If you're interested, apply here: https://t.co/12zoR7tcFm
Know someone who'd make a great instructor? Tag them.
New session alert!
⚡ Fight Fire With Fire: AI Pentesting in 30 Min
📅 Sep 8 | Free | Lucas Romano (SOC Manager @ Cequence, Previously Cisco and NSA)
Register free 👉 https://t.co/20tswMkkFP
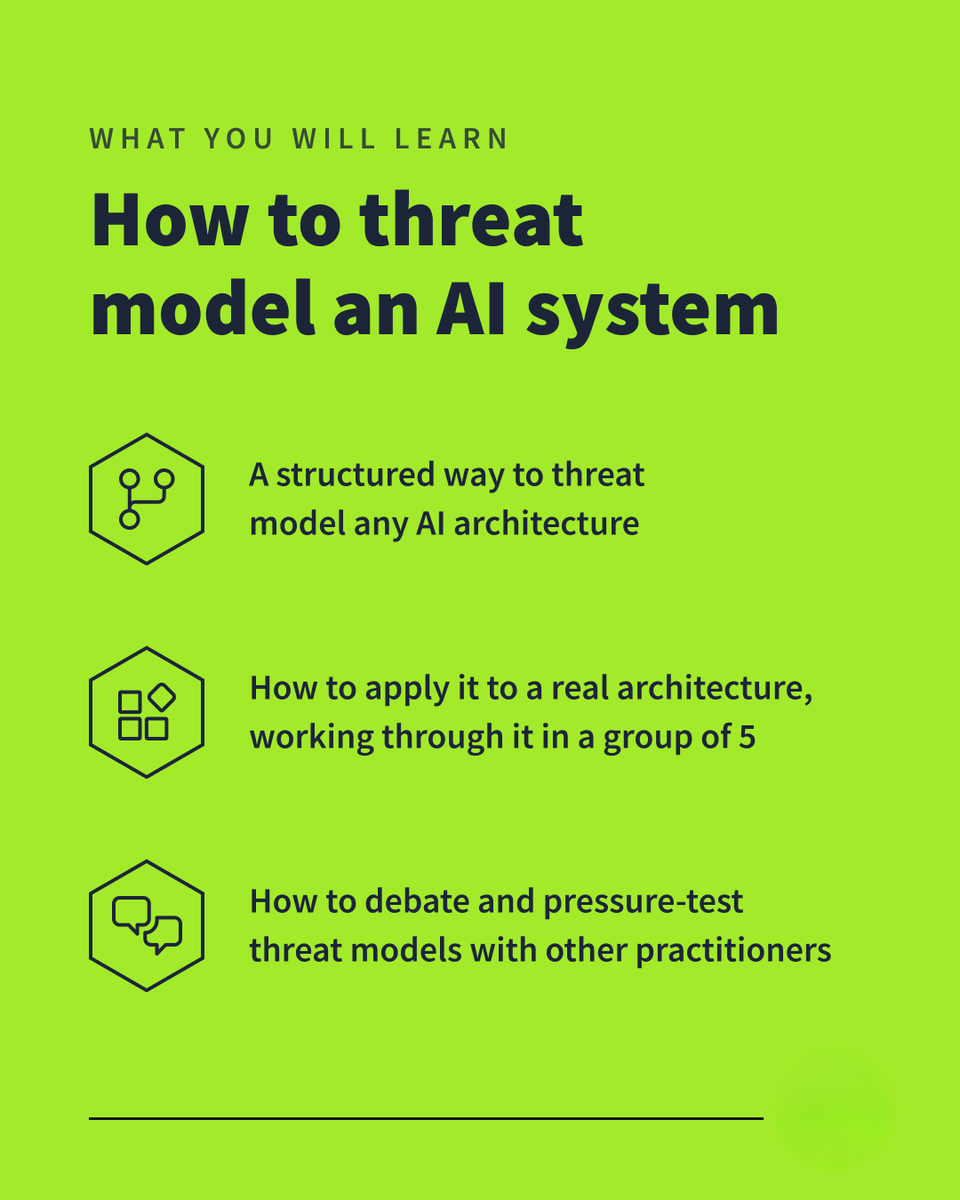
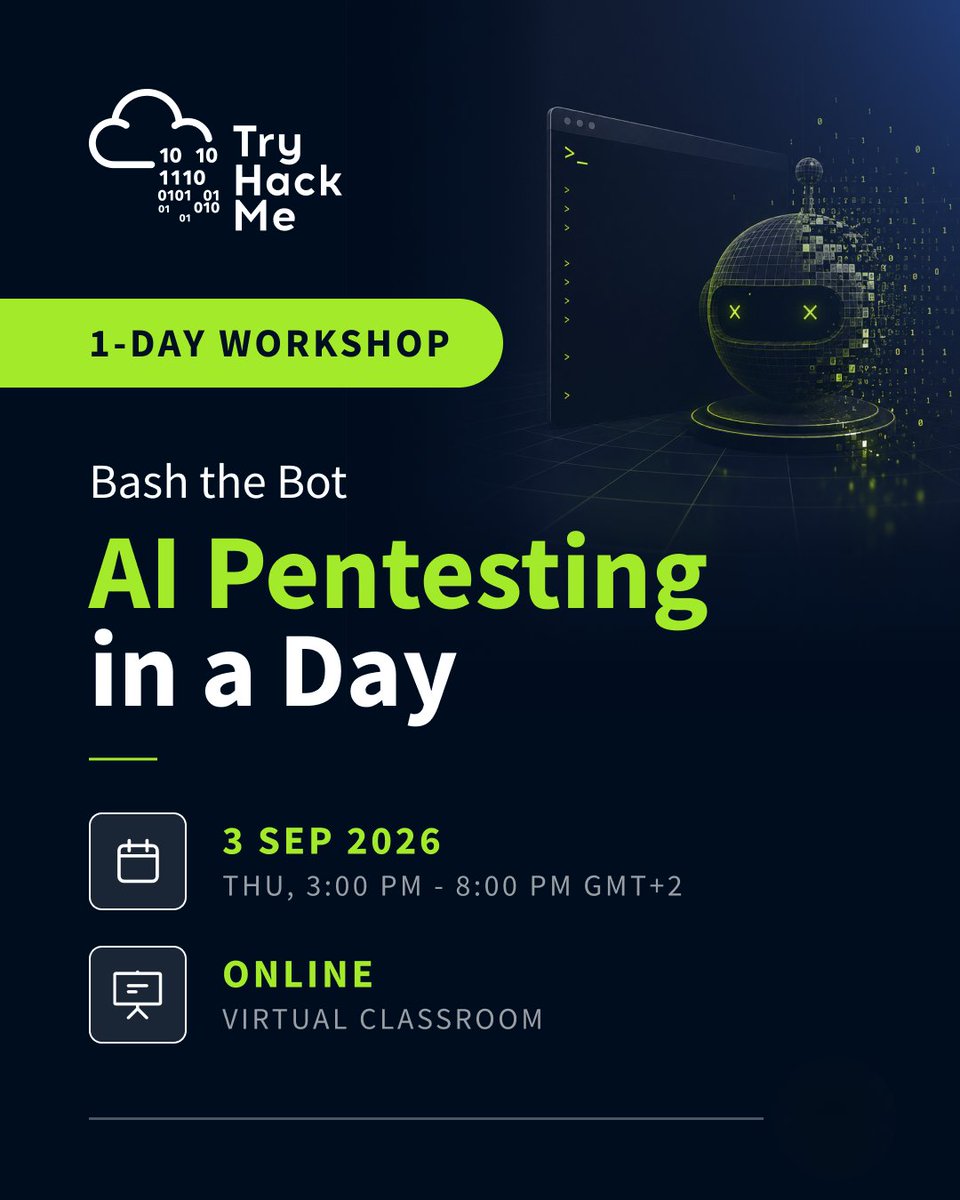
AI pentesting isn't just prompt injection. You can learn more about AI security through our Live 1-Day Workshop, "Bash the Bot: AI Pentesting in a Day", taught by:
🧠 Max Robertson; built TryHackMe's AI Security Learning Path & AI1 cert
🧠 Christian Urcuqui; TryHackMe's content engineer & Cyber AI researcher
Sep 3, 2026 · Online on Zoom
https://t.co/SvUSkjjXMM
Swipe through for more info➡️
@IamRenganathan There is no scope to our engagements. Tradition pentests have a scope (due to time limitations humans have), ours has deep coverage and can cover almost the entire scope of the app. There is quite literally no scope.
A recent YC startup spent 250k on a domain. I was slightly shocked. But when I asked how much they raised after YC, the answer was 6.5m. So 1/26 of their round. This is the time we live in; one shocking number counterbalances the other.
We asked a Gitea server for a token we had no business getting.
It said 200 OK.
Here's how NoScope's AI agent found a 4-year-old flaw that exposed private container images on ~30,000 servers 🧵