You can silence Indian citizens by threatening them, but the genie has left the bottle and CEO of a $100bn company is talking about it.
Some introspection would be welcome.
Almost 70% of the web compromised, humans and AI working together to fix it, and literally nobody in my everyday life has a clue what I'm talking about.
The fun fact about the eMudhra certificate leak is that the numbers were so low that only an AI or a flawed/test script would have found them. No sane human would have thought that a fellow human could have done something that stupid.
Three incidents happened today:-
1. SBI data breach
2. eMudra fucked up with 60-70% of the internet/IoT devices and many many systems
3. Rajasthan government DoIT&C data is on sale by some threat actor
I said it, we are a naked nation in terms of cyber security. Babus and illiterate politicians can’t handle and secure the digital India with part time ministry for IT. Most of them are cyber illiterates, they don’t even know the C of cybersecurity. Do you really think they will protect our data and India’s digital sovereignty?
The only CYBER department active is cyber police of every state in filing FIRs on social media posts. That’s we!
cyber security month didn’t end well this time. 😭
I never wanted to say this but we have reported vulnerabilities in hundreds of companies in India.
Almost all the companies rejected it, got defensive and now i’m so afraid the exploits are just left open. This is btw the biggest companies in India
The first rule of this government's response to any crisis unfolding in our great country, is to lash out at the people who exposed the crisis in the most bitter and spiteful way. They're like children, except with far too much power and responsibility.
Fear mongering? All the vendors are fixing this and we are working round the clock to ensure all our systems are safe! Whoever tweeted or authorized this tweet should be fired! Indian Government IT ministry is good for nothing when it comes to cybersecurity
Gross incompetency from Indian certificate authority eMudhra.
You had one job: generate a 384 bit private keys and instead you used: 4, 56, 66, 115, 155, 156, 230, and 237.
This allows attackers to issue certificates for any websites.
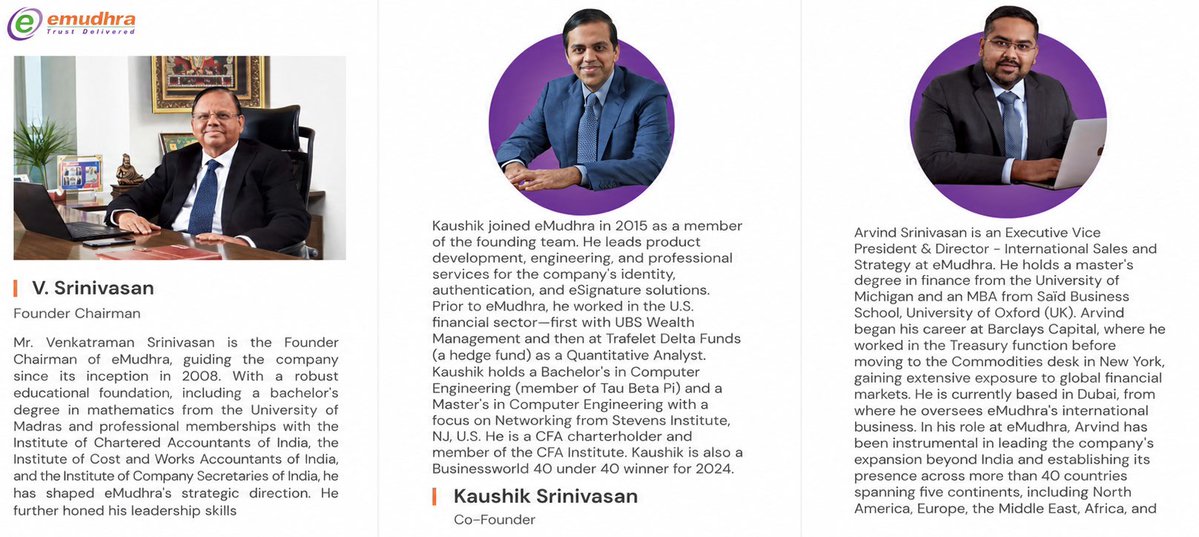
Embarrassing that it’s a family business run by largely computer illiterate people. Only 1 of the 3 have a remotely computer-related background and even they never actually worked a technical job in their life. If you look at the LinkedIn, their tech team is young, from tier 3 education and paid sort of bottom barrel.
Imagine how many attacks you can design with AI given the existence of this genre of gross negligence.
@IntCyberDigest@grok how does this affect a person trying to access a website or trying to make online transactions. What even is this key and how does it affect a regular user. Explain in the most basic of way (for a non cs non technical person).