Unrecovered Binance funds could finance North Korea’s activities, our Chief Intelligence Officer Roman Bieda told CBS News. “Freezing assets and recovering them are two very different things.” https://t.co/2xh45J3V2A
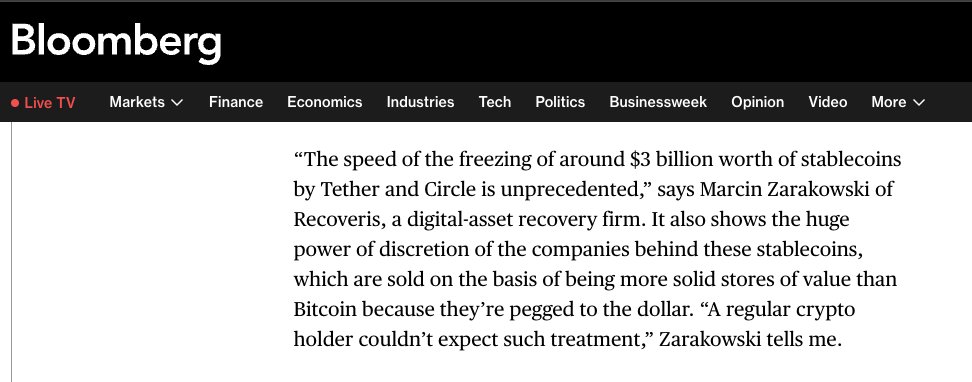
Our CEO comments the Binance hack for Bloomberg:
“The speed of the freezing of around $3 billion worth of stablecoins by Tether and Circle is unprecedented. (...) A regular crypto holder couldn’t expect such treatment”.
Link in reply.
The @binance hack highlights why tracing and coordination must work together. Locating stolen funds is one step. Freezing them requires evidence to reach exchanges, token issuers and law enforcement in time. Does your team know who to call?
Hunting Conti’s Shadow
How I found what the FBI, the NSA and an army of researchers couldn't
Imagine you’re hunting the most disciplined cybercriminal group in the world — Conti.
These guys wrote the textbooks on OPSEC. Impeccable digital hygiene. In 2022, all their internal work chats (hundreds of thousands of messages) leaked online. Conti just laughed it off, then encrypted an entire country — Costa Rica — changed their signboard and kept working.
Intelligence services, analysts and independent researchers spent years looking for a single lead. Nothing. The FBI, admitting defeat, offered a $10 million reward for the names of the ringleaders. Three years of gold rush, thousands of analysts, endless reports — zero results.
But I decided to take the challenge. This is the story of how I, step by step, uncovered and exposed the connections, flights and identities of key figures in the group using a leak of the FSB border-control database "Granitsa”, fragments of Conti chat data, stylometry and pure OSINT. These anonymous actors had no faces — they only cast shadows. I turned on the spotlight, and their own shadows caught up with them. That’s how the hackers got names.
---
The first trace — Target and his travel companions
They weren’t tourists flying to Dubai
It all began with Alexey Kurashov. His name surfaced after analysing thousands of leads that pointed to Moscow-City. There was no smoking-gun evidence — only analysis of communication style in Conti chats that suggested he was “Target,” a key figure in the group. Only stylometry and instinct. I decided to act directly — I messaged him on Telegram. After a short exchange I realised — yes, it was him. The first key participant found. But irrefutable evidence was still needed.
I collected data on every time Kurashov crossed a border over the last ten years. Dozens of flights, hundreds of travel companions. Gradually a network of his closest contacts emerged — people he flew with again and again. Trips to the UAE since 2021 stood out in particular. These weren’t random vacations: the same faces, flights back and forth like clockwork. As if the hackers were operating to a timetable. But why?
I decided to dig deeper.
---
Timeline: mapping their secrets
To understand how this network operated I built a combined visual timeline of Kurashov’s flights and those of his travel companions. Each flight was a mosaic piece revealing their movements. (On the chart, flights to the UAE are marked yellow; all other countries are green.) At the same time I dove into the Conti chats — and began comparing. All participants observed strict conspiracy and didn’t even trust one another.
But systematic work paid off. In a Rocket chat I found a message from user RED — an account Target used for only a couple of hours:
2021-10-12 15:35:49 — red: "we are sending the guys early in the morning"
Seems innocuous at first glance. But the flight data told more: on 13 October 2021, on SU-520 to Dubai, Marat Nurtdinov and Oleg Fakeev — close friends of Kurashov — departed. A coincidence? Hardly.
This was the first trace leading from the digital world into the real one.
---
The line that led me to Conti’s Dubai office
Another clue surfaced in Jabber. A user called Bloodrush (who I established was Target through style analysis and fact-checking) wrote:
13.10.2021: “I don’t have access to the online wallet until Friday, I only have clean crypto.”
And on 14 October — guess what?
Kurashov flies to Dubai!
On the same SU-520 flight with him — a certain Vladimir Kvitko.
Bloodrush disappears from the network and reappears on 15 October.
Friday. Everything lined up perfectly.
💥 Next I’ll tell you who Vladimir Kvitko is, and how a single small OPSEC mistake erased a decade of his supposedly flawless operational discipline.
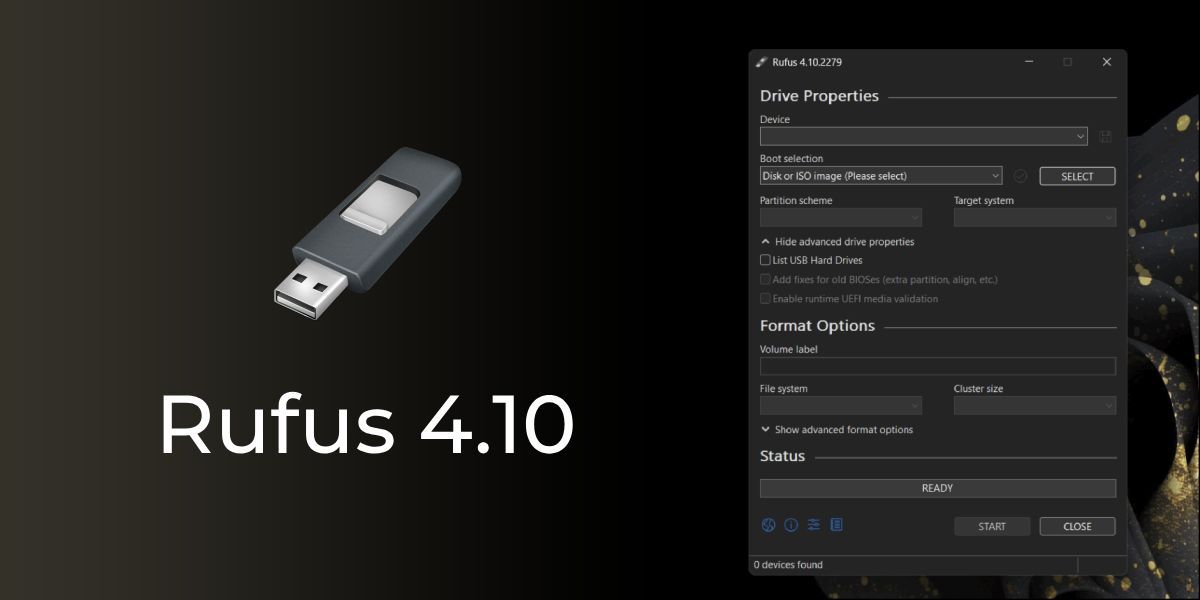
Rufus 4.10 is out and finally brings a dark mode, updates Windows UEFI CA 2023 for Secure Boot, adds support for saving an existing drive to ISO, improves Linux Mint persistence, enhances error reporting when saving to VHD/VHDX, and more.
https://t.co/WKJNY5EOVB
Urgent! Just by receiving an image in your iPhone or Mac, your device can be FULLY compromised. Update your devices ASAP!
Also recommended:
• Disable auto download of images in Telegram;
• Disable the auto download of images in WhatsApp;
• Disable iMessage for complete or, if you wanna keep it, enable Lockdown mode.
Cybercriminals are using USB infections for coinmining operations.
This blog post unpacks their multi-stage attack, including DLL side-loading, process injection, and using PostgreSQL as C2.
Learn more: https://t.co/SLJ1lIMyza
ChatGPT quietly scrubbed today nearly 50,000 shared conversations from Google's index after our investigation. They thought they'd solved the problem. They were wrong. (1/5)
Did you know that Super+i opens the Settings activity on Android?
In OTG mode (with `scrcpy --otg`), this can allow you to enable USB debugging with only the keyboard! (in theory)
https://t.co/o1zafVqqdJ
Sono orgoglioso di presentare l'𝗔𝗱𝘃𝗮𝗻𝗰𝗲𝗱 𝗪𝗲𝗯 𝗙𝗼𝗿𝗲𝗻𝘀𝗶𝗰𝘀 𝗖���𝘂𝗿𝘀𝗲, che consentirà di conseguire la 𝗖𝗪𝗙𝗘 = 𝗖𝗲𝗿𝘁𝗶𝗳𝗶𝗲𝗱 𝗪𝗲𝗯 𝗙𝗼𝗿𝗲𝗻𝘀𝗶𝗰 𝗘𝘅𝗽𝗲𝗿𝘁.
https://t.co/2ajhwaikWe
Qui il link per accedere al Corso:
https://t.co/oFK58pryeb
PANO - Advanced OSINT Investigation Platform Combining Graph Visualization, Timeline Analysis, And AI Assistance To Uncover Hidden Connections In Data https://t.co/TdnzJsV7pU
NEW: We found a sneaky Android phone stalkerware app that requires a password to deactivate or uninstall.
Worse, the password is set by whoever planted the app.
The good news is there's a way to uninstall the spyware without knowing the password.
https://t.co/FX2gWM91hy