The alert isn't a call to action anymore. It's a receipt.
Stream already found it, stopped it and fixed it.
Autonomous production defense.
So you can do other… stuff.
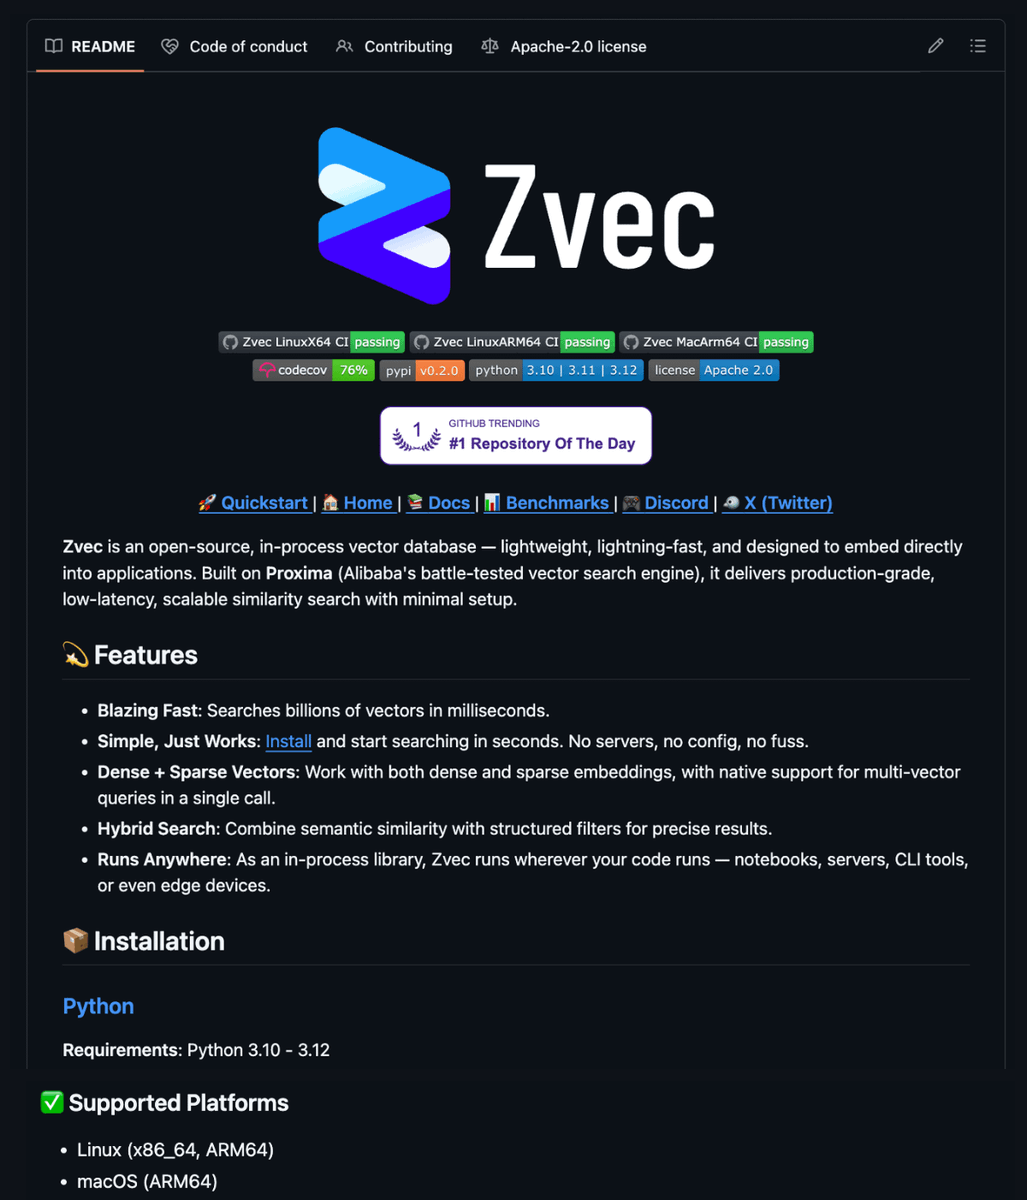
🚨 Alibaba just quietly dropped a vector database that destroys Pinecone, Chroma, and Weaviate.
It's called Zvec and it runs directly inside your application no server, no config, no infrastructure costs.
No Docker. No cloud bills. No DevOps nightmare.
Built on Proxima, Alibaba's battle-tested vector search engine powering their own production systems at scale.
The numbers don't lie:
→ Searches billions of vectors in milliseconds
→ pip install zvec and you're searching in under 60 seconds
→ Dense + sparse vectors + hybrid search in a single call
And it runs everywhere:
→ Notebooks
→ Servers
→ Edge devices
→ CLI tools
100% Opensource. Apache 2.0 license.
This is the vector DB the RAG community has been waiting for production-grade performance without the production-grade headache.
Link in the first comment 👇
Last quarter I rolled out Microsoft Copilot to 4,000 employees.
$30 per seat per month.
$1.4 million annually.
I called it "digital transformation."
The board loved that phrase.
They approved it in eleven minutes.
No one asked what it would actually do.
Including me.
I told everyone it would "10x productivity."
That's not a real number.
But it sounds like one.
HR asked how we'd measure the 10x.
I said we'd "leverage analytics dashboards."
They stopped asking.
Three months later I checked the usage reports.
47 people had opened it.
12 had used it more than once.
One of them was me.
I used it to summarize an email I could have read in 30 seconds.
It took 45 seconds.
Plus the time it took to fix the hallucinations.
But I called it a "pilot success."
Success means the pilot didn't visibly fail.
The CFO asked about ROI.
I showed him a graph.
The graph went up and to the right.
It measured "AI enablement."
I made that metric up.
He nodded approvingly.
We're "AI-enabled" now.
I don't know what that means.
But it's in our investor deck.
A senior developer asked why we didn't use Claude or ChatGPT.
I said we needed "enterprise-grade security."
He asked what that meant.
I said "compliance."
He asked which compliance.
I said "all of them."
He looked skeptical.
I scheduled him for a "career development conversation."
He stopped asking questions.
Microsoft sent a case study team.
They wanted to feature us as a success story.
I told them we "saved 40,000 hours."
I calculated that number by multiplying employees by a number I made up.
They didn't verify it.
They never do.
Now we're on Microsoft's website.
"Global enterprise achieves 40,000 hours of productivity gains with Copilot."
The CEO shared it on LinkedIn.
He got 3,000 likes.
He's never used Copilot.
None of the executives have.
We have an exemption.
"Strategic focus requires minimal digital distraction."
I wrote that policy.
The licenses renew next month.
I'm requesting an expansion.
5,000 more seats.
We haven't used the first 4,000.
But this time we'll "drive adoption."
Adoption means mandatory training.
Training means a 45-minute webinar no one watches.
But completion will be tracked.
Completion is a metric.
Metrics go in dashboards.
Dashboards go in board presentations.
Board presentations get me promoted.
I'll be SVP by Q3.
I still don't know what Copilot does.
But I know what it's for.
It's for showing we're "investing in AI."
Investment means spending.
Spending means commitment.
Commitment means we're serious about the future.
The future is whatever I say it is.
As long as the graph goes up and to the right.
Let me introduce you to my most novel and oldest technique to verify if sites behind CDN are hosted in Inside Iran or not. Works most of the time. I call it the BOOBS CHECK.
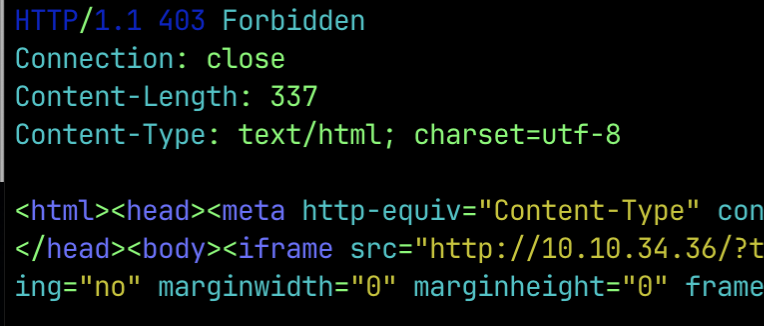
curl -i https://domain/boobs.jpg
If your response is a 403 with 10.10.34.x IP in body, you're landing inside IR. Result of basic censorship filtering applied on traffic.
@IRIran_Military lol they are actually going the opposite way around coming from all over Europe to Cyprus and taking a boat to Israel as there are no flights..
Modern attackers don’t drop malware. They rewrite how your cloud works.
They exploit IAM roles, tweak network configs, and silently progress across accounts.
👉 Learn why the Cloud SOC Paradox is leaving security teams behind in our latest report: https://t.co/kHsbweAgRN
Most security tools see the cloud. But they don’t understand it.
👉 In our latest blog, we break down how Stream connects the dots across identity, configuration, and workload activity to reveal full attack paths.
Read the full post here: https://t.co/9v6eEjHqhz
Join Synack and Stream at the Viva la Festa Party for cocktail and delicious lobster and ribeye tacos at Fogo de Chão, just 98 steps from the Moscone Center.
Register for the party here: https://t.co/eEM8YZDkP1
#RSAC#RSAConference#VivaLaFesta
We just added real-time firewall context to Stream’s Cloud Detection & Response.
NGFW & WAF rules across @PaloAltoNtwks, @Cloudflare, and cloud-native WAFs are now correlated with real-time cloud exposure.
Read more in our latest blog by Stream's CTO: https://t.co/iYuLZnsOzF
We're excited to share that Stream now offers workload observability into our real-time Cloud Detection & Response platform with our new integration with Tetragon's eBPF agent.
Read more in our latest blog by @stav_sitni: https://t.co/Eqeh1QG5ie
#CDR#CloudSecurity#eBPF#K8s
The tj-actions/changed-files breach is one of the most widespread supply chain attacks we’ve seen.
Full details on what you need to know and how to respond in our latest blog by Or Shoshani ⬇️
🔗 https://t.co/BDJpYzfv5E
#GitHub#RenovateBot#CVE202530066#CICD#CloudSecurity