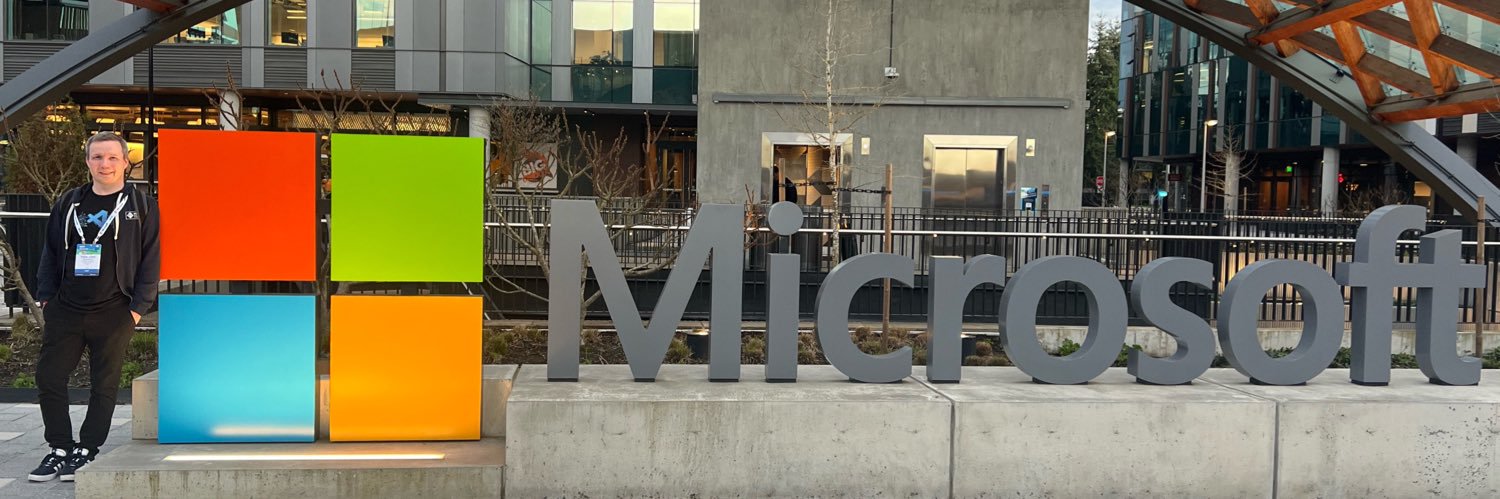
It’s official now. I’ll be joining @troyhunt and @Charlotte_Hunt_ later this summer, working full time for @haveibeenpwned!Really excited about this awesome opportunity and I’m very much looking forward to it! 🥳
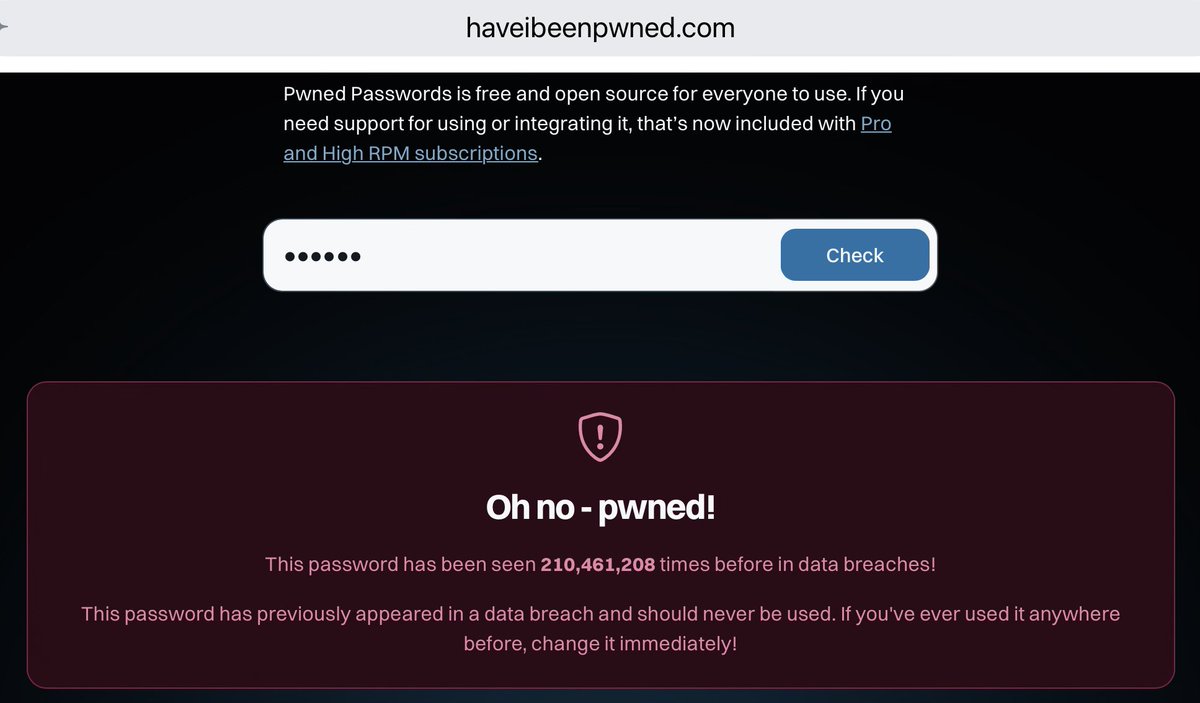
New breach: Europol and partners dismantled infrastructure supporting the CastleRAT remote access trojan this week, providing HIBP with 180k email addresses and 893k unique passwords seen 3M times. 41% of addresses were already in @haveibeenpwned. More: https://t.co/bP4WuhRAxM
We've found 15,579 websites serving malicious JavaScript, with an estimated 135 MILLION visits every month. 🤯
We know they're infected, and we have the evidence, but how on Earth do we notify them all?!
We need help from the security community 👇
https://t.co/RRSEhO3tEh
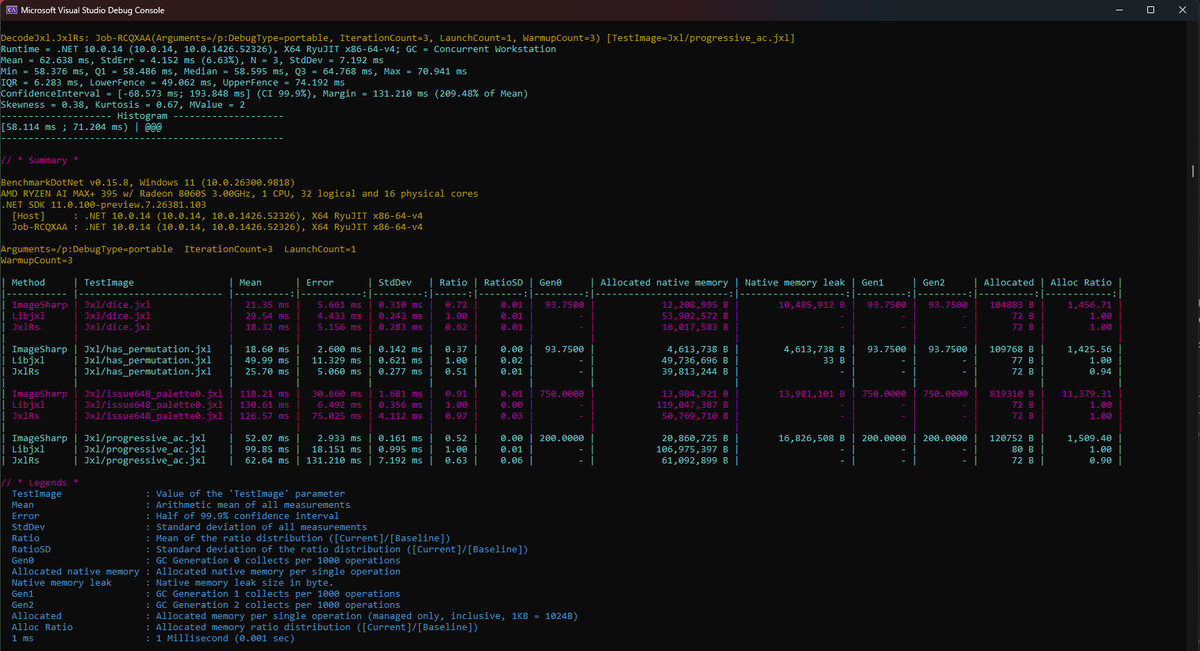
Current @SixLabors ImageSharp (C#) JPEXL decoder benchmarks vs libjxl (C) and jxl-rs (Rust).
Faster for 3/4 benchmarks and uses less memory for 4/4. BenchmarkDotNet sees native memory pooling as a leak but it's not (obvs cos pooling).
#dotnet FTW
@dinodaizovi Having used a “black box” HSM with limited documentation on a few occasions I think you’d have to make an effort or not know what you are doing to have a proper HSM generate bad keys like this. So either this is deliberate misuse or incompetence, both not fit for a proper CA
Ok, I'm a former MS MVP and a pretty big fan of a lot of stuff Microsoft does, but this is just silly at this point. Can we ease up on the Bing upselling and not just make up BS reasons for the average user to use Bing instead of something else they prefer.
If passkeys have people this upset, wait until they hear about DBSC 🤣
Your session is hardware bound to your device...
Somewhere, a cookie just found out it can be device-bound 🍪🔐
https://t.co/WJUR8i9yLm
@kellabyte We make pretty good use of Azure SQL for @haveibeenpwned and with some recent changes we made, we have pretty damn good perf as well :) it’s not the cheapest though but we’re also working on reducing that while improving perf and minimizing disruptions at the same time
Quite a few people have sent me the "Passkeys are a trap. Do not use them." post on Substack.
The post recommends people abandon passkeys and stick to passwords + TOTP, citing what appears to be concerns with attestation as the primary reason.
I’ve written a rebuttal as this is really dangerous advice and it's based on some incorrect technical claims.
https://t.co/XULAcwyi1A
Quite a few people have sent me the "Passkeys are a trap. Do not use them." post on Substack.
The post recommends people abandon passkeys and stick to passwords + TOTP, citing what appears to be concerns with attestation as the primary reason.
I’ve written a rebuttal as this is really dangerous advice and it's based on some incorrect technical claims.
https://t.co/XULAcwyi1A