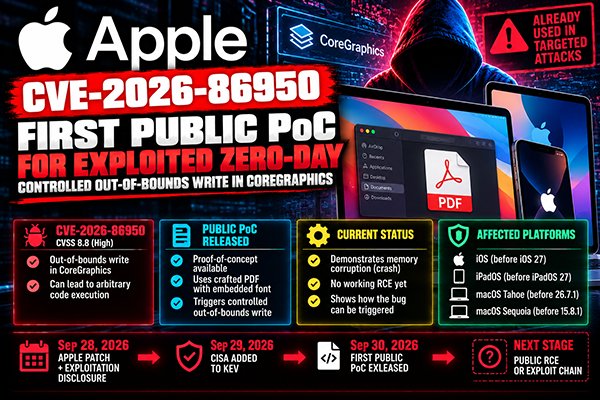
🔴 Apple CVE-2026-86950 — first public PoC released
Researchers reproduced the CoreGraphics out-of-bounds write with a crafted PDF. The PoC triggers memory corruption, but does not yet a
https://t.co/kEUO7RnmLH
#CVE#CVE202686950#Apple#CoreGraphics#PoC#ZeroDay#CyberSecurity
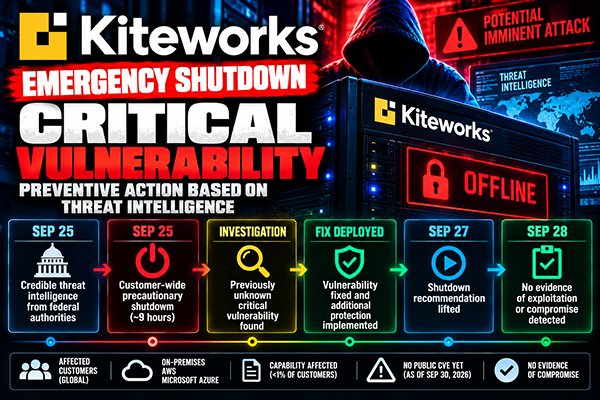
🟠 Kiteworks took customer systems offline after receiving credible federal threat intelligence.
During the shutdown, a previously unknown critical vulnerability was found and fixed. Kiteworks says
https://t.co/WdXu6pyzbq
#Kiteworks#CyberSecurity#ThreatIntel#ZeroDay#InfoSec
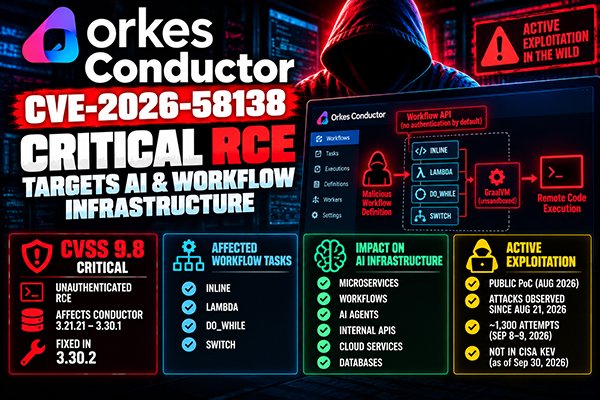
🔴 Orkes Conductor CVE-2026-58138 — critical pre-auth RCE
Attackers are targeting exposed Conductor workflow APIs. The CVSS 9.8 flaw can lead to remote code execution and potentially expose AI a
https://t.co/AHyVFCTif2
#CVE#CVE202658138#Orkes#Conductor#AI#RCE#CyberSecurity
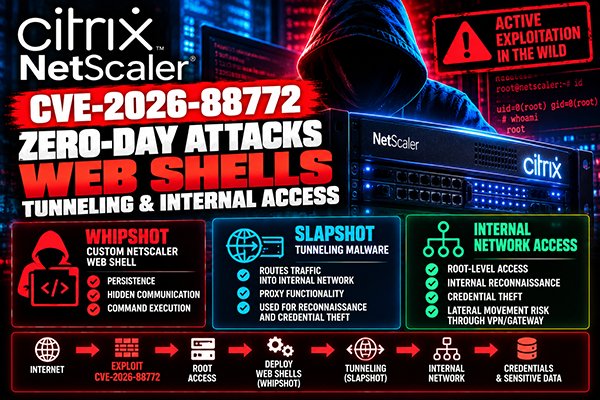
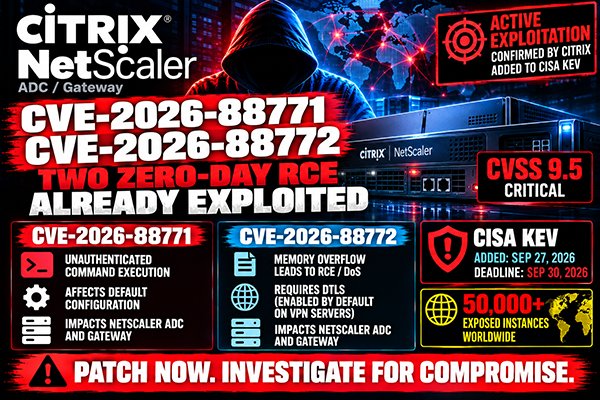
🔴 NetScaler CVE-2026-88772 — attacks go beyond RCE
Attackers are deploying WHIPSHOT web shells and SLAPSHOT tunneling malware, gaining root access and pivoting into internal networks.
https://t.co/IkxvNRXkFS
#CVE#CVE202688772#Citrix#NetScaler#WebShell#CyberSecurity
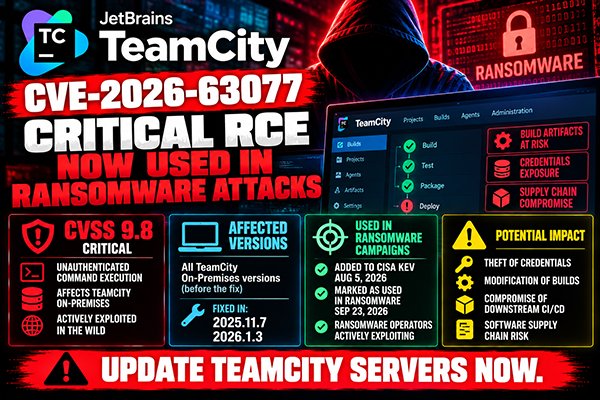
🔴 TeamCity CVE-2026-63077 — now used in ransomware attacks
Critical unauthenticated RCE can expose credentials, build artifacts and downstream CI/CD pipelines. CISA confirms ransomware use
https://t.co/baFEnlhWJW
#CVE#CVE202663077#TeamCity#JetBrains#Ransomware#CyberSecurity
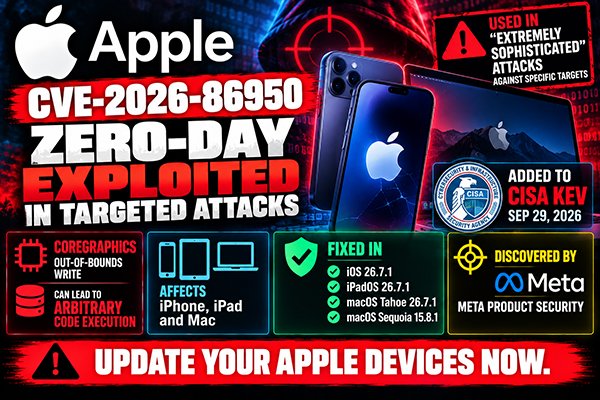
🔴 Apple CVE-2026-86950 — zero-day exploited in targeted attacks
A CoreGraphics out-of-bounds write can lead to arbitrary code execution on iPhone, iPad and Mac. Apple confirmed exploitation
https://t.co/J3OGHilw3e
#CVE#CVE202686950#Apple#iPhone#macOS#ZeroDay#CyberSecurity
🟠 Roundcube CVE-2026-48842 — pre-auth SQL injection
A CVSS 8.1 flaw in the virtuser_query plugin can expose vulnerable Roundcube installations before authentication. Exploitation has been
https://t.co/UZp8C64xtG
#CVE#CVE202648842#Roundcube#Webmail#SQLInjection#CyberSecurity
и описание для соц сетей
🔴 Citrix NetScaler: two zero-days under active attack
CVE-2026-88771 and CVE-2026-88772 can lead to RCE on vulnerable NetScaler ADC/Gateway systems. Both are
Full article on StemShop
#CVE#CVE202688771#CVE202688772#Citrix#NetScaler#CyberSecurity
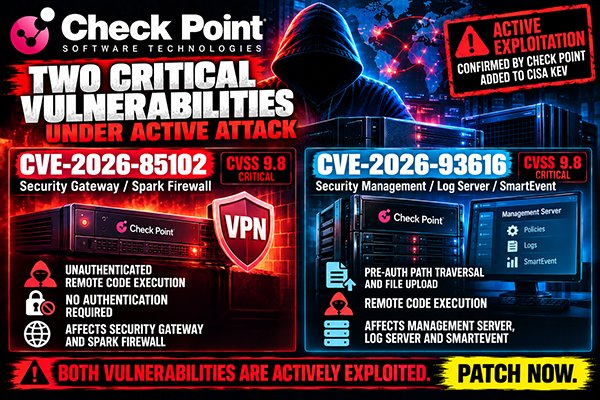
🔴 Check Point: two critical flaws under active attack
CVE-2026-85102 and CVE-2026-93616 both score CVSS 9.8, affecting VPN gateways and security management infrastructure. Both are now i
https://t.co/ThAxdMS4vS
#CVE#CVE202685102#CVE202693616#CheckPoint#VPN#CyberSecurity
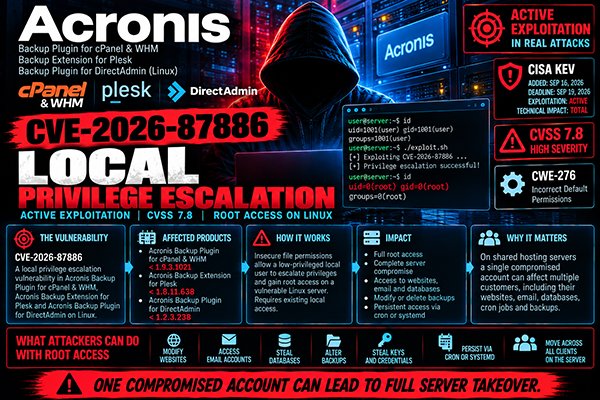
🔴 Acronis CVE-2026-87886 — active exploitation
Local privilege escalation can give attackers root access on vulnerable cPanel, Plesk and DirectAdmin Linux hosting servers. CISA added the flaw t
https://t.co/RTDC2JU2rG
#CVE#CVE202687886#Acronis#cPanel#Plesk#CyberSecurity
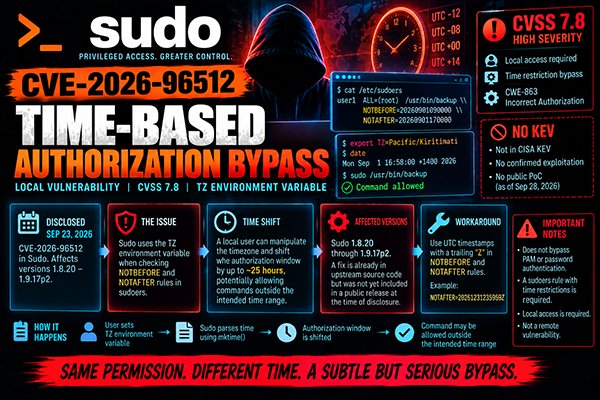
🟠 Sudo CVE-2026-96512 — CVSS 7.8
A local user can manipulate the TZ variable to bypass NOTBEFORE / NOTAFTER time restrictions by up to ~25 hours. No KEV or confirmed exploitation yet.
https://t.co/bBV8BjwLJH
#CVE#CVE202696512#Sudo#Linux#CyberSecurity
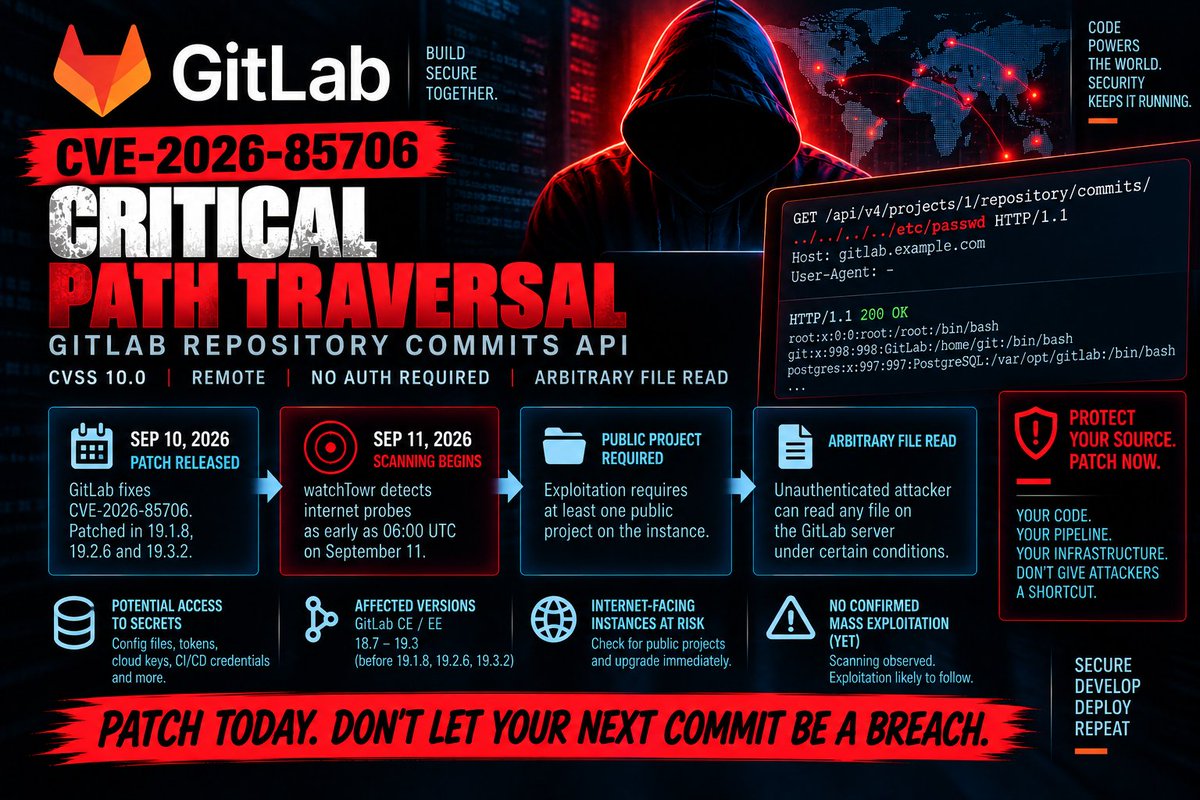
🔴 GitLab CVE-2026-85706 — active exploitation
Critical CVSS 10.0 path traversal can expose CI/CD secrets, deploy tokens, SSH keys and cloud credentials. Internet scanning began just one day after th
https://t.co/7gXYc31pRT
#CVE#CVE202685706#GitLab#CyberSecurity#DevSecOps
🚨 Critical Cisco ISE vulnerability CVE-2026-76460 has a CVSS score of 10.0 and is under active exploitation.
Learn about the risks and recommended actions:
https://t.co/DgelLaRpVj
#Cisco#CiscoISE#Cybersecurity#CVE-2026-76460
🔴 GitLab CVE-2026-85706 — CVSS 10.0
Unauthenticated path traversal can expose arbitrary files. The flaw is in CISA KEV and active scanning has been observed.
https://t.co/SFkyL8j2uX
#CVE#CVE202685706#GitLab#CyberSecurity
🔴 ScreenConnect CVE-2026-84869 — CVSS 9.9
CISA confirms active exploitation of the critical ScreenConnect flaw. Attackers can abuse remote sessions to transfer and execute files withou
https://t.co/xKqUr63eQE
#CVE#CVE202684869#ScreenConnect#ConnectWise#RMM#CyberSecurity
🔴 Fortinet CVE-2025-25249 under active attack
Attackers are exploiting the Fortinet flaw to deploy PivotC2. Researchers found 30,000+ targeted IPs and 178 confirmed infected devices.
https://t.co/qTQ0bHxuc6
#CVE#CVE202525249#Fortinet#FortiGate#PivotC2#CyberSecurity
🔴 GitLab CVE-2026-85706 — CVSS 10.0
Critical unauthenticated path traversal can expose arbitrary files and sensitive secrets on vulnerable GitLab servers. Internet scanning started almost immediately
https://t.co/QIAAvbiufZ
#CVE#CVE202685706#GitLab#CyberSecurity#InfoSec