1. How did you got into hacking
2. Who inspired you
3. Who helped you to become a hacker
4. Who is your favourite hacker
5. What is your best advice for beginners
**Extra : Pic of your pc setup **
#infosec#cybersecurity@johnjhacking @JacksonHHax @RealOGAnonymous
1- Fuzzed a JS file, found some endpoints—only one responded.
2- Tried IDOR, no response. Added ', noticed an anomaly.
3- Sent a blind SQLi payload—got 504 & 1 min timeout.
4- Used time-based SQLi to verify—yes, it worked! But the timeout made exploitation hard.
5- Tried OOB to get RCE, but it didn’t work because the current user lacked permission.
6- SQLMap didn’t work at times, but Ghauri did! ghauri -r Request.txt --technique=T --time-sec=5. Use * in Request.txt for injection points (even tricky ones)
this extension is amazing find some thumbnails endpoint and just one directory back and access full database including sensitive api keys of stripe,paypal,youtube etc
Ever explored HTTP request smuggling? 🕵️♂️
Our huntr @1nt3rc3pt0r discovered a vuln in Gunicorn where improper validation of the 'Transfer-Encoding' header leads to request smuggling. Can you spot similar issues in other HTTP servers? 👉 https://t.co/XrUScP4euA
1/1
Bypass Authorization Login into the Admin panel
1 download appe.exe and install it for windows
2 capture requests i used fiddler
3 update your profile the app sends a request to the server via the admin account i don't know why
#bugbountytips#BugBounty
5 Unusual Qualities That Will Make You a Pro at Pentesting:
1. Creativity
2. Persistence
3. Attention to detail
4. Adaptability
5. Communication skills
(thread)
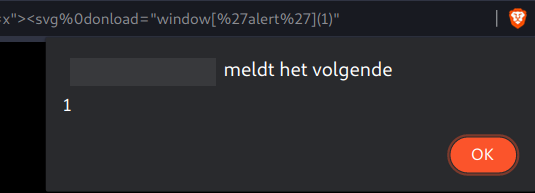
XSS bypass payload:
x"><svg%250donload%3D"window%5B%27alert%27%5D(location[%27hostname%27])"
Tip: Obfuscation almost always works to bypass WAFs (this target was behind Akamai WAF)
#bugbountytip#bugbounty
📌Docker Images for Penetration Testing & Security
• docker pull kalilinux/kali-linux-docker official Kali Linux
• docker pull owasp/zap2docker-stable - official OWASP ZAP
• docker pull wpscanteam/wpscan - official WPScan
🧵👇
#Pentesting#infosec#cybersecuritytips