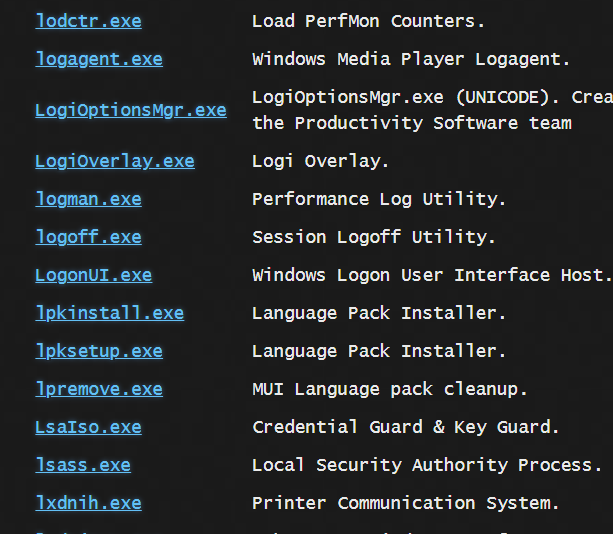
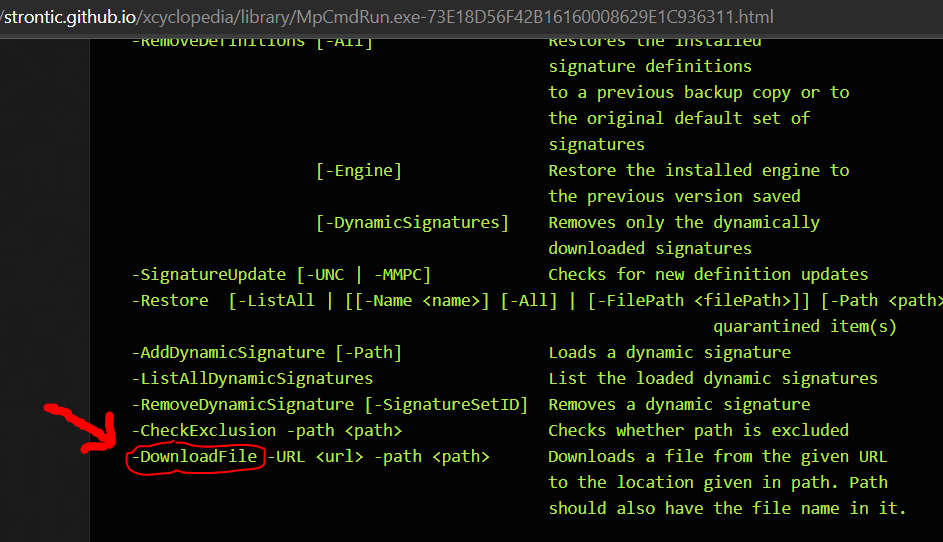
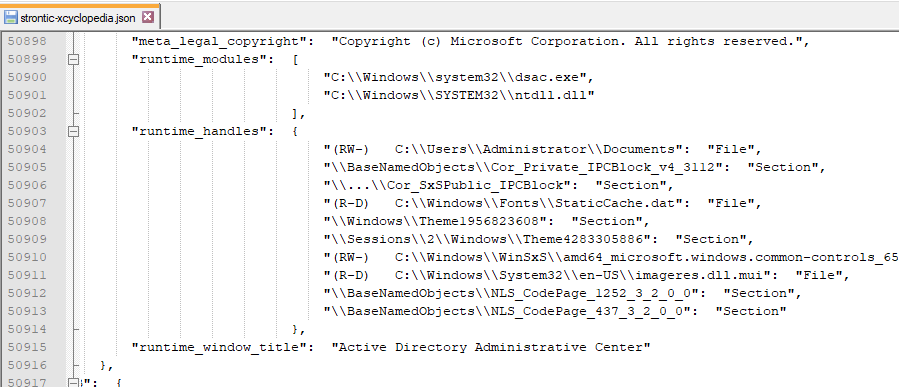
#DFIR. Know yourself. Know your system32. Enrich your process data with xCyclopedia! The machine-readable encyclopedia for executables. It’s free and open source. https://t.co/QM86PsVrfC. #hunt#lolbas#lolbin
Wow 3 years since last post. Tons of private work on detection engineering (similar to #SIGMA). Maybe some occasional posts about that? Any interest from the #DFIR community?
@cyb3rops Thanks! Community-sourcing would be great. But might expose this known-good dataset to tainting, e.g. bad actor inserting falsified hashes — which there’s no reliable way to detect. Not opposed to the idea if somehow sufficiently vetted. +Improved file consolidation coming ~July
@mabraFoo Agreed! And you're very welcome. Some new features coming soon. No hashes needed atm - not that it wouldn't be useful, but because new features will change how some files are organized. Looking into consolidation based on ssdeep, filepath, etc. It's growing too fast.😅
UPDATE: Was able to confirm @bing blocked https://t.co/E51QjepiG9. Fortunately, the merciful "Product Review Group" reviewed the site and decided to "lift the block".🙃 Does anyone else in #infosec/#DFIR community have issues with search engines delisting your content?
It appears @bing delisted https://t.co/ymwFaxZ4x7 (hosted at https://t.co/E51QjepiG9), which is a free and open source project for the #infosec community. The pic shows the dropoff in Bing traffic. Ever wonder why @google gets better results? This is why! ...hoping for resolution
It appears @bing delisted https://t.co/ymwFaxZ4x7 (hosted at https://t.co/E51QjepiG9), which is a free and open source project for the #infosec community. The pic shows the dropoff in Bing traffic. Ever wonder why @google gets better results? This is why! ...hoping for resolution
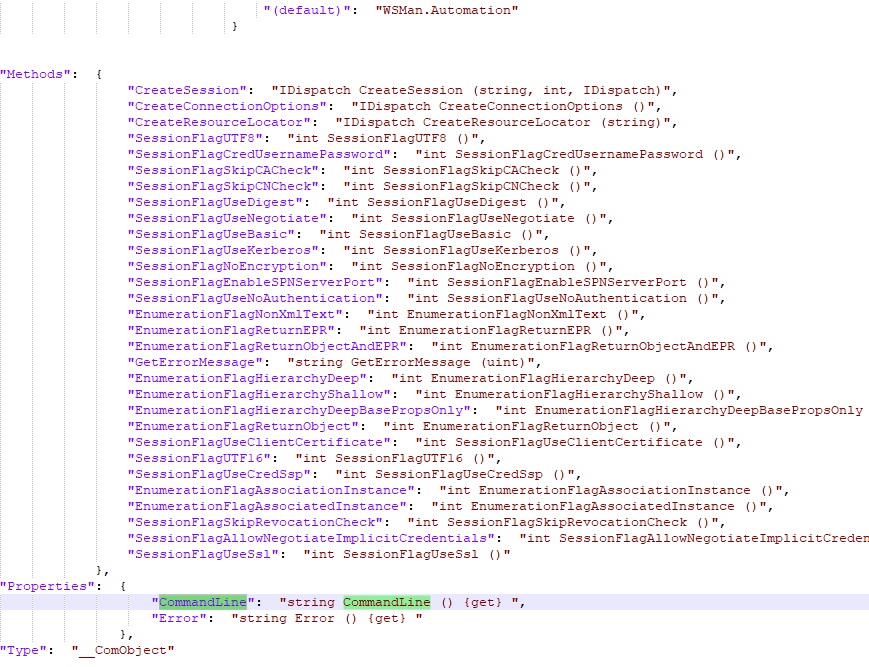
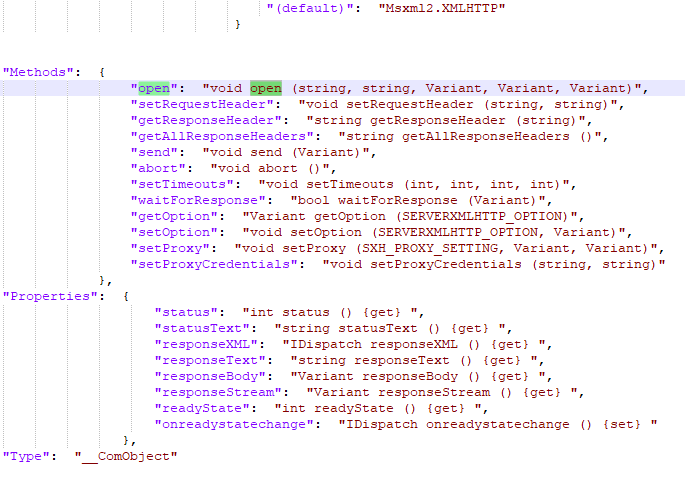
🆕 Unidentified COM Objects (UCOs) have landed in the xCyclopedia project! 🙃🛸 Beam it down now.... https://t.co/ok7BEVq6jp #TheTruthIsOutThere#DFIR#ThreatHunting
@DFIR_Zach @rimpq For legitimate software, the hash will typically be identical between machines if they are the exact same version/patch level. However, that means many of those hashes will change, as updates/patches are regularly applied.
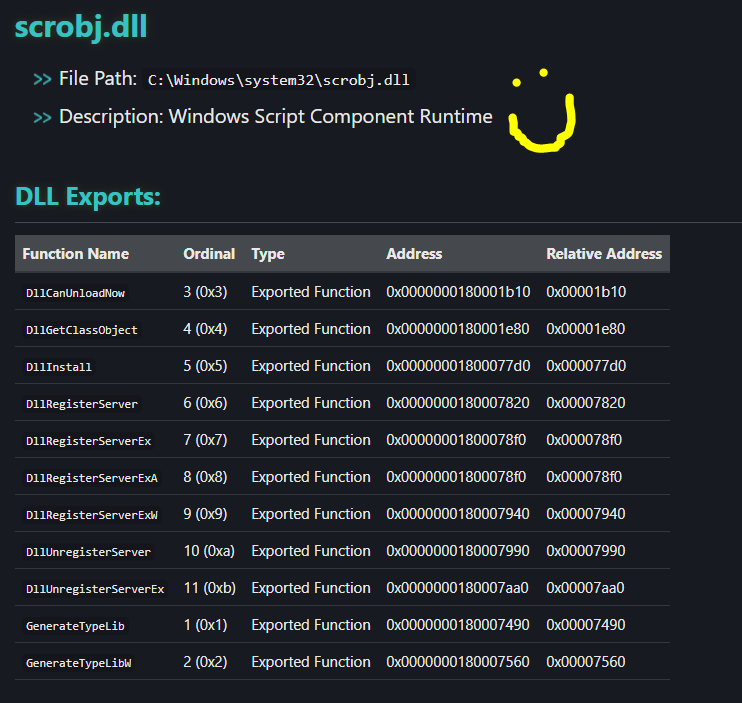
🆕Now find DLL's on https://t.co/ymwFaxZ4x7! Discover the DLL Exported Functions available to you (and attackers) on a typical Windows deployment (hint: 283k known functions! 🙀). Also available as JSON: https://t.co/szDLIqEG2P. More to come! #DFIR#lolbin#lolbas#sysadmin
New design. Same great stuff. https://t.co/ymwFaxZ4x7 needed a makeover. Now it has search and navigation! Still has over 1,700 unique executables and growing. Still has relevant #lolbins from atomic-red-team, #lolbas, #sigma, and others. #dfir#sysadmin
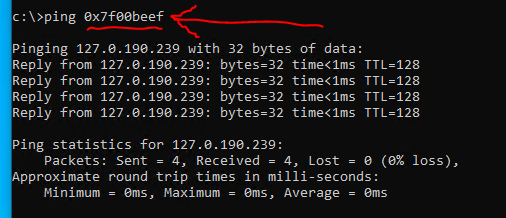
😁Pinging 0x7F00BEEF translates to lookback 127.0.190.239. Might rearchitect network to #hexspeak IPs. Thank you @Trustwave for the inspiration. https://t.co/GO6lhvMziU.
Does that DLL normally get loaded by that binary? Find out! #xCyclopedia has 3 new data points available: Open Handles, Loaded Modules, and Window Titles. Check it out @ https://t.co/ymwFaxZ4x7! And get the raw CSV/JSON at https://t.co/szDLIqEG2P #dfir#sysadmin#knowyoursystem
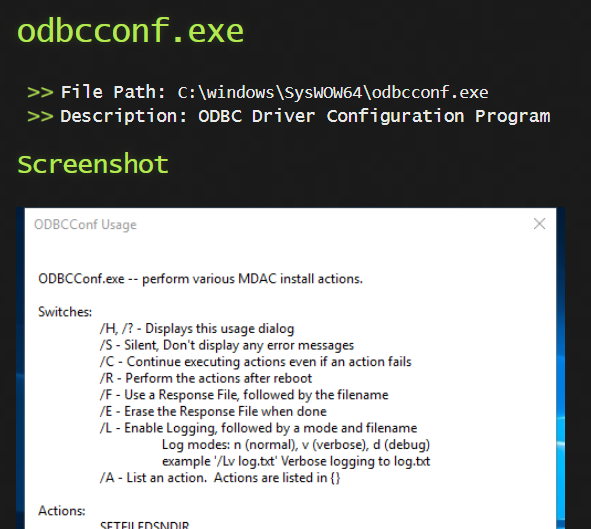
Which of your legitimate executables are are being abused? xCyclopedia now shows you known attack techniques. See the new feature at https://t.co/DvtKD168mG. It's our🆓labor of love! It has screenshots now too. Check it out, comment, and share! #dfir#sysadmin#hunt#lolbin
Now you can easily view the xCyclopedia data! Take a look at https://t.co/ymwFaxZ4x7 (new!). There you will find descriptions of each binary executable (.exe) found on a modern Windows OS, usage/syntax, and much more. It's also downloadable in JSON or CSV! #lolbin#dfir#sysadmin
Don't know what that #lolbin/command does? Not documented in #lolbas project? I created a machine-readable clone of #ss64's command reference site. It should help with automated #syslog and #eventlog enrichments. Useful to #DFIR? (more to come!) https://t.co/tae5rTfIJC #firstpost