Truly living with your toolset and _failing_ with it is a profound aspect of expertise. I doubt there have been any % of tech who were ever taught this. It's too dumb and obscure. You have to learn it by failing.
This is the Lock Picking Lawyer, and what I have for you today is a standard business desktop. I'm going to use a USB stick, which I of course sell on Covert Instruments dot com. I insert it, click the obfuscated batch script... and we're admin.
One of the worst things you can do during an Incident Response scenario is to make assumptions.
Train your team to identify and question their assumptions.
How come there’s no reality TV show starring multiple programmers that get dropped into an unknown repo and have to fix a bug, the fastest one wins.
I’d watch that.
Took a miniature painting class this weekend with my wife. She's definitely more artsy than I am but I'd like to think my warrior (left) looks pretty good! #miniaturepainting
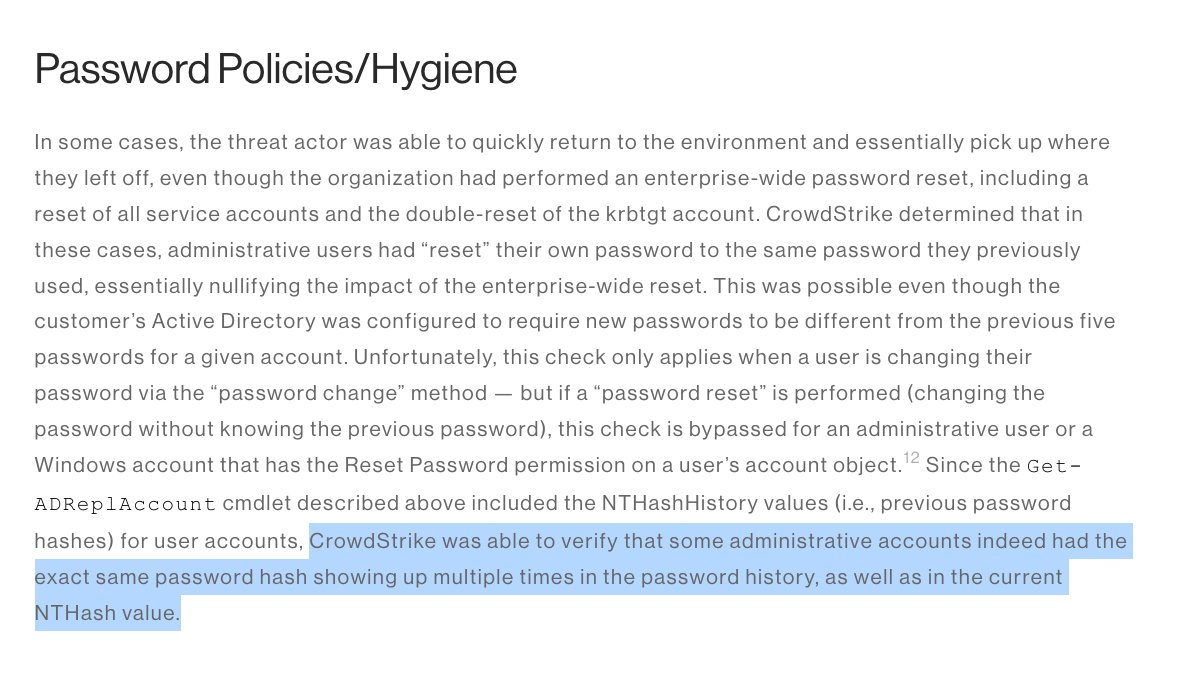
I've been looking forward to the release of this article for a long time! Really happy to be able to share what myself and others from the CS Services team have seen in the field from this advanced adversary. #StellarParticle https://t.co/x2POvVw5R2
For the record, I wanted to call the cookie theft/reuse technique something cool like "Cookie Monster" but fortunately @MITREattack already had the technique so no one in #DFIR will have to include my meme name in a report https://t.co/8mMYW7xxpS
I've been looking forward to the release of this article for a long time! Really happy to be able to share what myself and others from the CS Services team have seen in the field from this advanced adversary. #StellarParticle https://t.co/x2POvVw5R2
What people seem to miss:
The #Log4Shell vulnerability isn't just a RCE 0day.
It's a vulnerability that causes hundreds and thousands of 0days in all kinds of software products.
It's a 0day cluster bomb.