Unfortunately, we are being blocked by certain oligarchs in order to maintain their monopolistic chokehold on the Indian people. You can guess who they are …
This is a crime against the people of India!
🔴 The Fastest Technique to Find Data Leaks!
Most people search Google for leaks, find nothing, and stop there.
The problem is that a lot of leaked data never shows up on the open web. It gets passed around in Telegram channels. 📲
I usually start outside Telegram.
First, I look for news reports, blog posts, forum threads, or breach writeups.
That usually gives me a few useful clues:
the type of data exposed, possible filenames, database names, or where the leak first appeared.
Once I have a filename or database name, I search for it with an operator like this:
→ site:https://t.co/fr5ddXnMYh "NAME.7z"
I walk through this workflow in my LeakHunt course, including how to find leaks and search inside them safely.
Sometimes that one search is enough to find the Telegram channel where the file was posted. 🔍
⚠️ Important: never open leaked files on your main machine. Use an isolated virtual machine first.
🔗 Link: https://t.co/ykCXgDutMz
P.S. ♻️ Repost if you found this helpful.
@therealDeFlock 🚀 Wire Tapper for OSINT & SIGINT just got updated!
Added:
📷 Flock camera
🗺️ Custom wardriving data
📍 IoT device locator
📡 Bluetooth radar
📻 SDR support
https://t.co/OAiI8GEd0U
Also u can install via pip -- pip install wiretapper https://t.co/YJYRWtf5CJ
🚀 Wire Tapper for OSINT & SIGINT just got updated!
Added:
📷 Flock camera
🗺️ Custom wardriving data
📍 IoT device locator
📡 Bluetooth radar
📻 SDR support
https://t.co/OAiI8GEd0U
Also u can install via pip -- pip install wiretapper https://t.co/YJYRWtf5CJ
Drone Hacking - Hacking UAVs with Damn Vulnerable Drone
The Damn Vulnerable Drone, or DVD, is a training simulator that was made for people who want to learn drone hacking without buying a drone. It recreates an entire drone system in software, including a flight controller, an onboard companion computer, a ground control station and the wireless links connecting them all. Every piece is there, and every piece runs inside Docker containers on a single computer.
It has more than 40 realistic attack scenarios with walkthroughs
https://t.co/5Ctu4BK4m6
building aerial object detection + tracking system for drones
interested in how to make the cheapest + most efficient drone system for deployments in agriculture, surveillance, etc
current tech stack:
> YOLO26n model fine-tuned on the VisDrone dataset
> YOLO model is pretrained on the MS COCO dataset
> will run on a MaixCAM2 with an Axera AX630C chip
> switch between ByteTrack / BoT-SORT for detection, depending on drone movement
full drone build coming soon stay tuned
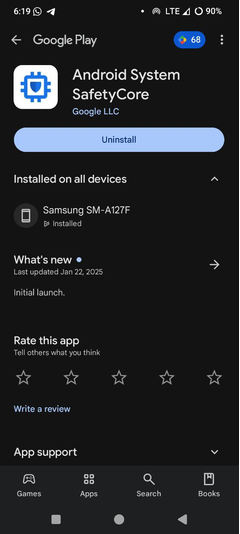
If you’re still on stock Android…
Google silently installs SafetyCore (on-device sensitive content scanning)
and it reinstalls itself every time you try to remove it.
The community’s solution is simple and effective:
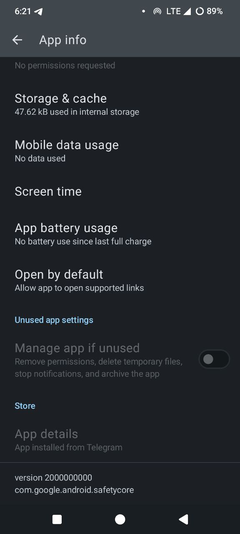
a placeholder APK with an absurdly high version number (2,000,000,000).
Once installed, Google can no longer overwrite it.
1. Uninstall SafetyCore
2. Install the placeholder
3. Keep control of your device
GitHub: https://t.co/enSZbjA2Ho
Even blocking a Google component requires workarounds on stock Android.
Have you tried it? Does it hold up over time for you?
#Privacy #DeGoogle #Android #SafetyCore #DigitalSovereignty
Do you know one of the ways police, military personnel, intelligence agencies, and digital forensics investigators can trace your activities?
They use call detail records, commonly known as CDRs.
CDR is telecom metadata generated when a mobile subscriber makes or receives a call, sends an SMS, or uses certain network services.
A CDR may contain:
Calling and receiving numbers
Date, time and duration
Incoming or outgoing direction
Cell tower or Cell ID used
IMSI, which identifies the SIM subscription
IMEI, which identifies the mobile device
Event type, such as call, SMS or data session
Roaming and network-routing information
A CDR normally does not contain the audio of a call or the content of an SMS. It records the circumstances surrounding the communication.
CDR analysis does not reveal what was said, it helps establish who, when, where and how. This is how you are mapped.
You see, for you to get the data for this work, you need to visit the telecom with a police report or warrant, and then it's game over.
CDR can be dangerous because it exposes a person’s behavioral patterns, even though it usually does not contain call audio or message content.
With enough records, someone may infer:
Who a person communicates with most.
Where they were approximately located.
Their daily routine, travel patterns and regular meeting places.
Relationships between individuals or groups.
Which SIM cards and devices they use.
Periods of coordinated activity.
Visits to sensitive locations, such as hospitals, courts, religious centres or political meetings.
#CDRAnalysis #DigitalForensics #DFIR #TelecomForensics #CrimeAnalysis #HIVEConsult
Scrapes publicly available CCTV camera metadata from DOT (Department of Transportation) and other open sources, then stores it in a structured database for research, analysis, and indexing.
https://t.co/OoW6nCNfxh