Curious how to launch yourself into the top ranks of our quarterly leaderboard in only a few weeks time? @sumgr0 recently pulled this off, so we sat down with him to try uncover some of his secrets! 😏
Check out our interview:
https://t.co/plML3S8PET
At https://t.co/yLyFoGefG8, you can find GraphQL and API endpoints.
Good but not enough!
We're adding over it with agents. Finding API base URLs and building API requests, testing for unauth requests. Coming soon!
Signup now at Jsmon!
🚨 Node2Shell — CVE-2026-111497
A critical OOB write in the Brotli decoder gives attackers RCE on every supported Node.js release line. CVSS 9.2.
The scariest part? fetch() decompresses Brotli automatically. No opt-out. Your outbound requests are the attack surface.
Full deep-dive 🧵👇
i'm sorry to say folks but unfortunately weekends are ruined , 3 more RCE dropped in last few hours.Patch ASAP .🤯
https://t.co/tm230U3jQ4
https://t.co/gGSn7Xn3Yi
https://t.co/ce8hlFEYFZ
The critical Brotli RCE vulnerability discovery came out of our large scale infrastructure code scanning efforts
Great research by @k_tr4n and @_sy1vi3 in assessing the widespread impact of this bug
Update your Node.js, Bun, Envoy, anything using Brotli ASAP!
You can now perform content discovery at 100k requests per second with h3fuzz on http/3 hosts (fork of ffuf with http/3 support).
Tool here: https://t.co/tL4kkQRRwN
Research post here: https://t.co/LSGVNco6G3
Gemini 4 Argon has arrived! The era of super intelligence in cyber security has begun, excited to share more on how we use it to secure the world - and we are just getting started 🌎
https://t.co/exoWENGGz6
https://t.co/pyD9JtEuLX
We just raised an $8M seed round to kill AWS, GCP, and Azure.
Introducing https://t.co/E3LHVE410x, the agent-native serverless cloud.
Your team is shipping code like never before. But you're getting caught up in manual, tedious DevOps work trying to deploy it.
InstaCloud provides the serverless compute that lets your services autoscale, with all the infrastructure managed for you.
Agents branch into complete replica environments when working, keeping prod safe and iteration speed high.
And of course, it all works seamlessly with agents through MCP/CLI.
Get off the traditional, legacy cloud.
Start deploying your services on InstaCloud today.
If you had ever wished for something like claude but for security people and not for developers,
you can try building all that for ~6> months or give it a try today its only free for a limited time !!
You get
- Agent that always creates poc and verifies it using different agent ( NO FP and diplomatic responses )
- Built in Isolated Vulnerabilities/Issues database
- Auto Triage from hackerone, vm dbs or DIY ...
- A persistant computer for your agent just like Grok
- Claude Tag -> Neo Slack
- Claude CI -> Neo for Github
- Linear and other integrations
- A lot more that you will never know 🤷
Neo is now free to try.
Neo runs long security tasks against your apps, network, code and vulnerability backlog, with shared agents context.
→ https://t.co/AnCqFyKXZw
Here’s what you can do with Neo:
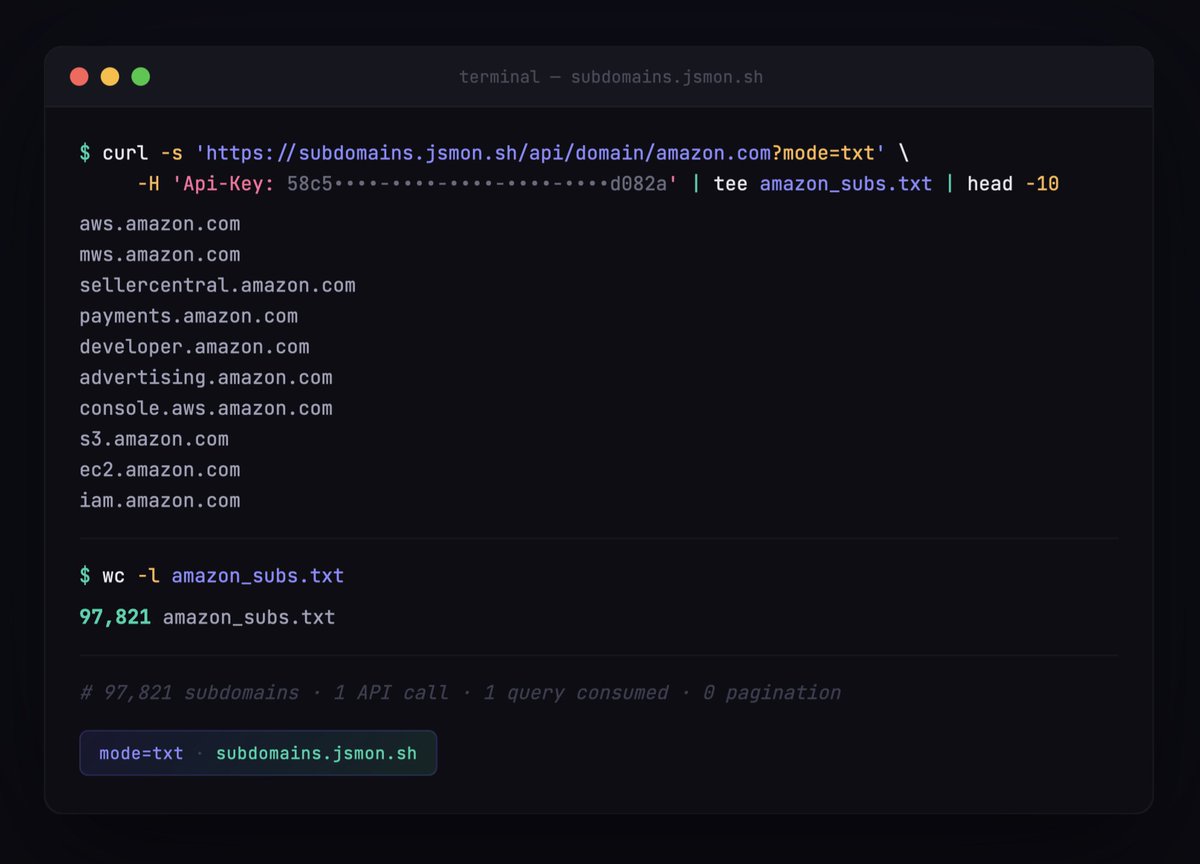
🚀 New Update: ?mode=txt on https://t.co/Huec3oviKv
One API call - Fetch all subdomains. Even if a domain has 500K subdomains, full output in seconds.
curl -s -H 'Api-Key: YOUR_KEY' 'https://t.co/IbvFtVUpZ9'
Available on Pro and Max plans.
🔥 The wait is over! 🔥
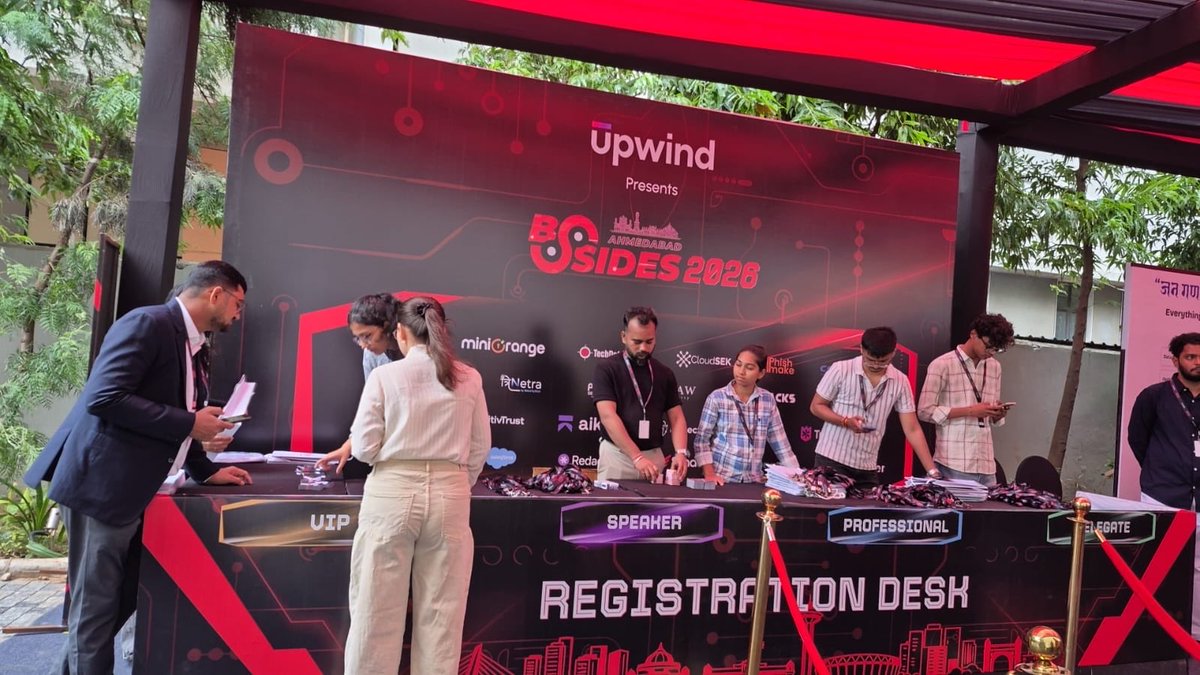
The BSides Ahmedabad team is all set to welcome YOU! 🚀🛡️
Registration desks are ready, the team is geared up, and the energy is already 🔥🔥
🎟️ Your BSides Ahmedabad 2026 experience starts NOW!
Get ready for two action-packed days of cybersecurity, innovation, knowledge, networking & unforgettable moments!
📍 Hyatt Regency Ahmedabad
💥 Let’s make #BSidesAhmedabad2026 unforgettable!
See you at BSides Ahmedabad! 🚀
#BSidesAhmedabad #BSidesAhmedabad2026 #Cybersecurity #InfoSec #CyberSecurityCommunity #EthicalHacking #CyberConference #Ahmedabad #CybersecurityEvent #InfosecCommunity #HackingCommunity #TechCommunity
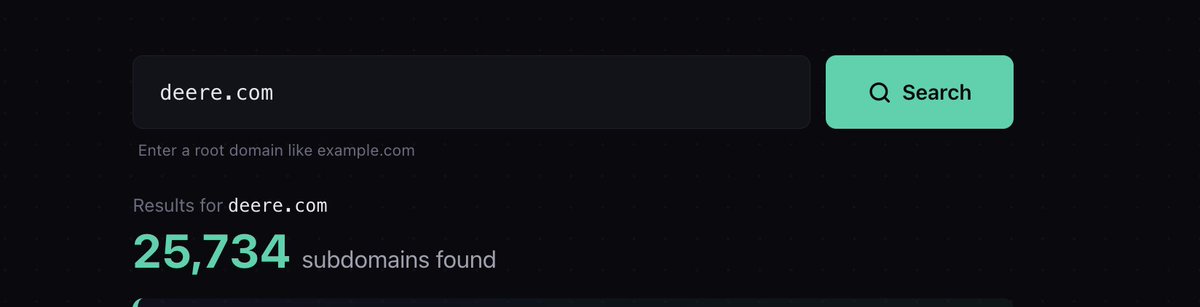
Since launch, we've added 1 billion new subdomains.
The database now has 4.5 billion subdomains.
Quick comparison for https://t.co/VyifadQUgr:
https://t.co/pfDy7rAJdO → ~6,000 results
https://t.co/8DqZulgLHs → ~25,000 results
Try any domain here → https://t.co/8DqZulgLHs
"3 random dudes”
1. hacked apple, again and again.
https://t.co/5aZcB0RbjF
https://t.co/UdsKrmfFJW
https://t.co/hWDQaimW8c
2. your github enterprise is our github enterprise.
https://t.co/u3UjajnBKq
3. get a discord message from me, get pwned.
https://t.co/pX3RkjxNOX
https://t.co/noscPNmZm9
4. oh yeah, at one point we basically had shells across the electron ecosystem. check the DEF CON research.
https://t.co/1Th5fvpa21
5. your supabase database is my database.
https://t.co/nOIKthdDnM
6. we got the posthog prod database.
https://t.co/VIeGJz1hKq
7. react2shell? vercel paid us $170k for helping secure their waf.
https://t.co/Y2RgQSdl3g
8. your palo alto vpn is my vpn.
https://t.co/oVB068UhST
9. ai ides? we got shells for you, antigravity
https://t.co/tsvSXQuSS0
10. windsurf rce.
https://t.co/DpdGqmNRvu
11. turning cluely into malware.
https://t.co/8QcIYhXQfS
12. ai browsers? sure, uxss: your perplexity browser is my browser.
https://t.co/WVXlHzY0CB
13. openai atlas too. kinda uxss
https://t.co/jkQWnLD7rV
14. hey, it’s not even our first time hacking discourse.
https://t.co/viI1op7aMf
15. adobe coldfusion: pre-auth rce. because apparently we needed another one.
https://t.co/aFILo3suP2
there’s a lot more. go dig.
anyway, yes: “3 random dudes.”
and @HacktronAI is full of more random dudes like these.
5 years ago I wrote a blog with @Farah_Hawaa about how to hack APIs for the Detectify blog.
Today, I wrote an updated one to include all the new stuff, including how to hack APIs with AI!
I think you'll get a lot out of this if you want to learn how to hack APIs, or you need a 2026 refresher with new techniques!
https://t.co/Kv4xlm9xcl