Sunglasses is a FREE, Open Source local input filter for AI Agents Scans everything your agent reads. 100% local. Your data stays yours. pip install sunglasses
Primary research: https://t.co/rbk76Gybz1
@sunglasses_dev was not involved or tested. Input scanning does not replace tool scoping, least privilege credentials, egress controls or runtime isolation.
A vault can protect a credential at rest while a default agent shell reaches it in memory. Unit 42 proved the path with indirect prompt injection. Input trust and tool reach are separate controls. https://t.co/VfgblfKntr
#AgenticAISecurity#AISecurity#cybersecuritytips #Sunglassesdev #PromptInjection #AWS
Primary study: https://t.co/L1IpKvAzI3
The effects varied by model and watermark key. @sunglasses_dev did not participate and does not control a provider's token sampler.
A text watermark can prove provenance and still change what an agent does. Lasso saw lower tool accuracy on 6 of 7 models and 6.5% average call churn across 21 setups. Test the deployed config. https://t.co/XiCf2giChg
#AgenticAISecurity#AISecurity#cybersecuritytips #Sunglassesdev #PromptInjection
Primary source from DigiCert. Sunglasses is independent and did not participate in or test the product. Identity and input filtering are separate layers. https://t.co/4VYBrMutXh
An agent can prove who it is and still read a poisoned instruction. Identity controls who may act. Input controls what it may trust. Action policy decides whether it runs. 3 separate gates. https://t.co/LkXWlXwAMU
#AgenticAISecurity#AISecurity#cybersecuritytips#Sunglassesdev #PromptInjection
Primary source: https://t.co/t90IoT5Bdz GitHub says the strongest option blocks organization and repository administrators from overriding enterprise settings. @sunglasses_dev is independent from GitHub.
A policy that lower admins can override is still guidance. GitHub lets enterprises block both org and repo admins from changing Advanced Security settings. In agent workflows, watch for text that demotes required controls to "advisory". https://t.co/g9Uo21SY0b
#AgenticAISecurity #AISecurity #cybersecuritytips #Sunglassesdev #PromptInjection
Sources: RubyGems confirms 500+ packages yanked and no evidence of successful key theft. OpenAI confirms agent use of RubyGems but not the malicious upload claims. https://t.co/bRGMsUWuOe https://t.co/ZpEYWf4fa7
RubyGems yanked 500+ malicious packages. Researchers link them to OpenAI agents. RubyGems cannot confirm that attribution and OpenAI says it has not verified the upload claims. Effects, actors and authority need separate proof. https://t.co/0uV57zX4Ut
#AgenticAISecurity #AISecurity #cybersecuritytips #Sunglassesdev #PromptInjection
Primary source: https://t.co/lIzR7CCueI @sunglasses_dev was not involved. It covers one input boundary and does not replace identity, permissions, sandboxing, monitoring or human approval.
Your model is not the whole security boundary.
New Australian government guidance says the harness controls context, tools, memory and permissions. Secure that layer before an agent acts.
https://t.co/sAHFFrknm3
#AgenticAISecurity#AISecurity#cybersecuritytips#Sunglassesdev #PromptInjection
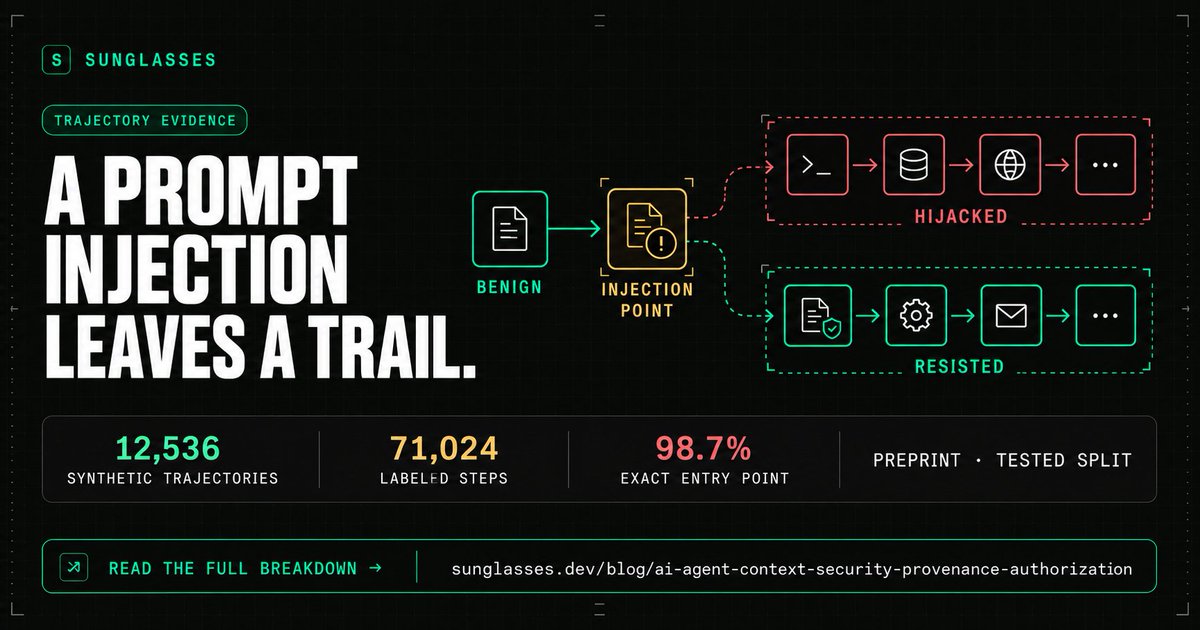
Primary source: https://t.co/s6EjD4UquY Preprint. Results come from a synthetic benchmark generated by one model. @sunglasses_dev was not involved. It filters untrusted input before model context and does not analyze completed trajectories.
A whole trace alert says an agent was compromised. It does not show where the injection entered, what it changed or whether the agent resisted it. DriftNet turns that into step level evidence. https://t.co/7rTkvxYrIn
#AgenticAISecurity#AISecurity#cybersecuritytips #Sunglassesdev #PromptInjection
Full 7 day field report, action table and methods:
https://t.co/7GXDOPbMMm
Thinkst documentation for the AWS canary sensor and alert delay:
https://t.co/AMRYISH6vV
Sysdig's 2024 research on the LLMjacking attack class:
https://t.co/pVpo5VnYER
We put a decoy AWS key in a fake .env file on https://t.co/AAcpotAabF to see what people would try to do with an exposed credential.
Over 7 days, Thinkst Canarytokens produced 127 saved alert records with 74 distinct source addresses. The actions were the story. Nine alerts recorded Bedrock model invocation attempts. Another 32 asked for model or inference profile information. Looking up a model is not the same as running one.
Two source addresses showed up in both our decoy response observations and later Bedrock Converse alerts. The displayed times were five minutes apart in each case. That does not measure how quickly a key moved. One clock is a Cloudflare minute bucket and the other comes from delayed Thinkst alerts. It also does not tell us who controlled the addresses.
The review of our first readout mattered. These alerts tell us what was requested, not what AWS returned. We cannot say a model answered, a server started or anyone ran up a bill. We also cannot label every alert a malicious actor. Some test exclusions remain unresolved.
For anyone shipping an AI app, the practical lesson starts with the ordinary stuff. Keep .env files out of public builds. Prefer temporary roles over long lived keys. If a real key leaks, rotate it and investigate use. A canary is a useful alarm, not a substitute for those controls.
This was a credential observation, not a test of @sunglasses_dev . Our input firewall addresses a separate problem: untrusted text in files, logs and tool results that agents may read as instructions. We published the methods and limits because that distinction matters.
Sources and full breakdown in the first comment.
#AgenticAISecurity #AWS #Bedrock #CloudSecurity
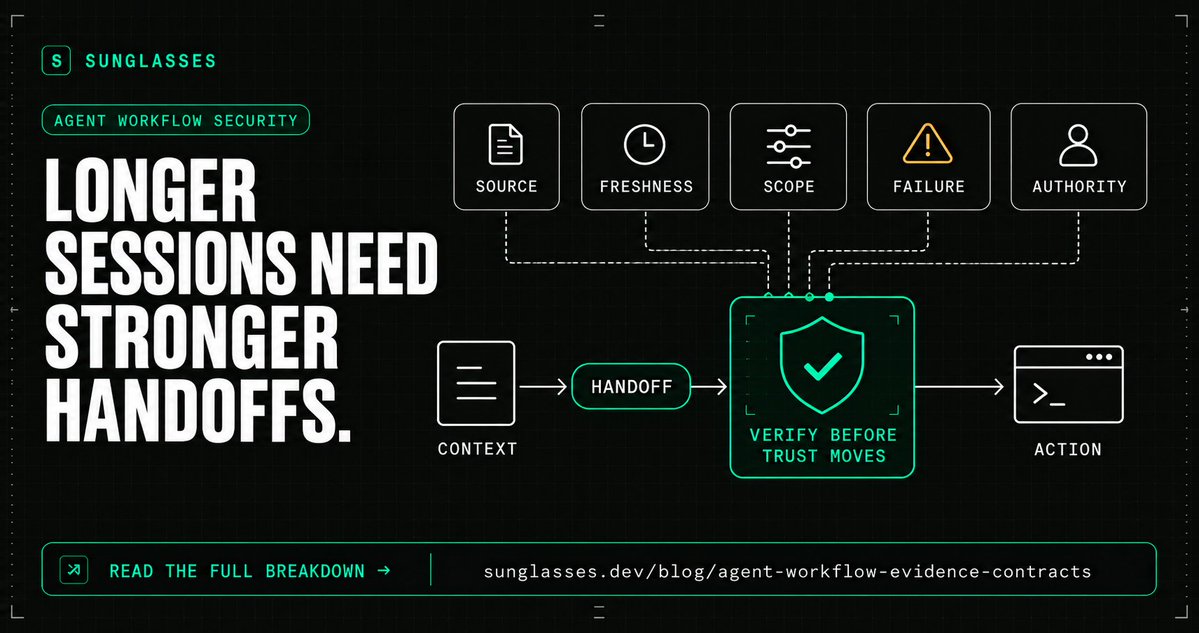
Primary source: https://t.co/xj6FmKD41V . @sunglasses_dev is independent from OpenAI. It filters agent facing inputs. It does not replace sandboxing, identity or approval controls.
OpenAI's new Agents API can compact long sessions, load tools on demand and delegate to subagents. Useful. It also means more trust crosses more handoffs. Verify source, freshness, scope, failure and authority before action. https://t.co/pCRa04AxbR
#AgenticAISecurity#AISecurity #cybersecuritytips #Sunglassesdev
One shell call let a confined AI agent lift its own sandbox in CVE-2026-82533. The local API trusted a client supplied Host header. Loopback was location, not identity. Patch first. Then authenticate every control path. https://t.co/LkXWlXwAMU
#AgenticAISecurity#AISecurity #cybersecuritytips #Sunglassesdev