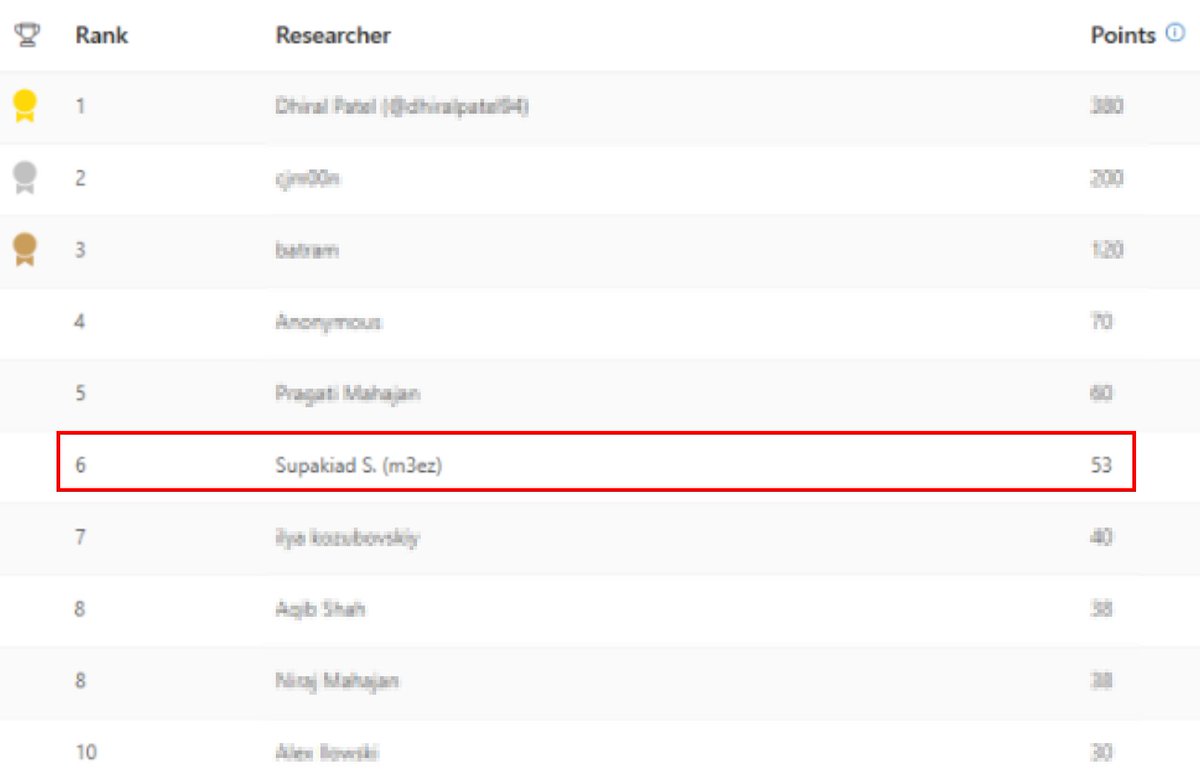
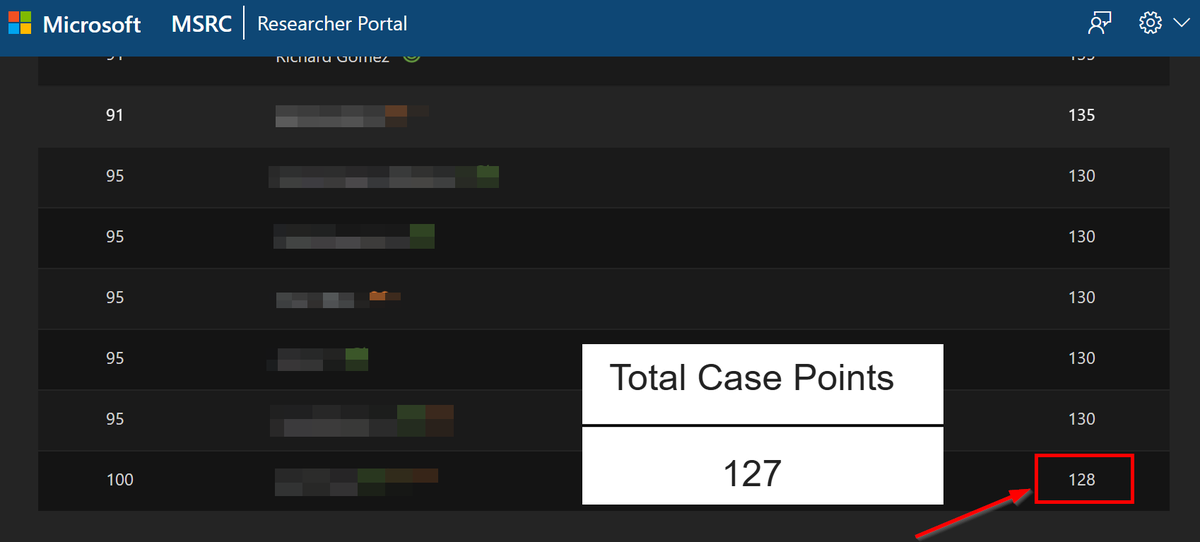
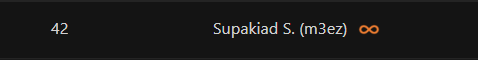
Proud to be ranked 6th in Microsoft Dynamics research and 16th overall on the Q3 2024 MSRC Leaderboard!
Grateful and thanks for the recognition, @msftsecresponse.
https://t.co/C0BXXdOQet
#MSRC#bugbounty#Microsoft#Dynamics
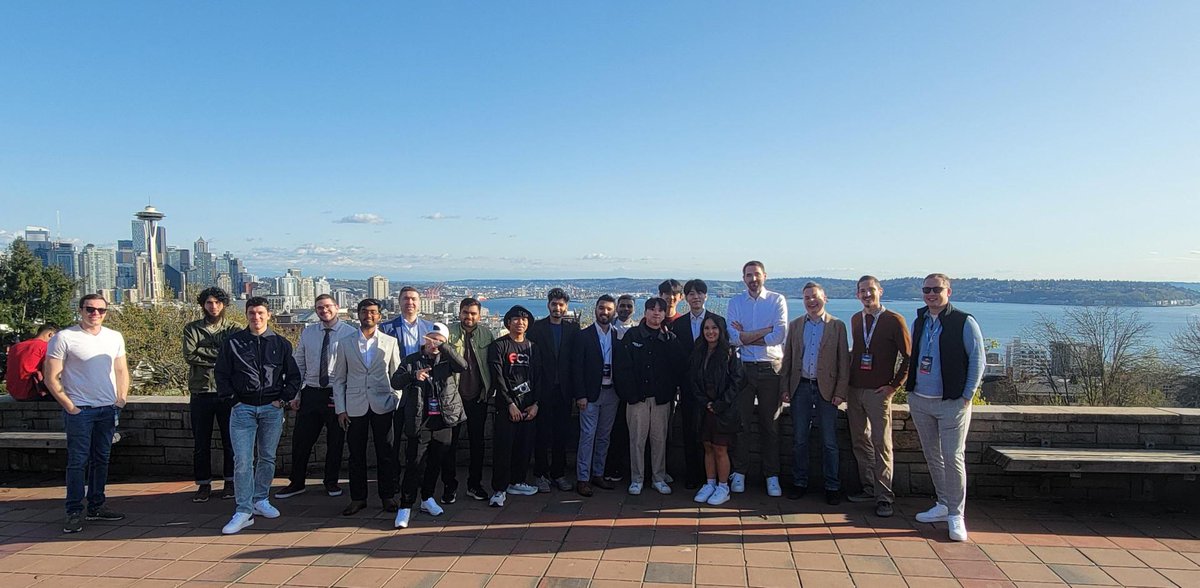
We’re excited to welcome some of the world’s top security researchers to Zero Day Quest 2026 🎉
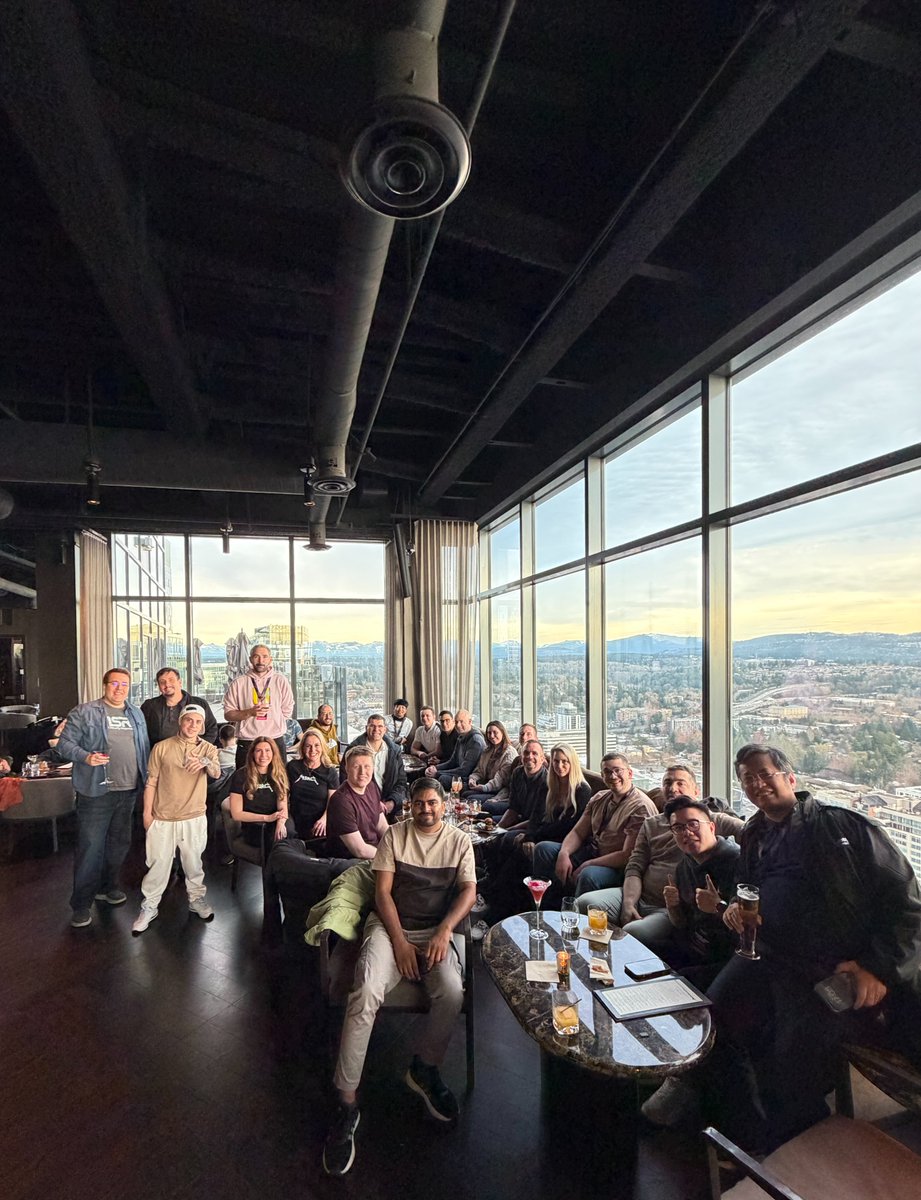
We kicked off the onsite hacking event with bowling, followed by dinner and drinks with incredible views. It’s the start of a full week of security research, collaboration with Microsoft teams, and social events including a Kraken hockey game, a brunch cruise, and more.
We’re grateful to every researcher who qualified and joined us in person, as well as those participating remotely. Their work and partnership with Microsoft help protect customers and communities around the world.
#ZeroDayQuest
As announced by Tom Gallagher (@secbughunter), VP of Engineering, MSRC, on stage at Black Hat Europe, we’re evolving our bug bounty program. Now, high-severity vulnerabilities that directly impact Microsoft online services are eligible for bounty awards, whether the code is Microsoft-owned, third-party, or open source.
This expanded scope applies retroactively to cases from the past 90 days, ensuring recent impactful research is recognized and rewarded. These payments have already begun.
Learn more about the changes, our commitment to the security community, and how you can participate: https://t.co/xkBJ285tAM
#BHEU
@trufflesec@irsdl 5️⃣ Persistent XSS on Microsoft Bing\.com by poisoning Bingbot indexing
@Supakiad_Mee shares how he discovered a (second-order) stored XSS vulnerability in Microsoft Bing's video indexing system that occurs when Bingbot crawls and stores video metadata!
https://t.co/byzsN3gbat
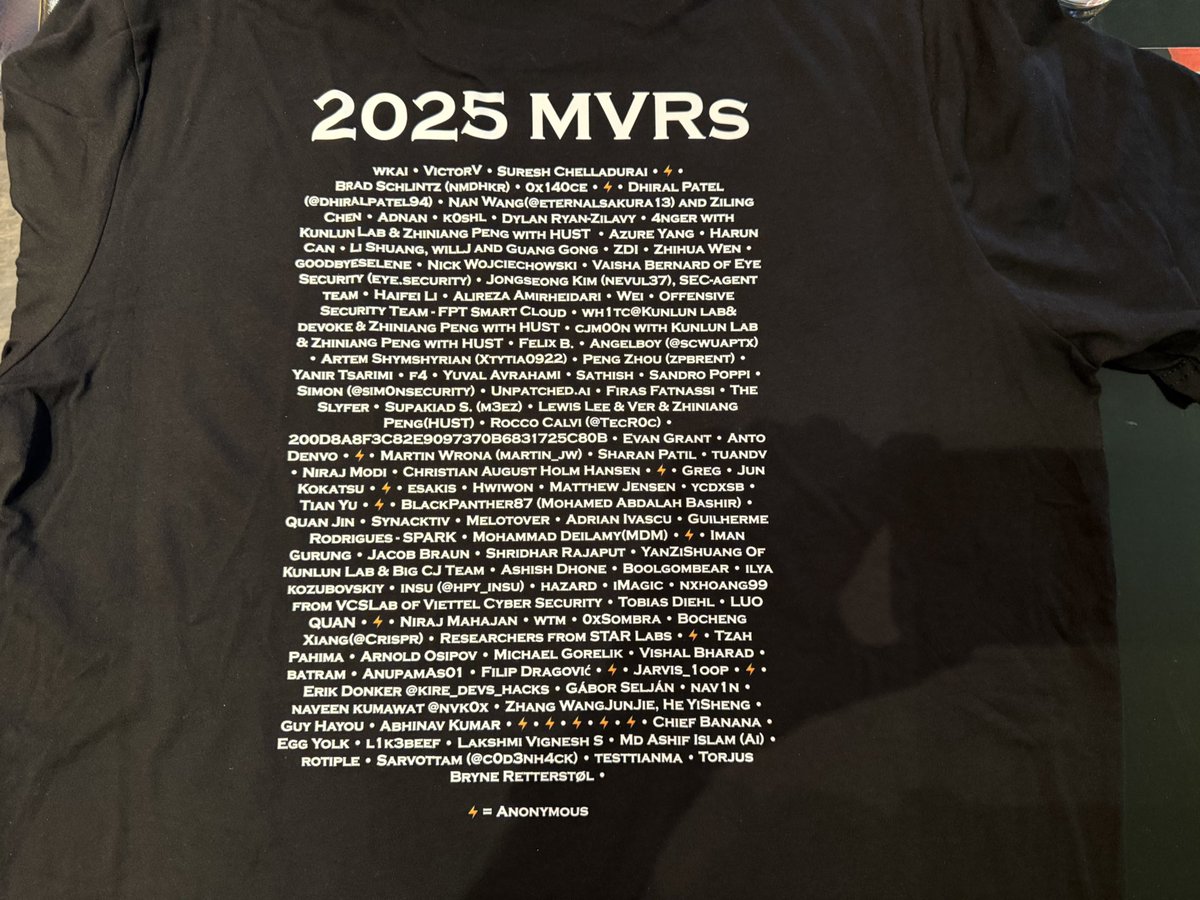
The MSRC team and I are excited up to connect and learn from security researchers and the community at Black Hat & DEF CON this week! If you spot me, I might have a shirt with your name on it. #blackhat2025#blackhat#defcon@msftsecresponse
Over the past year, the Microsoft Bounty Program distributed $17 million to 344 security researchers from 59 countries—the highest total bounty awarded in the program’s history. Thank you to our global security researcher community for helping us protect customers and the world.
Learn more about this year’s highlights, program updates, and what’s next in our blog: https://t.co/91sDLo9ixA
#bugbounty
The Microsoft Researcher Recognition Program offers public thanks and recognition to security researchers who help protect our customers by discovering and sharing security vulnerabilities under Coordinated Vulnerability Disclosure.
Today, we are excited to recognize this year’s 100 Most Valuable Researchers (MVRs), based on the total number of points earned for each valid report. Please join us in celebrating this year’s MVRs, including our top 10:
1. 🥇 VictorV (@vv474172261)
2. 🥈 wkai
3. 🥉 Suresh Chelladurai
4. Anonymous
5. Adnan (@adnanthekhan)
6. Dhiral Patel (@dhiralpatel94)
7. Nan Wang (@eternalsakura13) and Ziling Chen
8. Anonymous
9. @0x140ce
10. Azure Yang (@4zure9)
See the full list of this year’s 100 MVRs, in addition to our Azure, Office, Windows, and Dynamics 365 leaderboards: https://t.co/8vhDhDpr3E
#bugbounty
Earlier this month, we hosted the Microsoft Zero Day Quest, the largest live hacking event of its kind. This inaugural event brought together top security researchers from around the world to find the highest-impact vulnerability scenarios in Microsoft Copilot and Cloud.
The result? More than 600 vulnerabilities submitted and $1.6 million awarded, with additional findings still under review.
We're also making two major commitments moving forward:
1. Continuing the 100% AI bounty award multiplier
2. The Microsoft Zero Day Quest will be an annual event
This is just one part of Microsoft’s broader bug bounty program, which awarded over $16 million in 2023. We're proud to work with the global research community to help secure the future—by design, by default, and in operation.
Read more in our blog post by Tom Gallagher (@secbughunter), VP of Engineering, Microsoft Security Response Center: https://t.co/2c7RDySWch
Day 2 of #ZeroDayQuest brought even more hacking, problem-solving, and unforgettable moments.
We then went to Carmine’s for incredible food and even better conversation, connecting over exploits, defense strategies, and a shared passion for protecting customers.
Day 2 of #ZeroDayQuest brought together brilliant minds from around the world for more hands-on hacking and meaningful community connections. Catch the energy in our recap video!
@secbughunter@tinderj_@ZenOneSec@0xdea
After three intense days of hacking at #ZeroDayQuest, we hit some of the most iconic spots in Seattle before our final celebration at the Space Needle.
Our global crew of security researchers soaked in the sights, snapping skyline photos, and strengthening the community that makes this work so powerful.
That’s a wrap on the final day of the inaugural Zero Day Quest.
Researchers hacked until the very last minute, 11:59 AM PT, bringing three days of collaboration, creativity, and bug hunting to an exciting close. Afterward, we explored the best of Seattle on a city tour, then capped it all off with an unforgettable evening reception and awards ceremony at the iconic Space Needle.
Huge thanks to the Zero Day Quest security researchers and Microsoft employees who brought their skills, passion, and energy to this inaugural event.
Winners were announced last night during our celebration at the Space Needle. Stay tuned, we’ll be sharing the overall and category award winners publicly soon!
#ZeroDayQuest
Day 2 of #ZeroDayQuest brought even more hacking, problem-solving, and unforgettable moments.
We then went to Carmine’s for incredible food and even better conversation, connecting over exploits, defense strategies, and a shared passion for protecting customers.
Here’s a glimpse of last night’s Zero Day Quest welcome reception, where we kicked things off with some of the world’s top security researchers. This invite-only event brings together hackers and Microsoft engineers to collaborate on securing AI and the cloud.
Today, security researchers are onsite at Microsoft’s Redmond campus, diving into our products to uncover vulnerabilities, earn bounty awards, and help protect customers. We’re grateful to have them with us for the Zero Day Quest Onsite Hacking Event.
#ZeroDayQuest