🎤 BlueHat Redmond speaker announcement
We're excited to announce Varsha Chahal and Henrique Pereira (@ikkebr), Senior Security Engineers at Microsoft, will be speaking at BlueHat Redmond with their talk, “Gotta Catch’em All: Hunting Azure Anonymous Functions in the Wild.”
Azure Functions often expose anonymous HTTP endpoints, creating a broad and overlooked attack surface. In this session, Varsha and Henrique share how they identified and exploited vulnerabilities at scale, leading to 40+ MSRC cases, including multiple high-impact issues.
From CodeQL to automated exploitation pipelines, learn how small misconfigurations can turn into critical cloud risks and how defenders can better secure serverless workloads.
#BlueHat
📣The BlueHat Asia Call for Papers is now open! 📣
BlueHat brings together security researchers and defenders to exchange ideas, experiences, and best practices. We’re looking for talks on novel research that hasn’t been presented before, including vulnerability research, mitigations, emerging threats and techniques, and related areas across the security landscape.
📍Singapore | September 17–18, 2026
🗓️CFP deadline: June 15, 2026
Submit your paper now: https://t.co/BAtZHRg7co
There is a lot of momentum around AI in cybersecurity and its ability to improve security outcomes at scale. At Microsoft, we are applying these capabilities to our long-standing work with the community to find and mitigate vulnerabilities more quickly and augmenting our security and development toolsets so we can better protect customers and Microsoft.
Read more: https://t.co/0GqRtiJMSn
I don’t have the word to fully articulate how great this event is. The benefits are layered and invaluable. It’s fun. It’s collaborative but most of all, it’s protecting you, the customers! Thank you researchers for what you do and thank you @msftsecresponse for this event.
Day 1 of the Zero Day Quest Onsite Hacking Event is in the books and we’ve kicked off Day 2.
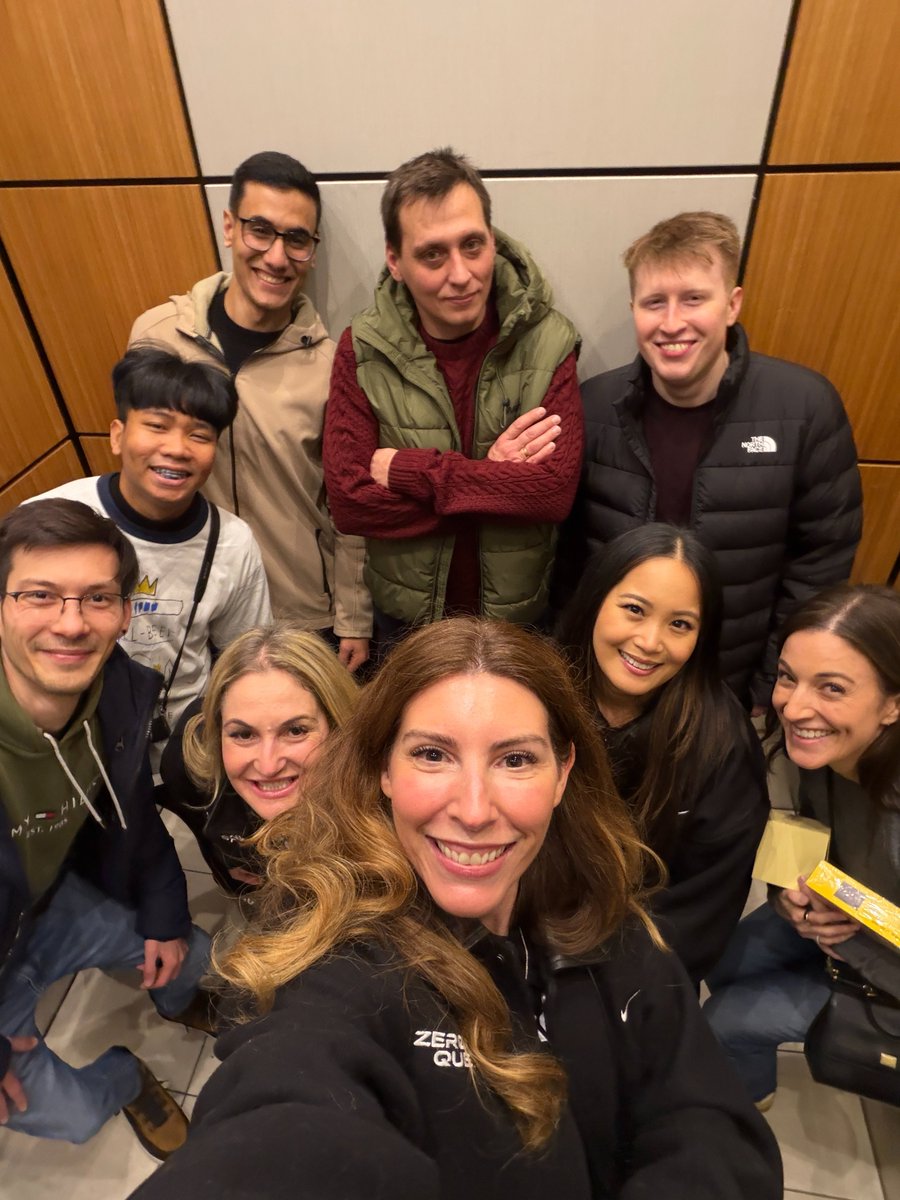
We welcomed top security researchers from around the world to Microsoft’s Redmond campus for a day of live hacking, collaboration, and connection.
Researchers worked side-by-side with Microsoft engineers and product teams to identify vulnerabilities across our AI and cloud platforms. Lots of amazing reports and discussions flowed throughout the day with MSRC, product teams, and the researchers themselves all driving security forward together.
We wrapped the day with a Seattle Kraken vs. Tampa Bay Lightning game in Seattle (tough loss, but the vibes were strong!).
We’re incredibly grateful to the security researcher community. Your work makes a real impact in helping protect customers.
#ZeroDayQuest
Today, we’re welcoming top security researchers from around the world to Microsoft’s Redmond campus for the first official day of the Zero Day Quest Onsite Hacking Event. They’ll collaborate with Microsoft engineers and product teams to uncover vulnerabilities across our AI and cloud platforms over the next two days.
We’re thankful for the security researcher community and the impact their work has in helping protect customers.
#ZeroDayQuest
We’re excited to welcome some of the world’s top security researchers to Zero Day Quest 2026 🎉
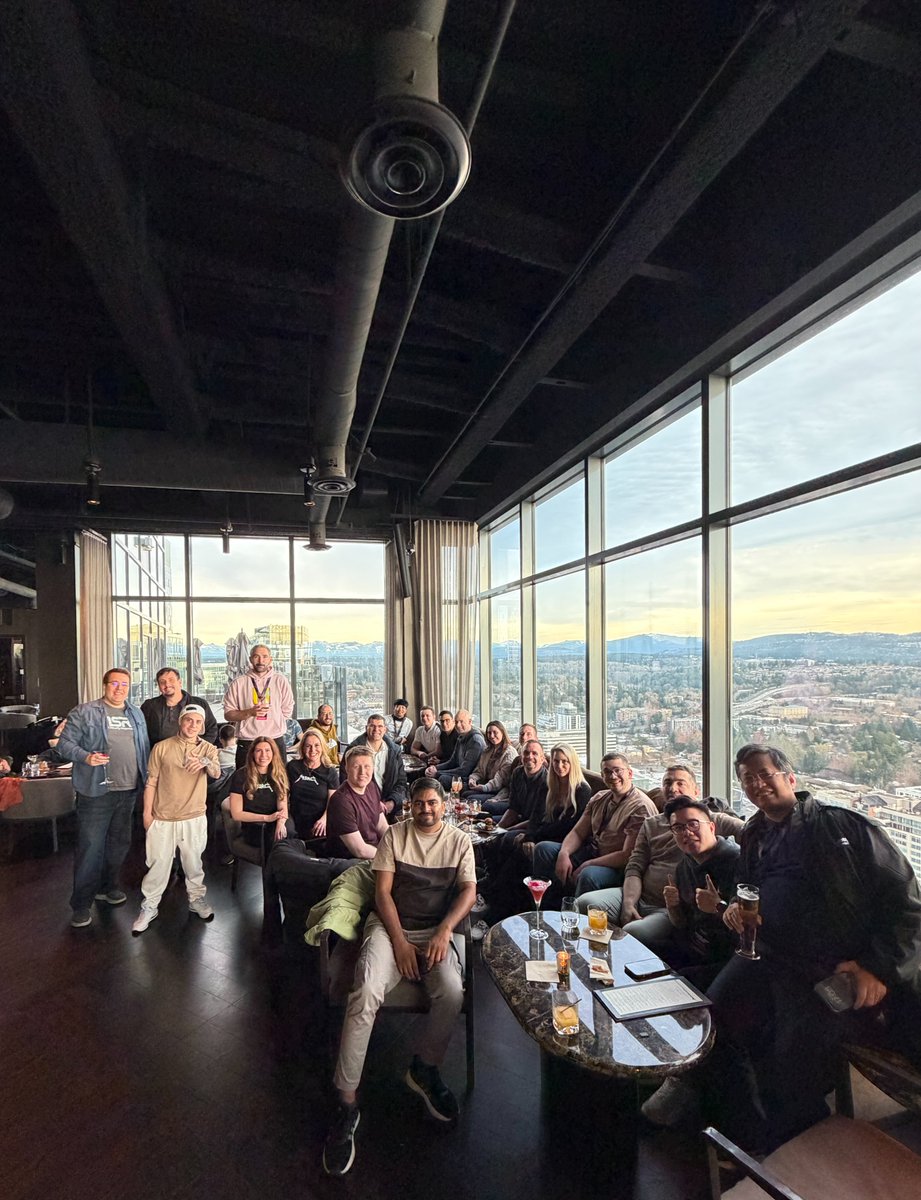
We kicked off the onsite hacking event with bowling, followed by dinner and drinks with incredible views. It’s the start of a full week of security research, collaboration with Microsoft teams, and social events including a Kraken hockey game, a brunch cruise, and more.
We’re grateful to every researcher who qualified and joined us in person, as well as those participating remotely. Their work and partnership with Microsoft help protect customers and communities around the world.
#ZeroDayQuest
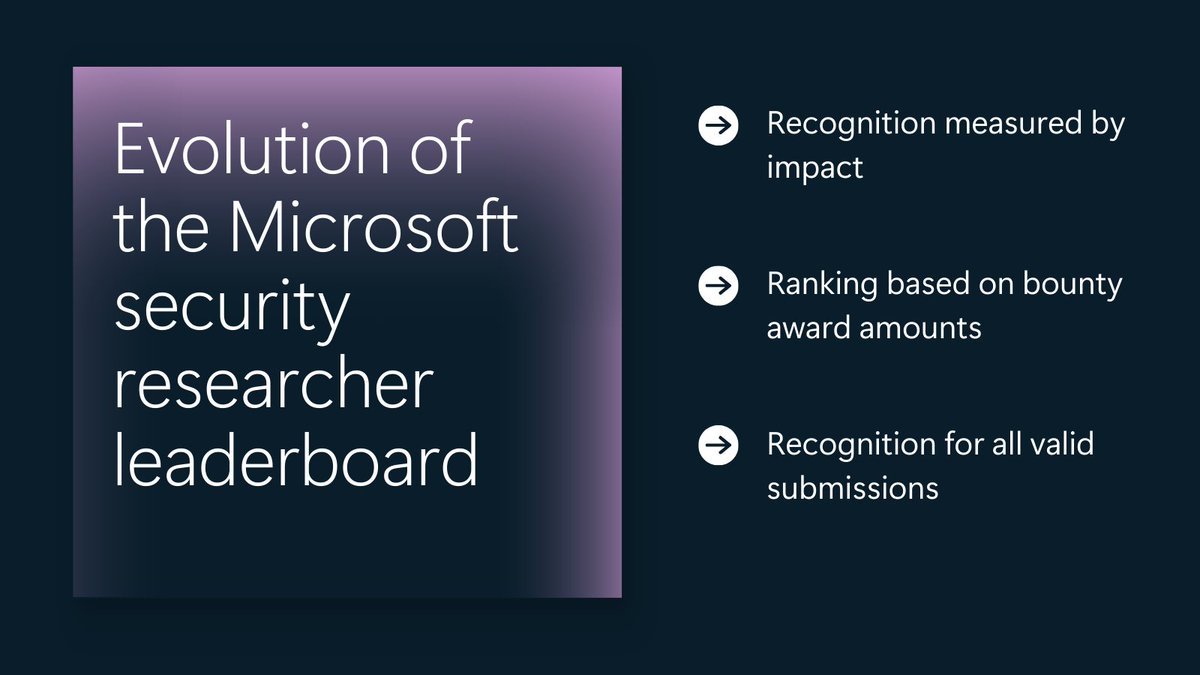
The global security research community plays a critical role in protecting Microsoft customers. As Tom Gallagher (@secbughunter), VP of Engineering at MSRC, shares in today’s announcement, we’re evolving how researcher impact is recognized.
Starting with the July 2026 Most Valuable Researcher (MVR) leaderboard, rankings will be based on bounty award amounts, providing a consistent signal that aligns recognition with vulnerability severity and security outcomes. We’re also introducing honorable mentions to recognize all researchers who submit valid vulnerability reports, independent of ranking.
Read the full announcement for more details: https://t.co/PY2amshwcm