I've been researching the Microsoft cloud for almost 7 years now. A few months ago that research resulted in the most impactful vulnerability I will probably ever find: a token validation flaw allowing me to get Global Admin in any Entra ID tenant. Blog: https://t.co/jD6EaGtsn3
And now have it confirmed from multiple people that the new tenant arrives in a broken-by-default state where MFA is required for your one admin user but MFA registration is blocked by CA, no workarounds 😬 cc @olafhartong
Seems Microsoft is nuking all M365 developer program tenants, with no path to migrate to their "new" setup. Just create a new tenant, of course subject to the current eligibility requirements. There goes my research tenant I've been using for 7 years... 🙄 https://t.co/sQ7Fsz0Wg9
Seems Microsoft is nuking all M365 developer program tenants, with no path to migrate to their "new" setup. Just create a new tenant, of course subject to the current eligibility requirements. There goes my research tenant I've been using for 7 years... 🙄 https://t.co/sQ7Fsz0Wg9
@_dirkjan@PyroTek3 This is a huge burden on so many people and a huge pain to migrate all these tenants. Very strange decision. I’m sure there has been some abuse but this is not the way to treat many paying researchers.
Last chance to sign up for my Entra ID class in The Hague, starting November 16th.
If that doesn't work out, I will also be back teaching at Insomni'hack next year in the first week of February.
More info: https://t.co/RowaIQlU5e and https://t.co/J7yYUnMHc3
@al3x_n3ff For most tools it wouldn't make a huge difference but bloodhound python has quite some LDAP code that I'd prefer not to have to rewrite. Besides impacket LDAP is very minimal and I'm not sure it even supports the mechanisms I use for efficiency like generators.
Last week me and GPT-6 wrote a wrapper library for ldap3 AD auth methods and ported several of my AD tools to use it. BloodHound-py, krbrelayx and adidnsdump now use it for their LDAP connections: signing/sealing over 389 by default (ntlm+kerberos) and channel binding for ldaps.
Works on top of the stable ldap3 version, no forks needed, no GSSAPI library dependencies, impacket only. Thanks to the folks who submitted PRs to add support for signing, which was the base for much of the implementation.
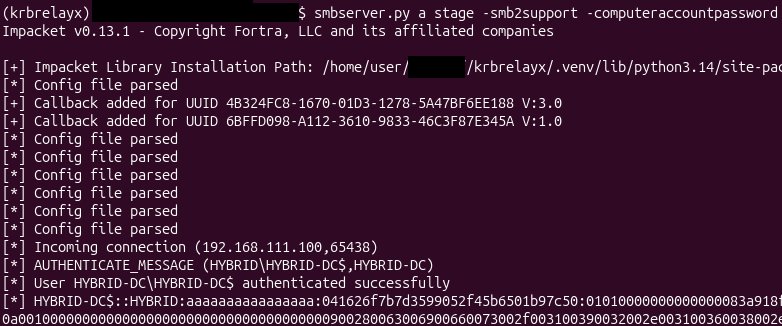
I wrote up a way to defeat enforced SMB signing for relay.
It abuses a documented SMB re-authentication behavior.
I'm surely missing nuance and prior art. Corrections welcome.
Writeup:
https://t.co/qzF9MUF9MJ
PoC:
https://t.co/O0UN4gdVfJ