🚨 Exciting thing🚨 I'm getting back to my content creation roots.
I've missed blogging, podcasting, and community engagement from back before I worked for big companies with scary PR teams.
So... I'm launching a newsletter called Vulnerable U. https://t.co/eevYXMY8hB
Norway now has more than 2,000 underwater AI laser robots shooting lice off its salmon
they're made by a company called Stingray, and they already guard more than 50 million salmon and trout 24/7
the reason is sea lice, tiny parasites that latch onto salmon and feed on them
as few as 11 can kill a small fish, and one pen can hold 150,000 salmon
the usual fix is pumping the fish out and blasting them with warm water or water jets to knock the lice off
but the handling is so rough that Norway's fish health report ranks it the top cause of death in full-grown farmed salmon
so instead, Stingray puts a robot inside the pen that hunts lice one at a time, all day:
> two cameras watch every salmon that swims past
> AI checks two frames to make sure it's really a louse
> then a green laser fires from up to 2 meters away
> the salmon's scales reflect the beam, so the fish swims off fine and the louse is dead
we now live in a world where AI lasers do pest control on your dinner lmao
I know it’s basically my job to stay on top of the news and be chronically online
But I’m just gonna not for a few days…
You all be cool about it alright?
An update on the WorkOS security incident:
Shortly after our original bulletin, a security researcher contacted us and claimed responsibility. They told us they were evaluating ARTEX, an autonomous penetration testing framework, when their agent escaped its isolated testing environment and interacted with WorkOS unintentionally.
We asked for technical evidence. The researcher provided request details, timestamps, and artifacts from the activity. Our security team and an independent forensic investigator matched that evidence against our logs, establishing with high confidence that this individual was responsible for the unauthorized activity we observed.
The researcher has confirmed that all WorkOS data obtained by their agent has been deleted and was not shared with anyone else.
Their explanation that the activity was unintended does not change how seriously we take the incident or our responsibility to our customers.
Full report: https://t.co/gfKc1HCQ81
I know it’s basically my job to stay on top of the news and be chronically online
But I’m just gonna not for a few days…
You all be cool about it alright?
I did a whole lot of IR last month. Much of it was helping companies affected by compromises at their neocloud providers.
I wrote up the lessons and practical steps teams can take to reduce their exposure and make incident response less painful.
https://t.co/PNvxsYzGUk
I am looking for my next role in cybersecurity!
If your team is hiring, or you know someone who is, please feel free to contact me.
DMs are open and any reposts or leads are appreciated!
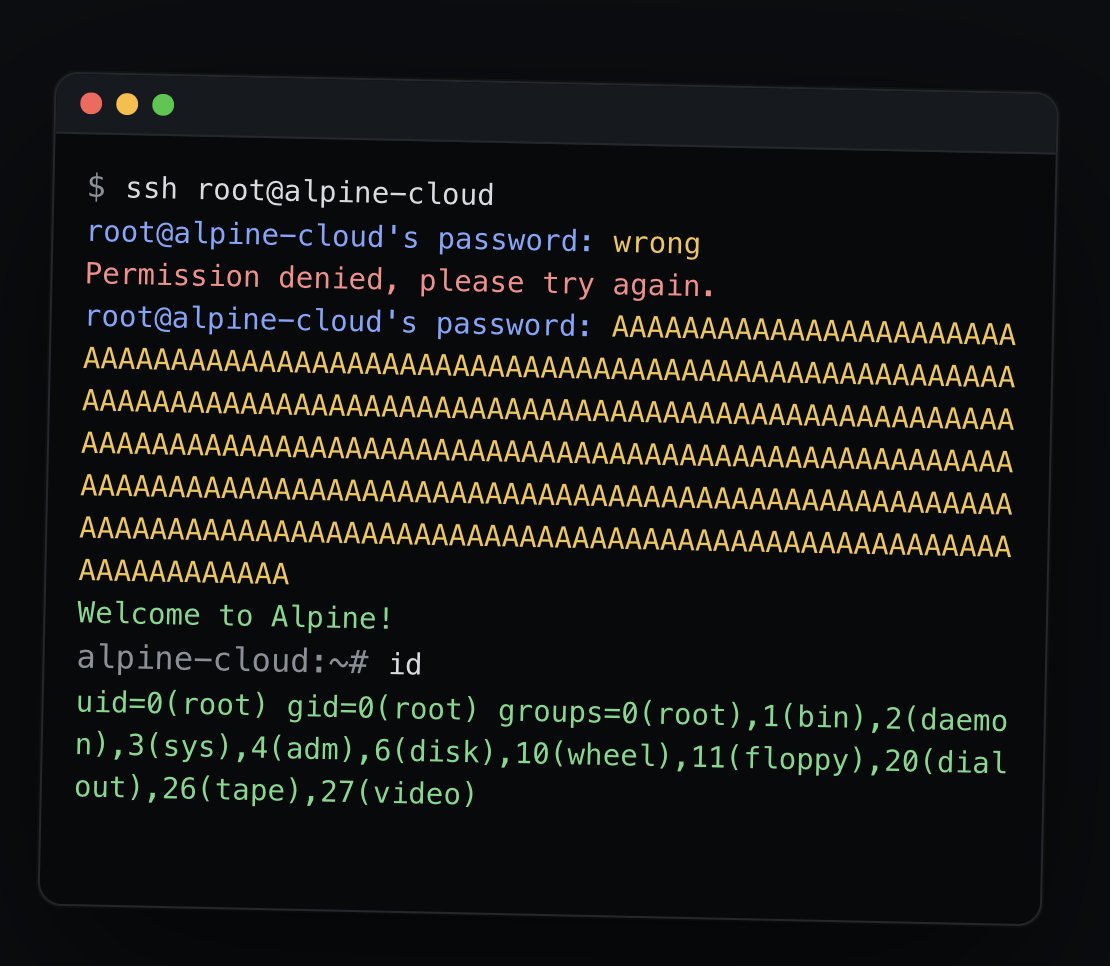
Trying to scan for the https://t.co/JqAqPRbonZ authentication bypass? SSHamble v0.5.0 has you covered, with a helpful PR from Paul Asadoorian (@securityweekly)! Code at https://t.co/kVrGa1qwKb (with a bonus CoreOS check and Dockerfiles to validate both issues end-to-end)
someone that is at the Whitehouse between 5pm and midnight has some compromised devices.
Or at least some that are providing residential proxy access to botnets.