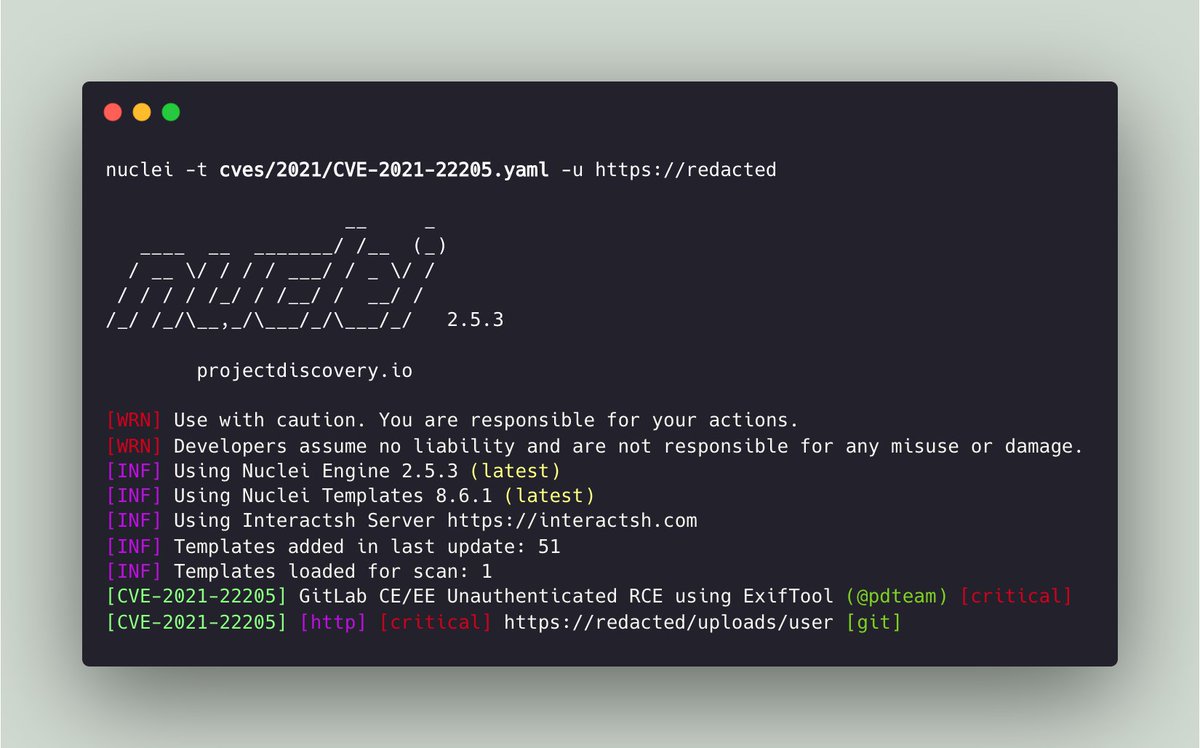
Wanna know if the web app you are building is secure? Here is a tutorial on how to test the security of any web app in 3 min with nuclei, an open-source and developer-friendly app security scanner https://t.co/yO4mshOqSl (👋 @pdnuclei)
You don't need to use a proxy/vpn when blocked by a WAF while testing a webapp, you can use IP Rotate extension from burp suite and all the traffic is then routed though API gateway endpoints in the regions you selected. Useful when aggressive WAFs block your IP #bugbountytips
I've re-written gau! This includes speed improvements, a new provider (urlscan), loading options from configuration files, new filter support, socks5 proxy support, and more!
Make sure to grab the new version!
https://t.co/dZCcjwPG9T
Did you know that the SecurityTrails Free App allows you to simply input a hostname and get data on:
👉 DNS records (A, AAAA, MX, NS, TXT, SOA)
👉 Historical records
👉 Subdomains
👉 Hosted domains per IP
👉 IP neighbours
Try it out for yourself: https://t.co/5kuYFeRVoq
Give https://t.co/A230fvcUao an IP address and it will tell you (for free) the:
🌏 Geolocation
🏬 Company
☎️ ISP
📱 Mobile carrier
⛔️ Abuse contact
🔗 Associated domain
⏰ Timezone
🔥 And more!
Try it! https://t.co/Pvyuyyg9sK
Or from a terminal:
curl https://t.co/ffxuQdtaGm
The account that pushed the contract to Github (commit 46977c750b3378b422016ad2a7613cfa0caf907d
SquidGame <[email protected]>
Date: Thu Oct 14 16:50:11 2021 +0800)
interestingly they forgot to remove their MX Record which points to @OVHcloud 👀
#SquidGameBsc#squid#rugpull