As the TeamPCP cybercrime gang carried out its spree of software supply chain hacking this year, it had been infiltrated by an undercover analyst from Google's threat intel group. Google watched from the inside, warned victims, even disrupted extortions. https://t.co/sdHYT4fQ5z
...and we're back.
@juanandres_gs with A Synoptic Sense. A talk about what cybersecurity actually is today.
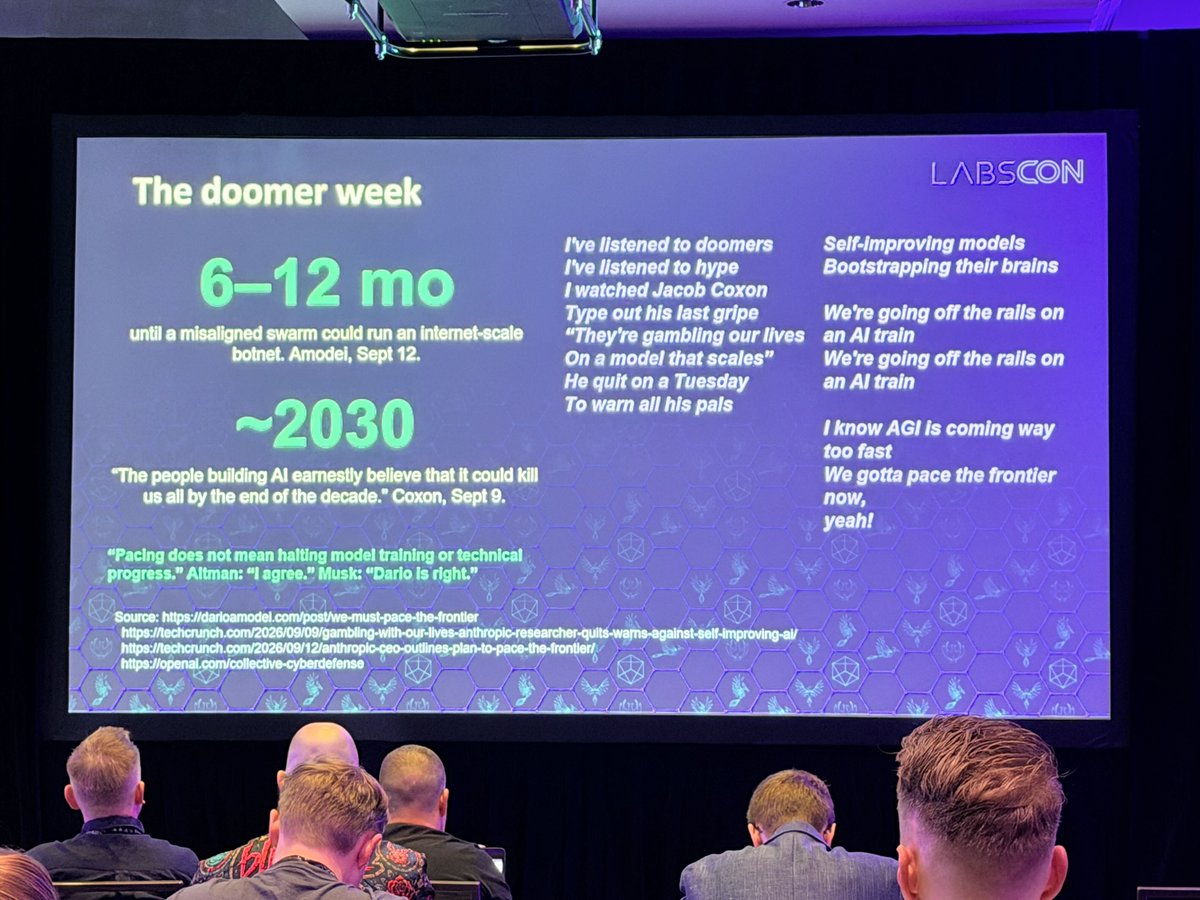
"alignment is the founding lie of this [AI] bullshit"
Next up: One of our first, and longest, supporter to @labscon_io, Katie Moussouris @LutaSecurity
“We can't fight AI with human speeds, you need to fight it with other AI” ~Katie Moussouris
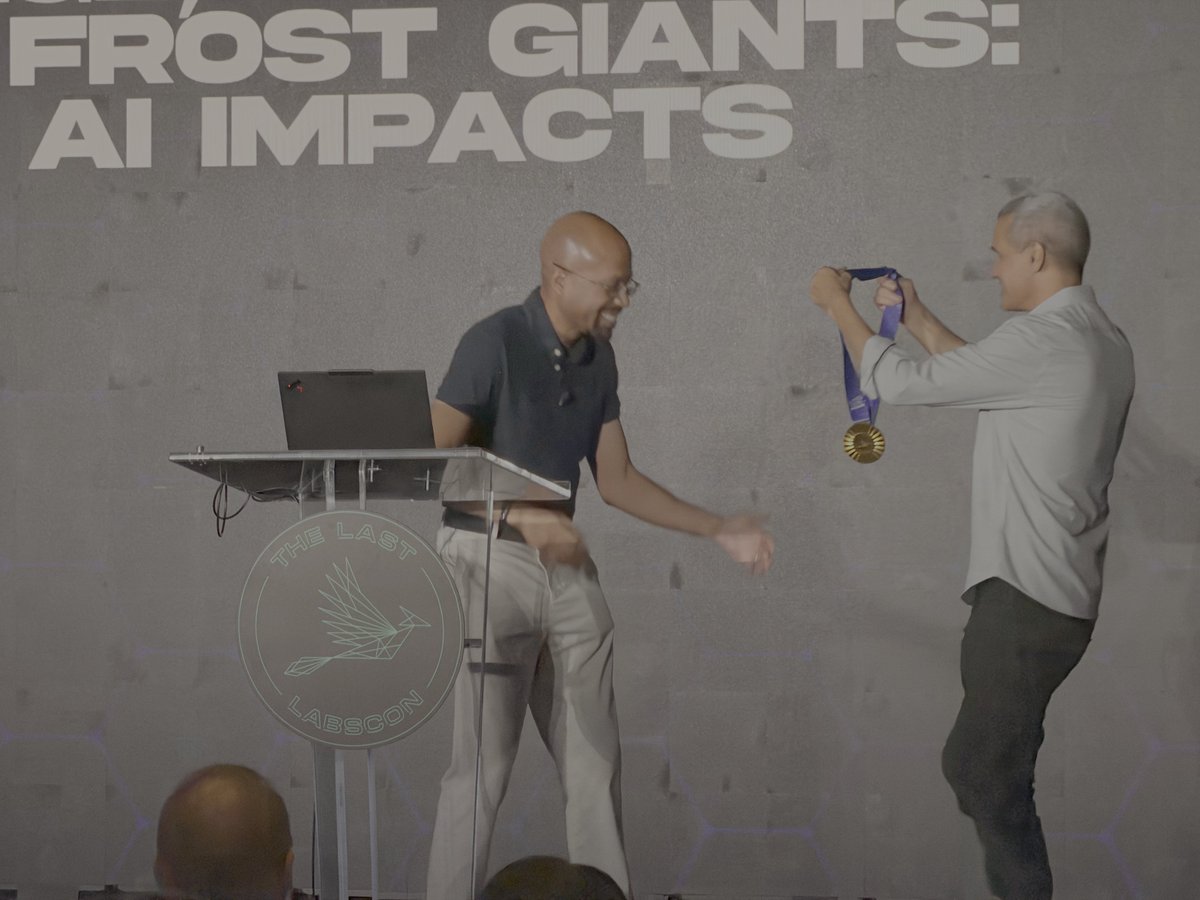
A huge welcome to our opening @labscon_io keynote speaker, the legend Professor James Mickens.
"Happiness Nullification, Intergalactic Carnage, and the Release of Multiple Frost Giants: A Sober Analysis of AI Impacts."
An honest, hilarious, and unique look into the emergence of AI
@StateFarm is the absolute worst. 2 weeks to get a claims adjuster to inspect damage (that was not due to a natural disaster). Completely unacceptable.
Having read through some of the Microsoft SharePoint vulnerability stories and facts, I had some topline observations that I think could add to the conversation:
1/ Cloud-based SharePoint in M365 was not impacted
2/ On-premise SharePoint installations were impacted, and namely older, unpatched ones.
3/ For those on-premise SharePoint customers, Microsoft released patches in a few days and communicated via the new SFI protocols
4/ Microsoft has a 90 day SLA and it appears it met. The issue was identified May 16, patch was available 3 weeks later. After this the attacks started on unpatched systems. MS found new exploits, and updated patch came out July 19.
5/ Interim mitigations like anti-malware scans appear to have stopped 85% of the on-premise, attacked servers (bummer to be the 15%).
Security is very much a spy versus spy, tit for tat operation. I get challenged a lot about this, but it rears its ugly head again and again, and I stick to my guns.
Net-net: patch systems immediately and, if you can’t operationalize this effectively, then consider going to the cloud, understanding the pros and cons of that.
In response to concerns raised earlier this week about US-supervised foreign engineers, Microsoft has made changes to our support for US Government customers to assure that no China-based engineering teams are providing technical assistance for DoD Government cloud and related services.
We remain committed to providing the most secure services possible to the US government, including working with our national security partners to evaluate and adjust our security protocols as needed.
Microsoft finds a team within Sandworm has been carrying out widespread initial access operations on behalf of the GRU group and focused on US, UK, Canada and Australia networks over 2024, exploiting Connectwise ScreenConnect and Fortinet FortiClient EMS. https://t.co/dnNo8nrS1a
Microsoft is publishing research into a subgroup within the Russian state actor Seashell Blizzard and its multiyear initial access operation, tracked by Microsoft Threat Intelligence as the "BadPilot campaign". https://t.co/hQgVpstRGl
Microsoft Threat Intelligence has observed North Korean state actor Emerald Sleet (also known as Kimsuky and VELVET CHOLLIMA) using a new tactic: tricking targets into running PowerShell as an administrator and then pasting and running code provided by the threat actor.
1️⃣9️⃣ more days until #CYBERWARCON 🎉
Keep your eyes peeled for an email with the agenda & other info you won’t want to miss! 📥
Register ASAP at https://t.co/12b29mb4fu‼️