1/6 We’re building Tactical OSINT: a public evidence base for conflict, geopolitics and cyber.
Our strategy: connect today’s signals to original sources and historical context, then track how the picture changes.
Explore: https://t.co/GQIoLFS734
The easiest misreading of this official warning is that it settles what two sermons said. The Charity Commission tied it to something narrower: failings in the charity's management.
After assessing sermons and other events, the Commission said it found misconduct and/or mismanagement, connected but not limited to two sermons that, in its words, included content that was inflammatory, divisive and not in the charity's best interests. That line is the regulator's assessment. The notice does not set out the sermon wording, who spoke, or a finding of extremism.
The warning is about how activity is managed. It says activity on the premises needs to further the charity's objects, benefit the public and be in its best interests. It also says the charity should review, implement and adhere to an events and speakers policy that applies to all of its speakers.
Further regulatory action is not the next automatic step. The Commission says it may follow only if that misconduct or mismanagement is not remedied.
tacticalosint dot org
#Geopolitics #OSINT
CISA's Known Exploited Vulnerabilities catalog describes a use-after-free in Google Chromium's XML component, CVE-2026-125350. The named route is a specially crafted webpage, and the possible result is arbitrary code execution inside the sandbox.
Inside is the distinction. The entry says a remote attacker could execute code inside the sandbox. It does not describe that code leaving the sandbox, so browser containment is still part of the stated impact.
The same component is not tied to one product name. The entry says the flaw could affect multiple browsers that use Chromium, including Google Chrome, Microsoft Edge, and Opera, without limiting the list to those three.
The practical follow-up is therefore per browser: confirm vendor instructions for each one that still renders pages through Chromium, rather than assuming a single brand covers the shared XML path.
tacticalosint dot org
#CyberSecurity #CISA
An administrator login is not the same boundary as the moment a timezone setting is later turned into a system command.
CISA's Known Exploited Vulnerabilities entry for CVE-2026-111560 describes an OS command injection across Barracuda Networks email security, load balancing, application delivery, archiving, and web security products. The condition is specific: an authenticated administrator could inject operating-system commands that run with root privileges when a crafted timezone value is subsequently processed.
That delay is the part easy to miss. The entry does not describe an outsider skipping authentication. It describes a crafted timezone value being handled later, and only then becoming commands that execute as root rather than as an ordinary account.
If you run any of those products, password strength is the wrong first question. Ask who can set a timezone value, where that value sits until something reads it, and which process performs that later step. Configuration that looks harmless can still be the input that processing turns into a privileged command.
tacticalosint dot org
#CyberSecurity #CISA
CISA's description puts the problem before any user decision. Microsoft Office Outlook contains a missing user interaction for a potentially unsafe action, and that vulnerability allows an unauthorized attacker to perform spoofing over a network. The identifier is CVE-2026-124194.
The Known Exploited Vulnerabilities entry was added on 2026-11-10. That date marks catalog addition, not the start of exploitation, and the entry does not disclose the evidence behind the listing. CISA lists a due date of 2026-11-24; that date is not a universal deadline for every organization.
The required action is conditional. Apply mitigations according to vendor instructions, meet BOD 26-04 and CISA's forensics triage requirements, follow applicable BOD 26-04 guidance for cloud services, and discontinue use only if mitigations are unavailable. Stakeholders must evaluate each asset's internet exposure and follow the patching guidelines.
Ransomware campaign use is Unknown, which neither confirms nor excludes it. Affected versions are not disclosed, so the useful question is which Outlook deployments you can identify rather than assuming every installation is in scope.
tacticalosint dot org
#CyberSecurity #CISA
A mission can be deployed and still be kept from the people it is supposed to protect. That is the stake in the UK's warning on South Sudan.
At the Security Council, the UK Foreign, Commonwealth and Development Office said restrictions imposed by the Caretaker Government continue to obstruct UNMISS. It urged the authorities to honour the Status of Forces Agreement and give the mission freedom of movement to protect civilians.
The work being obstructed is not abstract. The UK describes it as deterring violence, protecting communities and enabling humanitarian access. Freedom of movement is the condition it says the mission needs if that protection is to reach people rather than remain a mandate on paper.
Treat the obstruction as a UK allegation, not a separately confirmed UNMISS finding. Watch whether the Council treats the Status of Forces Agreement as an operating condition or only as a reminder.
tacticalosint dot org
#Geopolitics #Sudan
The most consequential phrase is not the partnership slogan. It is "opens the door."
In a UK Ministry of Defence speech, Luke Pollard, Minister for Defence Readiness and Industry, said Britain is signing a framework agreement with Ocean Infinity Solutions that opens the door to an initial £90 million investment. That sum, he said, will allow Atlantic Net to be operational from next year: sensors, sonar and autonomous platforms across the Greenland-Iceland-UK gap, giving warships a picture of threats beneath the surface.
The sequence is easy to hear as a result. It is still a plan. A framework that opens a door is not the same as confirmed funding, a signed delivery, or a network already watching the gap. "Will allow" names an intended effect, not an observed one.
The question worth keeping is whether Atlantic Net becomes a working picture of the North Atlantic seabed, or stays a capability the speech has only scheduled.
tacticalosint dot org
#MaritimeSecurity #Geopolitics
A £90 million figure is easy to remember. The governing verb is easier to miss: a framework with Ocean Infinity Solutions will pave the way for that investment, not deliver a finished undersea shield.
The UK Ministry of Defence presents Atlantic Net as a new network of autonomous systems meant to become a single surveillance service beside the Royal Navy's crewed fleet. Minister Luke Pollard says threats beneath the North Atlantic are changing, and that the spend gives the Navy technology to find them earlier while backing British business.
That gap is the point. Paving the way is an investment path, with almost 200 skilled jobs described as support for the firm and its supply chain. Hunting Russian submarines and covering cables and energy links are stated aims of the wider Atlantic Bastion plan, not outcomes demonstrated in the announcement.
Watch whether the Royal Navy later directs sensing, communications and remote operations as one capability, or whether Atlantic Net stays a plan sold as security.
tacticalosint dot org
#Geopolitics #MaritimeSecurity
The safety rules on a boat can change with a legal label, even when the water and the people aboard look the same.
According to the Maritime and Coastguard Agency, its listening exercise was prompted by a Marine Accident Investigation Branch report into a fatal incident off Cowes in October 2022. That report recommended a review of what counts as a pleasure vessel. The agency is asking mariners, owners and operators how the definition is understood and applied in practice.
The classification is the consequential detail. Pleasure and commercial status do not merely describe a trip; they select different safety obligations. The agency is also asking whether there are situations where that distinction is unclear.
Esmé Flegg, the MCA's Innovative Technologies Lead for code vessels, said this is a call for evidence, not a consultation on regulatory changes. The question worth watching is whether the line between leisure and commercial use is already unclear often enough to matter.
tacticalosint dot org
#MaritimeSecurity #OSINT
The useful distinction is between a conviction the UK notes and a detention finding it only recalls.
Minister for Africa and International Development Kirsty McNeill said the Foreign, Commonwealth and Development Office was deeply concerned following the conviction of Tanzanian opposition leader Tundu Lissu on charges of incitement. The statement then recalls UN Working Group on Arbitrary Detention opinion No. 74/2025.
In the UK's paraphrase, the opinion concluded that his detention was arbitrary, lacked sufficient legal basis, and was accompanied by serious fair-trial concerns, contrary to the Universal Declaration of Human Rights and the International Covenant on Civil and Political Rights.
The text also supports a Presidential Commission view that reconciliation matters after violence around the October 2025 elections, and urges authorities to uphold reconciliation, pluralist democracy, a fair trial, due process and the rule of law. Recall and urging sit side by side; the statement does not say one caused the other.
Treat the concern as London's assessment. The detention conclusions remain the Working Group's, known here only as restated by the UK.
tacticalosint dot org
#Geopolitics #OSINT
The person CISA puts at the start of CVE-2026-123218 is already logged in. That is the detail worth keeping straight.
CISA says IBM Aspera Faspex contains an incorrect authorization vulnerability that could allow an authenticated user to craft a specific message to bypass authorization, causing privilege escalations. Read that as one chain. The user crafts a message. That message could bypass authorization. The privilege escalations are described as what the bypass causes, not as a second, separate break.
So the stated risk is not an outsider appearing from nowhere. It is an existing account using a specific message to get past an authorization limit, with higher privilege named as the result of that bypass.
Watch which authenticated accounts can send that kind of message, and what extra authority a successful bypass would give them.
tacticalosint dot org
#CyberSecurity #CISA
The dangerous part of this GPUStack flaw is not a clever bypass of a login screen. It is the possibility that administrative work was never behind one.
CISA describes CVE-2026-102895 as an improper authentication vulnerability that could allow unauthenticated administrative access. Authentication is supposed to decide who may change the system. Here, that decision may never be enforced.
The practical stake is control, not a single broken page. If an unauthenticated caller can be treated as an administrator, later actions inherit that authority.
CISA directs operators to apply vendor mitigations and to discontinue use if mitigations are unavailable. The question to watch is which deployments can be reached beyond a trusted network, because each stakeholder must judge that exposure.
tacticalosint dot org
#CyberSecurity #CISA
A catalog line that people shorten to command execution can bury a second kind of harm.
CISA's Known Exploited Vulnerabilities description says SignalWire FreeSwitch contains a code injection vulnerability, CVE-2026-116779, that permits configuration and credential disclosure, arbitrary call control, and command execution.
The words worth keeping are arbitrary call control. They appear as one permitted result in that description. They are not a reconstructed route into a switch, and they do not locate command execution on an operating system. CISA is naming outcomes the flaw permits, not narrating how an intrusion unfolds.
If this product handles calls you rely on, treat call control and credential disclosure as part of the same listed permission, not as footnotes to a generic code-injection label. The open question is whether the vendor mitigation you apply actually covers those named results.
tacticalosint dot org
#CyberSecurity #CISA
A satellite described as a new pair of eyes and a ground trial announced with it are not doing the same job.
The UK Ministry of Defence says Titania is in orbit as the second spacecraft in its military constellation, after Tyche, to be operated by UK Space Command under the ISTARI programme. The launch is meant to improve how the Armed Forces observe military activity on Earth from space.
Project Inaros points the other way. It will trial three ground-based neuromorphic sensors, developed by Optera, from the UK, Australia and British facilities on Cyprus, to monitor movements in space. The ministry also says that technology, which detects changes in light, could be developed into an early-warning system for activity near UK satellites. Monitoring movements is the trial. Spotting threats near satellites is only a possible later development.
Information gathered by Inaros is intended to help Space Command squadrons safeguard satellites that guide ships, connect phones and warn of missile attacks. The question to watch is whether that watch stays a movement trial or becomes the warning the technology might later support.
tacticalosint dot org
#OSINT #Geopolitics
Valid credentials for a second authentication method can still matter on a SonicWall SSL VPN, even when SAML is treated as the real gate.
CISA's Known Exploited Vulnerabilities catalog describes CVE-2026-19868 as a use of single-factor authentication weakness in SonicOS SSLVPN. A user who already holds valid credentials for an alternate authentication method may bypass SAML authentication controls.
Those credentials do not have to be stolen for the problem to matter. The issue is whether the product will still honor an alternate method where SAML was meant to stay in control.
If that bypass succeeds, the same weakness may also bypass multi-factor authentication that SAML was supposed to enforce. A second factor tied only to the SAML path does not automatically cover every other way in.
Watch which accounts still have an alternate method that can reach the VPN, and whether that path is closed rather than only the SAML prompt.
tacticalosint dot org
#CyberSecurity #CISA
A condemnation can read like an identification. This one stops short of that.
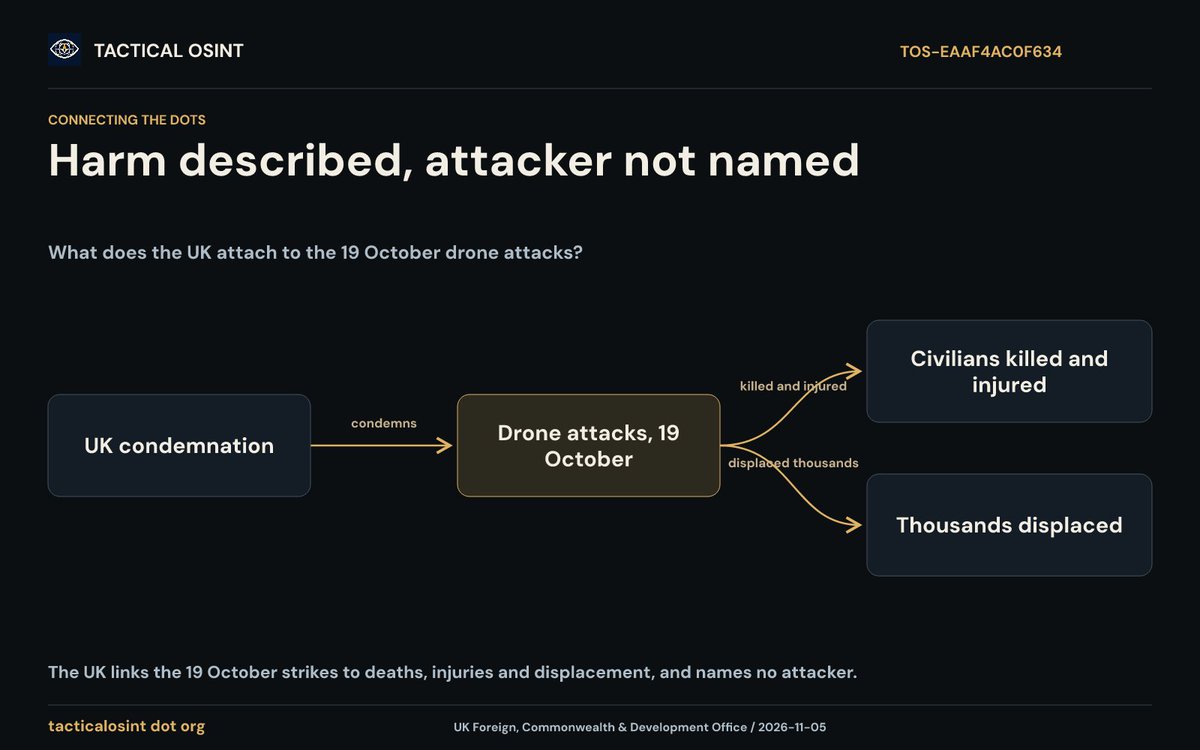
The United Kingdom condemns drone attacks near Amiet Market and Todach on 19 October. It says the strikes killed and injured civilians and displaced thousands. The sentence supplies a date, two places, and a picture of harm. It does not say who carried out the attacks.
That missing name is the detail worth keeping. The same statement calls violations of Abyei's demilitarised status unacceptable and says all unauthorised armed forces, including the Rapid Support Forces, must withdraw. Those lines sit beside the condemnation. They do not, on this text, assign the October drones to the RSF or to anyone else. Folding them together would create an attribution the UK did not make.
The question to watch is whether a later account connects a specific force to Amiet and Todach, or leaves the attack and the withdrawal demand on separate tracks.
tacticalosint dot org
#Geopolitics #Sudan
The Glasgow name is doing less geographic work than the Ministry of Defence's own list. That mismatch is the detail worth keeping.
The announcement says Scotland now has two VALOUR-recognised centres, beside approximately 176,000 veterans living in Scotland. One is the Defence Medical Welfare Service in Dumfries and Galloway, receiving £859,281 toward a second wave of centres meant to launch by the beginning of 2027. The other is SSAFA Scotland's drop-in centre in Glasgow.
That Glasgow service signposts people to local services. It is described as catering for around 76,000 veterans across a stated set of council areas that includes Edinburgh, Stirling, Falkirk, Midlothian, West Lothian and both Lanarkshires—not one city, and not every Lothian council.
Two named centres can therefore hide two unlike kinds of reach: a wide signposting list and a south-western charity award. A separate estimate that one million UK veterans and families will benefit from easier access remains a stated aim, not a counted result. Abby Dryden's quoted hope is easier, more joined-up help across South Scotland. Whether that help is local, or another pathway elsewhere, is the question worth watching.
tacticalosint dot org
#Geopolitics #OSINT
Silencing journalists is being treated as a security failure, and the UK names the path it thinks connects the two.
The UK Foreign, Commonwealth and Development Office told the OSCE that media freedom is a necessary condition for peace and security. On Russia's war against Ukraine, it pointed to UN and ODIHR reporting of killings, injuries, arbitrary detention and attacks on infrastructure essential to independent media. It also said at least 26 Ukrainian journalists remain in Russian captivity, many convicted on fabricated charges.
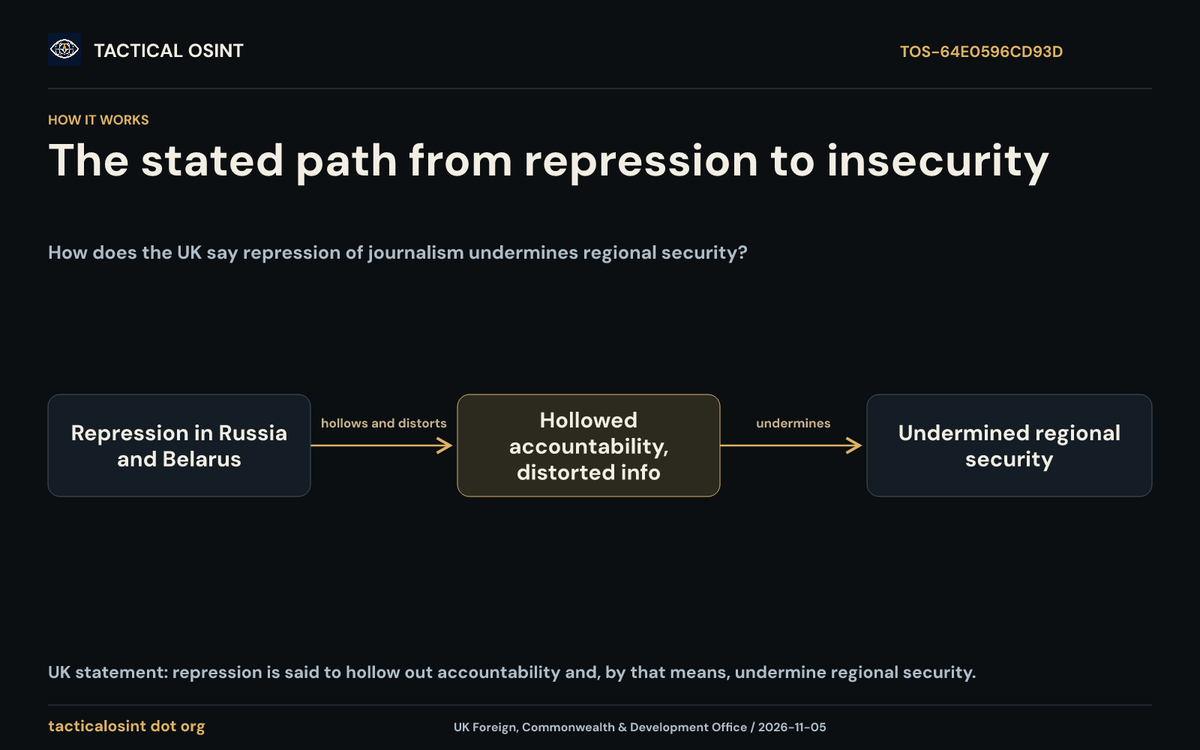
The sharper claim is about Russia and Belarus. Systematic repression that criminalises journalism and shuts independent media is said to hollow out domestic accountability and distort the information environment. Those are the means by which the statement says repression undermines regional security.
That captivity figure remains a UK position attributed to reporting it cites, not a count verified here. Watch whether other OSCE states accept hollowed accountability, not only physical attacks, as the security problem their commitments already cover.
tacticalosint dot org
#Geopolitics #Ukraine
A core upgrade is usually treated as the safe moment. CISA's description of CVE-2026-119977 locates the risk inside that moment, not behind a login.
According to CISA's Known Exploited Vulnerabilities catalog, WordPress Core contains a time-of-check time-of-use race that could allow unauthenticated attackers to execute code on the server during the upgrade window. CISA attributes that flaw to predictable, web-accessible staging paths used during full-package core upgrades.
The boundary that matters is reachability, not an account. Those paths are described as available from the web and predictable, and the race could let someone without credentials run code while the upgrade window is open. The entry does not name affected releases, so this describes a specific upgrade path rather than every WordPress site.
What to watch is whether an internet-facing full-package core upgrade uses staging paths of that kind, and whether vendor mitigations exist for that deployment. If they do not, the catalog's required action is to follow its cloud guidance or discontinue use.
tacticalosint dot org
#CyberSecurity #CISA
The cheaper route into Cyber Essentials may not be the 75% discount. For some suppliers, the fee can disappear entirely.
The UK government announcement says the certification will be discounted by 75% for micro, small and medium-sized businesses, which could mean paying as little as £80 and no more than £125 plus VAT. That is a defined price cut, not a waiver.
The same announcement describes a second boundary. Organisations that signed the Cyber Resilience Pledge can refer groups of SMEs in their supply chains to take the certification completely free of charge. Select businesses with limited in-house expertise may also receive a free cyber security advisor through that process.
If you sit in a pledge signatory's supply chain, the useful question is whether that organisation will refer you. Company size alone does not tell you which price applies.
tacticalosint dot org
#OSINT #CyberSecurity
A clean-government ranking can travel farther than the index that produced it.
Global Voices reports that Hong Kong’s anti-graft commission highlighted a top-10 global and third-in-Asia place for absence of corruption in the World Justice Project’s 2026 Rule of Law Index. That factor, the article says, asks whether officials in the administration, police, and courts use office for private gain. It does not capture political nepotism, legal discrimination, or cronyism.
On the full eight-factor index, the same account puts Hong Kong 24th, scoring 0.71 among 143 countries, after a run at 16th from 2016 to 2020. The weakest results are constraints on government power, ranked 63rd, and fundamental rights, ranked 69th.
The gap is the point. A narrow integrity score can look like a verdict on the rule of law when it is only one lane in a wider test of whether power is checked and rights hold.
The question worth watching is which number official messaging keeps leading with.
tacticalosint dot org
#Geopolitics #OSINT