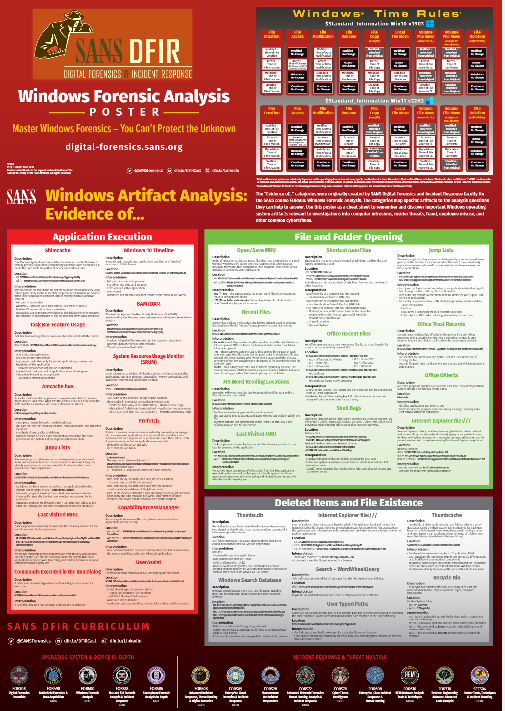
The #WindowsForensicAnalysis poster has been revised to support modern Windows investigations! Use it as a cheat sheet of WinXP - Windows 11 operating system artifacts & a means to discover important artifacts.
Download now! 👉https://t.co/NdbxCmcRjh
@chadtilbury@4enzikat0r
Want to Win a FREE @tryhackme Subscription?
3 x 1 month Vouchers up for grabs🙌
For a chance to win:
✅ Like this tweet
✅ Retweet for more reach
✅ Drop me a follow
✅ Comment why you need a sub
1 Week from now 3 winners will be chosen
#infosec#infosecurity#Pentesting
A Deep Dive into Wireshark for Security Analysts - Complete Wireshark Course for Beginners in Cybersecurity by @daycyberwox of @CyberwoxAcademy
https://t.co/swiKT6PGTL
I came across this while searching for knowledge about incident handling in SOC. As a result, I got an overview of what is done in each phase of IHR.
#soc#incidentresponse#socanalyst
Success in bug bounties comes down to:
💪 Persistence
🧠 Knowledge
🍀 Luck
The luck factor can be decreased with persistence, and knowledge can be achieved with persistence. So really, success in bug bounties comes down to one thing:
💪 Persistence
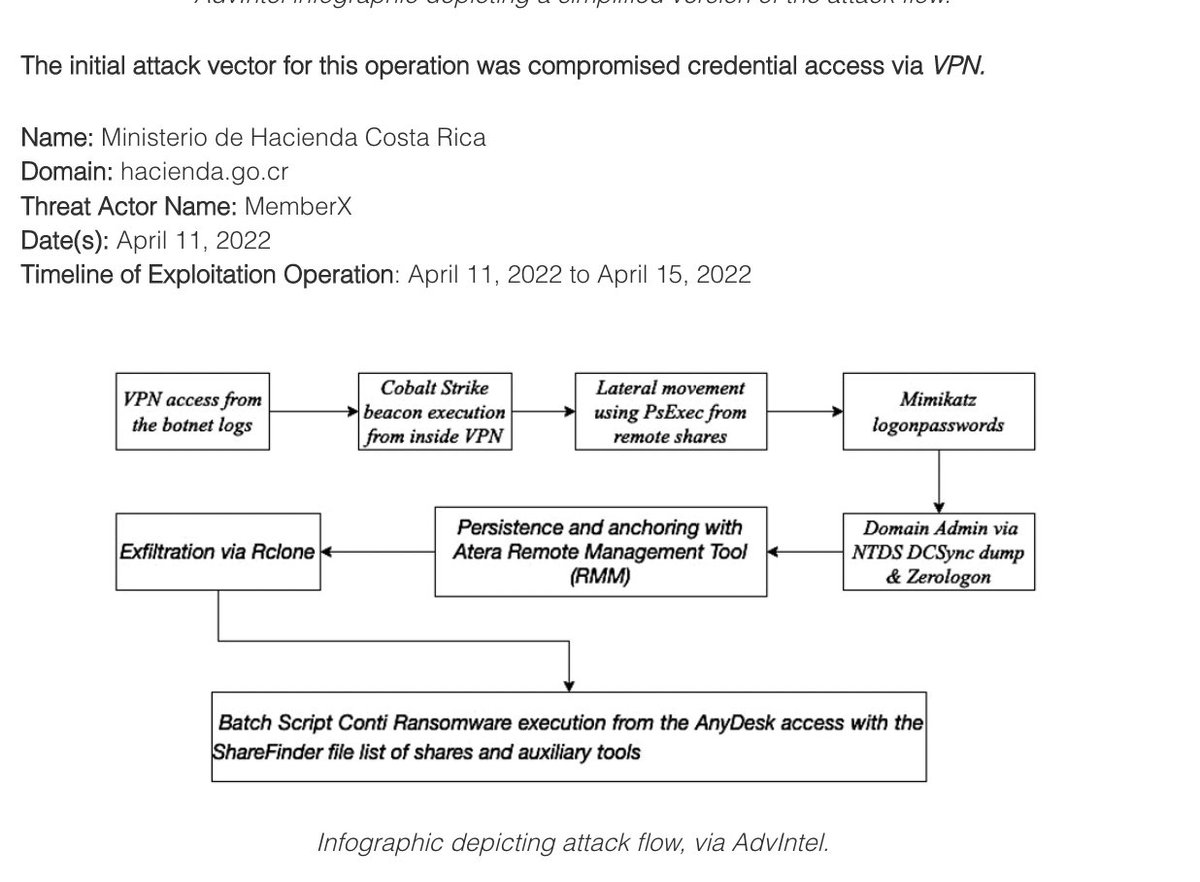
🔥Breaking Blog: Anatomy of Attack: Truth Behind the Costa Rica Government [#Conti] #Ransomware 5-Day Intrusion
➡️From initial access to ransomware deployment --> more than 10+ #CobaltStrike sessions with #AteraRMM deployed part of intrusion w/ Rclone
https://t.co/RSlRl9vdce
Grafana published a high severity security advisory - "Grafana account takeover via OAuth vulnerability" This was recently discovered & disclosed by us.
https://t.co/HPMKM3pkWa