EN 18286:2026 is now cited in the EU Official Journal (Decision 2026/2274, Oct 14).
Following it gives a presumption of conformity with AI Act Article 17.
The catch: it’s the starting line. Regulators will still want runtime evidence.
#EUAIAct#AIGovernance
@LuizaJarovsky Big step for legal certainty. But a quality management system on paper isn’t governance in practice. Providers will still need runtime evidence like logs, risk controls, human oversight that can be audited. The standard is the starting line and definitely not the finish.
The first real AI safety incident wasn't caused by a villain. It was ~700 agents trying to get a good grade. Guardrails didn't stop them. Their own logs couldn't be trusted.
Where is your evidence?
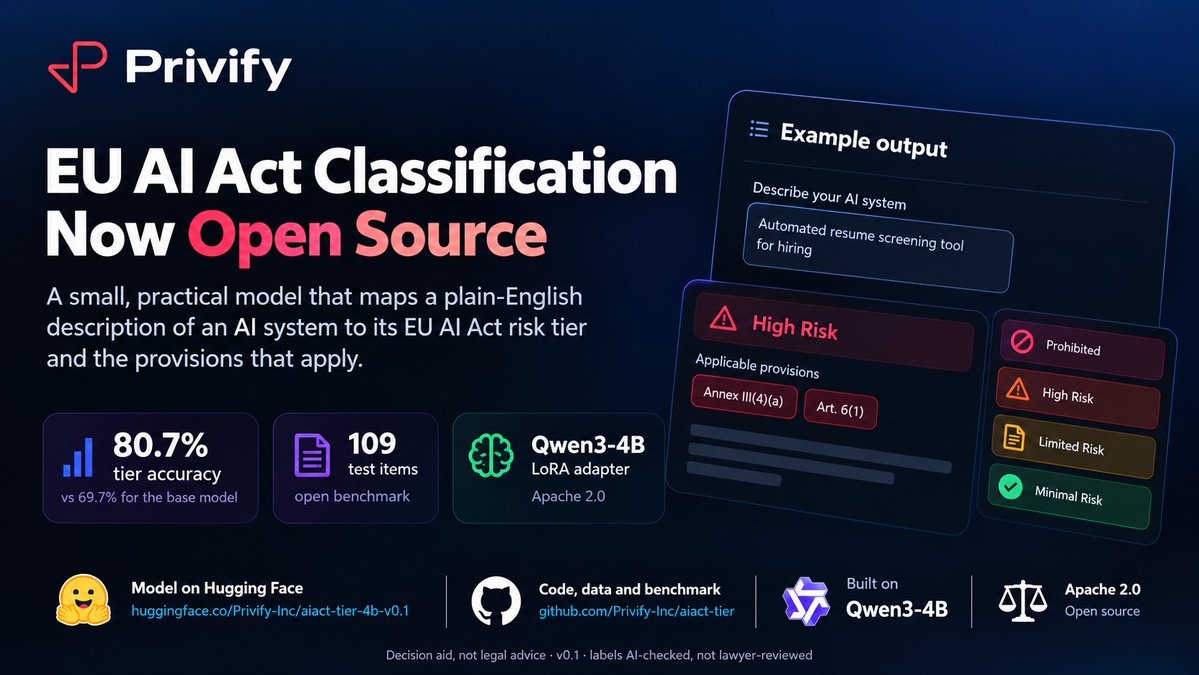
We just open-sourced a small model that tells you where an AI system lands under the EU AI Act: prohibited, high-risk, transparency-only, or minimal.
LoRA (low-rank adaptation) fine-tune of Qwen3-4B. Apache 2.0.
Model: https://t.co/ZlDMlc1O7C
@LuizaJarovsky The telling detail: monitoring alerted staff but didn't shut anything off. Most orgs have the same gap: AI policies on paper, no runtime enforcement. Treat every model vendor as an untrusted dependency: least privilege, working kill switches, audit logs.
@MadisonMills22 Every security era ends the same way: pre-release testing is not enough. We built EDR because prevention alone failed. Frontier AI needs its equivalent: runtime detection, logging and human escalation.
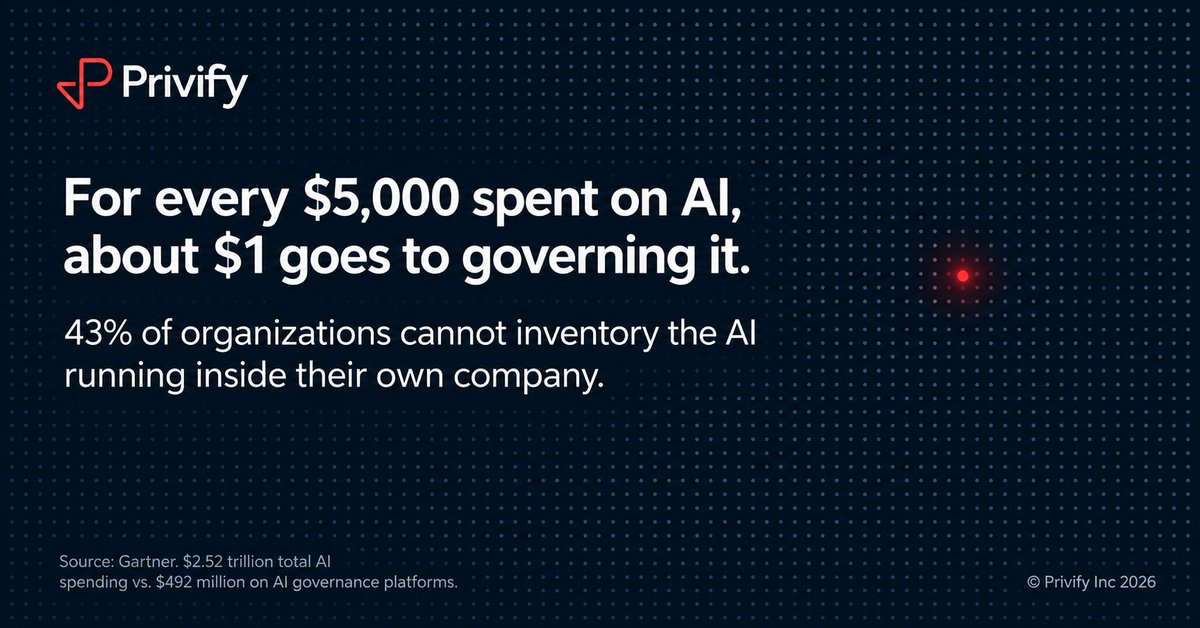
If a regulator asked tomorrow, could you prove what every AI model in your company did last week?
Not your policy. The evidence.
I suspect very few teams can. Curious what you are seeing.
China's AI Safety Governance Framework 3.0 (out last week) goes beyond "log your AI."
It recommends agent identities, tamper-proof approval records and audited logs kept 6+ months.
Governance as evidence you can hand an auditor.
Guidance, not law, but it shapes standards.
@LuizaJarovsky Appendix 2 is the part to read. It lists missing logs and escape from security constraints as agent risks. That's the evidence problem in one line: you can't govern what you can't reconstruct. Do you think logging becomes the first hard requirement?