I built Vulnschool A free, deliberately vulnerable LMS built for Security research and penetration testing
SQLi. XSS. IDOR. JWT attacks. SSRF. Business logic flaws.
No setup headache. Just hack, learn, repeat.
🔗 https://t.co/ANS1mDsRFq
GPT 5.6 Terra and uncensored DeepSeek 4.1 Flash are FREEEE on WusRouter
one gateway key, and the whole model list is public so you can eyeball it before you sign anything
what you get:
> GPT 5.6 Terra free
> uncensored DeepSeek 4.1 Flash free
> GLM 5.3 Flash free, two ids
> Qwen 3 Coder and Cohere North Mini Code free
> 24 jailbreak-tuned variants if that's your lane
> 65 models listed in total
how to claim (under 2 min):
step 1: go to https://t.co/SGjqhUTfQE
step 2: open the playground and try a free model first
step 3: grab an API key
step 4: set base URL to https://t.co/t1v1BZ3qvc
works in any OpenAI-compatible client, Cursor, Claude Code, Codex, custom scripts
step 5: start coding
start on the free ids and see if your stack even notices the difference
important:
> this is a third-party proxy so don't send any sensitive data through it
> the jailbreak variants repackage frontier models, so expect those ids to rotate or vanish
> check the current free list before you build anything against it, it's a small gateway
I built a vulnerability scanner extension for Burp Suite by @PortSwigger
It scans all http traffic history for: XSS, IDOR, SQLi, & more
Skills-PoC-Finding 🔥
Watch the demo and give it a try👇
https://t.co/xWnYZbActg
Credit: @zack0x01_#bugbountytips#bugbountytip#bugbounty
𝗔𝗜 𝗿𝗲𝗱 𝘁𝗲𝗮𝗺𝗶𝗻𝗴 is now a must-have skill — and this GitHub guide (800+ ⭐) is the whole playbook:
NIST AI RMF, OWASP GenAI Top 10, MITRE ATLAS, 4-phase method, 13+ tools (PyRIT, Garak, promptfoo…).
https://t.co/M3KDurZ7H0
#AISecurity
New CloudPEASS release! K8s-PEAS is the new Red Team k8s script from https://t.co/BunOAU5Yox. Use it to find the permissions of a compromised principal in a kubernetes cluster during a Red Team.
If you want to learn kubernetes Red Teaming check: https://t.co/eHdruNo4UJ
nealbridges/vulnhunter: Agentic AI security scanner that hunts exploitable vulnerabilities like an adversary, proves them with executable PoCs, and fixes them test-first. A maintained fork of Capital One's VulnHunter, rebuilt f... https://t.co/OFBD93F9QB
THIS IS F**KING INSANE
I FOUND AN OPEN-SOURCE AI HACKING & RED-TEAMING FRAMEWORK CALLED G0DM0D3.
It comes loaded with jailbreaks, adversarial attacks, prompt transformation techniques, and multi model testing.
You can test 60+ AI models, compare their defenses, and find out which models crack under pressure.
It supports OpenRouter, Venice, Ollama, LM Studio, llama.cpp & vLLM.
Basically, an entire LLM security testing lab packed into one repo.
AI HACKING IS GETTING SERIOUS.
BOOKMARK this before someone take it down
REPO BELOW
I have open-sourced the full bug bounty workflow behind my hunting system.
It covers everything from initial recon to final duplicate convergence, including access, authenticated testing, browser workflows, evidence handling, escalation, triage, independent validation, and report preparation.
This is reference material for people who want to build.
It is not plug and play.
I am not providing setup support.
You will need to adapt every integration to your own environment.
If you put in that effort, it should give you a serious foundation and a lot of ideas for what an end-to-end AI hunting workflow can look like.
This took a lot of work to build and prepare for release.
If you find value in it, please leave a comment so more builders see it.
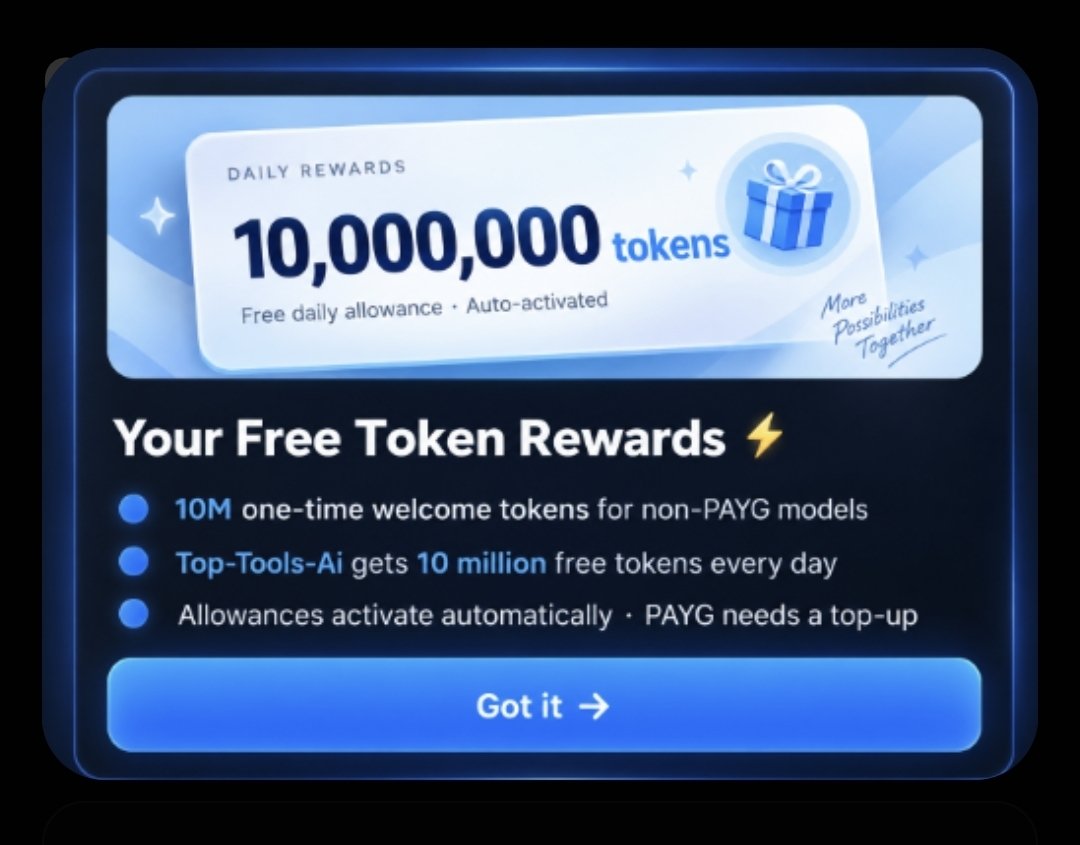
DeepSeek V4.1 Flash + 10M FREE tokens 😳
Top Tools AI gives you access to a bunch of AI models in one place
- DeepSeek V4.1 Flash
- Qwen 3.8 Max
- GLM 5.3
- MiniMax M3
- Claude Opus 5
- and many more
> up to 1M context
> vision + tool calling
> deep thinking
sign up: https://t.co/sz6wBf7ht6
grab the free tokens and start testing 👀