"Die Dokumentation „Naza: The Real Story“ ist eine Gegendarstellung zu den Vorwürfen des Films „Naza“. Nachdem sie auf YouTube nicht mehr verfügbar ist, stellen wir einen neuen Link bereit, über den der Film kostenlos angesehen werden kann."
https://t.co/kmRQL8yuz0
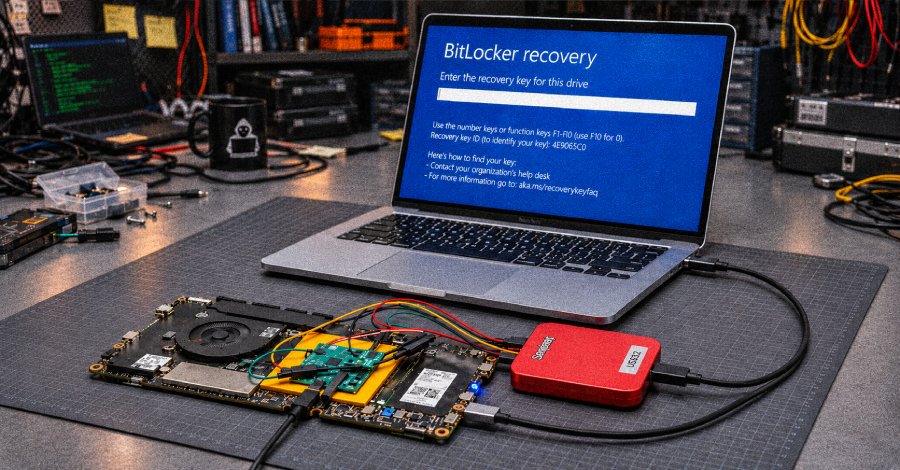
‼️ BREAKING - Researchers bypassed TPM lockout protections to Windows Hello and BitLocker PINs.
A flash-chip attack cuts brute-force times from YEARS to DAYS on affected AMD and Intel PCs.
Here's how it works → https://t.co/eQ3yEBGnpQ
This is f*cking insane: OpenAI co-founder Andrej Karpathy says a tiny 1B model can beat most of today's giant LLMs.
"A 1B model can be much more effective than most current LLMs. 90% of current models waste a ton of capacity and money on remembering stuff that doesn't matter"
In 64 seconds he explains why intelligence lives in the system around the model, not in its size.
Memorized Internet → Cognitive Core → Tools → Feedback Loop → Agent That Works
Save this before it gets lost in X's algorithms.
Everything below is free:
Neural Networks: Zero to Hero
Karpathy's own course, from scratch
https://t.co/43Htnj4go4
nanochat
Karpathy's "best ChatGPT that $100 can buy"
https://t.co/B0RlVzl1i9
Effective Harnesses for Long-Running Agents
The system around the model, by Anthropic
https://t.co/BAWfoVWQAx
Effective Context Engineering for AI Agents
What to feed the model and what to cut
https://t.co/dBVaoEVPNY
All of this costs $0
99% will keep waiting for a bigger model.
The 1% who build better systems will win with a smaller one.
Bookmark it and start with the first link tonight
The EU is worried Le Pen will win in France and end France’s financial support for Ukraine. The answer is very simple: Send $300 billion in frozen Russian funds to Kyiv NOW.
https://t.co/FXRn0e1se4
WordPress 7.1.5 is a security release with fixes for multiple issues. Update your sites immediately from the WordPress Dashboard. If a site supports automatic background updates, the process will begin automatically. https://t.co/0NkayX4F3u
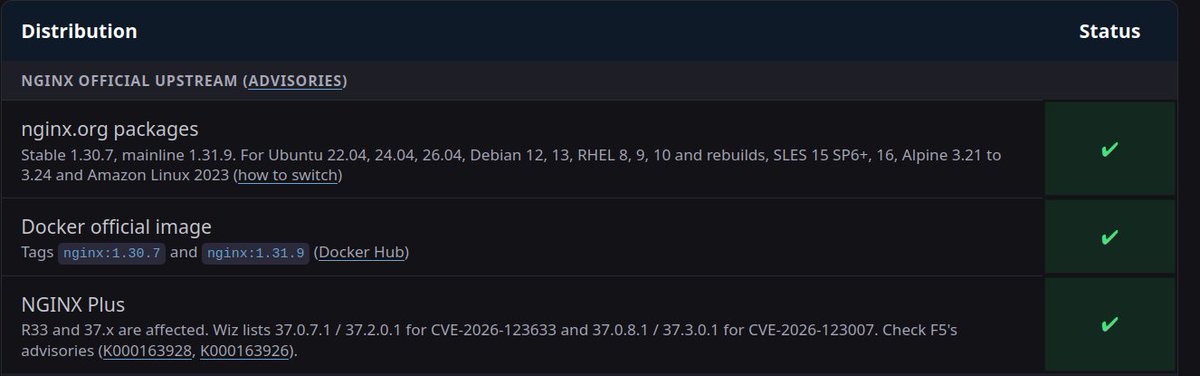
At this point, everyone should just switch to Nginx's official repos and patch instead of disabling HTTP/2, get it straight from the source
Patching/upstream instructions: https://t.co/NB7NfHr9Po
‼️ NGINX HTTP/2 Flaws Could Allow Memory Corruption and Remote Code Execution on Web Servers
Details: https://t.co/xKxzCTWF7f
Two critical vulnerabilities in NGINX could let remote attackers run code on vulnerable web servers without logging in. The flaws, tracked as CVE-2026-123633 and CVE-2026-123007, were disclosed on November 18, 2026.
Both require NGINX to accept HTTP/2 connections from clients, but the conditions differ. One affects certain reverse proxy setups, while the other can affect a server that does nothing more than serve static files.
The flaws are in NGINX itself, not the websites or APIs behind it. NGINX often handles HTTPS and routes incoming requests to several applications.
#cybersecurityNews #NGINX #Vulnerability