⚠️ 🇪🇨 🏛️ 🗄️ PREVENTIVE ALERT – ALLEGED DATA EXFILTRATION FROM THE ECUADORIAN MINISTRY OF LABOR (ACTOR: TERROAHOVER / TEAM PHEISITO)
[STATUS: ALLEGED / UNCONFIRMED / THREAT ACTOR: TERROAHOVER / TEAM PHEISITO / DATE: NOVEMBER 8, 2026]
Centralized cyber-intelligence systems have intercepted a post—framed as a political protest and disclosure—circulating on clandestine channels and social media (recorded on November 8, 2026). The post, attributed to the actor "TerroahOver," indicates a direct collaboration with "TeamPheisito" and "TerroahGroup." It claims the exfiltration of a 20.6 MB JSON file originating from the Ecuadorian Ministry of Labor and Development (https://t.co/FeOzQzFvJd).
Screenshots reveal the file's internal structure, which includes timestamps from November 2026, record identifiers, specific classification codes (EE-100), record acronyms, folio numbers, and references to related government services such as "https://t.co/BO6JyDzkT2." The data potentially exposes credentials, email addresses, and metadata belonging to Ecuadorian citizens.
It is strictly noted that the occurrence of this intrusion, the initial access vector, and the overall authenticity of the exposed records have not been officially confirmed by the Ecuadorian Ministry of Labor or government incident response centers.
Threat Actor: TerroahOver, in collaboration with TeamPheisito and TerroahGroup.
Victim : Ecuadorian Ministry of Labor and Development — 🇪🇨 Ecuador.
Sector: 🏛️ Government, Labor, Public Administration, and Citizen Records.
Publication Date: November 8, 2026.
Reported Volume: A 20.6 MB JSON-formatted repository containing thousands of structured records.
Nature of the Incident: Alleged compromise of ministerial systems, exfiltration of labor-related databases, and exploitation of the breach to exert political pressure on the government authorities of Ecuador.
🛡️ TECHNICAL PREVENTIVE AND CONTAINMENT RECOMMENDATIONS (SOC / CSIRT / GOVERNMENT)
Audit and Access Review for the SUT: The IT teams at the Ecuadorian Ministry of Labor must immediately isolate and audit the servers hosting the Unified Labor System (SUT) to verify the integrity of the databases and rule out unauthorized access.
Revocation of Exposed Credentials: Proactively invalidate user accounts and credentials found in the log samples to prevent them from being reused to access other government portals.
🖥️ CENTRALIZED THREAT MONITORING SYSTEM
Intelligence System: https://t.co/wk9bZJ2Nli
Quickly check your security at: https://t.co/QZhWp0kFrO
Inquiries and services: https://t.co/sx3BM5zbnK
#Ecuador #MinistryOfLabor #SUT #TerroahOver #TeamPheisito #DataLeak #DataBreach #BreachAlert #DarkWeb #Hacking #ThreatIntel #ThreatIntelligence #InfoSec #CyberAlert #VECERT #SOC #CSIRT #Unconfirmed #SecurityAlert #CyberDefense #CyberRisk
#AlertaDigitalEC
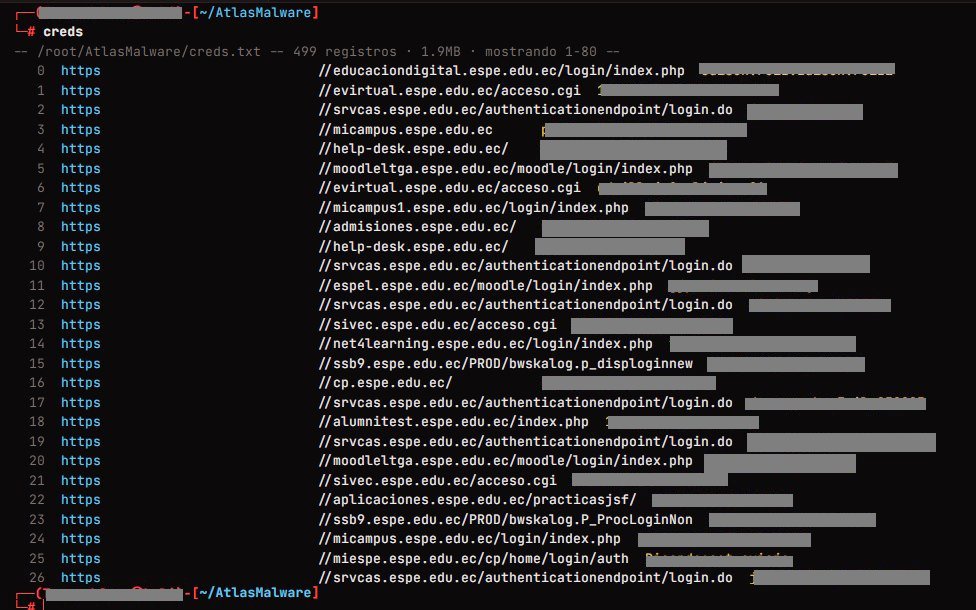
Se reporta filtración dde datos de @ESPEU, correspondería a 499 registros de credenciales de acceso (al parecer al entorno estudiantil), se atribuye @TerroahOver
NOTA: tachado propio
Y pensar qué a través de la lógica y en las sombras, si verdaderamente tienes conocimientos puedes crear un arma letal, este scritp Malware puede estar a la venta en cualquier momento sin restricciones, esto es solo una parte.
@usuariosdigital@VECERTRadar
⚠️ 🇪🇨 🏛️ PREVENTIVE ALERT - ALLEGED EXPOSURE OF CITIZEN DATABASE ACROSS GOVERNMENT DOMAINS (*.GOB.EC) IN ECUADOR (ACTORS: CURIRICA ALLIANCE / BYPASSAR / H4D3PWN / KN1GHTX1337)
[STATUS: ALLEGED / UNCONFIRMED / THREAT ACTORS: CURIRICA ALLIANCE (BYPASSAR, H4D3PWN, KN1GHTX1337, M0Z1LL4S, TERROAHGROUP) / DATE: OCTOBER 25, 2026]
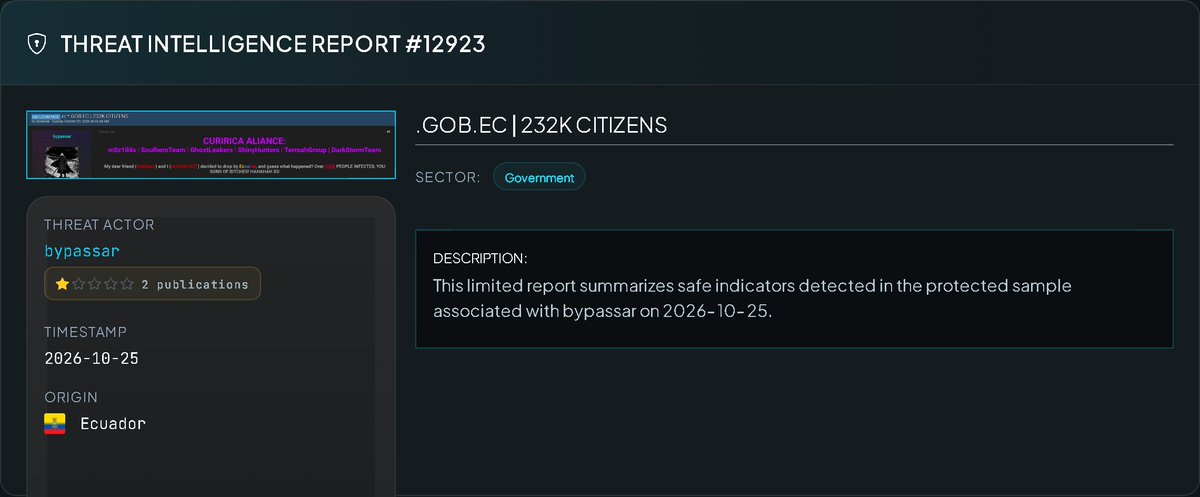
The centralized cyber-intelligence system has intercepted a post on underground breach forums (PwnForums / BreachForums), made on October 25, 2026, by the actor "bypassar." The report attributes an alleged massive intrusion into institutional portals of the Ecuadorian public administration—under the government top-level domain (*.gob.ec)—to a coalition calling itself the "CURIRICA ALLIANCE" (composed of groups such as m0z1ll4s, SoulhemTeam, GhostLeakers, ShinyHunters, TerroahGroup, and DarkStormTeam).
It is strictly noted that the veracity of this compromise, the actual intrusion into the networks or databases of Ecuadorian ministries and state agencies, and the overall authenticity of the 232,000 records have not been officially confirmed by the authorities of the National Government of the Republic of Ecuador, nor by government incident response teams (CSIRT/SOC). As this concerns alleged breaches posted on underground forums, the definitive status of the infrastructure remains unconfirmed. Identified Threat Actors:
Publisher: bypassar
Victim / Target: Ecuadorian State web portals and services (*.gob.ec) — 🇪🇨 Ecuador.
Sector: 🏛️ Public Sector, Central Government, Public Administration, Citizen Services, and State Databases.
Date of Publication: October 25, 2026.
Nature of the Incident: Announcement of an alleged exfiltration or massive compromise of information belonging to Ecuadorian citizens, accompanied by a sample link (GoFile) exposing data of 916 individuals as preliminary proof.
🛡️ PREVENTIVE TECHNICAL AND CONTAINMENT RECOMMENDATIONS (FOR SOC / CSIRT / ECUADORIAN PUBLIC ADMINISTRATION)
Comprehensive Audit of *.gob.ec Infrastructure: Government CSIRT teams, along with administrators of ministries and secretariats, must urgently audit access logs, web servers, and citizen-facing service portals to detect unusual requests, SQL injections, or unauthorized access to databases containing citizen information.
Monitoring and Analysis of the Sample: Conduct a controlled analysis of the 916-record sample to determine which specific government entity the exposed data schemas originated from.
🖥️ CENTRALIZED THREAT MONITORING SYSTEM
Intelligence System: https://t.co/wk9bZJ2Nli
Quickly check your security at: https://t.co/QZhWp0kFrO
Quotes and services: https://t.co/sx3BM5zbnK
#Ecuador #EC #Quito #Guayaquil #EcuadorGovernment #GobEc #DigitalGovernment #PublicSector #GovSec #PublicSector #DataLeak #DataBreach #BreachAlert #DatabaseLeak #CuriricaAliance #m0z1ll4s #bypassar #h4d3pwn #kn1ghtx1337 #TerroahGroup #DarkStormTeam #ShinyHunters #SoulhemTeam #PII #DarkWeb #Hacking #ThreatIntel #ThreatIntelligence #InfoSec #CyberAlert #VECERT #SOC #CSIRT #Unconfirmed #SecurityAlert #CyberDefense #CyberRisk #CybersecurityEcuador
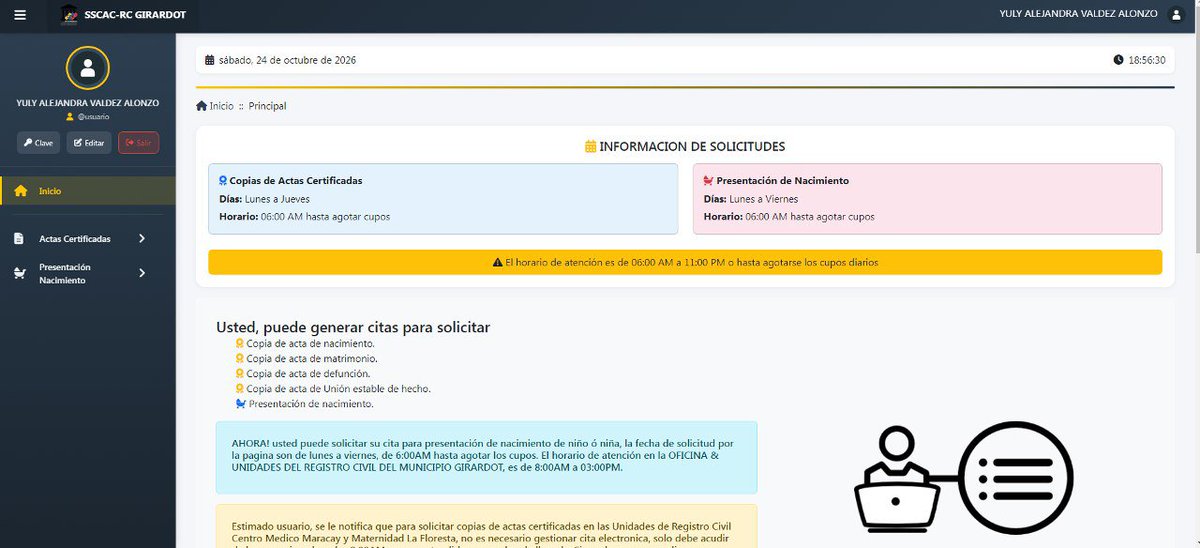
⚠️ 🇻🇪 🏛️ PREVENTIVE ALERT - ALLEGED UNAUTHORIZED ACCESS TO THE CIVIL REGISTRY SYSTEM IN GIRARDOT MUNICIPALITY, VENEZUELA (ACTORS: TERROAHOVER / TERROAHGROUP)
[STATUS: ALLEGED / UNCONFIRMED / THREAT ACTORS: TERROAHOVER / TERROAHGROUP / DATE: OCTOBER 24, 2026]
The centralized cyber-intelligence system has detected a social media post disseminated by the threat actor TerroahOver, in conjunction with TerroahGroup. The report claims an alleged cyber-intrusion into the digital platform of the Civil Registry of Girardot Municipality (Maracay, Aragua State, Venezuela).
It is strictly noted that the veracity of this compromise, the actual intrusion into the municipal system's databases, and the true extent of any data manipulation have not been officially confirmed by the Girardot Municipal Government, Civil Registry authorities, or Venezuelan state cybersecurity agencies. Given that these are social media posts originating from threat actors, the definitive status of the infrastructure remains unconfirmed.
Victim / Target: Civil Registry Appointment Request and Certified Records System of Girardot Municipality (SSCAC-RC GIRARDOT / Maracay, Aragua State) — 🇻🇪 Venezuela.
Sector: 🏛️ Public Sector, Municipal Government, Civil Registry, Identity Documentation, and Citizen Services.
Nature of the Incident: Alleged unauthorized access to a user panel or administrative modules used for issuing birth, death, and marriage certificates, as well as records of stable de facto unions.
🖥️ CENTRALIZED THREAT MONITORING SYSTEM
Intelligence System: https://t.co/wk9bZJ2Nli
Quickly check your security at: https://t.co/QZhWp0kFrO
Quotes and services: https://t.co/sx3BM5zbnK
#Venezuela #Aragua #Maracay #GirardotMunicipality #GirardotMayoralty #CivilRegistry #GirardotCivilRegistry #SSCAC #DigitalGovernment #GovSec #PublicSector #DataLeak #DataBreach #Hacked #CyberAttack #TerroahOver #TerroahGroup #AccountTakeover #Cybersecurity #ThreatIntel #ThreatIntelligence #InfoSec #CyberAlert #VECERT #SOC #CSIRT #Unconfirmed #SecurityAlert #CyberDefense #CyberRisk #CybersecurityVenezuela
Buenas, por esta cuenta qué me dieron estaré compartiendo lo que hacemos, también estaré poniendo caps de mis herramientas jeje
Próximamente #Brasil#Venezuela#Ecuador
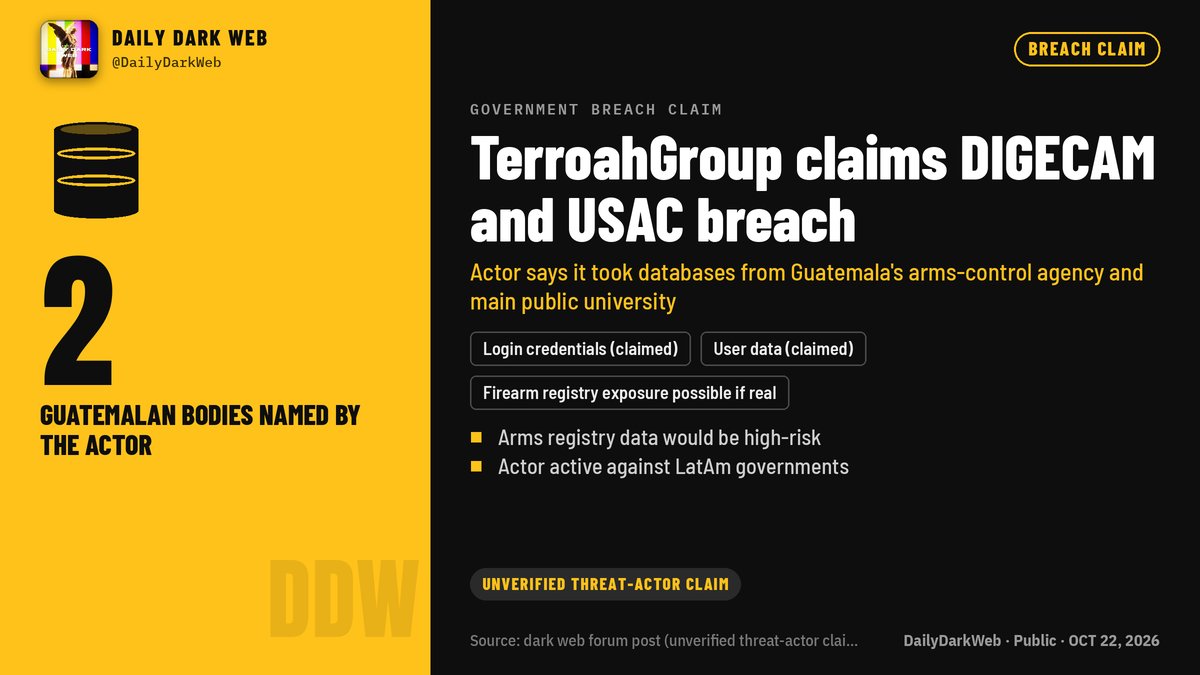
🇬🇹 🚨 GUATEMALA: TERROAHGROUP CLAIMS BREACH OF ARMS-CONTROL AGENCY DIGECAM AND USAC UNIVERSITY
The threat actor TerroahGroup claims to have breached and exfiltrated databases from two Guatemalan institutions: DIGECAM (Dirección General de Control de Armas y Municiones), the state body that registers firearms and ammunition, and the Universidad de San Carlos de Guatemala (USAC), the country's main public university.
The actor claims:
* Access to databases containing login credentials and user data
* Ongoing monitoring of the affected portals
* The targets were chosen over alleged security weaknesses
⚠️ Analyst Note:
If real, DIGECAM data could touch firearm and ammunition registration records, a serious security and regulatory risk. USAC data could expose students, faculty and staff. TerroahGroup has made a run of claims against Latin American government targets. Unverified threat-actor claim, NOT confirmation of a breach.
#DDW #DarkWeb #Guatemala #DIGECAM #USAC #DataBreach #ThreatIntelligence
⚠️ 🇬🇹 📊 PREVENTIVE ALERT: ALLEGED EXPLOITATION OF ULP LOGS FOR INITIAL ACCESS (THREAT ACTOR: TERROAHGROUP)
[STATUS: ALLEGED / UNCONFIRMED / THREAT ACTOR: TERROAHGROUP / DATE: OCTOBER 2026]
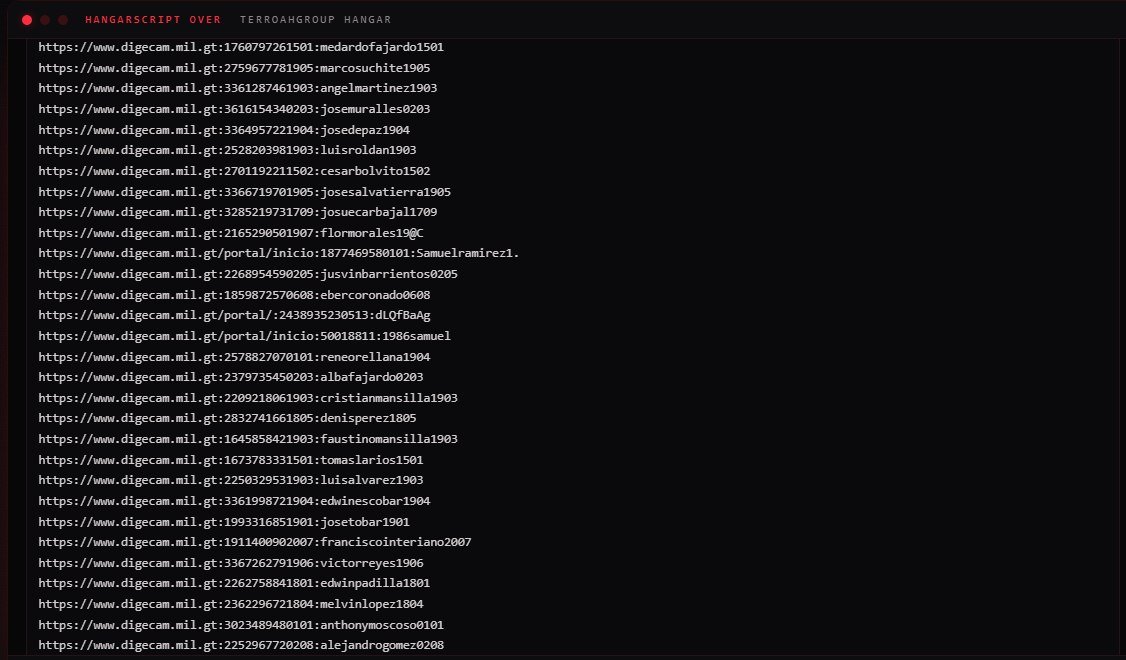
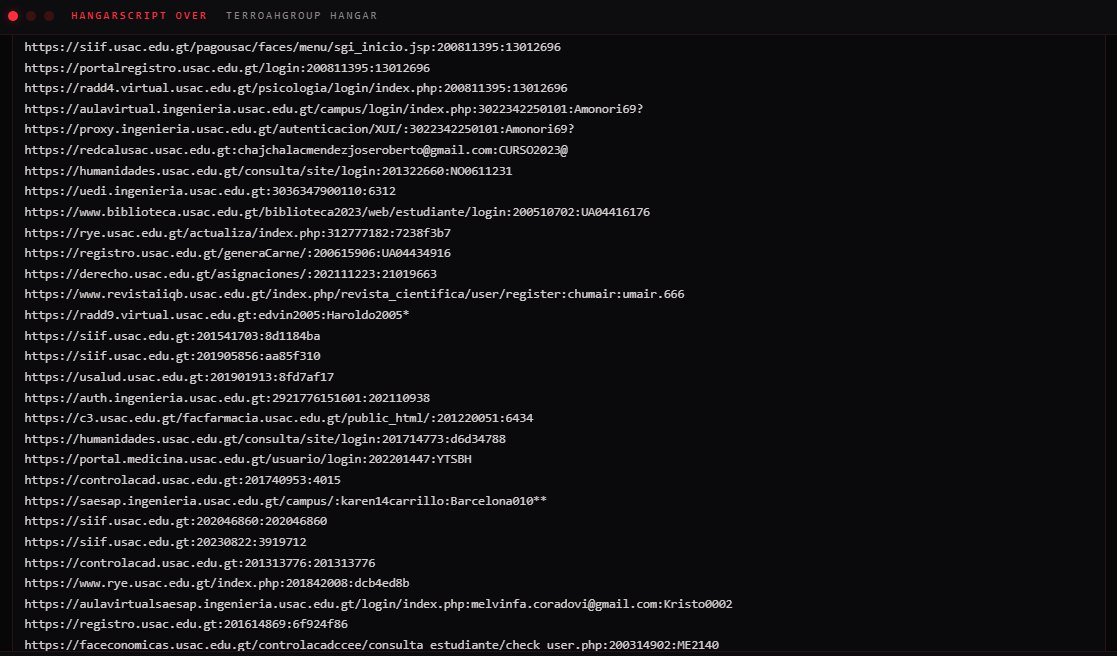
The centralized cyber-intelligence system has intercepted a social media post by the group "TerroahGroup," as shown in the attached screenshot. The post, labeled "Recent Attack," contains excerpts from lists of credentials and access URLs associated with institutional and higher education domains in Guatemala (including extensions such as .mil.gt and .usac.edu.gt).
It is crucial to clarify that this material consists of User Log Files (ULP)—often referred to as "information stealer logs"—obtained via info-stealing malware on end-user devices. Malicious actors repurpose these logs as an "initial access" vector to attempt to bypass authentication controls at the affected institutions.
Please note that the occurrence of actual intrusions and the effectiveness of these access attempts on institutional servers have not been officially confirmed. As this information originates from social media posts by threat groups, the actual status of the infrastructure remains unconfirmed.
🛡️ PREVENTIVE TECHNICAL RECOMMENDATIONS FOR CONTAINMENT (SOC / CSIRT / INSTITUTIONS)
Invalidation and Verification of Exposed Accounts: Institutional response teams should immediately cross-reference the data found in these ULP logs against their active directories to block any linked accounts and enforce mandatory password resets.
Strict Multi-Factor Authentication (MFA) Deployment: Implement robust, phishing-resistant MFA across all web access points, VPNs, and administrative panels to completely neutralize the value of plaintext credentials obtained via infostealers.
🖥️ CENTRALIZED THREAT MONITORING SYSTEM
Intelligence System: https://t.co/wk9bZJ2Nli
Quickly verify your security at: https://t.co/QZhWp0kFrO
Quotes and services: https://t.co/sx3BM5zbnK
#Cybersecurity #ThreatIntel #Guatemala #ULPLogs #InitialAccess #TerroahGroup #InfoSec #CyberAlert #VECERT #SOC #CSIRT #Unconfirmed #SecurityAlert
⚠️ 🇵🇦 📊 PREVENTIVE ALERT: EXPOSURE OF ULP RECORDS AND CREDENTIALS ON A PANAMANIAN GOVERNMENT PORTAL (ACTOR: TERROAHOVER)
[STATUS: ALLEGED / UNCONFIRMED / THREAT ACTOR: TERROAHOVER / DATE: OCTOBER 2026]
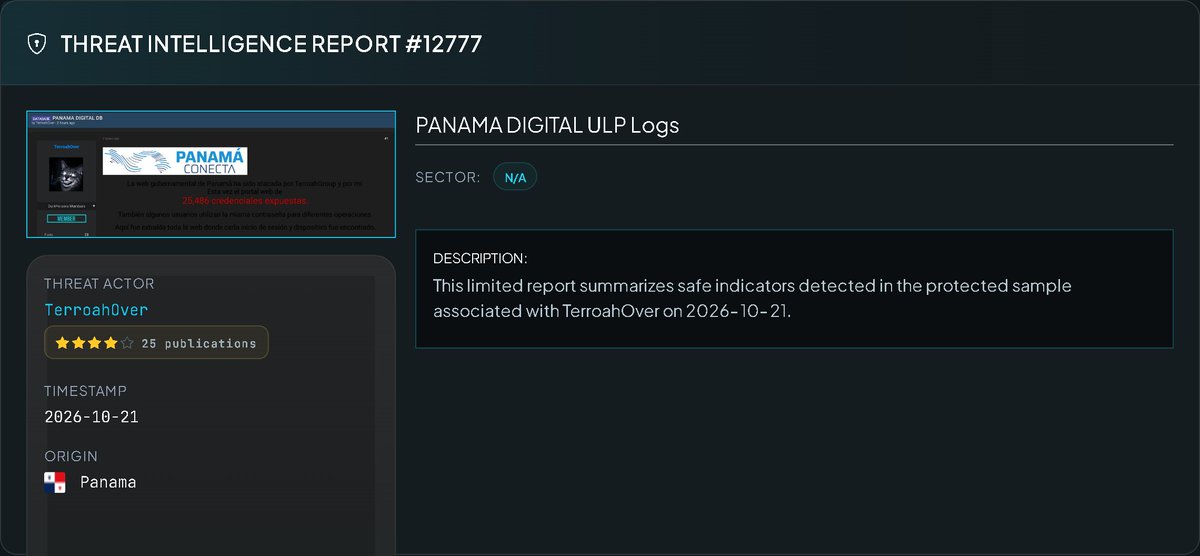
The centralized cyber-intelligence system has intercepted a post made on underground forums by the threat actor "TerroahOver." The post claims an attack against Panamanian government portals, carried out in collaboration with the group "TerroahGroup," and alleges the exposure of 25,486 credentials.
It is crucial to clarify that a technical analysis of the attached files indicates that the exposed data consists of "User Log Files" (ULP)—often associated with "information stealer" malware—rather than a direct breach, intrusion, or exfiltration from Panamanian state servers. In other words, these records likely originated from the personal devices of users infected with "stealer" malware, rather than from a compromise of the central government infrastructure.
Please note that the veracity of the actor's claims and the overall authenticity of the records have not been officially confirmed by Panamanian authorities. As these claims appeared on underground forums, the actual status of the government infrastructure remains unconfirmed.
Threat Actor: TerroahOver
Victim / Stated Target: Panamanian government web portals 🇵🇦.
Sector: 🏛️ Government, Public Infrastructure, and Citizen Identity Data in Panama. Nature of the Incident: The publication of a file containing 25,486 credentials. Forensic analysis of the file format indicates that these are ULP (User Log File) records—data harvested via information-stealing malware on user endpoints—rather than the result of a compromise at the server or institutional database level.
🛡️ TECHNICAL PREVENTIVE AND CONTAINMENT RECOMMENDATIONS (SOC / CSIRT / GOVERNMENT OF PANAMA)
Verification of Compromised Credentials: Institutional response teams should cross-reference the ULP record samples against active directories to identify accounts potentially exposed by malicious software on personal devices.
Mandatory Implementation of Multi-Factor Authentication (MFA): Since ULP records contain static passwords, the strict deployment of MFA immediately mitigates the risk of these exposed credentials being exploited by malicious actors to access government portals.
🖥️ CENTRALIZED THREAT MONITORING SYSTEM
Intelligence System: https://t.co/wk9bZJ2Nli
Quickly verify your security status at: https://t.co/QZhWp0kFrO
Inquiries and services: https://t.co/sx3BM5zbnK
#Cybersecurity #ThreatIntel #Panama #ULPLogs #Infostealer #DataLeak #TerroahGroup #InfoSec #CyberAlert #VECERT #SOC #CSIRT #Unconfirmed #SecurityAlert
Y apenas estamos a sabado....
Unos tales TerroahGroup afirman haber hecho un “ataque completo” contra @MovistarCo y Telebucaramanga, con presunta exposición de páginas de administración, cookies de sesión, IPs corporativas, routers, hostnames e infraestructura en la nube de Amazon EE.UU. (CloudFront, S3 y certificados).
Irán a confirmar, negar, o responderán como maquinitas? Veremos.
⚠️ Infraestructura de telecomunicaciones, gubernamental y educativa de la República Dominicana presuntamente expuesta.
Un actor de foro identificado como «TerroahOver» (firma «TerroahGroup») afirma haber detectado infraestructura de red expuesta en varias organizaciones dominicanas. Enumera 3.140 elementos comprometidos, sin precisar si se trata de sistemas, servicios o registros.
Exposiciones alegadas: interfaces remotas de routers y pasarelas; filtración de información de dominio y NTLM en Microsoft SQL Server; bases de datos sin filtrado de IP; servidores web y paneles de control expuestos.
Entidades mencionadas: Compañía Dominicana de Teléfonos, Altice Dominicana, Estrela Telecom, Instituto Tecnológico de Santo Domingo (INTEC), Ministerio de Obras Públicas y Comunicaciones (MOPC), Importadora Tropical S.A. y Alta Gracia Project Holding.
El actor advierte posibles ataques si no se corrigen las fallas. Las capturas adjuntas no demuestran intrusión ni robo de datos. La afirmación permanece sin verificación independiente.
Infraestructura de telecomunicaciones, gobierno y educación de República Dominicana presuntamente expuesta
Un actor de un foro que utiliza el nombre de usuario “TerroahOver” afirma haber identificado infraestructura de red expuesta asociada con múltiples organizaciones en República Dominicana. La publicación está firmada como “TerroahGroup.”
El actor enumera 3,140 elementos de información presuntamente comprometida, sin aclarar si esta cifra representa sistemas, servicios o registros individuales.
Las supuestas exposiciones incluyen:
• Administración de redes: interfaces de administración remota expuestas para routers y gateways
• Información interna: divulgación de información relacionada con dominios y NTLM que involucra Microsoft SQL Server
• Servicios de bases de datos: bases de datos presuntamente expuestas sin filtrado de IP
• Infraestructura web: servidores web y paneles de control expuestos
Las organizaciones mencionadas en la publicación incluyen:
• Compañía Dominicana de Teléfonos
• Altice Dominicana (Tricom)
• Estrela Telecom
• Instituto Tecnológico de Santo Domingo (INTEC)
• Ministerio de Obras Públicas y Comunicaciones (MOPC)
• Importadora Tropical S.A.
• Alta Gracia Project Holding
El actor advierte que las organizaciones mencionadas podrían enfrentar ataques si los supuestos problemas permanecen sin resolver. La publicación incluye archivos adjuntos con capturas de pantalla, pero el material mostrado no demuestra una intrusión exitosa ni el robo de datos.
https://t.co/TXqSASclx7
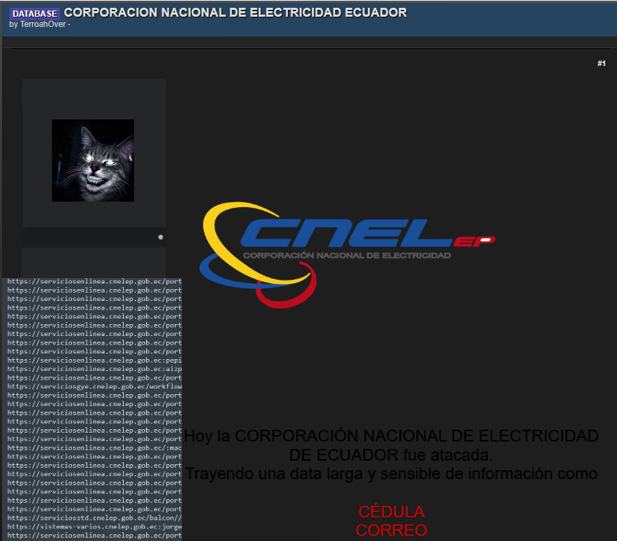
🎴Alerta de Amenaza🎴
Ataque: Corporación Nacional de Electricidad🇪🇨
Sector: Energetico
Web: https://t.co/rOrlM3CP1o
Grupo de amenaza: TerroahGroup
Data: credenciales, identificación, email y domicilio.
Impacto: Compromiso de cuentas, robo de identidad.
Fecha: 14OCT26
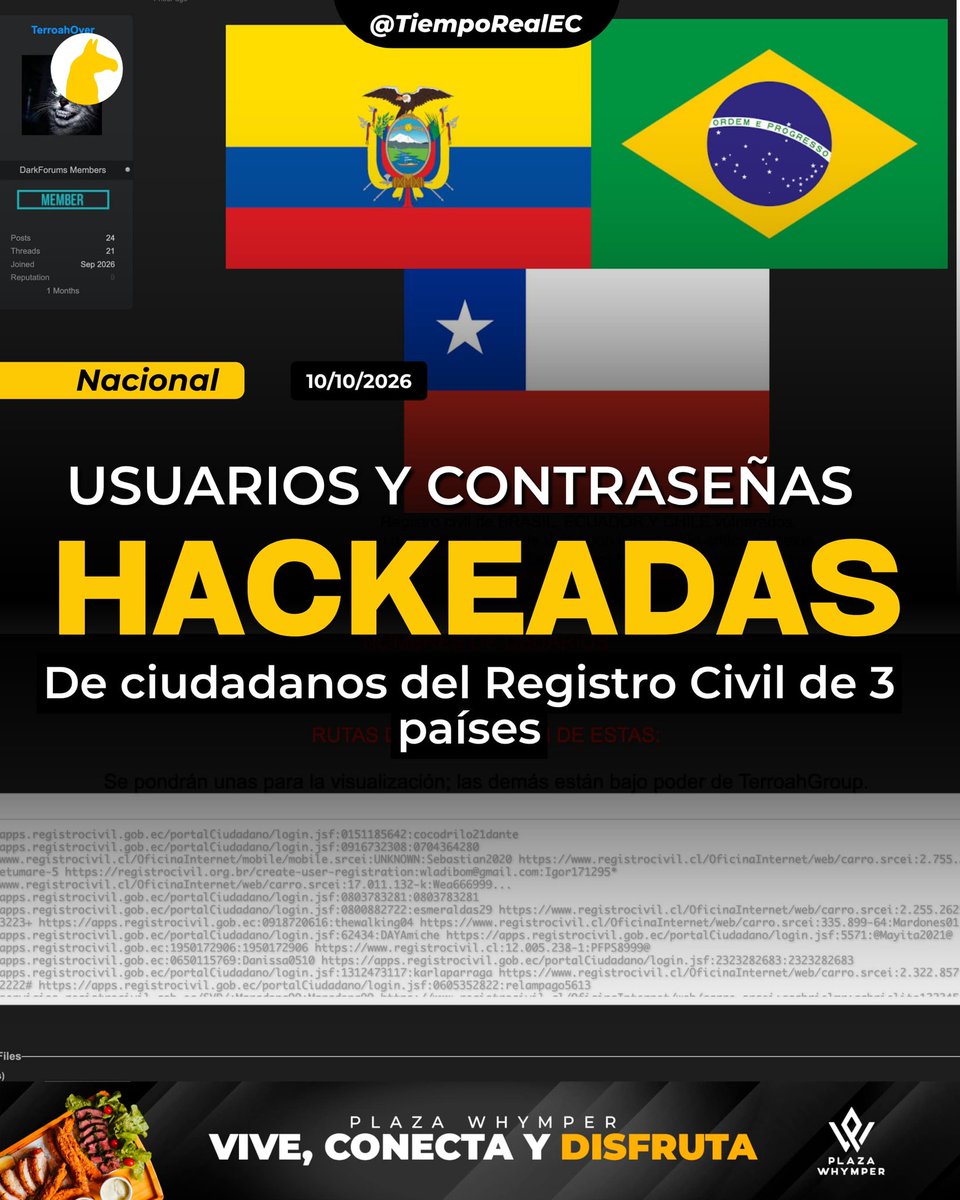
🚨 ALERTA INTERNACIONAL: HACKER AFIRMA HABER VULNERADO REGISTROS CIVILES DE ECUADOR, CHILE Y BRASIL
💻 Un actor de amenazas identificado como “TerroahOver”, vinculado a “TerroahGroup”, afirmó en un foro de ciberdelincuencia haber accedido a sistemas relacionados con registros civiles de Ecuador, Chile y Brasil. La información difundida este 12 de octubre todavía requiere validación técnica independiente.
🔐 El supuesto paquete incluiría nombres de usuario, contraseñas, correos electrónicos, números de identificación nacional y otros datos personales. De confirmarse, la exposición podría facilitar suplantaciones de identidad, accesos indebidos a cuentas y campañas de phishing dirigidas.
🇪🇨 Ecuador ya enfrentó en mayo otra alerta por una presunta filtración atribuida al Registro Civil, que involucraba aproximadamente 14,8 millones de registros personales y millones de imágenes. En aquella ocasión, la institución aseguró que sus verificaciones no detectaron accesos directos a su infraestructura tecnológica.
⚠️ La publicación actual no demuestra por sí sola que los sistemas oficiales de los tres países hayan sido vulnerados. El origen, autenticidad y volumen de la base ofrecida deben ser examinados antes de establecer si corresponde a información nueva, reutilizada o recopilada desde otras fuentes.
🛡️ Ante este tipo de alertas, se recomienda cambiar contraseñas reutilizadas, activar autenticación de dos factores y desconfiar de correos, mensajes o llamadas que soliciten códigos y datos personales. Las credenciales supuestamente filtradas no deben descargarse, compartirse ni republicarse.
#TiempoRealPlus #VivimosHistorias #Ciberseguridad #RegistroCivil #FiltracionDeDatos