They use #Plone indeed!
More than 1000 Plone CMS instances for more than 5600 sub-national legislative houses. 😯
That's a lot of Plone. 🩵
Read all about it:
👉 https://t.co/L7c3FdZoZC
Hear João Gouveia tell all: 🎬 https://t.co/GHbhLikDgb
#OpenSource#Interlegis
#feelgoodfriday
Plone Conf 2026 Talks are live!
If you weren’t able to join us at Plone Conf 2026 in Maastricht don’t worry, follow the link below, grab a drink and start your weekend on a high - with team Juizi.
https://t.co/ib87zPTlzZ
@IT_unhinged Once had a client. You recognize their name. Field trip to Barcelona office. "Where do you keep the server" They led me to a door.
Opened the door.
I am not making this up.
Resting on top of the toilet, the server.
Lid was down so everything was fine.
Security called me at 6:12 AM today.
"Patch every PHP server immediately."
I asked what happened.
"Two critical vulnerabilities. Remote code execution. No authentication required."
Cool.
How many PHP servers do we have?
According to inventory: 12
According to reality:
Nobody knows.
We found one running WordPress.
Three running old internal tools.
One under someone's desk.
Two inside vendor appliances.
A forgotten employee directory from 2016.
And a server named:
PHP-OLD-DO-NOT-TOUCH
Naturally, that one runs payroll exports.
Then we found a PHP 5.6 box.
I asked who owned it.
The documentation said:
BRIAN.
Brian left in 2019.
We called Brian.
He said:
"Oh wow, that's still running?"
Excellent.
By 8 AM, leadership joined the incident call.
CEO:
"Can hackers actually get in?"
Security:
"Potentially yes."
CEO:
"Without a password?"
Security:
"Yes."
CEO:
"Then why do WE need passwords?"
Not the lesson.
Finance asked if we could wait until the weekend to patch because downtime affects revenue.
Security explained that the alternative was letting strangers execute code on our servers.
Finance asked for a cost comparison.
At 9:17, someone suggested temporarily taking the vulnerable websites offline.
Marketing refused.
"Our campaign is live."
So for the next hour, the company officially decided maintaining a landing page for 20% off webinar registration was more important than preventing remote server takeover.
We finally patched everything we could find.
Then our scanner discovered another PHP server.
Hostname:
TEMP-PHP-2014
Uptime:
4,512 days.
Nobody knows what it does.
Nobody owns it.
Nobody can shut it down.
But every time we block network access, the warehouse stops printing shipping labels.
Security has classified it as critical infrastructure.
It is running PHP 5.4.
The vulnerability has existed longer than half our employees.
The emergency patch took four hours.
Finding out what PHP actually runs took eleven.
The internet isn't held together with code.
It's held together with servers everyone is afraid to turn off.
La crisis de PHP explicada para no informáticos 🧵
Hoy medio mundo apagó páginas web por una falla en algo llamado PHP. Si no eres informático y te preguntas qué pasó, por qué hubo gobiernos que cerraron sus sitios y si deberías preocuparte, te lo explico con ejemplos de cocina y cerraduras 👇
Government and business websites across Europe have been taken down because of a serious security flaw, discovered by a researcher using AI.
Science and technology editor @t0mclark3 tells @LeahBoleto the latest. ⬇️
🇬🇧 https://t.co/KG8L4TUSkI
Documentation, training materials, and developer meetups don't happen in a vacuum—they are fueled by dedicated community partners! 📚
Thank you to our Premium Sponsor webcloud 7 for helping us keep educational resources free and accessible to developers worldwide.
🔐 Node.js security updates are now available!
New releases for Node.js 22.x, 24.x & 26.x address multiple vulnerabilities, including high-severity issues.
Review the details and update your systems to stay secure.
🔗 https://t.co/W4kfzx5lxz
#NodeJS#Security
Behind every Plone release there is a quieter effort: getting the world to notice it.
That is the Plone Marketing team. And at Plone Conference 2026, Astrid Beyers gives the update on their year.
https://t.co/T8P0uoKvje
#PloneConf2026#Plone#OpenSource#Community
Stellenbosch Tech Meetup is bringing the heat this May 🔥
@johanbeyers : Building a scoring system for @RedBullZA King of the Air
Richard Craig: Hacking Multi-Factor Authentication
📅 May 14 | 15:00–17:30
📍 Capitec HQ, Stellenbosch
RSVP: https://t.co/33wdMAnyZo
Last week we met with the @NITheCS team at their @StellenboschUni office to discuss AI integration & improving the events page on https://t.co/48kMxAYk3H. Thanks to @petruccione, René Kotzé & @Belindaviret for the great session. Excited for our @plone strategy sprint in Jan '26!
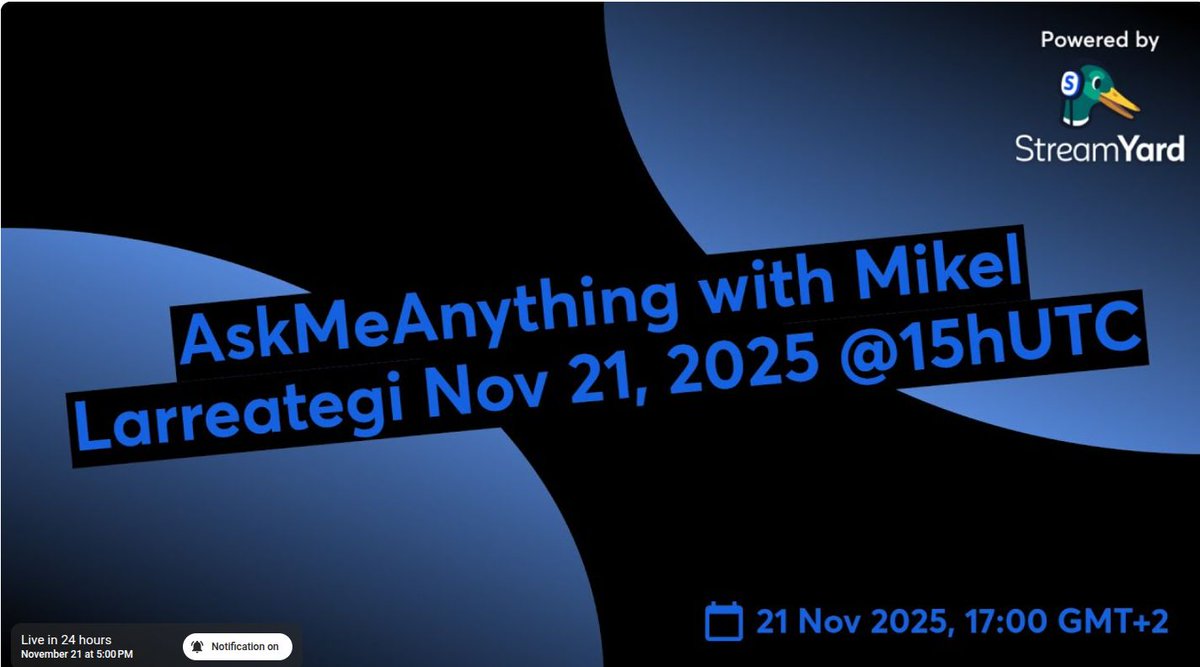
Next in our 🎤 AskMeAnything lineup, is Plonista, ex-Plone Foundation Board member, and current Sponsorship team lead Mikel Larrategi. Bring your questions, ask him anything.
🎬 https://t.co/UopSbwDWZ0
Get your questions ready and join us at 15h UTC tomorrow Nov 21, 2025!