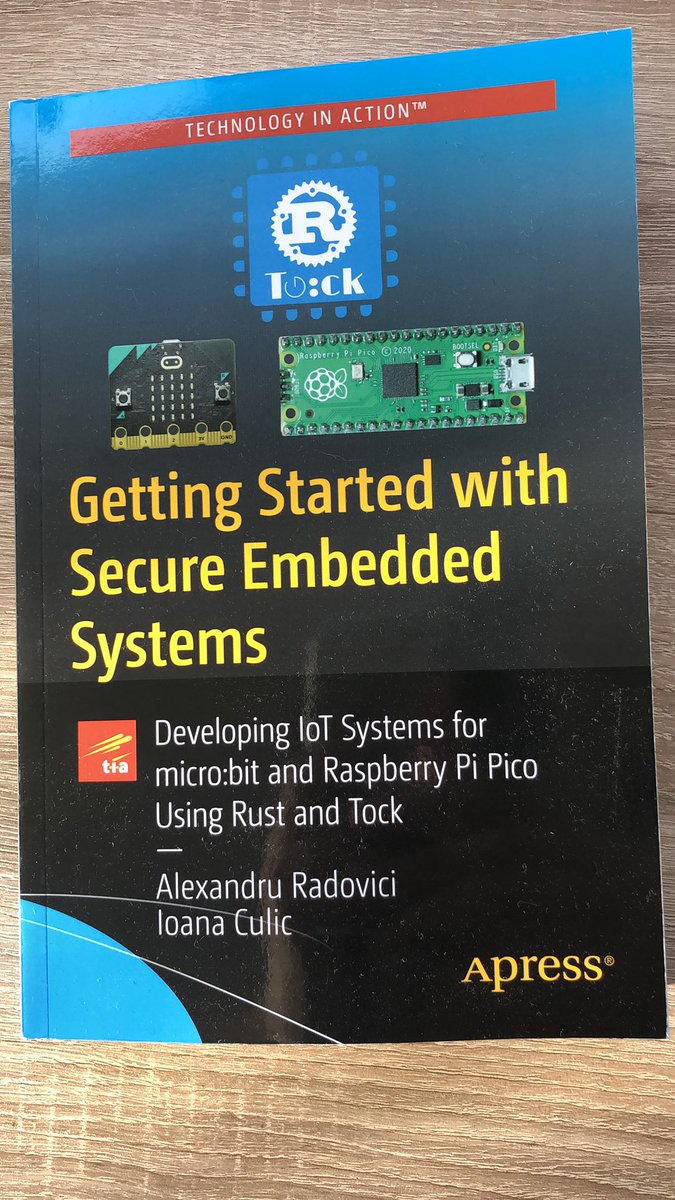
@rustembedded Excited to share a FREE book about developing secure and robust systems software, at the overlap of "state-of-the-art" and "near-term practical": https://t.co/tJnz0jjfJ5
It's here! 🎉 Ferrous Systems and @AdaCoreCompany just open sourced the first draft of the Ferrocene Language Specification, a description of the Rust programming language, made for safety-critical qualification. More on our blog: https://t.co/iytKgW4hU3
Thrilled and honored that "High Assurance Rust" was selected for the Rust Foundation's Community Grants Program! Looking forward to writing more chapters. Lots of exciting projects on this list! 🎉
We are delighted to announce the recipients of the 2022 Rust Foundation Fellowship and Project Grants.
These awards will support talented and committed community members all over the world to do great work.
Find out more: https://t.co/SpWQeBo1IT
The Fuzzing Book 1.1 is out! Now with 23 course videos, interactive quizzes, type annotations, updated code that you can run in your browser, and much more. Want to learn how to generate software tests? Check out @fuzzingbook at https://t.co/k2Z4uNcxni 1/6
@inicmu@MITREcorp Congrats to the students! Proud to see the INI field a winning team, the eCTF is a challenging competition that requires a broad attack/defense skillset.
async/await + Rust Embedded
@rustembedded = 💖⚡️ continues on @NordicTweets!
Embassy 🏰 is not so different from RTIC ❄️ in the feeling, except that interrupts are hidden in async/await mode.
Cannot put ALT text in video: little Ferris moves when pushing #nRF52840 buttons
This channel presents brief, accessible, accurate video summaries of academic research papers (many fields, recent and classic topics). Recommend Netflix-level bingeing. Thanks @vivekhaldar ! https://t.co/VrksQbMnjl
GCC 12 offers improved, experimental, static taint analysis (flow tracking for attacker-controlled data). Not as sensational a headline as a new nick-named CVE. But perhaps it'll prevent one someday.
Kani, the model checker introduced in this talk, supports unsafe Rust and CI integration. And it's open-source and peer-reviewed. Lot of boxes to tick at once. Kudos to the Kani team for exemplary applied research!
My turn to add to the Linux security "fun" of the past few weeks :)
I walk through the entire process of discovering and exploiting CVE-2022-25636, a 0day in the Linux kernel. https://t.co/2GvBUxyt82
Yes, #TheBatman is a footnote in the history of Nolan's trilogy. But it's also well-done, self-aware film noir. Worth a watch. Even if its critique of vigilante justice is somewhat undermined by its ending.
Todays announcement is a partnership: @FerrousSystems@AdaCoreCompany are combining their experience in memory-safe systems programming to bring @rustlang into safety critical project through the Ferrocene project. Read our announcement here: https://t.co/MzqgNFYBXw
As technologists, we're always looking forward - seeking the next big thing. This post takes a trip backward, sampling past innovations with enduring legacies.
https://t.co/O39jE20E9r
Reminder: you can now put `rust-version` in your @rustlang libraries’ manifest to declare the MSRV!
https://t.co/ohDvIIYKRz
https://t.co/FUoUo0KLTB
It's okay to do even if you support versions of rust <1.56 – the older versions of cargo will emit a warning & work normally..
Scapegoat v2.0 is out! The library is a safe, fallible, stack-only alternative to BTreeSet/BTreeMap (Rust's standard ordered set/map implementations). Primarily for resource-constrained embedded: https://t.co/erjemAbtzW
#DuneMovie is an earnest reimagining of a beloved space opera. Somehow both thunderously epic and, relative to David Lynch's 1984 rendition, tastefully understated. Melange indeed.