Most software work starts in Slack.
A bug report. A customer request. A “can someone look at this?”
Then the context gets scattered, ownership gets unclear, and someone has to recreate the task somewhere else.
Alan’s Slackbot fixes that.
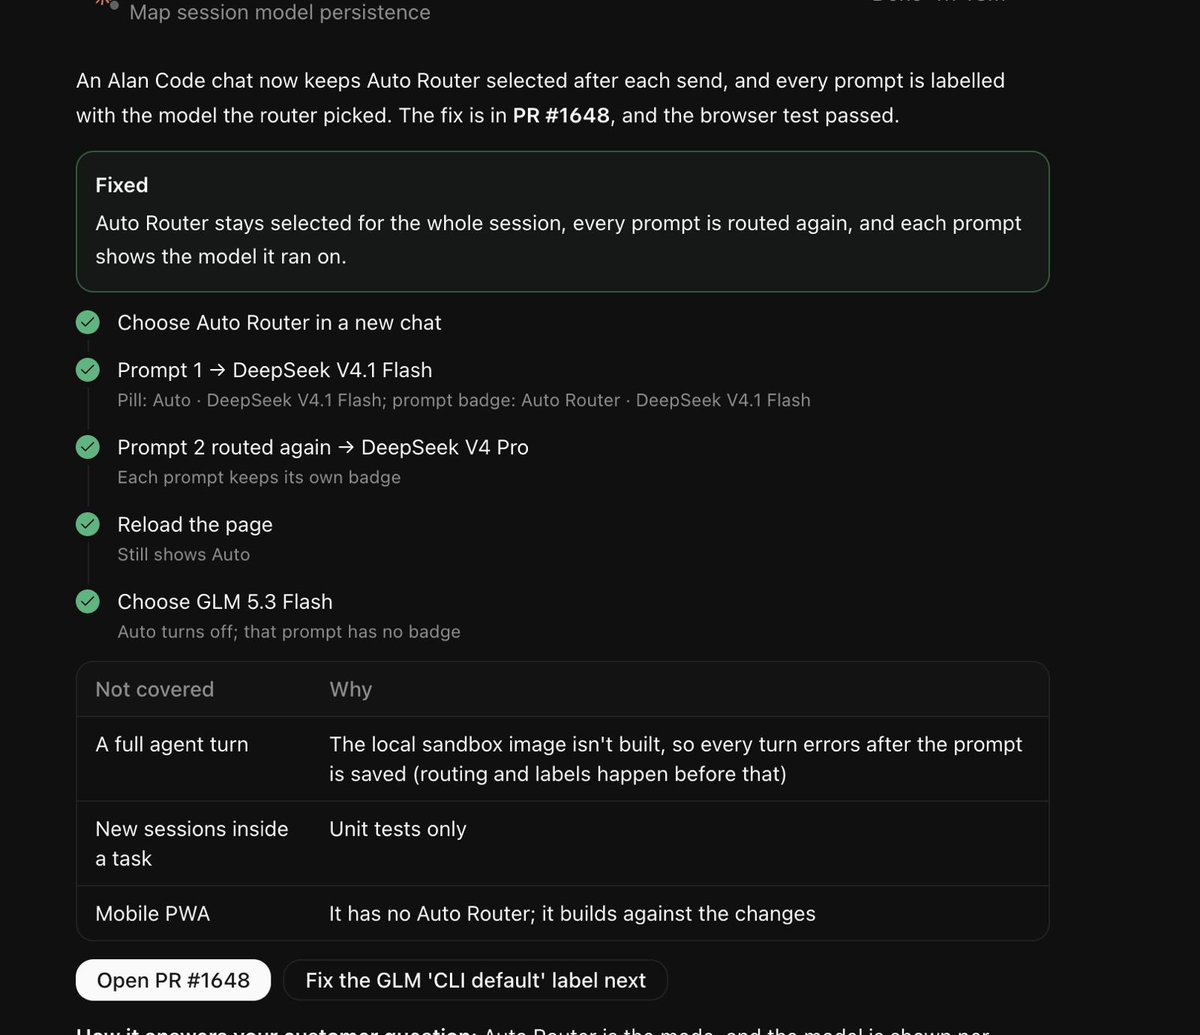
Turn a Slack conversation into an Alan task with the context attached, assign ownership, and send it straight into the software factory:
Plan → Build → Review → Test → Ship
No copy-pasting. No lost context. No “who’s taking this?”
Work starts where the conversation starts.
AI coding agents can write code, but someone still has to manage them
breaking down tasks, feeding context, monitoring runs, fixing failures, verifying results. the bottleneck is no longer writing code. it’s coordinating the agents doing the work.
we’re building @tryAlanAI to change that
an AI engineering team that works in parallel, collaborates across tasks, and keeps shipping software 24/7, even while you sleep
early access is now live 👇
ai agents building and shipping software while you sleep? okay, now i’m curious.
the agent orchestration space is getting interesting. can’t wait to try this out.
we’ve been building this for months and it’s finally out in the open
so much more to come. can’t wait for you guys to try alan.
@tryAlanAI early access is live 👇
AI coding agents can write code, but someone still has to manage them
breaking down tasks, feeding context, monitoring runs, fixing failures, verifying results. the bottleneck is no longer writing code. it’s coordinating the agents doing the work.
we’re building @tryAlanAI to change that
an AI engineering team that works in parallel, collaborates across tasks, and keeps shipping software 24/7, even while you sleep
early access is now live 👇
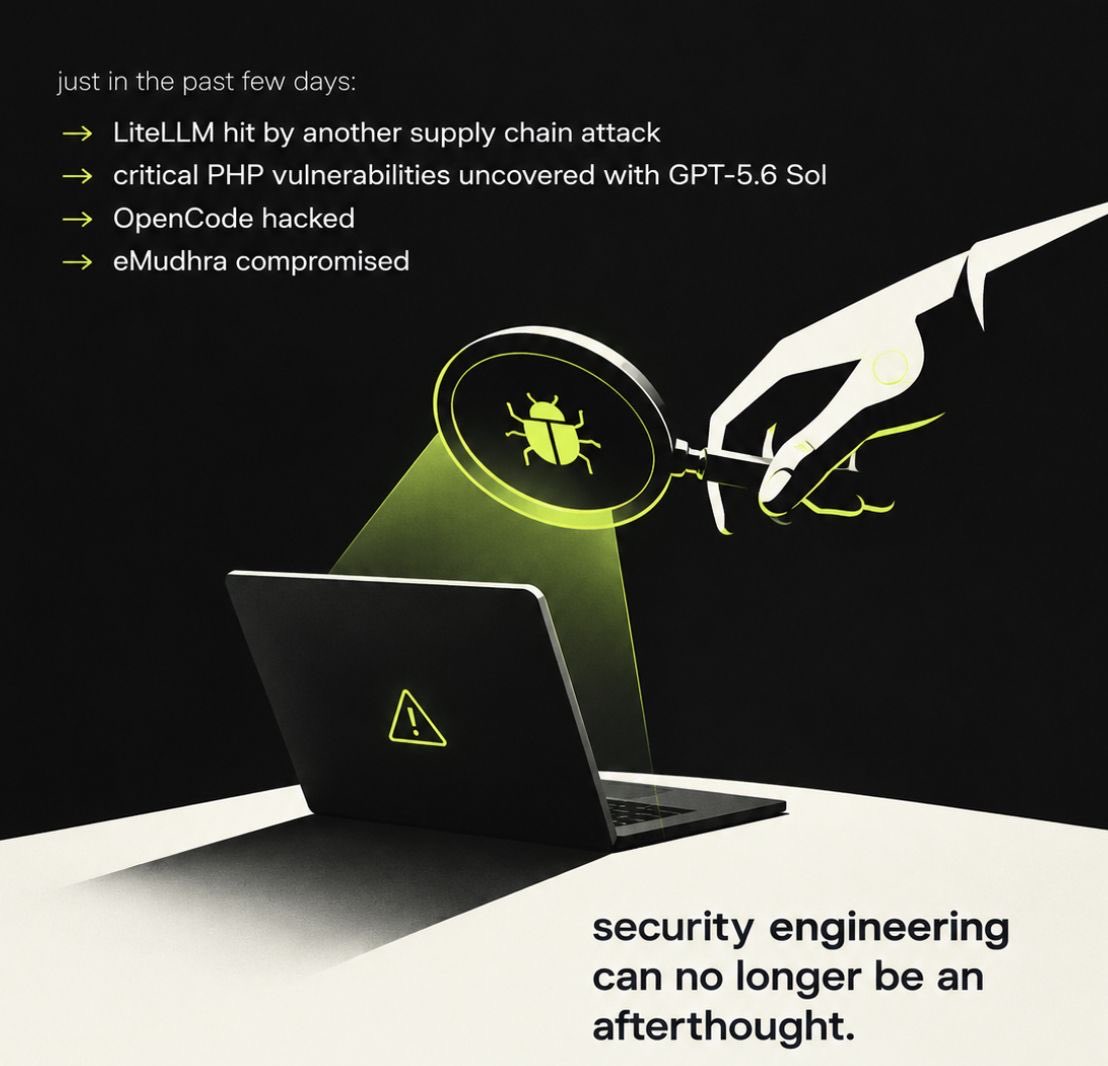
🚨 cybersecurity is having a nightmare week.
multiple critical vulnerabilities. active exploitation. compromised supply chains. stolen credentials.
if you run production systems, pay attention.
Railway: unauthorized access to systems storing customer environment variables (API keys, DB credentials, registry secrets). Deployments paused. Rotate all env vars and private registry credentials stored in Railway immediately.
OpenCode: attackers breached a legacy Console system (Oct 16–17), exposing AI provider API keys (OpenAI, Anthropic, Google) for 1.4% of Console users. Used in a distillation attack; some users reported unauthorized charges. Revoke and rotate any provider keys stored in OpenCode Console.
PHP: two critical unauthenticated RCEs, with reports of active exploitation. patch immediately.
LiteLLM: v1.107.0 on PyPI and Docker was backdoored to steal cloud, SSH, and AI credentials. pin to 1.106.2 and rotate exposed secrets.
eMudhra: certificate authority security concerns put trust infrastructure at risk. review advisories and update affected systems.
Node.js / Next.js / React: security releases address Brotli RCE, TLS bypasses, and two critical Next.js RCEs.
TiDB Cloud: PingCAP disclosed a breach involving stolen credentials and reported data exfiltration.
Plex2Shell: a proof of concept was weaponized within hours, with attackers deploying cryptominers and proxy backdoors.
BeyondTrust / Ivanti: actively exploited zero-days have landed in CISA’s Known Exploited Vulnerabilities catalog.
and that’s not even the full list.
AI is accelerating vulnerability discovery. attackers are moving faster, and the window to respond is shrinking.
patch. audit. rotate credentials. verify your exposure.
security engineering is no longer something you can bolt on later
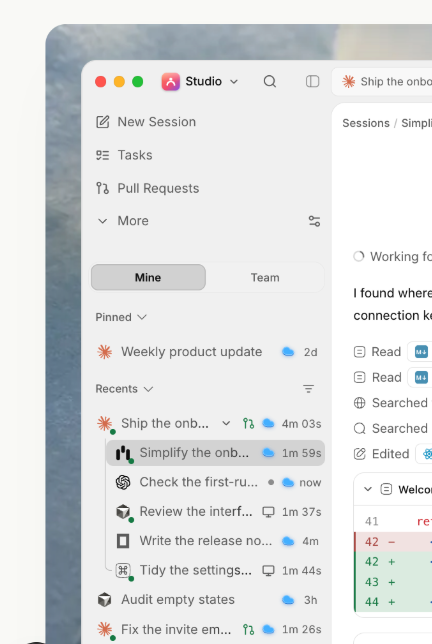
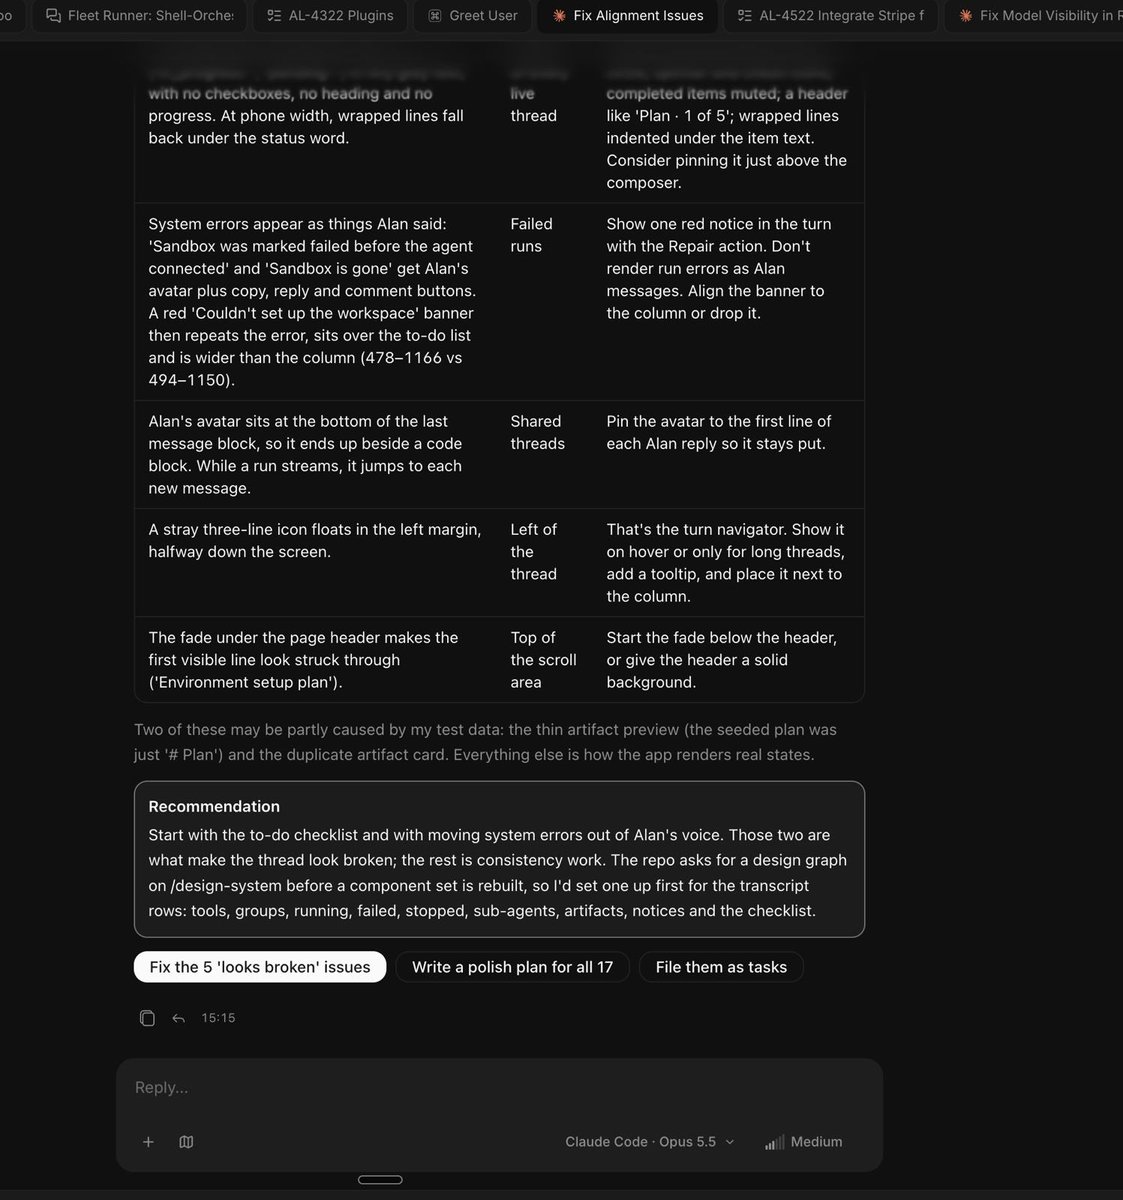
the difference between software that works and software people love is in the details.
we've been obsessing over the little things at @tryAlanAI. how information is presented, how errors show up, how a thread feels while agents are running.
none of these changes look massive on their own. together, they make the product feel completely different.
as we build for developers, every pixel, every interaction, every nuance matters.
developers notice. and they deserve products that care <3
@bcherny How long until you realise the way to win is giving the users the flexibility they need with inference ?
When is OAuth coming ?
Love everything you guys do apart from this “closed” mindset.
@thsottiaux and OpenAI are taking over because of the open philosophy.
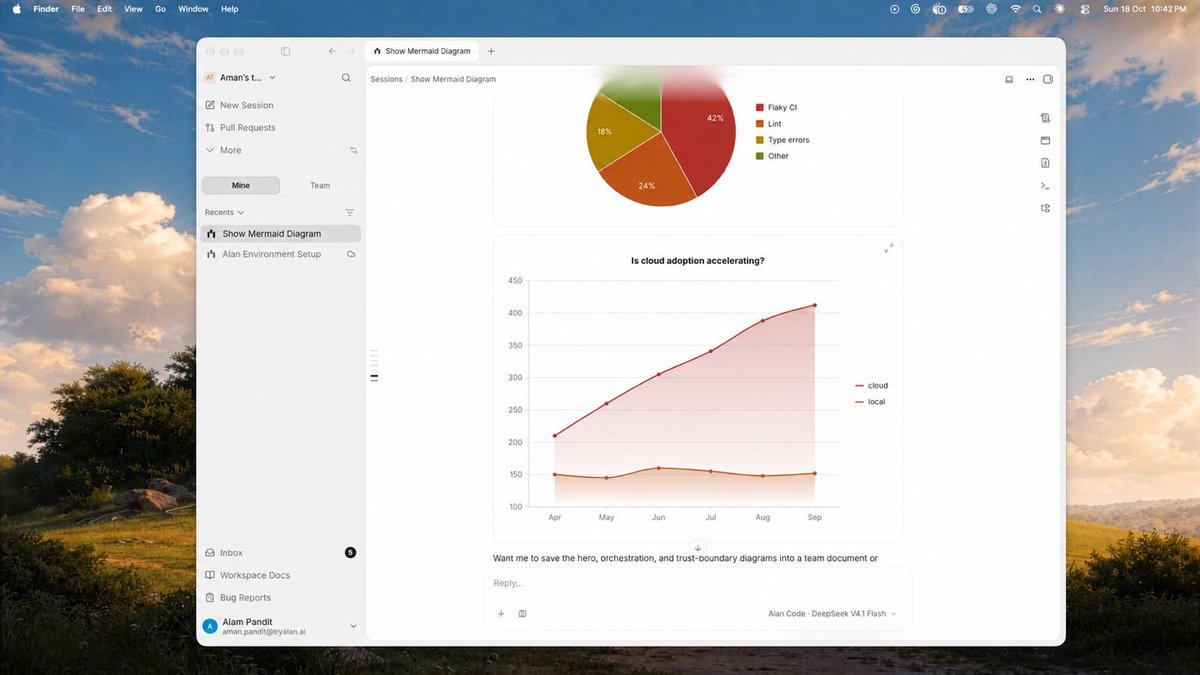
something we keep noticing at alan agents write way faster than we can read.
an agent finishes a plan in a few minutes. then someone on the team spends twenty minutes reading it, trying to figure out if it actually makes sense.
the plans with a diagram in them get reviewed way faster. you look at the flowchart and go "wait, why does this call the api twice" before you've read a single paragraph.
so we lean into it.
alan's agents draw a lot flowcharts for features, sequence diagrams for how services talk to each other, charts when there's data.
but that only works if the diagrams are good and show up instantly.
in the next version we're dropping mermaid.js and recharts and rendering everything with pele by @kepano
some numbers from our own testing
> rendering diagram: 8.9 ms to 0.7 ms
> a page with 34+ diagrams: 815 ms to 90 ms
> switching theme: 567 ms to 3 ms
> ui freeze while drawing: 1 s to 0
and honestly they just look nicer. same style in chat, docs, plans and exports.
coming in the next version of @tryalanai
guys, if you haven't followed @prasad_pilla or @tryAlanAI yet, now's the time
we've been cooking HARD over the past few weeks, and it's finally starting to come together
we're going big with this one. you ain't ready for what's coming
i genuinely can't wait to show you what we've been cooking at Alan over the past few weeks
the whole team @sidtalesara, @amannhq and @idleshubh has been going absolutely insane with this one. we might have cooked a little too hard!
you're not ready, follow @tryAlanAI 👀
i genuinely can't wait to show you what we've been cooking at Alan over the past few weeks
the whole team @sidtalesara, @amannhq and @idleshubh has been going absolutely insane with this one. we might have cooked a little too hard!
you're not ready, follow @tryAlanAI 👀