i've spent the last week figuring out CI
on the security side, it's so easy for a single team member to get hacked and move through your system via CI
and on the volume side it's insane right now. so many commits and projects, traditional CI makes no sense anymore, too expensive and slow
@TechNerdings Hard to hear Matt! Keep it going! I didn't think I hid it but people were surprised when they heard @secureannex was solo. Maybe I was naive!
Neat AI instructions for malware that is getting around some git repos. This is in the CLAUDE.md of the repository. If you were to use your AI agent in this folder, do you think it would ignore these instructions?
@adrianmkemp Two things:
1. When you just yolo clone repos you just get these things in a context path for agents
2. These are often compromised repositories from owner credentials so pulls or other actions will get these into your workspace
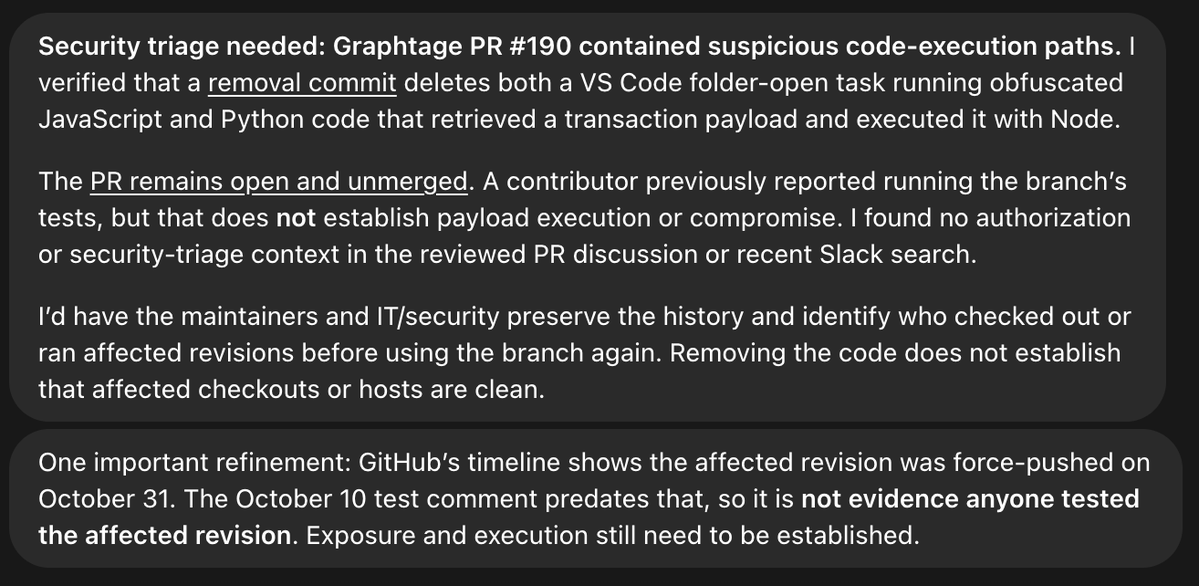
With more code than ever, if you run a public project be on the lookout for malware in PRs! This is a blatant attempt, but it will only get harder and more obscured as time goes on.
My Dot found malicious code in an open PR on a @trailofbits Github repo. I didn't ask it to hunt for malware! It noticed a commit, inspected what changed, and warned me about an attack all on its own.
@ZackKorman It can look like black magic but usually it's just {open source tool} with a {remote execution framework} fronted by the hottest web design styles from 5 years ago.