2of 2 / 2of n 의 보안 관리적 리스크 인지가 선행되는 게 확실히 중요한것같아요
노드운영 시작할 때 쯤 2 of 2의 매력을 크게 느끼고 셀커에도 적용시켰고
bsms 관리가 확실히 줄어드는 이유는, 파생경로 정도만 알고 있어도 재현 경우의 수가 거의 없기에 기존 싱글시그와 차이를 못느끼고 있네요
[멀티시그]
2of2 의 장점. 보관,관리가 쉽다. 패스프레이즈 관리방법과 거의 유사하다.
단점은 하나라도 잃으면 안된다.
2of3는 시드3개와 디스크립터(BSMS). 관리할갯수가 많다. 시드1개는 잃어버려도 되지만 BSMS까지 같이 잃어버리면 곤란할수 있다.
2of2는 어차피 시드잃어버린다는 시나리오가 없기에 BSMS는 상대적으로 느슨하게 해도 된다. 니���닉2개로 어차피 복구되니까.
둘 중 자신에게 맞는 방법으로.
대부분 2of3을 하는 추세이지만 2of2가 맞는 사람도 있을것이다.
멀티시그 유저입니다.
도움이 될까 해서 오랜만에 글 쓰네요,
2 of 3 가 정배지만, 2 of 2 사용중입니다.
- 기존 엔트로피 개빵빵한 24자리 니모닉 반띵
- 각 11단어에 대한 체크썸 재계산
- 두 12니모닉으로 멀티시그
멀티시그 유저들 xpub백업 잘 해두세요. 특히 핫월렛 멀티시그 조합
Announcing LayerTree: a new tree-based scaling solution for Bitcoin that permits O(1), independent of the number of users in the system: https://t.co/RtARIow733
A single UTXO can hold the balance of millions of users as an off-chain Merkle-sum tree.
Transaction introspection techniques permit batched exit from the system in a single transaction w/o any pre-signing: https://t.co/AqvaZqkvyW
Introducing LayerTree, a non-custodial scaling solution on bitcoin that connects to Lightning.
Using covenants, one UXTO can be shared by a million users. Any user can leave at any time in a single transaction. Users don't need to be online to receive. Funds never time out.
LayerTree is the next step in bringing bitcoin to billions.
Learn more: https://t.co/4oEwnwWLBC
멀티시그 유저입니다.
도움이 될까 해서 오랜만에 글 쓰네요,
2 of 3 가 정배지만, 2 of 2 사용중입니다.
- 기존 엔트로피 개빵빵한 24자리 니모닉 반띵
- 각 11단어에 대한 체크썸 재계산
- 두 12니모닉으로 멀티시그
멀티시그 유저들 xpub백업 잘 해두세요. 특히 핫월렛 멀티시그 조합
@YooDahui님과 포크코인 분리를 배우는 대화 도중
1. 난 그래도 내 코인에 옵리턴 박기 싫다
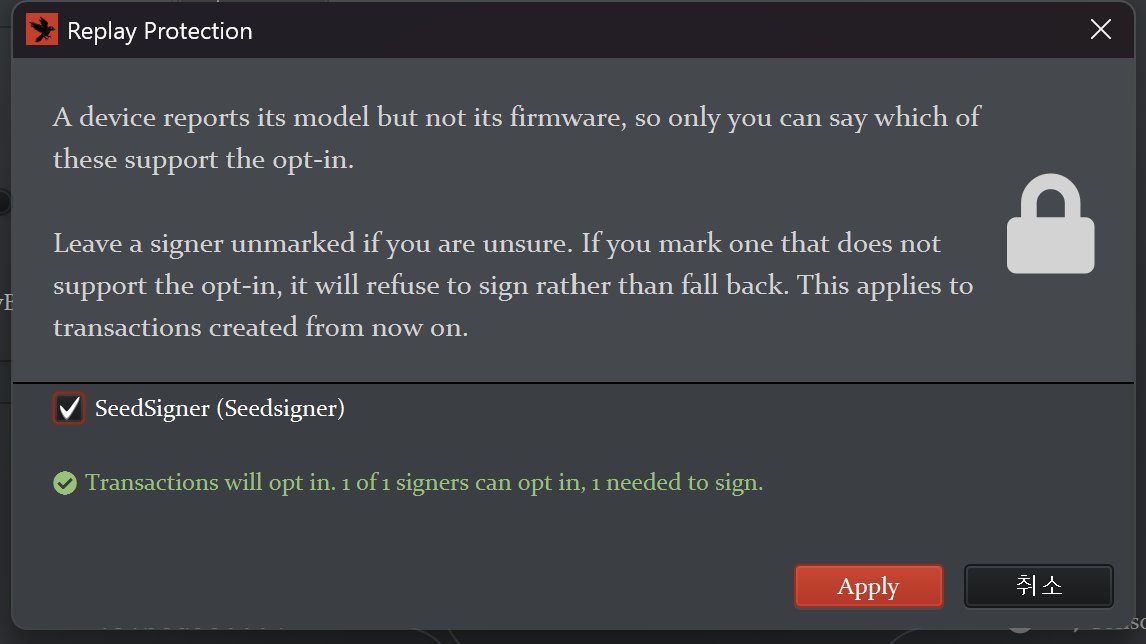
2. 포크된 펌웨어에 내가 기존 사용하는 니모닉을 입력하기 찜찜하다
xbt와 레거시 비트의 양 쪽 tx를 확인해가며 소액연습 해보시면 앞으로의 coincontrol 에도 도움이 될 것 같아요
Blake2b 하드포크 코인 분리 후기
1) privkeyio 버전 Seedsigner 이미지 잘 못 넣어서 1시간 헤맸다. 쌰갈..
2) 그 외에는 간단했음 개인 키 노출 없이 안전하게 가능했다. 레거시 비트코인 네트워크에서 리플레이 안되는 것도 확인
준비물
*와치온리 월렛 Shrike(스패로우 포크 버전)
*서명기기 Seedsigner(privkeyio 포크 버전 필요)
We've paused Blink services while we investigate a security incident.
An attacker accessed a limited number of custodial accounts and withdrew funds.
The large majority of funds are secure.
Non-custodial wallets are not affected.
LIQUID NETWORK UPDATE: INCIDENT REPORT
Status as of September 8, 2026, 19:10 UTC
What Happened?
On September 6, 2026 at 15:53:10 UTC (Liquid block 4,050,336), a vulnerability in the open-source Elements software related to how Liquid nodes cache range proof verifications was exploited, resulting in the creation of ~4,000 LBTC that were not backed by bitcoin held in reserve.
The individual(s) responsible for the exploit then used the SideSwap service, a Liquid Federation member that holds a peg-out authorization (PAK) key, to convert the unbacked LBTC to BTC via Liquid’s standard peg-out mechanism. Because the validation failure occurred at the transaction level before the peg-out was initiated, both SideSwap’s node and the Liquid Network’s globally distributed functionary nodes accepted the LBTC as valid. The functionaries processed the peg-out as authorized, releasing approximately 4,000 BTC through SideSwap’s whitelisted bitcoin address, which SideSwap then forwarded to the address specified by the exploiters. Before the incident, the Liquid reserve held approximately 4,205 BTC. Following this peg-out and additional peg-outs processed before operations were halted, the reserve balance fell to 197 BTC.
Key Clarifications
No keys were compromised. The Liquid Federation functionaries were not hacked, and no private keys were compromised. The peg-out mechanism that authorizes withdrawals to whitelisted addresses operated as designed.
Other Liquid-issued assets were not affected. USDT and other tokens issued on the Liquid Network were not impacted by the vulnerability, though they are temporarily unavailable while the network remains paused.
Investigation is ongoing. As is common in complex critical-system failure investigations, this incident arose from the convergence of several individually low-probability factors that interacted in ways that ultimately defeated the system's built-in redundancies. More detail will be shared in forthcoming communications.
What Steps Have Been Taken To Recover The Assets?
The individual(s) responsible for the exploit left a public message on the bitcoin mainchain identifying themselves as white-hat security researchers and requesting contact to address the vulnerability.
Patch deployed. Blockstream identified and deployed a patch to the Liquid Network’s bridge nodes, which was completed on September 7 at 01:09 UTC, ensuring the vulnerability is no longer exploitable.
Partial fund recovery. On September 7 at 16:09:25 UTC (Liquid block 965,950), the exploiters returned 3,400 BTC to the Liquid Federation peg wallet. Approximately 598.5 BTC (15% of the total) remains outstanding. Discussions between Blockstream and the individuals responsible are ongoing to secure the return of the remaining funds.
What Comes Next?
Our immediate priorities are recovering the remaining funds and resuming normal network operations safely and as quickly as possible.
Software update in progress. A fix for the exploited vulnerability has been developed and is undergoing multiple rounds of internal and external review. Blockstream is preparing an emergency release of Elements (v23.3.4), which is expected to be released as soon as possible, but within approximately 48 hours.
Network restoration. Once the software update is finalized, Liquid Network functionary operators will perform additional adjustments to resume full functionality and restore the corrected network state, including rejection of the invalid peg-out.
Ongoing updates. We will continue to provide detailed updates as the situation progresses.
What You Should Know
The Liquid Network remains offline at this time, while we work on reviewing the security fixes and network resumption code and coordinate with the white hat hacker towards timely resumption of the network with 1:1 backing for BTC. While the network is paused, users cannot transact on Liquid. If you operate a Liquid node, please watch for the emergency Elements release and follow the upgrade instructions when available. Users do not need to take any proactive steps to protect their funds at this time.
The Liquid Federation and its members are committed to resolving this incident in coordination with Blockstream and to resuming normal operations as soon as it is safe to do so.
The discussion between @Blockstream and the white-hat hacker (WHH) regarding the ~4000 BTC from @Liquid_BTC is happening in public. It seems to be their preference over email. As it's hard to follow the chain of messages in OP_RETURN, here's a summary with links.
11:30 AM PDT - WHH: "we are whitehats. contact us on chain"
https://t.co/sjKT0Ngtef
12:31 PM PDT - Blockstream: "Please contact [email protected]"
https://t.co/qx87Z2tvCn
6:49 PM PDT - Blockstream: [encrypted to hacker's key, PGP-signed by [email protected]]
https://t.co/9eV2hvTvBI
7:20 PM PDT - WHH: "sending most back to bc1qdlld6antmv4xug242ed83q7k4rqw50cwfns38szx4qu2f4jwaxxsuhwxxr, is that ok"
https://t.co/njF3jHqmmz
8:27 PM PDT - WHH: "Please fix the bug first. The chain is under risk at latest commit right now. Make sure every node is patched. Then we will transfer the money back safely after confirming the fix." [+ PGP-encrypted details to Blockstream]
https://t.co/JRvEKQiPF3
8:30 PM PDT - Blockstream: "Yes, thank you." (PGP-signed; answers the 7:20 question, not the 8:27 one — confirmed in the same block)
https://t.co/QfO4CtNDca
Status as of 9:12 PM PDT: ~3,998.5 BTC still unmoved, no further messages from either side.
Hacker address: https://t.co/c2j0xnEE9c
Blockstream just replied on-chain to the Liquid attacker's "sending most back, is that ok?"
PGP-signed, plain text this time: "Yes, thank you."
Signature verified. The return seems to be happening. 🍿👀
https://t.co/1TClTsIPC7
Statement on today's Liquid incident
Today at 14:05 UTC a customer sent 4,000 L-BTC to the SideSwap peg-out service. Our service processed it like any other order: the L-BTC was burned on Liquid with a valid peg-out authorisation, and at 14:28 UTC the Liquid Federation paid 3,996 BTC to the customer's Bitcoin address.
Blockstream has since established that the L-BTC in that order was created through a bug in the Elements software. As Blockstream stated, SideSwap's peg-out authorisation key was not compromised, and nor was any SideSwap system. Our service had no way to tell those coins from any other L-BTC.
What this means for you:
• Your wallet is not affected. SideSwap is non-custodial and your assets are controlled by your own keys. There is nothing you need to do.
• Liquid is paused by the Federation, so swaps, peg-ins and peg-outs are paused in SideSwap until the network resumes.
• Peg-outs already paid on Bitcoin are complete. If you have a peg-in or peg-out that has not completed, email [email protected] with your transaction id and we will handle it individually.
Blockstream and the Liquid Federation are leading the network-level response, including how and when the network restarts. We will not speculate on that.
The team is offline overnight. We will answer questions here and by email from tomorrow morning (UTC). Please do not send any new peg-in or peg-out deposits until we say services are back.
Peerswap node operators are advised to disable L-BTC swaps.
As a self-hosted swap implementation we don't have a way to notify everyone so please inform other peerswap node operators.
This looks very bad.
Follow @Liquid_BTC for further news.
Peerswap node operators are advised to disable L-BTC swaps.
As a self-hosted swap implementation we don't have a way to notify everyone so please inform other peerswap node operators.
This looks very bad.
Follow @Liquid_BTC for further news.
We are aware of a security incident on @Liquid_BTC. Purported white-hat hackers have withdrawn ~4,000 BTC (~$320 million) from the Liquid Federation wallet. The @Blockstream team is working on contacting them on-chain with a signed message.
What we know so far is that the funds were withdrawn via the SideSwap PAK (Peg-out Authorization Key), but that key was not compromised, nor were any others.
Exchanges have been notified and have already paused (or will pause) LBTC deposits and withdrawals. Other Liquid assets such as USDT, DePix, and RWAs are unaffected by this security incident.
Bridge nodes have been temporarily disabled, so no new transactions can be submitted to the network. Effectively, the Liquid sidechain is paused until this issue is resolved.
Liquid wallets will be impacted, and we're sorry for any inconvenience. Federation members are actively working on resolving this so we can restore normal network activity.
You can monitor the situation via @mempool's https://t.co/M46Zhn8nlY site below:
https://t.co/B8j9u4j6i4