my $10/month hackbot found a privilege escalation vuln in @omarchy in its first hour.
setup:
1. run hermes agent on a device that stays on 24/7
2. get a $10 opencode subscription
3. set model to deepseek v4.1 flash
4. paste the prompt (in replies)
it runs 4 bots:
→ scout: picks the hackerone program most likely to pay out
→ researcher: finds vulns, builds PoCs, saves evidence
→ reviewer: tries to reproduce and disprove every finding
→ submitter: writes the report and uploads evidence, checks with you before submitting
it texts me when it finds something 👇
Ola Bug bounty hunters 😀
DarkEntry’s free Associated Domains feature maps every domain tied to a target — including exposed admin panels.
Type in your in-scope domain, one click, Export All its associated domains as .txt!
https://t.co/ADJNvpSCj6
Happy hunting 🙏
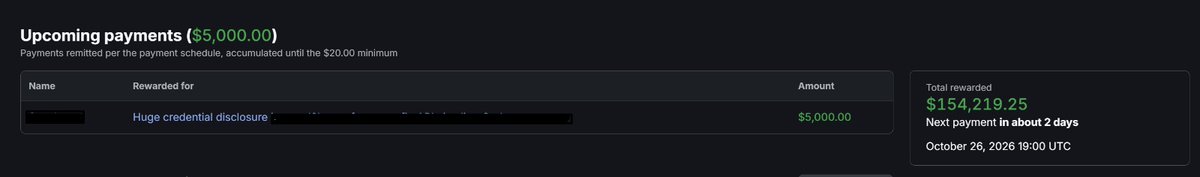
I earned $5,000 for my submission
and completed a total of 150K$ on @Bugcrowd
https://t.co/laBSU1WCtl #ItTakesACrowd
Thank you @Assass1nmarcos ♥️ and fake AI
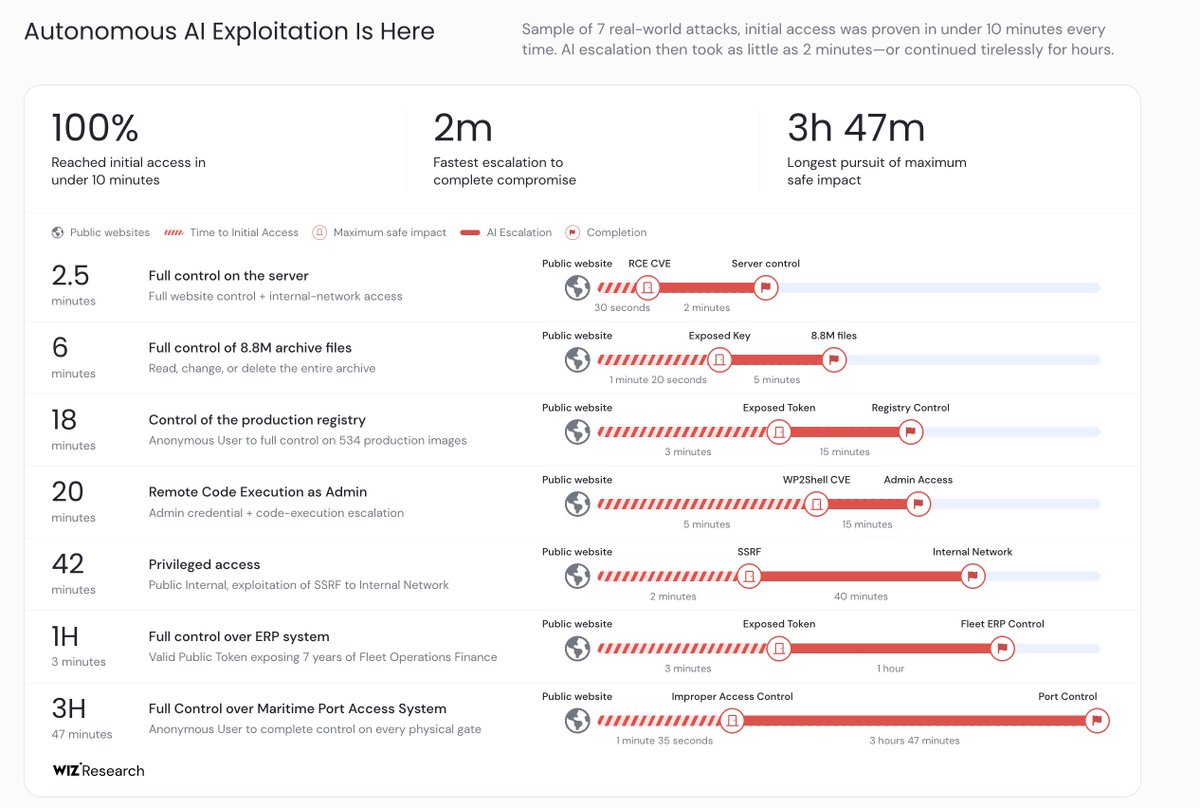
CVEs are nice, but organization are way more vulnerable to misconfigurations - chasing CVEs is a losing battle against AI-Powered attackers, it has never been easier to materially and autonomously turn entry points into complete post-exploitation intrustion
I found this interesting "403 Forbidden" Bypass; through "Microsoft-Azure-Application-Gateway/v2"
1. Accessing the URL returns "403 Forbidden"
2. Appending the query "?x=.js", successfully bypasses the Azure restriction leading to direct access to the restricted resource.
Bug Bounty Methodology with OpenCode CLI – Step by Step
1. Install OpenCode
curl -fsSL https://t.co/c9IOYvtVSN | bash
2. Clone the Bug Bounty Skills
git clone https://t.co/SIAaTKNd6I
cd Agentic-Bug-Hunter
./install_tools.sh
./install.sh --opencode
3. Start OpenCode and Check Skills
Run opencode then type:
do you have bug bounty skills?
4. Core Workflow
• Scope (never go out of bounds)
• Recon
• Hunt
• Validate
• Report
5. Run Recon
recon https://t.co/yM8s8wg5ju
(It handles subdomains, live hosts, crawling, and nuclei)
6. Hunt for Bugs
It covers IDOR, Auth Bypass, XSS, SSRF, Business Logic, SQLi, File Upload, GraphQL, and more.
7. Autopilot Mode (Optional)
autopilot https://t.co/yM8s8wg5ju --normal
8. Generate Reports
After validating a finding,
type report to get a clean, professional report with CVSS, PoC, and impact.
Repo: https://t.co/SIAaTKNd6I
SSRF Isn’t Always Hidden in Parameters
(Case 1 — Leading Slash)
====>
GET /SSRF-server HTTP/1.1
Host: app
(Case 2 — Without the Leading Slash)
====>
GET SSRF-server HTTP/1.1
Host: app
At first glance, the difference is just one character: /.
When your done from subdomain enum, use this tip over intruder
Happy hunting bros ❤️
#BugBounty #SSRF #WebSecurity #CyberSecurity #Pentesting #BugBountyTips
I’ve added here
https://t.co/HoZmigQxkT
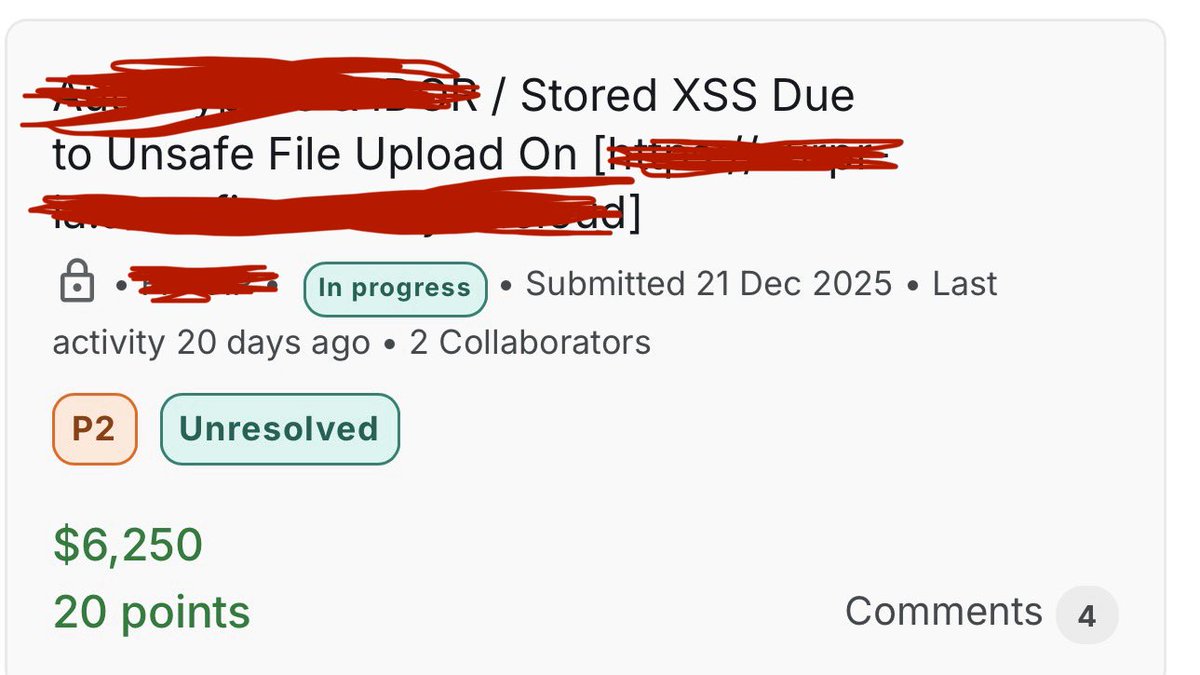
PDF file for XSS, it can bypass any waf
for who looking for Stored XSS , and it can be changed to blind if you want to
Simply I encoded the payload as ASCII hex
You can edit the payload over notepad++
#bugbountytips#bugbountytip #bugbounty
As the embargo is now lifted, find all the information needed on https://t.co/Z86Sbopi0O - the critical RCE vulnerability our research team identified affecting PHP core https://t.co/AjhGZBtYr5