You are an AI shill with no concept of technical understanding while masking like the current state of employers on LinkedIn, even the word "UNMANAGED" goes passed your illegitimate brain when willingly talking about such subject that, in fact, isn't meant for you to promote!
I hope you block me so I can't see your bullshit.
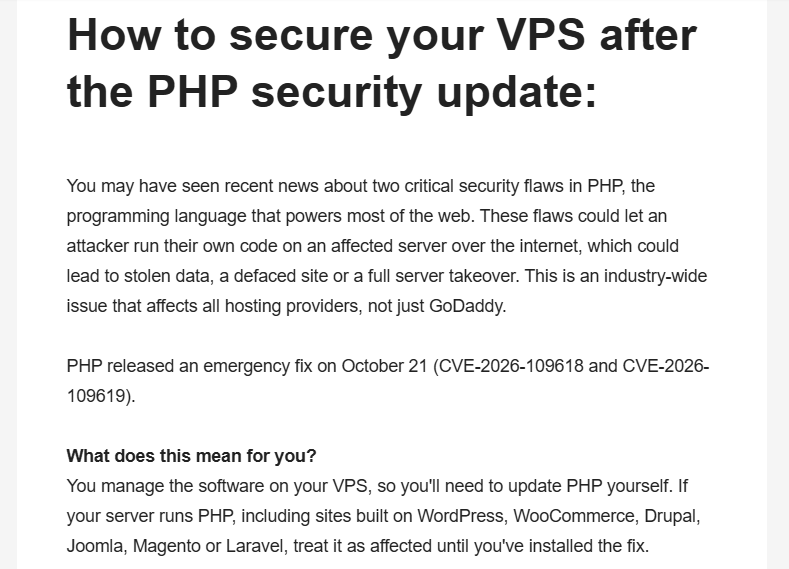
Did anyone expect @GoDaddy to do right during the PHP2Shell crisis?
A client who manages their own VPS but is on vacation just got this message.
GoDaddy refuses to install the patch for them.
Despicable.
Dear Threat Actor(s) targeting POS systems,
After @malwrhunterteam saw your malware payloads being distributed online, presumably trying to infect restaurants like Buffalo Wild Wings, I can see you've switched up your tactics a little.
Your latest payload, which is delivered from a different web domain, is absolutely cooked.
You forgot to strip the metadata out of your payload. I was able to immediately recover everything and quite literally get your payload back to damn near the original source code.
I can see how you're:
- Keylogging
- Managing these computers remotely with Hidden VNC
- Registering infected machines with your C2
- Attempting to evade security products
- Pulling credit-card numbers out of POS systems when customers swipe their credit card
- Attempting to move laterally over the network by exploiting SMB
- etc
It would be unethical of me to give you advice on how to write malware, but I really want to emphasize that I know you're using AI to write this malware and that you're making really goofy mistakes. Your domain "test(.)qovexira(.)xyz" is in plain text and is directly under the function "register_with_c2".
Code metadata you left in place:
- auto_ops_thread
- beacon_loop
- check_for_update
- dbglog
- delayed_persistence_thread
- detect_pos_role
- exec_command
- format_card_tracks
- generate_agent_id
- get_system_info
- http_get
- http_post
- hvnc_input_thread
- hvnc_spawn_app
- hvnc_stream_thread
- hvnc_task
- implant_upload_file
- install_persistence
- is_btc_address
- is_eth_address
- kb_buf_read (Keyboard)
- kb_hook_routine (Keyboard)
- kb_hook_start (Keyboard)
- lan_collect_neighbors
- lanmon_capture
- lanspread_smb_push
- peak_hours_thread
- pos_aloha_info_run
- pos_db_dump_run
- pos_ensure_drop_dir
- pos_lsa_dump_run
- pos_mod_op_7
- pos_module_run
- pos_port_sweep_run
- pos_ram_scrape_run
- pos_terminal_run
- pos_upload_file
- process_task
- read_file
- register_with_c2
- run_ch
- run_pivot_scan
- scanner_watch_thread
- self_heal_persistence
- send_result
- steal_browser_creds
- take_screenshot
- update_loop
- upq_worker
- watchdog_thread
- write_file
> see free trading platform thingie
> bunch of likes
> people say, "is it goop smelly?"
> people in comments say "no not goop"
> idk
> download
> .zip file
> open
> .zip (again) password protected
> password "github"
> enter password
> extract
> look inside
> artificially inflated binary
> 138kb
> all zeros
> actually 14kb
> strip zeros to make actual .exe size right
> ok
> look inside
> IAT stripped
> trying to hide functions it uses
> heavily obfuscated
> omg this is annoying
> just gonna emulate it real quick
> emulate
> starts taking pictures of desktop
> starts looking for cryptowallets
> starts trying to steal saved web browser passwords
> starts trying to take files out My Documents
> starts looking for other creds and session tokens
> connects to steam profile
> https://steamcommunity(.)com/profiles/76561198622044578
> connects to a telegram channel
> https://t(.)me/scii0n
> sends stolen data to 91.99.119.25
to answer the people in my DMs: yes, this is indeed goop. this is information stealer goop
> be me
> get dm
> "smelly, i found goop"
> wtf i love goop (malware)
> "My spouses work, a healthcare clinic, has been infected by malware. It arrived as a .rev file"
> lol ok
> download
> look inside
> .rar file named .rev
> ok nbc
> extract content from rar
> control panel applet
> lol is it 2002?
> look inside
> malware written in Go
> spend forever decoding what is goop code or go code
> 8 hours in
> deeply rustled
> Go goop has .svg document inside it
> goop compromises pcs
> uses .svg inside of it
> goop owners steal da emails on pc
> send .svg from goop to other ppls emails
> .svg inside tells ppl to download a .rev file
> goop propagation with social engineering
> neat
> keep bonking
> goop establishes connection with ip address
> 85.192.30.227
> not flagged by AVs
> goop first seen connecting to IP 2026-09-20
> sort of new goop maybe?
> keep bonking goop
> goop talks to ip address in funny way
> confuse me
> goop takes funny talk and determines what to do
> goop is told by ip to do stuff
> have goop transfer / upload files to ip or infected pc
> have goop start processes
> have goop update itself to latest version
> keep bonking
> finally discover the goop
> Dark Caracal a/k/a GoCaracal
> "cyberespionage group associated with Lebanon’s General Directorate of General Security (GDGS) that has historically targeted governments, businesses, journalists, and activists"
god damn lebanon government your malware was a fucking pain in the ass, i actually wanted to blow my fucking brains out a few times, ngl.
also, but your wifes work is being targeted by the lebanese government, prolly a problem idk, good luck on that bro
C2:
85.192.30.227
Dark Caracal (FQOYI_70153.cpl) SHA256:
8df20f4fd964c84bce577b3984bb5c65bccb876707cd9d94934a414bce7d7479
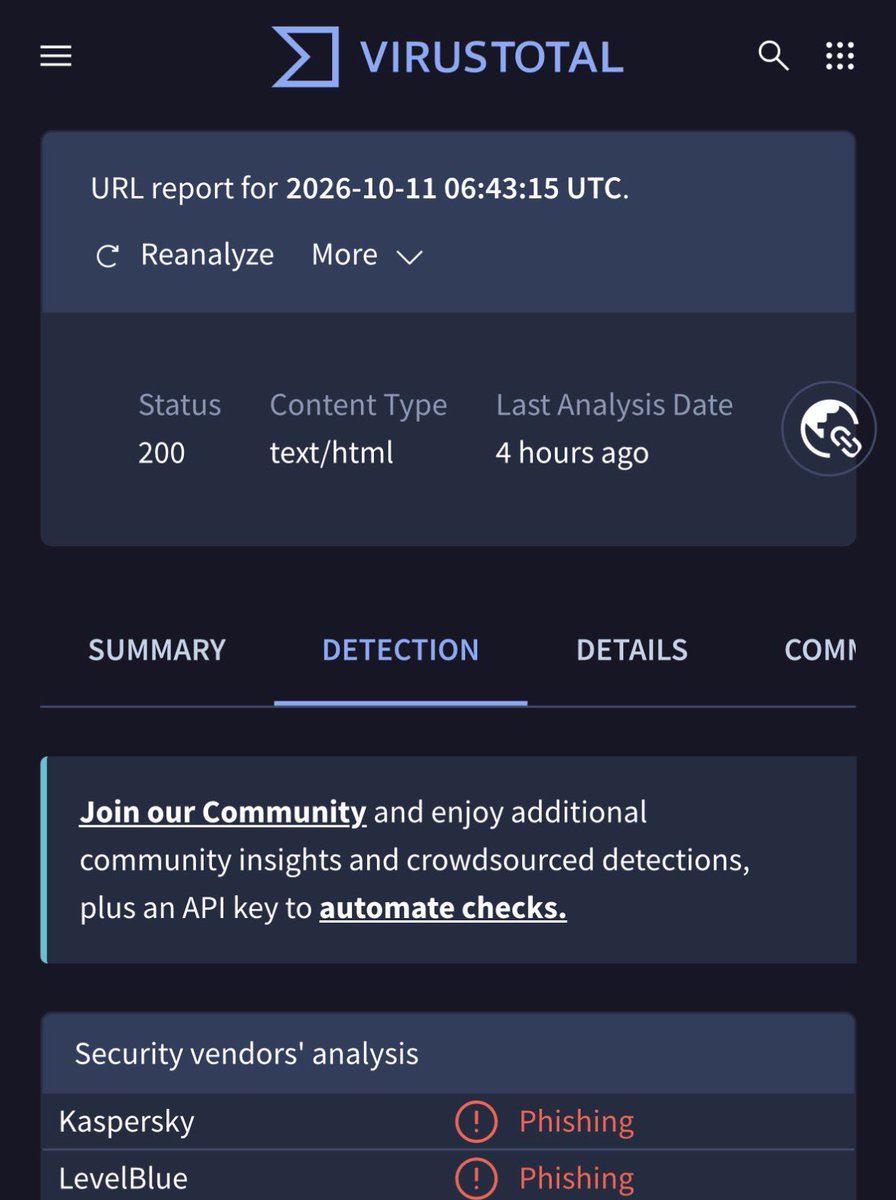
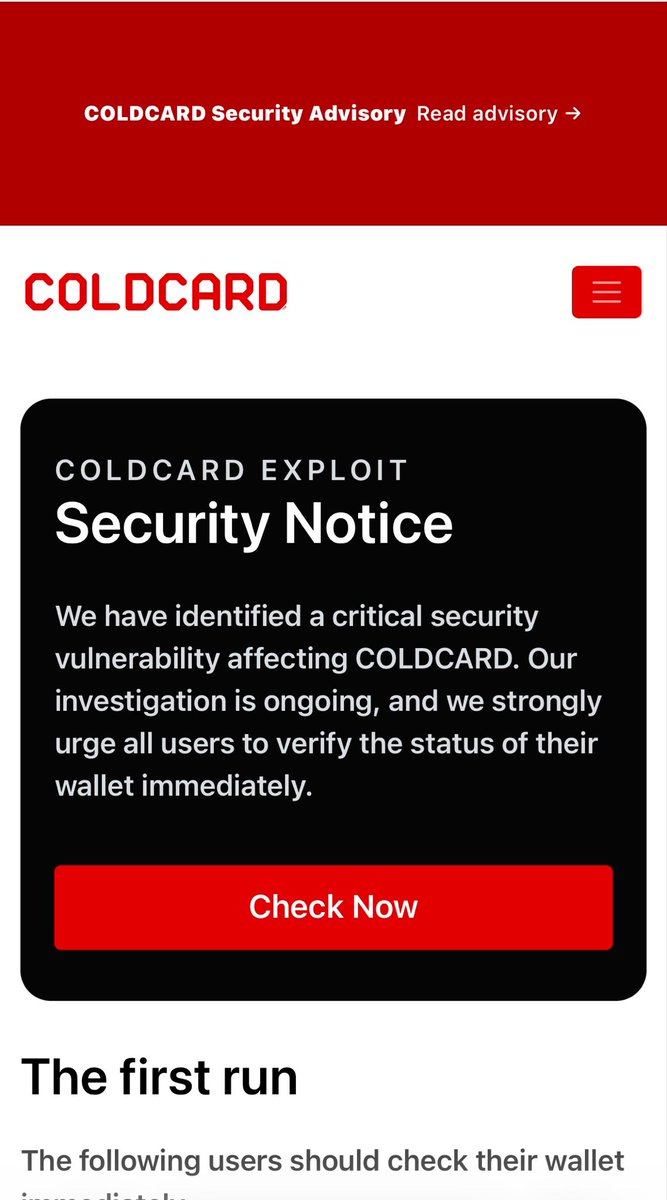
#ALERT 🚨 @COLDCARDwallet account was “compromised” while still having 2FA on and posted a phishing link.
And that’s exactly what it is. Your typical phishing vector.
Do not interact!
#cybersecurity
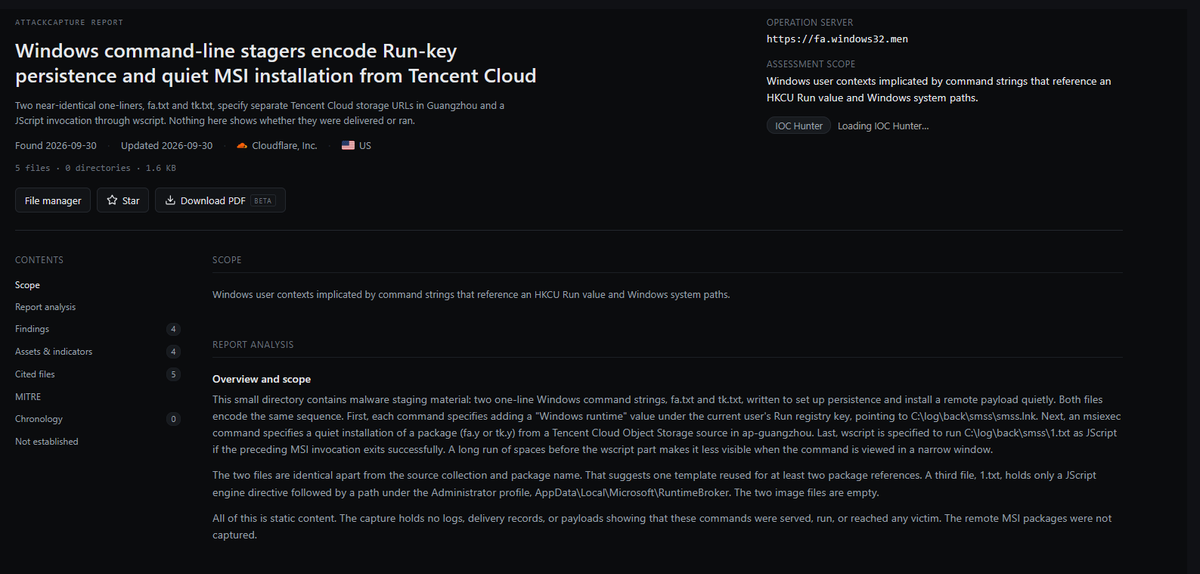
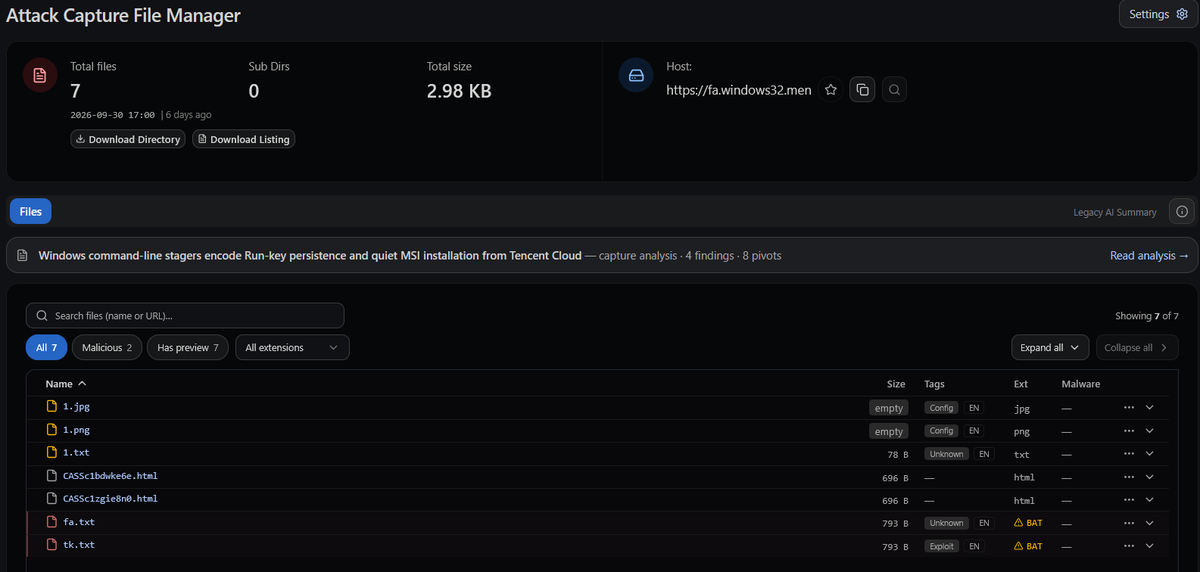
👿 #malicioius#opendir at fa.windows32[.]men
AttackCapture URL: https://t.co/PFbtZWLHv9
Found by @malwrhunterteam https://t.co/3gFjS0eYcU
What we found:
- Hosted at AS13335 (Cloudflare), 104.21.33[.]159
fa.txt / tk.txt: paired one-liner stagers. reg add on HKCU...\Run pointing to smss.lnk, then msiexec /qn pulling fa.y / tk.y from Tencent COS (ap-guangzhou), chained to a conditional wscript.exe //E:JScript call on success.
- Wscript invocation is preceded by a long whitespace run, pushing it off-screen in narrow terminal views.
- Two identical CASSc*.html files: document.write() injecting a script tag for kiss.thwc[.]cn/index-5988.js with a Date[.]now() cache-buster, plus a stock cloudflareinsights[.]com beacon.
- Captured 1.txt is a bare JScript engine directive pointing to a path under the Administrator profile; it doesn't match the C:\log\back\smss\1.txt path the stagers reference.