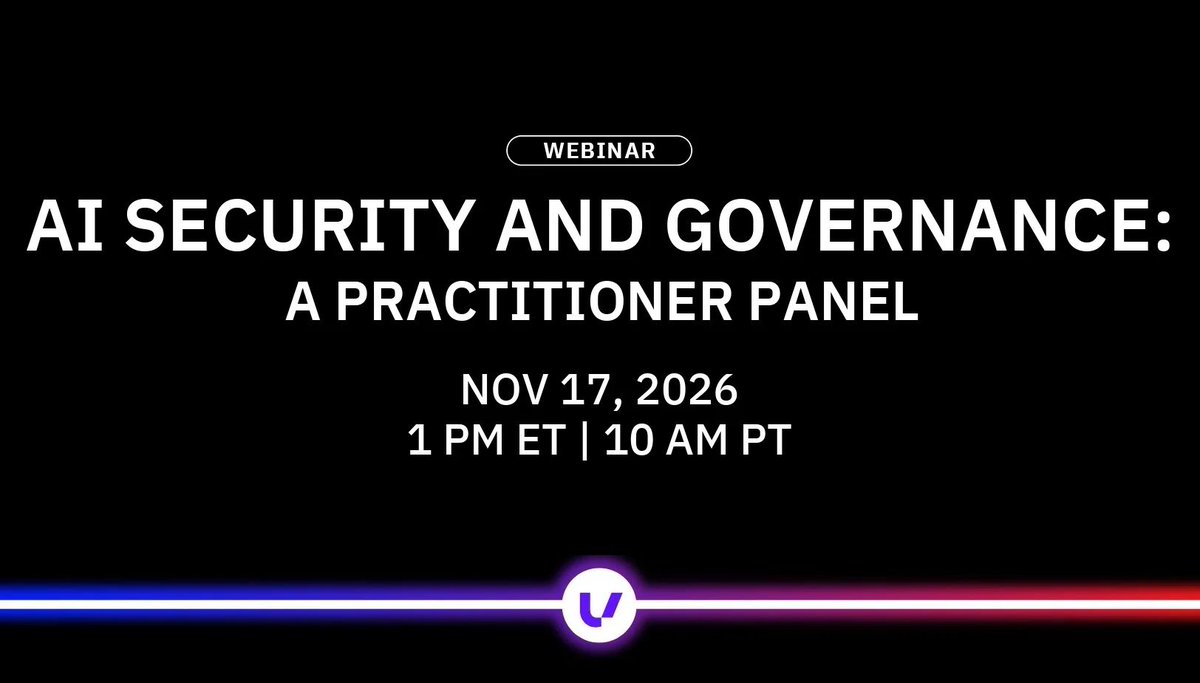
Tomorrow, 1 PM EST: Aravind Venkataraman, John Waller, and iMan Louis on who confirms AI policy shows up in how systems run.
Register for the live panel or the recording. https://t.co/gAQOCxPHfX
UltraViolet TIDE pairs threat intelligence with detection engineering. Every advisory covers how a threat operates, what it means for your organization, and the response steps your SOC can take. Get them delivered straight to your inbox: https://t.co/UZ4HGS2hZ9
Naming a RaaS operator rarely slows affiliates or ransom payments.
Without sanctions or a takedown, Qilin's 80% affiliate payout model keeps running.
TIDE's advisory covers the detections and backup checks to prioritize:
https://t.co/xCgKMEdHZZ
PHP runs on 70.8% of sites with a known server-side language. Every app on the host shares the runtime.
Learn how to validate your scope with offensive testing before year end:
https://t.co/Mp3uQvVkXw
Where does your AI policy end and your AI system behavior begin? Panel with Aravind Venkataraman, John Waller, and iMan Louis. Nov 17, 1 PM EST. https://t.co/gAQOCxPHfX
Ira Goldstein, CEO of UltraViolet Cyber, expects every security approach to get more purple within 3 to 5 years.
His @pulse2news interview covers why the job ends when the fix ships. 🔮
https://t.co/Gym8GYSGFl
ARTEX, an open-source AI attack framework documented by Google Threat Intelligence Group and Mandiant, ran a password spray with a 1-second median gap between logins. Your firewall and VPN logs see it first.
Full advisory: https://t.co/6GPSVuwdNG
Same model name, new quantization, different host. John Waller's paper ties each assurance result to the exact version tested. He presents it Nov. 6 at https://t.co/DLNMjm9DOa:
https://t.co/fYG1qDBxyX
Which identities in your enterprise will carry the most consequential access in 2027? John Waller expects the answer to be AI agents. 🔐
That is 1 of 9 predictions in our @VMblog byline, from John, Dan Gittis, and Drew Thompson.
Get the full set at https://t.co/fyuZaHCZi2
AI governance sets the rules. AI security tests whether they hold.
Three UltraViolet practitioners on how to connect them.
Nov 17, 1 PM EST. Register here: https://t.co/gAQOCxPHfX
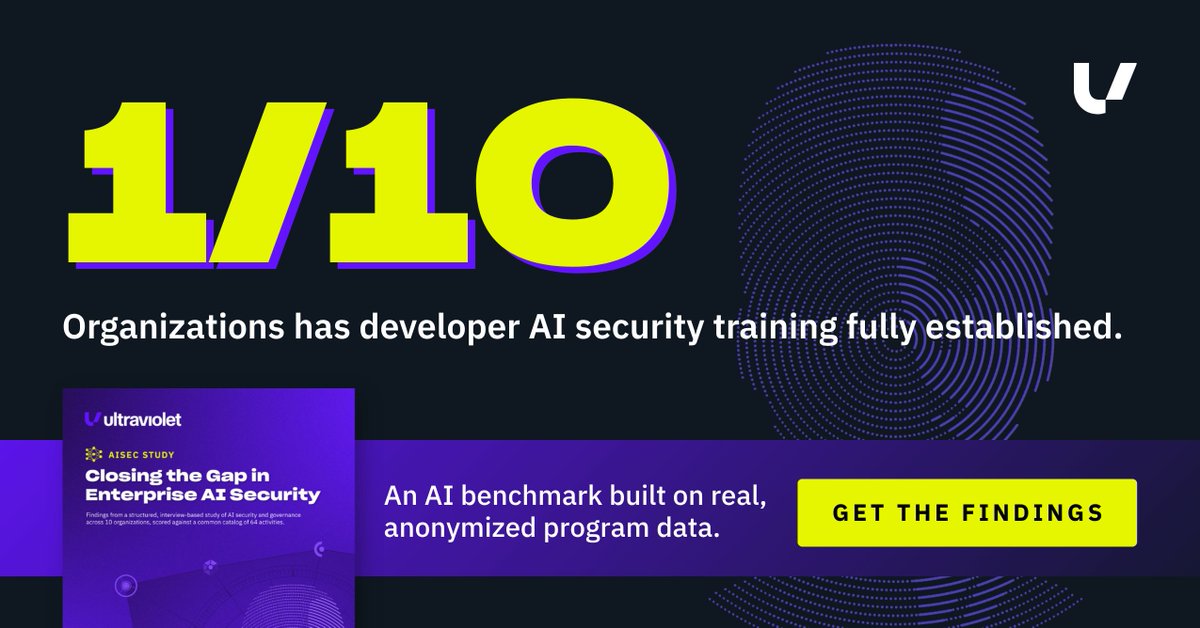
The biggest gap in the secure AI development lifecycle, from our AISec Study: developer AI security training. Only 1 of 10 has it fully in place.
https://t.co/9Rc5HuZYdQ
Before the next executive trip: check the cyber risk level for the destination. The TIDE Worldbook 2026 covers 199 countries, with a print edition to download. https://t.co/XulY6ceUpy
APT28 has abused Mocky, MockBin, InfinityFree, and Webhook for over 3.5 years, through heavy public reporting. The HOOKEDGE backdoor reuses HEADLACE code.
UltraViolet TIDE expects the same playbook to continue.
Full advisory:
https://t.co/c8Lp61bj4W
New PHP2Shell guidance from PHP on Oct 23: keep session.upload_progress.enabled=0 until the next bugfix release, and note separate CVE-2026-115560.
TIDE's update covers config, PHP 8.1, 8.0, and 7.4 backports, and WAF scope: https://t.co/x6DEemkkNN
Who at your institution can declare a video call with your CFO fake? 🤔
UltraViolet Cyber hosts the AI Impersonation Tabletop Exercise at #FSISAC Americas Fall Summit in Austin. Mon, Oct 26, 11:30 AM to 3:00 PM, led by Dan Gittis and Jonathan Leon.
https://t.co/YYldwXrIWb
Sysdig documented an AI agent cycling through six ransomware delivery methods in under 5 minutes until one worked. 🤖
UltraViolet TIDE's Q3 2026 Threat Review covers it and more.
https://t.co/bmEpdiZyHV
PHP2Shell: two unauthenticated RCE flaws in PHP core (CVE-2026-109618, CVE-2026-109619), both CVSS 9.2. Fixes shipped Oct 21 in PHP 8.5.12, 8.4.27, 8.3.36, and 8.2.35. No config workaround exists. Full advisory from UV TIDE:
https://t.co/EtQss0hGQw
This is what 130% more detection coverage looks like on the MITRE ATT&CK matrix. One real Equinox engagement.
The remaining gaps? Telemetry, not detections. Closing them just means enabling more log sources.
Dan Gittis breaks it down: