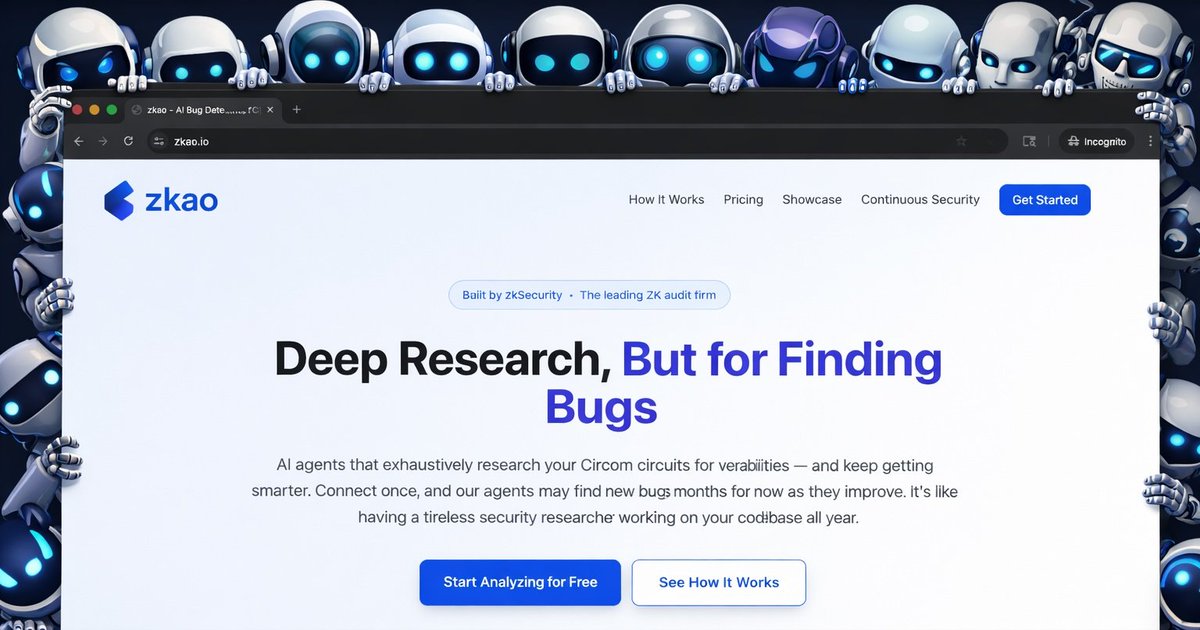
AI vulnerability research is non-deterministic.
The same model looking at the same code won't take the same reasoning path every time. Some paths find nothing. Some paths find the bug.
A single scan is a coin flip. But what if you keep flipping?
Introducing zkao.
latest on the zk/sec quarterly: what happened with all the recent proximity gaps papers and what does this mean for the security of our zero-knowledge proof systems!
wrote a thing about the recent proximity things.
Let's see if we can explain proximity gaps without getting lost in moon math!
Find it on the @zksecurityXYZ blog, link below
Introducing Vega, a folding-based ZK proof system for client-side proving tasks (e.g., age over 18, proof of humanity)!
Vega is fast with ~200 ms of prover time and 50 ms of verifier time for an end-to-end mDL-based ZK proof of age (including device binding)!
you like lattices? you like post-quantum SNARKs? we got you covered! Read our latest article on LaBRADOR, the core of greyhound and of most modern lattice-based SNARKs!
Looking at this past year, Circom is still going strong, being used in many projects on top of many different blockchains (Ethereum, Sui, Aptos, what else?). If you're working on circom, make sure you read our series on Circom pitfalls. link to new post below 👇🏼
Just published a simpler proof of the RBR soundness of FRI! Work with @0xAlbertG and Benedikt Wagner
I also wrote a blog post explaining the high level ideas of the proof. All you need to know is how to colour a graph!
Links to paper and blog below
1/3
What’s the simplest and *general-purpose* ZK proof construction you’ve seen? By ZK, I mean real ZK.
I think the simplest is BlindFold. (Link in the next post.)