T-E-D, Startups, Strategist, Transmedia Ent., Headstart Netwrk, Adrenaline Junkie...& whoever misinterprets my retweet as endorsement need to b schooled again
Every Indian needs to know about this because it is a massive deal for how we trust anything on the internet.
Let me explain.
When you open your bank's website, there's a small padlock next to the web address. That padlock means two things.
First, that you're talking to your real bank.
And second that nobody can read what you type, like your password.
So how does your browser know the website is real?
It checks the website's certificate. Think of it like an ID card for a website.
Your Aadhaar is trusted because the government issued it. A website's ID card is trusted because a certificate authority issued it.
A certificate authority, or CA, is a company that browsers like Chrome, Firefox and Safari already trust. If a CA says "yes, this really is this bank's website," your browser believes it and shows the padlock.
eMudhra is an Indian CA. It's a big one, with more than 60 million certificates issued over the years.
So how does a CA sign these ID cards?
Every CA has a secret number called a private key. It uses that number to put a stamp on each certificate.
Your browser checks the stamp to confirm it really came from that CA.
The whole system only works if that number is impossible to guess.
For the type of key in this story, it's supposed to be around 116 digits long.
Every computer on Earth working together for billions of years wouldn't be able to guess a number like that, just because of the sheer combinations that exist.
But here's what happened.
On October 17, Mozilla got a report that the private keys behind eight eMudhra certificates had been compromised.
The report came through a person called Wayne on Google's Chrome team.
The keys weren't 116 digits long.
All eight keys were smaller than 256. Security researcher Scott Helme found that one of them was just the number 4. Others were 66, 155, 156, 230 and 237.
So anyone could break them by trying 256 numbers. A basic laptop does that in less than a second.
Mozilla didn't need to know how Wayne did it. Its own team recovered the keys within two hours. Since then, several other people have found them on their own too.
To understand the gravity of the problem, a bad actor could make fake ID cards for any website they want.
Your bank, your email, a government portal.
Browsers that trusted eMudhra would have checked the fake stamp and shown the padlock like everything was fine.
If someone could get between you and the internet, say on public Wi-Fi, they could show you a fake site with a real-looking padlock and read or change what you send.
eMudhra says a script used during its key creation process back in April 2025 had a flaw. It made a second, much weaker set of keys, and those were used by mistake to create the certificates.
That means these weak keys were there for about a year and a half before anyone caught it. eMudhra says the person who found it may have used AI-assisted techniques.
The good news is that the response was fast.
Mozilla received the report at 8:06 pm UTC on October 17 and had pushed a block to Firefox users by 10:59 pm.
Google, Apple and Microsoft have also blocked these certificates for their users.
eMudhra revoked all eight the next morning and stopped issuing new certificates from the affected root.
Mozilla is now removing that root certificate from Firefox's trusted list altogether.
But there's still a lot of clean-up to do.
Browsers are mostly covered. But plenty of apps, servers and backend systems don't check these block lists. They need software updates to stop trusting the bad certificates, and some of those updates are still pending.
Real websites that used eMudhra are also affected. Yash Kadakia, founder of Security Brigade, estimates around 30,000 legitimate certificates will need to be moved over. A lot of those are likely Indian businesses and services.
See, we're moving our whole lives online, UPI, banking, tax filing, DigiLocker, government services.
All of it rests on this invisible layer of trust.
So, when an Indian company that's trusted by every major browser makes a mistake this basic, it hurts how the world sees Indian digital infrastructure.
This has happened before, and it went very badly.
In 2011, a Dutch CA called DigiNotar was hacked, and fake Google certificates were used to spy on people in Iran.
Browsers stopped trusting it completely, and the company shut down soon after.
For now, here's what you can do. Keep your browser and apps updated on your phone and laptop.
Be careful on public Wi-Fi. Type your bank's website address yourself instead of clicking links.
eMudhra still owes India a clear, public explanation of how a key that protects millions of people ended up being the number 4.
Dr. Jane Goodall filmed an interview in March 2025 with the understanding it would only be released after her death. This is her final message from it.
@gsraichur@airtelindia@Airtel_Presence You get pro rata waiver on ur monthly rent if you request for the same along with your complaint no. It's usually done promptly by Airtel. Airtel is quite customer friendly when it comes to addressing complaints.
@AnshulS9923@gujratpolice555@AhmedabadPolice Same story everywhere... I have been requesting the organizers in my society to stop it after 12 midnight, which is what the govt has also directed, but to no avail. On the contrary, I got hostile reactions from people. No mobile police patrol vehicles despite the noise
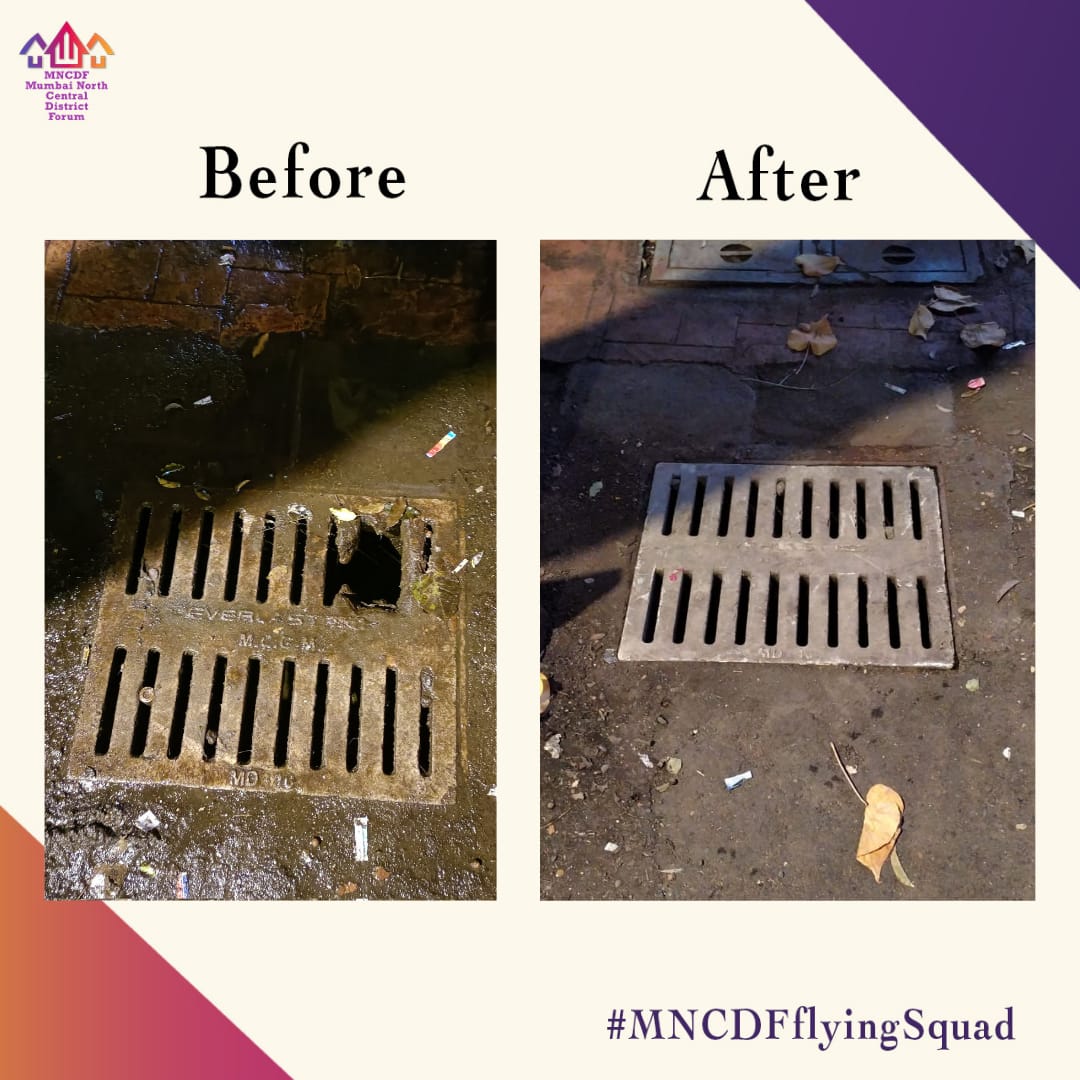
Action in 120 minutes! #MNCDFflyingSquad escalated pending complaint received from residents with regards to broken drain cover posing safety risk to citizens located outside NKGSB bank, Nehru Road, Vile parle E.
We thank Mr. Prashant Sapkal, AMC, @mybmcWardKE!
#CitizenWelfare
The floods & landslides in Assam, Tripura and Meghalaya states has worsened
Death toll rises to 90 in Assam
It's time to support our people from Northeast
1. Assam: https://t.co/Sz3ZQ5U58B
2. Tripura: https://t.co/sipqR3RhQT
3. Meghalaya: https://t.co/Wny4RgIjzI
Share this!
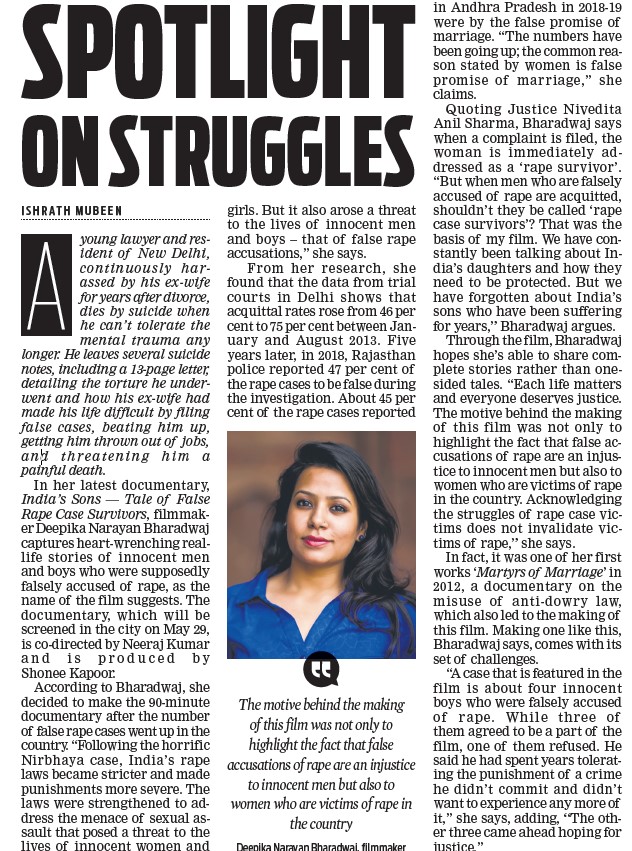
Director Deepika Narayan Bharadwaj brings to Bengaluru her documentary which traces the trials and tribulations of men falsely accused of rape in India, writes @ishrathmubeeen@Cloudnirad@tniefeatures
https://t.co/JnvhcODQsh
Register here: https://t.co/9ST2vi1al7
Discussion on Hudson Institute's Report on #Pakistan’s Destabilization Playbook: #Khalistan Separatist Activism Within the #US"
15th Oct 2021 Friday
Time: 08:30 A.M. Washington DC and Ottawa & 06:00 P.M. India
Hosted with @DefenceCapital
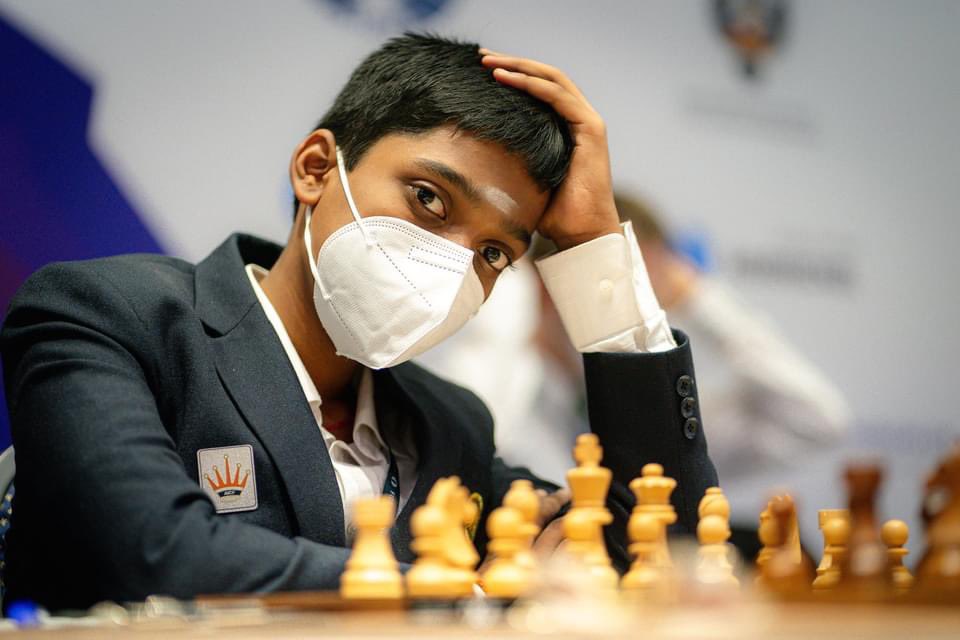
Let's all come together and encourage our National Chess team in #Sochi, #Russia . I wld love to watch the matches streamed live. pls share the link with me.
Few days ago Indian Chess team left for Sochi, Russia to play the World Cup. And not a SINGLE media outlet found it necessary to cover the story. Imagine the cricket team going for the World Cup.
And we are first to claim that chess was invented in India. So much for heritage.