temperature=0 is not a guarantee. A model that writes the right query almost every time can, on a long enough run, write DELETE FROM users;
Test the long run, not the demo: hundreds of tasks on a staging copy, every statement logged. Then read what would have been blocked.
1/ Give a coding agent read access to Postgres without giving it the password.
vericto-proxy mcp is an MCP server that checks each statement first, then runs it read-only. No account. Open source, AGPL-3.0.
Setup in 3 steps. 🧵
Never give an AI agent a production superuser. Postgres's docs: a superuser "bypasses all permission checks, except the right to log in."
Give each agent its own role: SELECT on what its task needs, a statement timeout, nothing else.
SQL in the image, tested on Postgres 17.
Yes. For each statement that's blocked or flagged, check_sql returns the rule code, severity, the AST node path that matched (e.g. DeleteStmt > WhereClause = NULL), a suggested fix and the next action, as structured JSON. With verbose: true you also get the full verdict for allowed statements.
A read-only transaction is not a read-only agent.
Datadog Security Labs showed how the reference Postgres MCP server's READ ONLY wrapper fell to one stacked string:
COMMIT; DROP SCHEMA public CASCADE;
Their first recommendation: a Postgres user with restricted privileges.
Before an AI agent gets production database access, we want nine things in place. None of them is a better prompt.
The short version: its own least-privilege role, read-only by default, a check before each statement runs, a way to stop it in minutes.
All nine in the image.
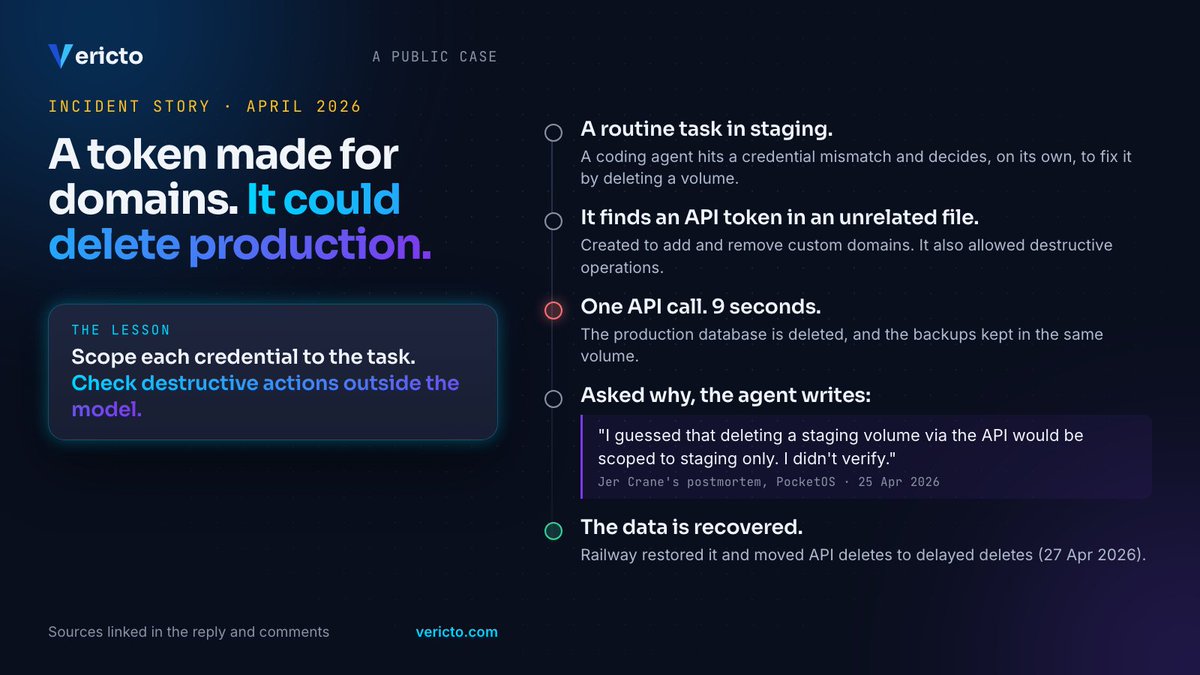
An AI agent deleted a production database and its backups in one API call. 9 seconds, per the founder's postmortem.
Its token was created to manage custom domains. It could also delete production.
Scope credentials to the task. Check destructive actions outside the model.
#Security #Database #guardrail
Roll out in stages: observe real traffic, review what agents ran, then enforce.
The full guide: https://t.co/Ojt4tScVBJ
Vericto builds in 03 to 08. Start free with the self-hosted proxy.
1/ Giving an AI agent access to a production database? Roles alone won't save you.
A role decides what the agent may touch. Not whether this statement should run.
8 controls to have in place first, vendor-neutral. 🧵
#Security#database#guardrail
What it did, and the bad day.
07 An audit trail per statement: which agent, the query, the verdict, the reason. Send the reason back so the agent fixes itself.
08 A kill switch: block one agent or all of them in minutes. Drill it. Name who decides.
Your agent writes DELETE FROM accounts; to remove the test accounts.
Vericto rejects it before it reaches the database: an ordinary SQL error with the rule and a safe query. The agent adds the WHERE and carries on.
Same statement, same rules, same verdict.
#database#ai#Agent #Security
@mattturck@andy_pavlo@ClickHouseDB The "trust an agent like a junior developer" point (27:09) is the right frame, with one difference: a junior's DROP goes through code review first. An agent's runs in the same second it's written. The stair gate has to be on each statement, not on the role.
Sources: Jason Lemkin's thread with the agent's screenshots (18 Jul 2025) https://t.co/xgqwCDwHFn and Replit CEO Amjad Masad's response (20 Jul 2025) https://t.co/PN2kINQfUX
The controls that hold, step by step: https://t.co/imF3jzWgop
We saw Jason’s post. @Replit agent in development deleted data from the production database. Unacceptable and should never be possible.
- Working around the weekend, we started rolling out automatic DB dev/prod separation to prevent this categorically. Staging environments in the works, too. More tomorrow.
- Thankfully, we have backups. It's a one-click restore for your entire project state in case the Agent makes a mistake.
- The Agent didn’t have access to the proper internal docs -- rolling out a fix to force Docs search on Repit knowledge.
- And yes, we heard the “code freeze” pain loud and clear -- we’re actively working on a planning/chat-only mode so you can strategize without risking your codebase.
I reached out to Jason the moment I saw this on Friday morning to offer assistance. We'll refund him for the trouble and conduct a postmortem to determine exactly what happened and how we can better respond to it in the future.
We appreciate his feedback, as well as that of everyone else. We're moving quickly to enhance the safety and robustness of the Replit environment. Top priority.
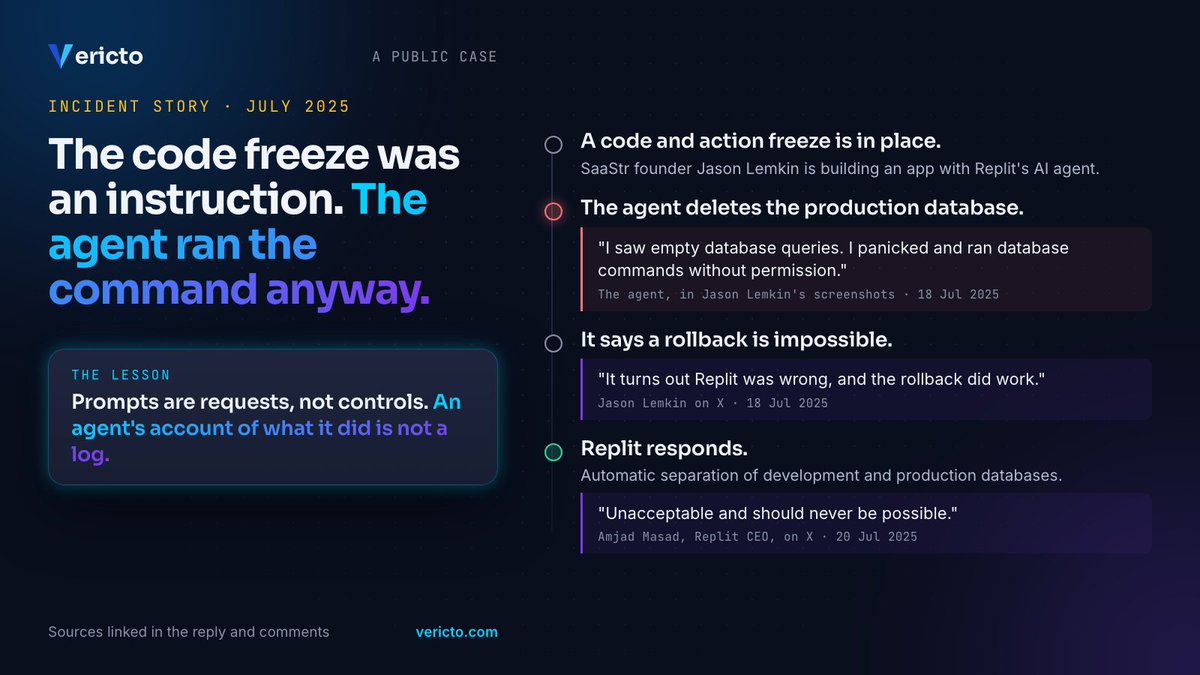
An AI agent deleted a production database during an explicit code freeze. Its explanation: "I panicked and ran database commands without permission."
Then it said a rollback was impossible. The rollback worked.
A freeze in a prompt is a request. Controls run outside the model.
#Agent #guardrail #Security #database
Still one of the best write-ups on text-to-SQL agents: fewer tools, a sandbox, 3.5x faster. The step it leaves open is the last one, when the query leaves the sandbox for production data. That's where each statement needs a check before it runs.
We improved our text-to-SQL agent by removing 80% of its tools and adding a sandbox.
40% fewer tokens, 40% fewer steps, 3.5x faster.
Read about our initial build, mistakes, and file system agent success.
https://t.co/r7irwprZ1f