BellsGive celebrates our Founders' Day, May 8 - the day Bellarmine first opened its doors for classes 170 years ago. BellsGive raises vital funds for our Direct Tuition Assistance Fund and The Bel... https://t.co/ct6F0ncTYZ #BellsGive
"Fixing the #AMNESIA33 vulnerabilities in impacted devices is particularly complicated because open-source software isn't owned by anyone. Such code is often maintained by volunteers. Some is two decades old; some of it is no longer supported." @Forescout https://t.co/487MJJFlVO
"The #AMNESIA33 disclosure is of particular concern because of its sheer scale and complexity, making patching very difficult and in some cases even impossible." @Forescout https://t.co/H0lt2Eg6dg
@Forescout discovered 33 new memory-corrupting vulnerabilities impacting millions of devices that can compromise your network. This presents immediate risk for orgs worldwide. Are you secure? #AMNESIA33 https://t.co/4LEtgvKfDQ https://t.co/pcnUCv5J0t
Researchers at @Forescout published a new whitepaper detailing how 33 security flaws baked into a handful of widely used code libraries could have catastrophic consequences for millions of internet-connected devices. @Gizmodo https://t.co/4P3RADljNk
“The issue is manufacturers w/ limited or no transparency into their supply chains. Beyond that some device manufacturers may go out of business or move onto other products, leaving consumers with no clue of what to do." @SCMagazine@Forescout#AMNESIA33 https://t.co/2dIqoVQD1K
Employees, partners & customers are all connecting to the data center or cloud from anywhere, securely or not. This makes each network environment complicated: a veritable #EnterpriseofThings. Here are 5 #EoT challenges from @Forescout to consider https://t.co/dOUnfXhph6
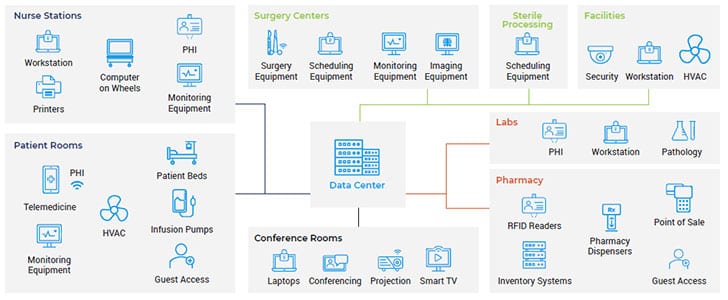
"Devices with distinct purposes are in the same network segments when they should not be communicating with each other. We see medical devices and personal devices in the same network segments. We also see a lot of mixture of healthcare and IT devices." https://t.co/7RRhwMZCtq
"Ransomware is ravaging businesses around the world, bringing manufacturing plants to a standstill, preventing hospitals from treating patients, and even keeping students from remote schooling during this pandemic." Greg Clark @Forescout CEO @DarkReading https://t.co/874Omeipy2
"The absence of any NAC protocol or technology for nontraditional devices connecting is the precise gap comply-to-connect (#C2C) seeks to close." Learn more from Katherine Gronberg, @Forescout VP Government Affairs https://t.co/fSy6skCWte
We're about to enter the next stage of complexity with the advent of 5G and while it comes w/ the promise of revolutionizing networking, the missing component is security. Learn more about how you can safely adopt #5G from @Forescout CTO @therobmcnutt https://t.co/jDm7QtDJHq
Michael Piccalo @Forescout is debunking myths surrounding the implementation of proactive cyber controls in operational technology. Learn more via @DarkReading https://t.co/M9sIfBj56t
“Some agencies are not able to detect all of the assets on their networks. If agencies are not reporting complete data, this seriously impedes the ability of the agencies and CISA to make the risk-based decisions that they are supposed to.” @Forescout https://t.co/uNcGH7V4lu
The latest report from @Forescout Research Labs shows 82% of US hospitals reported a significant security incident in 2018 or 2019. That's a lot of risk! Download the full report for the complete findings. https://t.co/rbkt3yReok
If you need help closing the gaps of existing security tools & making security processes more efficient, comply-to-connect is your answer. Learn more: https://t.co/hqBYwnlbz2
Did you know the typical healthcare org contains ~20k devices? New @Forescout Labs report shows these orgs have made great strides towards improving network security. But it only takes one vulnerable device to take down an entire system. @enterprise_time https://t.co/xOOMUSAeAQ