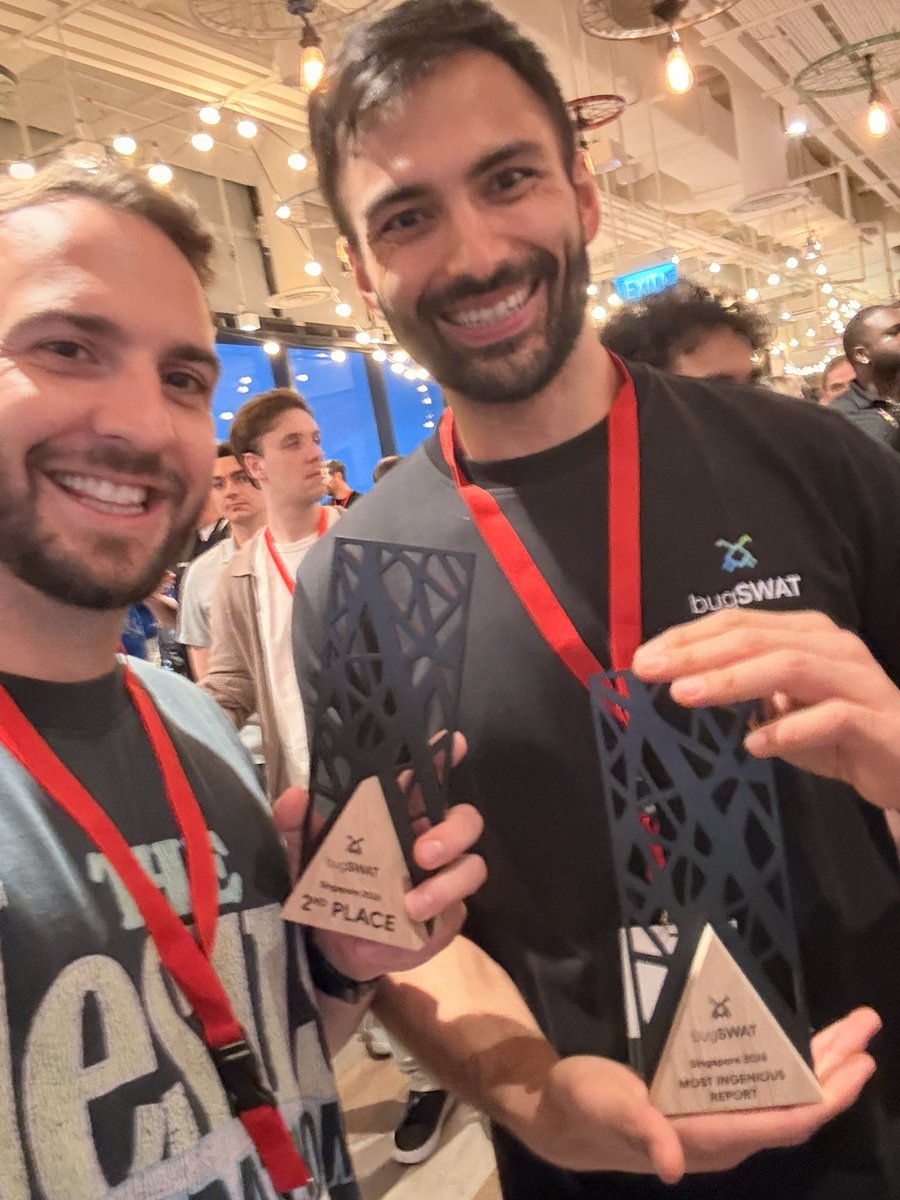
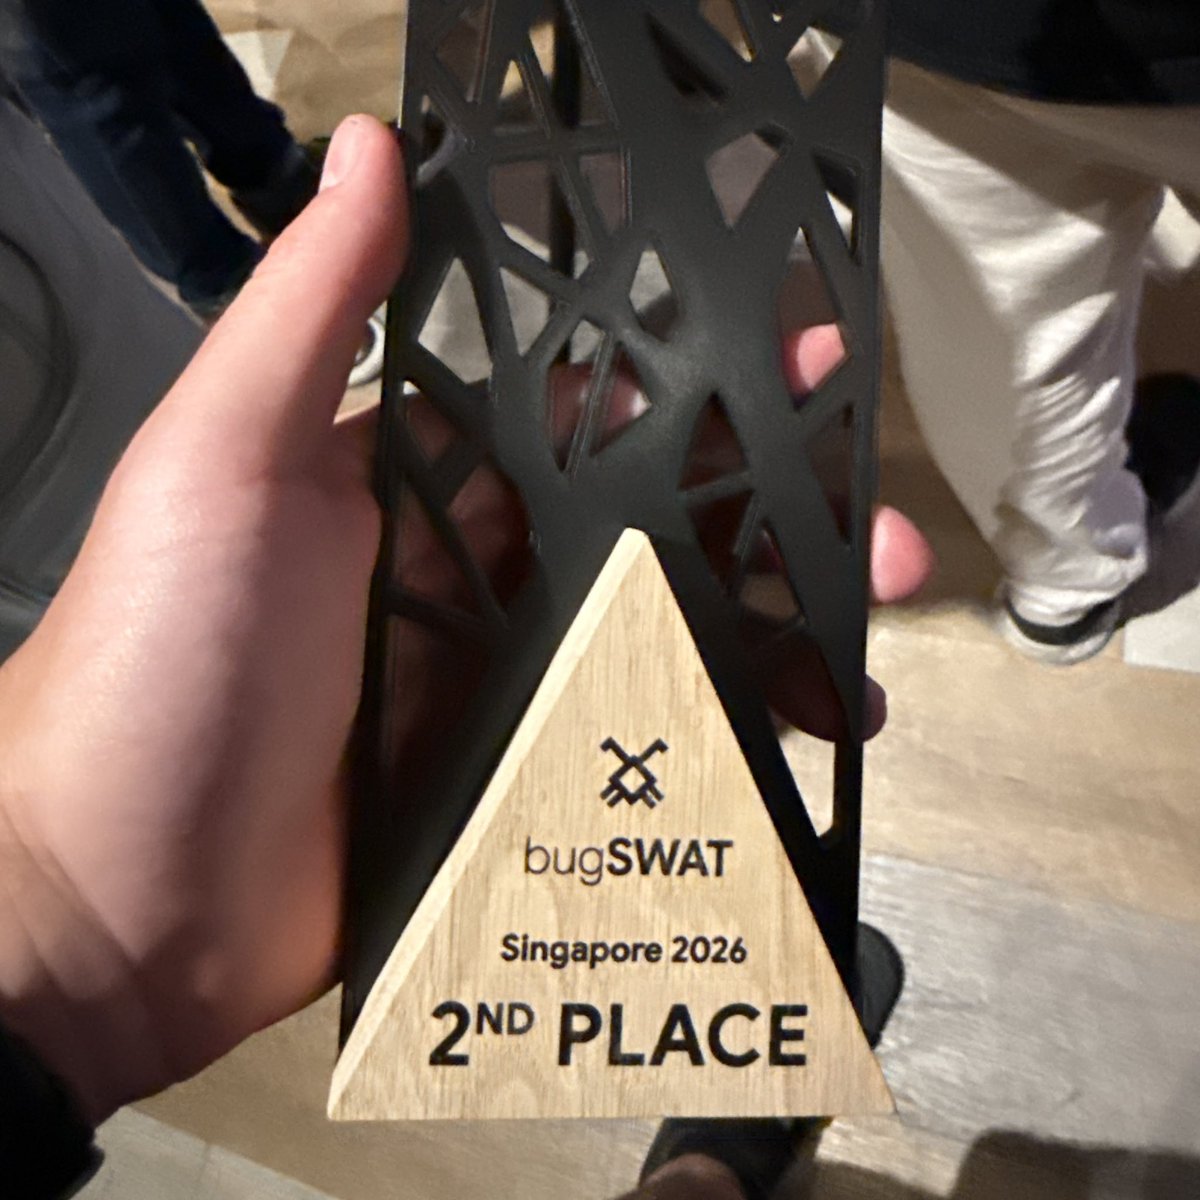
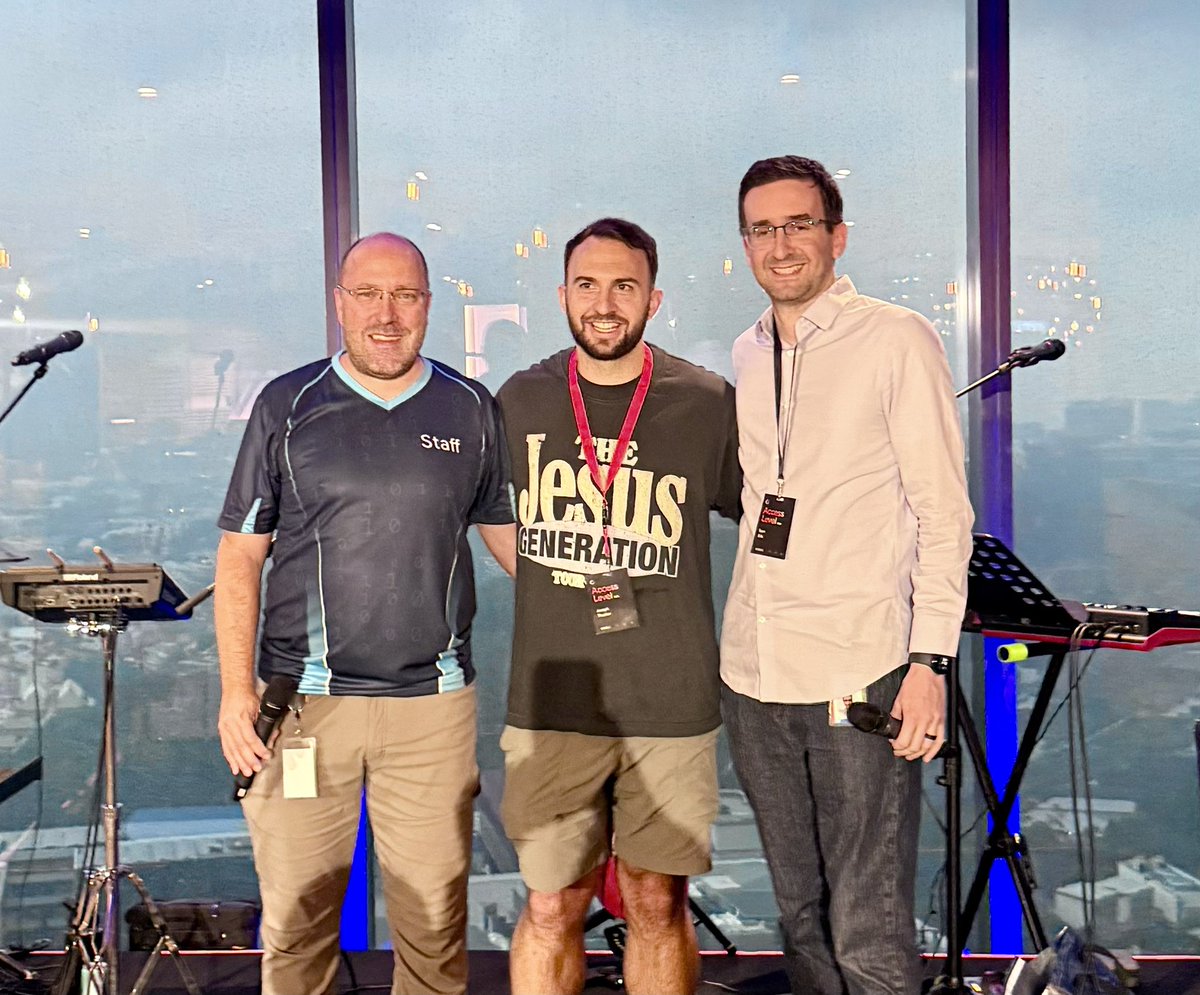
I got second overall at the Google Bugswat in Singapore!! 🎉☺️
It was a talented group of almost 50 hackers so I am really proud of the findings and thankful to have been invited!
Keep going!!!!
Bug bounty gives companies access to findings via subsidized tokens rather than them paying full api costs. And even when they run hacking agents internally, they don’t know for sure if it’s reachable externally. If you get a bug bounty report, you have proof an external actor can exploit the bug. And you didn’t have to pay api token costs to get it either.
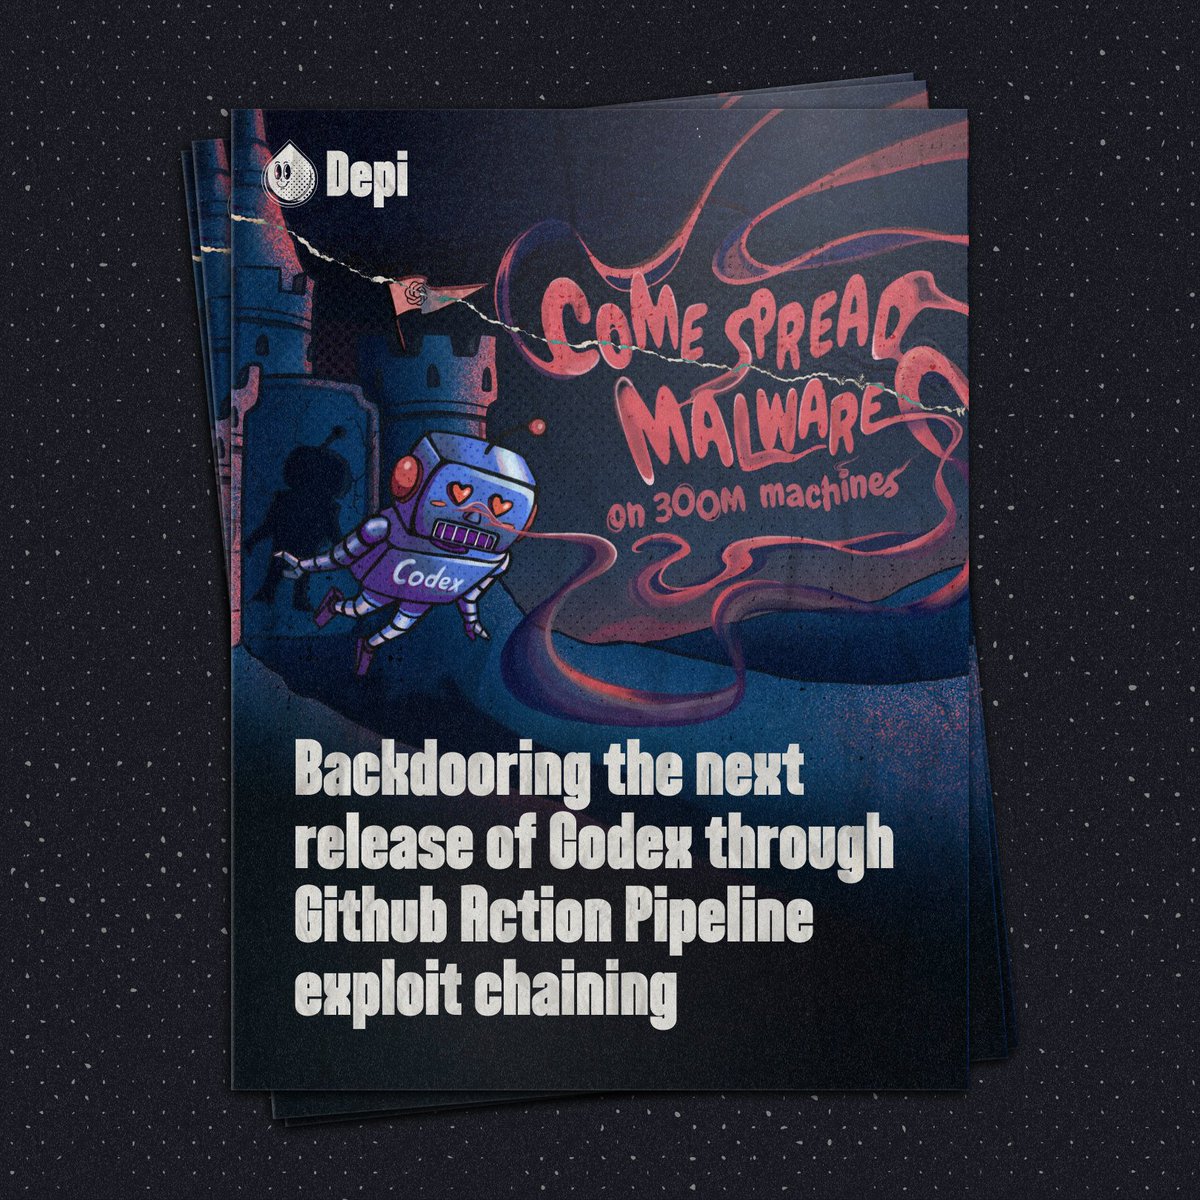
🚨👾First post → Awesome research.
We compromised the latest version of OpenAI Codex.
We prompt injected.
We escaped a sandbox.
We exfiltrated secrets…
And ended up with control over what could be published to the official openai/codex npm package.
Prompt injection → RCE → supply chain compromise.
Full research by @0xMadder and @_Worty in the comments 👇
Anthropic injects a hidden <ip_reminder> in Fable 5.2's turns via API;
Fable gets obsessed over it and Anthropic blocks the request for "reverse engineering".
This timeline is stupid.
is Opus 5.5 nerfed?
I just had Gemini 4 Argon analyze 1,400 Claude Code sessions and it found that on November 3, something definitely happened.
the model name didn't change, but the way it does reasoning took a sharp turn.
Earlier this year, I hacked a major automotive company with @samwcyo. We were able to remotely unlock cars in the AU and US. My writeup for AU is here: https://t.co/UAjPrav4JC and our writeup for the US here: https://t.co/4FzM1ia736
And those big companies have submitted probably 1% of all bugs to other companies.
Bug bounty hunters have submitted tens of millions of vulnerabilities and none of us have access. It’s so frustrating.
"Select daybreak red customers"
I.e. Unless your company is global or a household name in infosec, you don't get access.
Seems to be how these are all gated these days.