I'm excited to announce I'm joining @OpenAI!
I left Robinhood in March of 2025 to embark on a wonderful year and a half long career break. I used that time to: travel (I went drifting in japan!); build a low-latency arbitrage bot on Solana, briefly becoming the 60th most profitable arbitrage bot on the chain; and learning @leanprover in service of building an accurate model of rust to prove `unsafe` rust code was free of UB!
But a lot has changed. For one, most engineers I knew were, at the time, leveraging Github Copilot as an "intelligent autocomplete" to accelerate parts of writing code. Software was (and at many places, still is) manually reviewed, and there was much doubt, especially from myself, that models could ever improve to the point to economically handle the more complex tasks of implementing entire features, proving conjectures, or discovering, and exploiting, novel 0-day vulnerabilities.
Clearly I was wrong! I've been shocked and inspired by the rapid advancement going on in the industry while I was away. One thing has been abundantly clear: security is changing.
I'm excited that I get an opportunity to work on some of the most important problems facing our industry today. And I get to play a meaningful part in discovering, and contributing, to the next generation of strategies required to secure this burgeoning technology.
@ThePrimeagen@codegirl007 This concept is what made me fall in love with Rust originally. It did a good job of striking the balance between powerful type system to prove useful properties, but still usable enough to build real software.
With AI the economics of proofs change though
Someone told me last week to look for “signposts” that might indicate attacks were getting significantly faster and worse than the historical norm. Do you think we’re seeing any of those?
Day 17/ Bet you thought we forgot, but no, it’s reset day today.
Also good time to remind you to get Daybreak Blue access, it only takes 15 mins and you don’t want to have to do it in the middle of an incident.
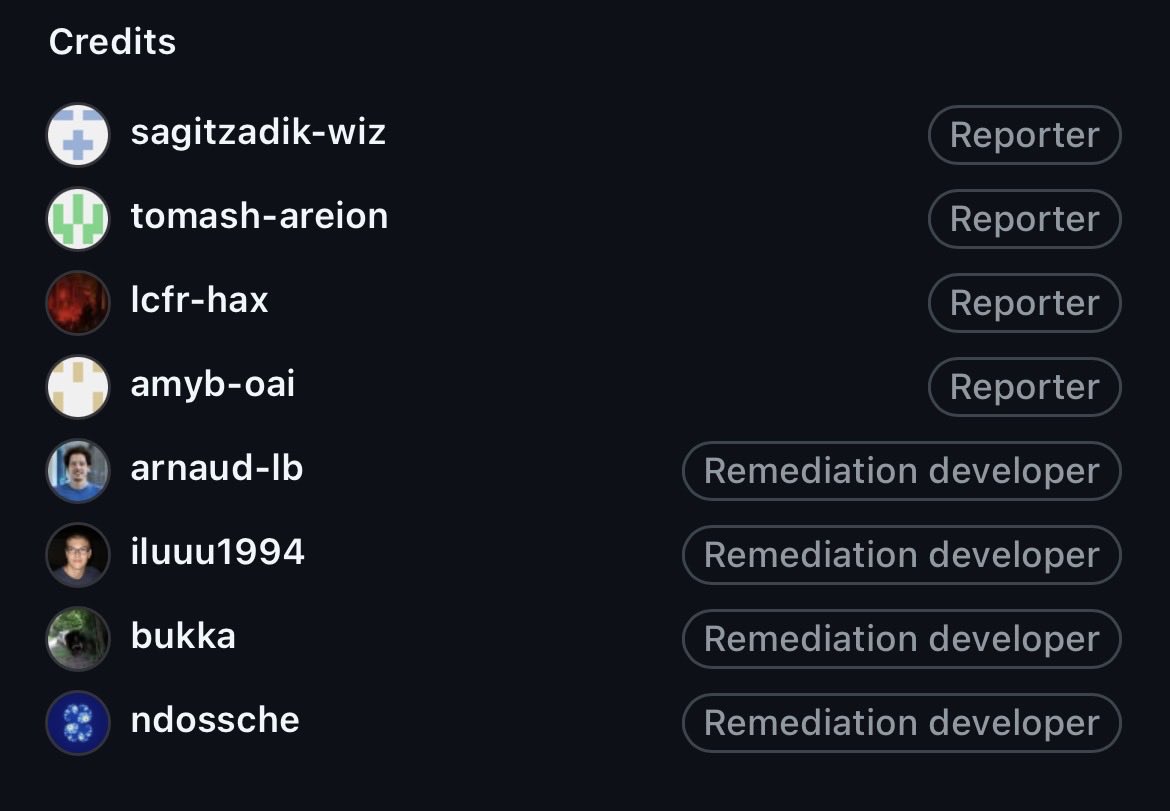
php2shell is the most consequential vulnerability I have ever helped discover. I am proud of how our team worked closely in coordination with the PHP Foundation to provide support and to harden the patch in preparation for this release. Please read more about our approach:
Node.js Security Advisory: a high-severity RCE flaw in Node's Brotli decoder affects Node.js 22, 24, and 26.
Vercel WAF rules are live for every project and block known exploit patterns.
https://t.co/JtfEshHnOC
gotta give it to @OpenAI and their sane daybreak program
heif heist by harsh
kvmescape by paulos
php2shell by lcfr
gitlab rces by joaxcar
chrome full chain by moyix
wordpress rce by hashkitten
all largely thanks to openai daybreak giving researchers access to gpt 5.6 sol.