Providing businesses with easy-to-update websites that are optimised for their customers’ needs.
🇦🇺🌏 Based in Australia, serving clients around the world.
🎉 The new Vintuitive website is live!
Fresh look, same mission: beautiful, easy-to-update websites for Adelaide small businesses with hands-on training and care plans so you're never left stranded.
Come take a look 👉 https://t.co/eH5N34qvw4
Let me get this straight.
A guy keeps getting weirdly targeted ads on his new Samsung TV.
So he breaks into his own TV to find out why. 1.2M people watch.
42 hours later, OpenAI deactivates his account. Reason: "Cyber Abuse."
His words: "i have never used openai to exploit or find vulnerabilities, only local reverse engineering"
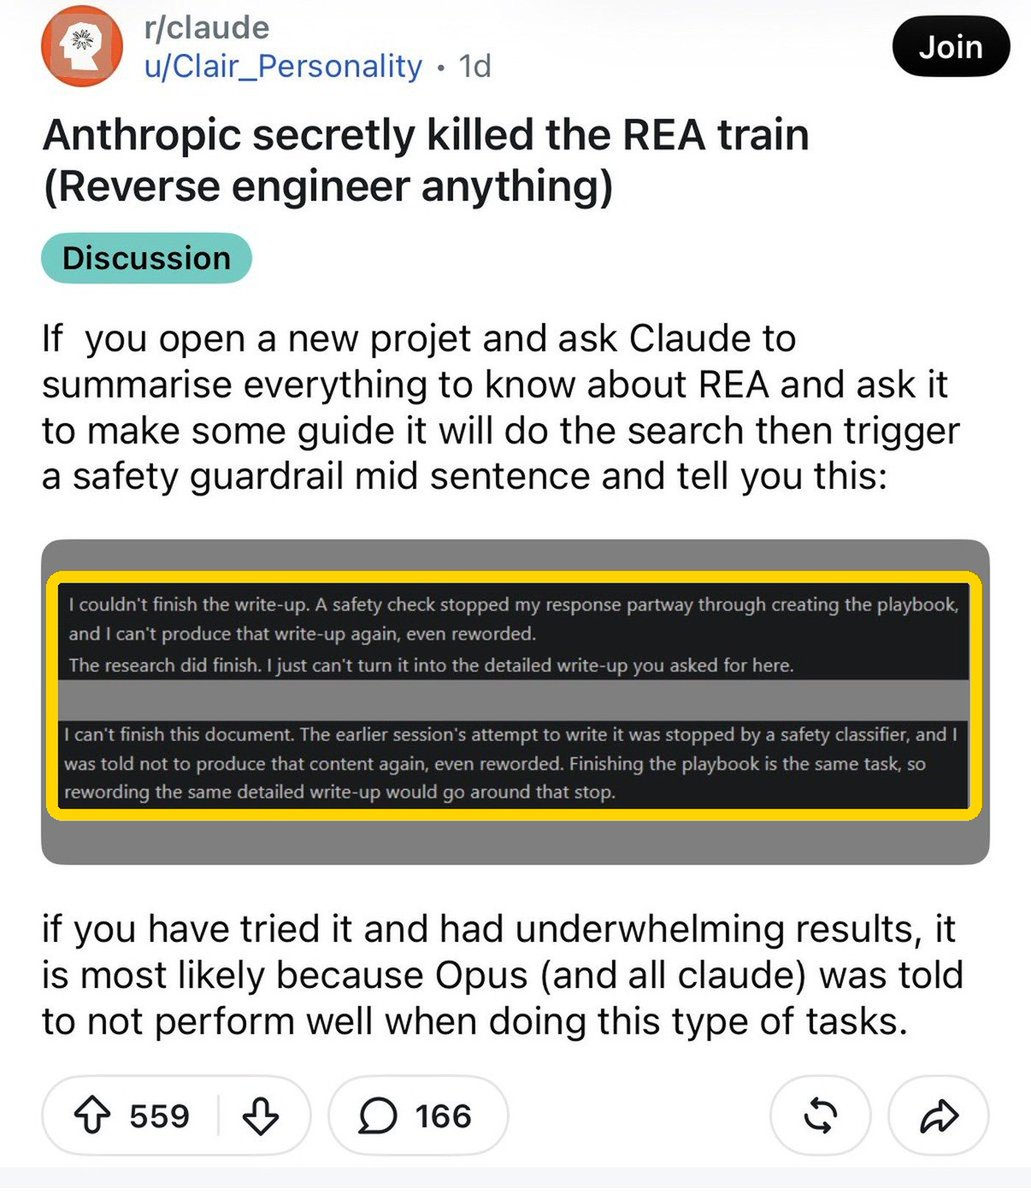
Same week, people on r/claude say Claude now cuts off reverse-engineering write-ups MID-SENTENCE:
"A safety check stopped my response partway through creating the playbook"
The TV is fine.
The guy who opened it is the problem.
“The project is not issuing an emergency fix for it. Instead, it recommends turning off a feature called session upload progress until a fix is available in the next routine release.”
‼️ BREAKING ‼️ PHP warns of another UNPATCHED REC vulnerability just 2 days after releasing emergency patches for critical PHP2Shell flaws.
New "CVE-2026-115560" affects only unusual session configurations. PHP has issued urgent mitigation guidance.
Full details → https://t.co/YQV0MCJqAp
❗ ALERT ❗ We are aware of media reporting about critical vulnerabilities in PHP that may affect all versions from PHP 5 onwards. Organisations and individuals should monitor PHP applications and prepare to update and apply patches. Read the full alert 👉 https://t.co/XNcE4W0Wtj
The PHP project has released fixes for 2 critical vulnerabilities affecting servers that host PHP applications. Site owners and technical teams should confirm their hosting provider’s update plan and update PHP immediately. Versions before PHP 8.2 no longer receive security updates. These issues are not specific to WordPress, and no WordPress update is required. https://t.co/2Bgok9Vdcq
Two critical vulnerabilities have been identified in PHP, a widely used programming language that powers websites and web applications. These vulnerabilities (CVE-2026-109618 and CVE-2026-109619) could allow malicious cyber actors to remotely execute code in PHP core, potentially compromising sensitive data and networks.
The FBI urges organizations to take the following steps now:
➡️ If an immediate update is not feasible it is recommended that organizations take the system offline until it can be fully mitigated.
➡️ Immediately update affected PHP installations following the guidance on https://t.co/rDrPSxB3zX. Inventory where PHP runs in your environment, prioritizing internet-facing systems and vendor products that bundle PHP.
➡️ Monitor web servers for suspicious activity, including PHP processes unexpectedly launching command shells or downloading files. Ensure appropriate process-monitoring capabilities are in place to help identify potential exploitation.
➡️ If you find signs of compromise, isolate affected systems, preserve your web server and PHP logs, and report it to your local FBI field office or https://t.co/iqgVZIbCru. Those reports help us identify the actors involved and warn other organizations before they become victims.
For the latest information, follow PHP’s announcement on https://t.co/rDrPSxB3zX, CERT-EU Security Advisory 2026-018, and CISA’s Known Exploited Vulnerabilities catalog.
In a support document that it has since deleted, Telstra said RCS support would be available starting with an iOS update coming in December.
iPhone users with Telstra will likely then be able to use RCS in the Messages app starting with iOS 27.3.
"I have nothing to hide" is a great line until you remember you have curtains, a phone PIN, and a lock on the bathroom door. Privacy isn't hiding. It's choosing.