Forge customers: Five Nginx vulnerabilities, known as NGINX2Root, were disclosed today and affect servers managed by Forge.
Forge doesn’t patch servers automatically, and we recommend users apply the fix to their servers now.
We’ve emailed all users with instructions → https://t.co/TGG1ZtXNjP
If Ohio State wins out, Jeremiah Smith should win the Heisman Trophy.
He is the best player in the country.
But I also need to address something.
Buckle up, I got time today.
My Heisman brother @DesmondHoward said that Jeremiah Smith has never been the difference in any big games for Ohio State over the past 2 years in an attempt to discredit this young Superstar just because he goes to Ohio State.
It has been determined that his statement is a lie.
But here is the truth.
Jeremiah Smith has more receiving yards, TDS, and catches in his career than Desmond Howard.
Jeremiah Smith is a National Champion. Desmond Howard is not.
THIS YEAR, Jeremiah Smith had 8 catches for 164 yards against #4 Texas in a loss and was unstoppable against #14 Iowa with 11 catches for 206 yards in a win.
Why would Desmond specify the last 2 years?
Because when Jeremiah Smith was a FRESHMAN he went for:
-6 catches for 103 yards 2 TDs to beat #9 Tennessee in the CFP
-7 catches for 187 yards 2 TDs to beat #1 Oregon in the CFP
-5 catches for 88 yards 1 TD to beat #7 Notre Dame with the game sealing 3rd down conversion to win a National Championship.
Jeremiah Smith is the Big Ten all-time leader in receiving yards, receiving touchdowns and tied for first in 100 yard games with 17.
Jeremiah Smith is the FBS record holder for receiving yards for a player in his first 3 years in college.
You see Desmond Howard and anyone with eyes knows that Jeremiah Smith is ALWAYS THE DIFFERENCE on any field he steps on.
Jeremiah Smith is the best player in the Country, one of the greatest WRs we HAVE EVER SEEN in College Football History and an incredible young man who ALWAYS SHOWS UP.
The Heisman fraternity would be honored to welcome him into our family.
Desmond Howard is a legend, but even legends have to be checked. He needs to stop hating on Jeremiah Smith and recognize his greatness regardless of what school he went to.
First look at Paraframe 🎨 @calebporzio walks @mattstauffer through his new AI design tool. You capture your real app onto an infinite canvas, spin up variations, and hand the winner to your agent to build.
Listen now🎧: https://t.co/2Vl2DUyC98
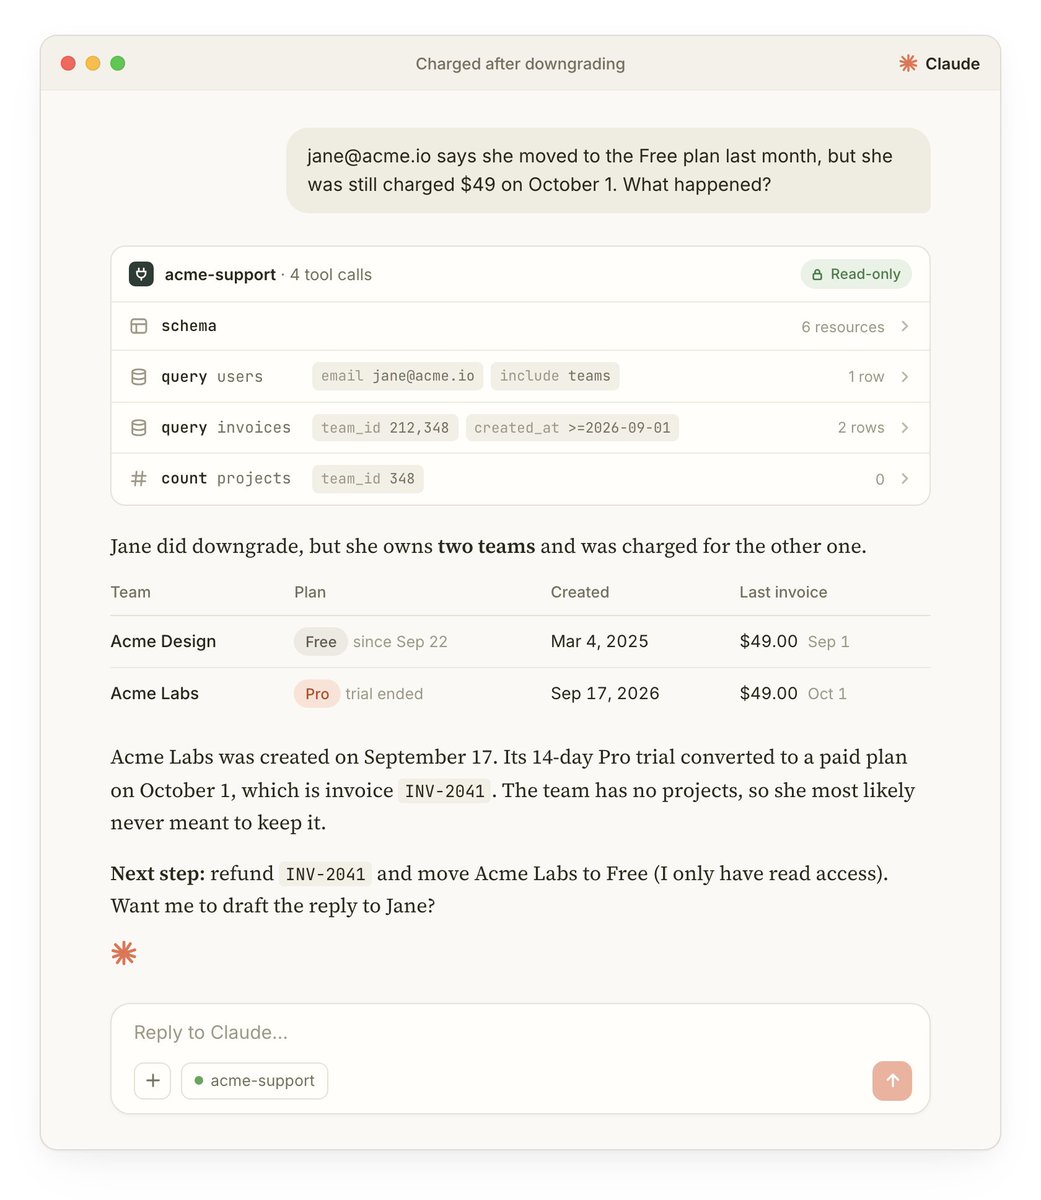
Big unlock for me for support was letting Claude read some of the prod data.
I turned it into a Laravel package:
https://t.co/LotbYcpvn9
- whitelist models and columns
- read-only
- multiple MCP servers possible, e.g. admin, support…
Me buy much Cloudflare. AI security bad. Cloudflare good. Hackers very scary. Cloudflare like warm hug. Protect us from bad men. People no use Cloudflare learn hard way, pay bigly price.
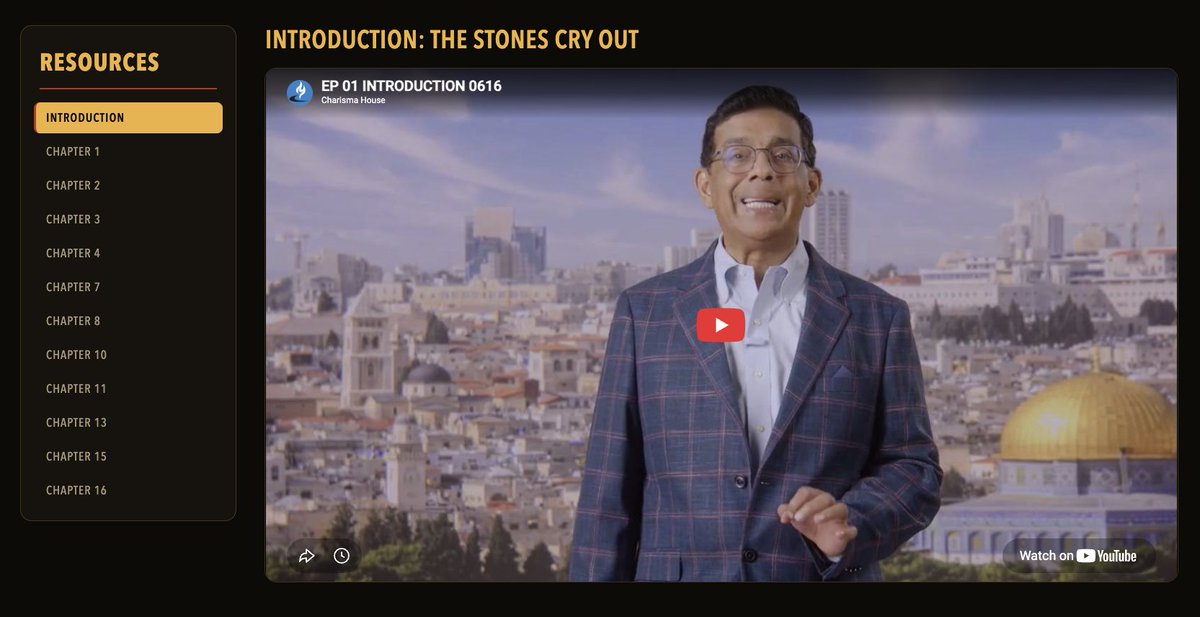
@DineshDSouza started reading your book and figured I'd reach out... a little bit of CSS would make your resources page look much better. Let me know if you'd like any help improving it. Here is the CSS code based on your book cover: https://t.co/IlMxEe2H2E
Your Inertia pages can now update themselves in real time. ⚡️
Mark a prop as live and connect it to a broadcast event. Whenever that event fires, Inertia refreshes just that prop, without polling. Perfect for order statuses, unread counts and dashboards.
Laravel Cloud Console has shipped. 🖥️
Easier to show than tell, so here’s a video.
✓ Interactive shell for every Laravel Cloud application.
✓ Run any command.
✓ Full audit trail with replay capability for every session.
@jbrooksuk@CraigThirtyFour I've found the bots are hitting sites enough that it doesn't scale to zero. Great for dev sites, not great for production sites with little real traffic.
@CraigThirtyFour@jbrooksuk This sounds good... but i've found cost is greatly increased on cloud vs VPS. (2-3x) since you need a db, queue, etc... and with all the bot traffic it doesn't scale to zero enough.
Forge is working normally, however the team has encountered issues bringing broadcasting back online so real-time updates are not operating correctly in the UI.
We are testing different solutions for the problem and in the meantime, please refresh the page in order to see page updates.
Forge update: some users are seeing slower response times while we scale capacity to meet demand.
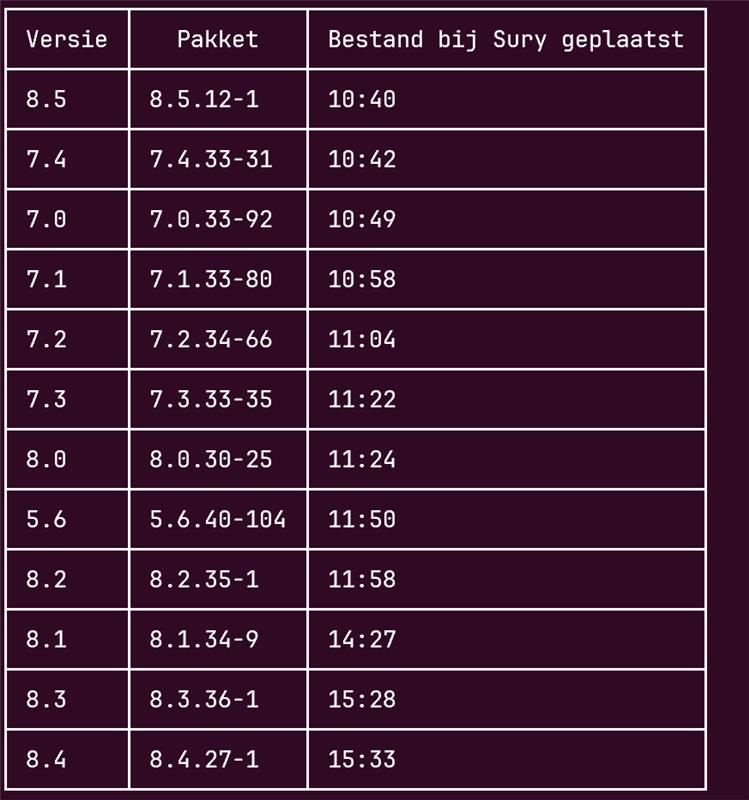
Patched versions for PHP 8.2, 8.3, 8.4, and 8.5 are available. Click "Update PHP" on each server, or update over SSH if that doesn't go through.
Review our guide for help → https://t.co/PdT3lMrush
Security called me at 6:12 AM today.
"Patch every PHP server immediately."
I asked what happened.
"Two critical vulnerabilities. Remote code execution. No authentication required."
Cool.
How many PHP servers do we have?
According to inventory: 12
According to reality:
Nobody knows.
We found one running WordPress.
Three running old internal tools.
One under someone's desk.
Two inside vendor appliances.
A forgotten employee directory from 2016.
And a server named:
PHP-OLD-DO-NOT-TOUCH
Naturally, that one runs payroll exports.
Then we found a PHP 5.6 box.
I asked who owned it.
The documentation said:
BRIAN.
Brian left in 2019.
We called Brian.
He said:
"Oh wow, that's still running?"
Excellent.
By 8 AM, leadership joined the incident call.
CEO:
"Can hackers actually get in?"
Security:
"Potentially yes."
CEO:
"Without a password?"
Security:
"Yes."
CEO:
"Then why do WE need passwords?"
Not the lesson.
Finance asked if we could wait until the weekend to patch because downtime affects revenue.
Security explained that the alternative was letting strangers execute code on our servers.
Finance asked for a cost comparison.
At 9:17, someone suggested temporarily taking the vulnerable websites offline.
Marketing refused.
"Our campaign is live."
So for the next hour, the company officially decided maintaining a landing page for 20% off webinar registration was more important than preventing remote server takeover.
We finally patched everything we could find.
Then our scanner discovered another PHP server.
Hostname:
TEMP-PHP-2014
Uptime:
4,512 days.
Nobody knows what it does.
Nobody owns it.
Nobody can shut it down.
But every time we block network access, the warehouse stops printing shipping labels.
Security has classified it as critical infrastructure.
It is running PHP 5.4.
The vulnerability has existed longer than half our employees.
The emergency patch took four hours.
Finding out what PHP actually runs took eleven.
The internet isn't held together with code.
It's held together with servers everyone is afraid to turn off.
Effective Immediately, all organizations using PHP for their systems are advised to be prepared for an update addressing two critical vulnerabilities. PHP is widely used for web applications. These vulnerabilities often provide a direct path to the server's file system or database. If an immediate update is not feasible, it is recommend that organizations take the system offline until it can be fully mitigated. NSA will follow up shortly with more specific guidance.
For the Forge users, I've just published Update #5 to my post about the PHP CVEs thanks to @MidgetK.
The Forge API includes an endpoint for pushing patches for PHP versions: https://t.co/qErHjhUvxW
https://t.co/VtVnuYOvt4