Today’s hunt: 23 fake “Find My” domains built to unlock stolen iPhones.
A thief texts the owner that their lost phone was found, and the link leads to an Apple ID phish. Everyone else, scanners included, gets bounced from /login straight to the real support[.]apple[.]com, so every passive check sees Apple.
Registered in same day batches since August across Sav[.]com, NameSilo, PDR and Namecheap, in English, Spanish, French and Vietnamese, with two more added yesterday. Six are live today.
The tell is the page they redirect to: one fuzzy DOM band, Apple’s own domains excluded. fingerprint.dom_band 1:cfae098131ec · verified 19 Nov 2026
40 domains, 8 languages, and not one brand to typosquat
Today’s Webamon daily hunt: a fake “AI Trading Platform” lead form for investment fraud, rebuilt under a new made-up name on every site (Alinixio, ApoyVex, Akaudalorio…) and localised from English to Japanese, Korean and Greek
Every page has a unique exact hash, but one fuzzy DOM fingerprint ties them all together. Many domains were registered months in advance and left to age before going live. 38 of 40 still hosting at time of check
Happy Hunting
Our analysts will get hands-on experience using Webamon’s real-time threat intelligence, domain monitoring, and campaign-tracking engine to hunt active attacker infrastructure, not just isolated indicators.
More tools. Deeper investigations. Job-ready defenders.🛡️
#GiSOC#Webamon
Today’s Daily Hunt: a fake trading platform kit that has shipped 291 invented brands since June, each titled “Trade With Ease”.
The pages promise 100x leverage, one click copy trading and fast deposits, with placeholder stats (0+ traders, $0B volume) that give away the template.
Not one carries a malicious or scam reputation flag. They are newly registered, spread across 15+ registrars, and we caught the whole fleet on a single shared page structure, not a domain name and not a blocklist. 29 domains in the current wave, 13 still hosting, verified today
90 fake trading brands. One kit. 20+ countries.
Today’s Webamon daily hunt: a localized AI investment-fraud factory. Each domain is a throwaway brand (“VeleroTokendes”, “Zeravisk”, “Bright Portmantage”...) localized for a different country, Spain to Brazil to Norway to Japan, with real firms abused too (Pepperstone, Petrobras, 3G Capital).
Every site renders the same page structure and loads the same backend host, tolfex[.]com. 90 distinct domains share one content fingerprint, 88 still hosting at time of check, all registered in the last three weeks behind Cloudflare.
Happy Hunting
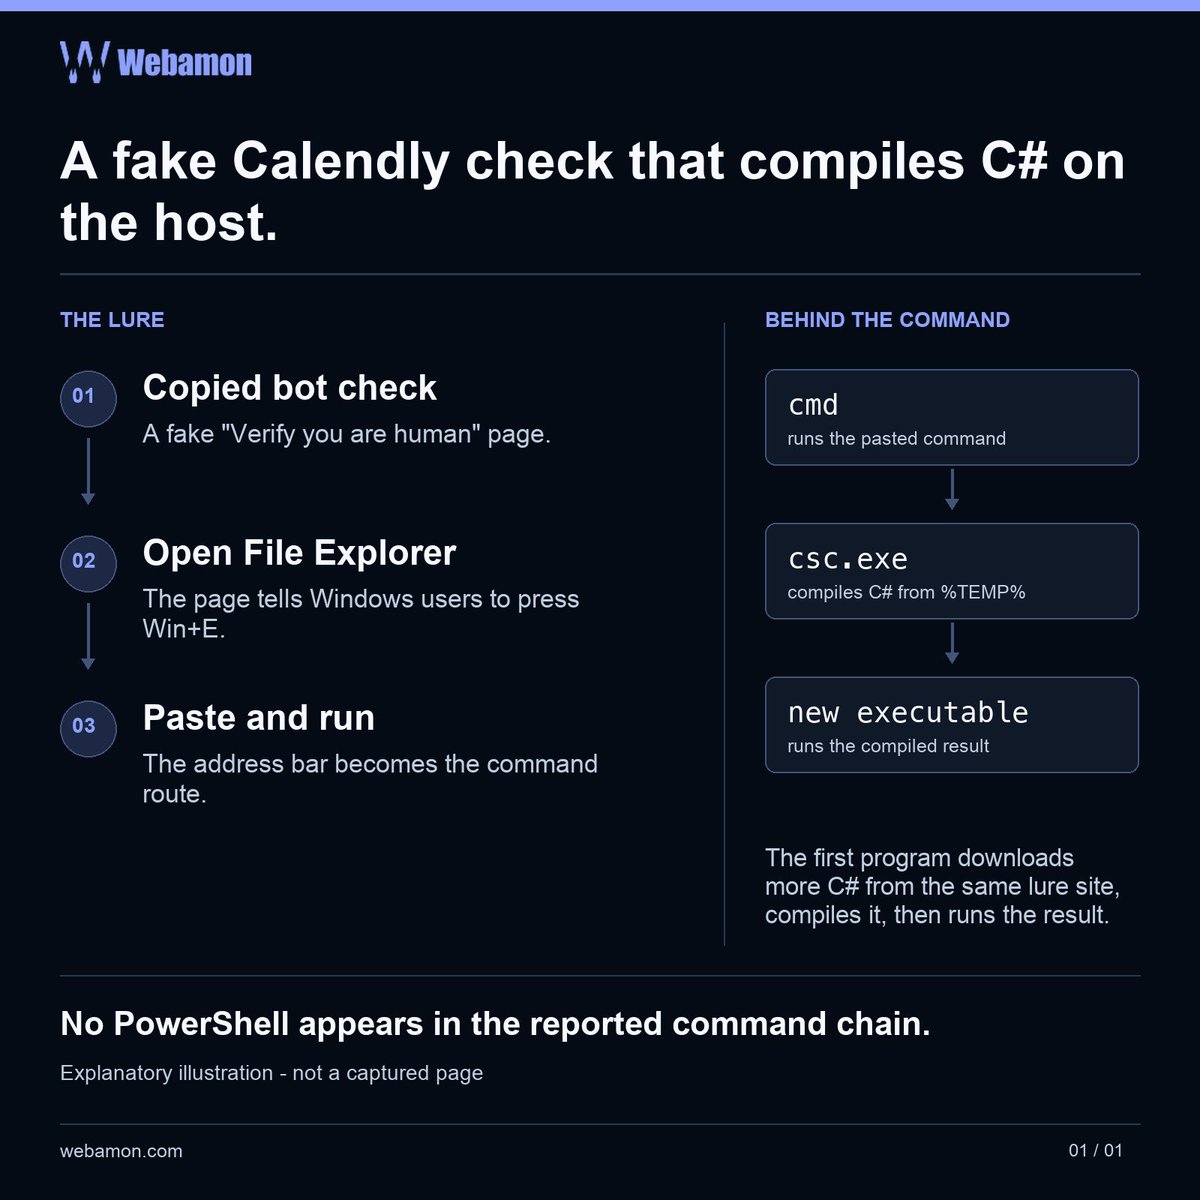
Webamon found a Calendly-dressed fake bot check that sends Windows users through File Explorer. The pasted command is designed to write C# into %TEMP%, compile it with csc.exe and run the result - no PowerShell involved.
https://t.co/Pg50GVTmeg
IOCs:
Observed lure/payload domains:
arrivals-creative[.]com
apt-finder[.]org
Historical Calendly-link fingerprint matches:
foursets[.]agency
fourset[.]digital
#ThreatIntel #Cyber #Malware
138 sites, one kit, and ADNOC’s name on one of them.
Today’s Webamon daily hunt: a fake “AI trading platform” lead funnel localised for 30 countries, with an Arabic “ADNOC Profit” version capturing UAE phone numbers for callback fraud.
138 domains share one page template, all still serving when checked. 137 of them never mention the brand in the domain name, so domain watchlists miss them.
448 parked domains, 13 landers, one fake "Virus scan: Safe" download page.
Today's Webamon daily hunt: lapsed business domains on a parking feed bounce visitors through an ad redirector to rotating .xyz pages that fake a security check before a download.
The landing links are single use, so replaying one shows a blank page. 448 domains share a single content fingerprint since 16 Aug, and all 13 landers were still hosting on one server at time of check
hashtag#threatintel hashtag#malvertising hashtag#malware
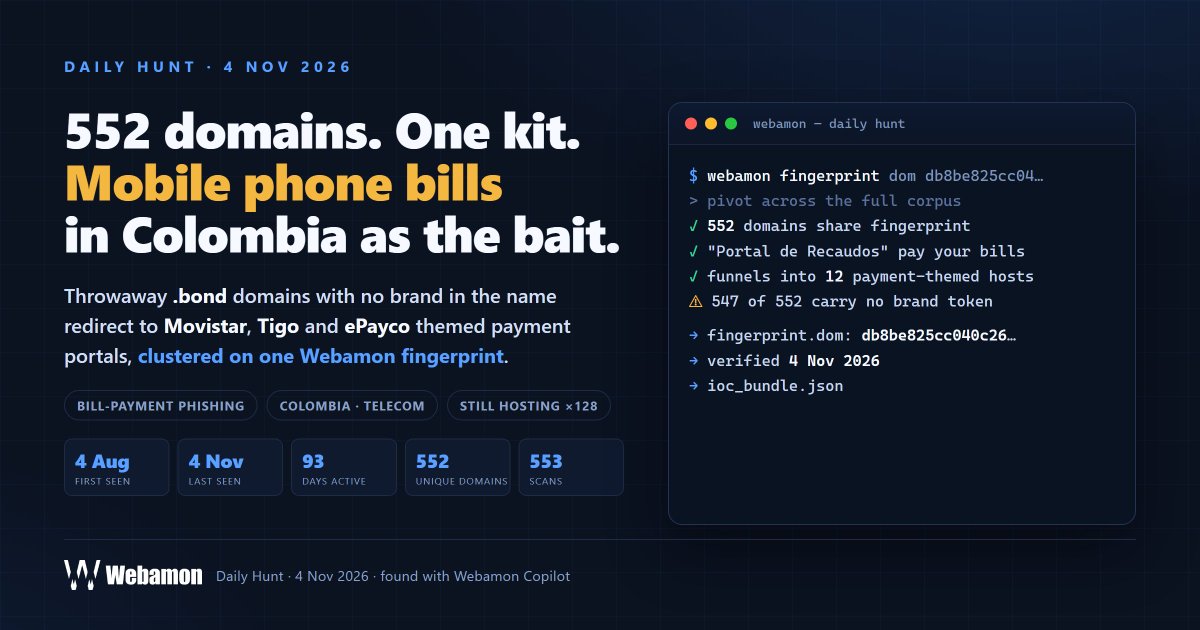
Today’s hunt: 552 throwaway domains, one phishing kit, and Colombian mobile phone bills as the bait.
Since 4 August an operator has been registering random .bond domains in batches, none with a brand in the name, and pointing them at “Portal de Recaudos” bill payment pages themed on Movistar, Tigo and ePayco. Scanners get a neutral decoy page; the lure lives in the title and the landing hostnames.
547 of the 552 would never trip a brand-name or typosquat alert. One page fingerprint finds all of them, and 128 are still hosting today.